
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended

 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 darthton/blackbone
Windows memory hacking library
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
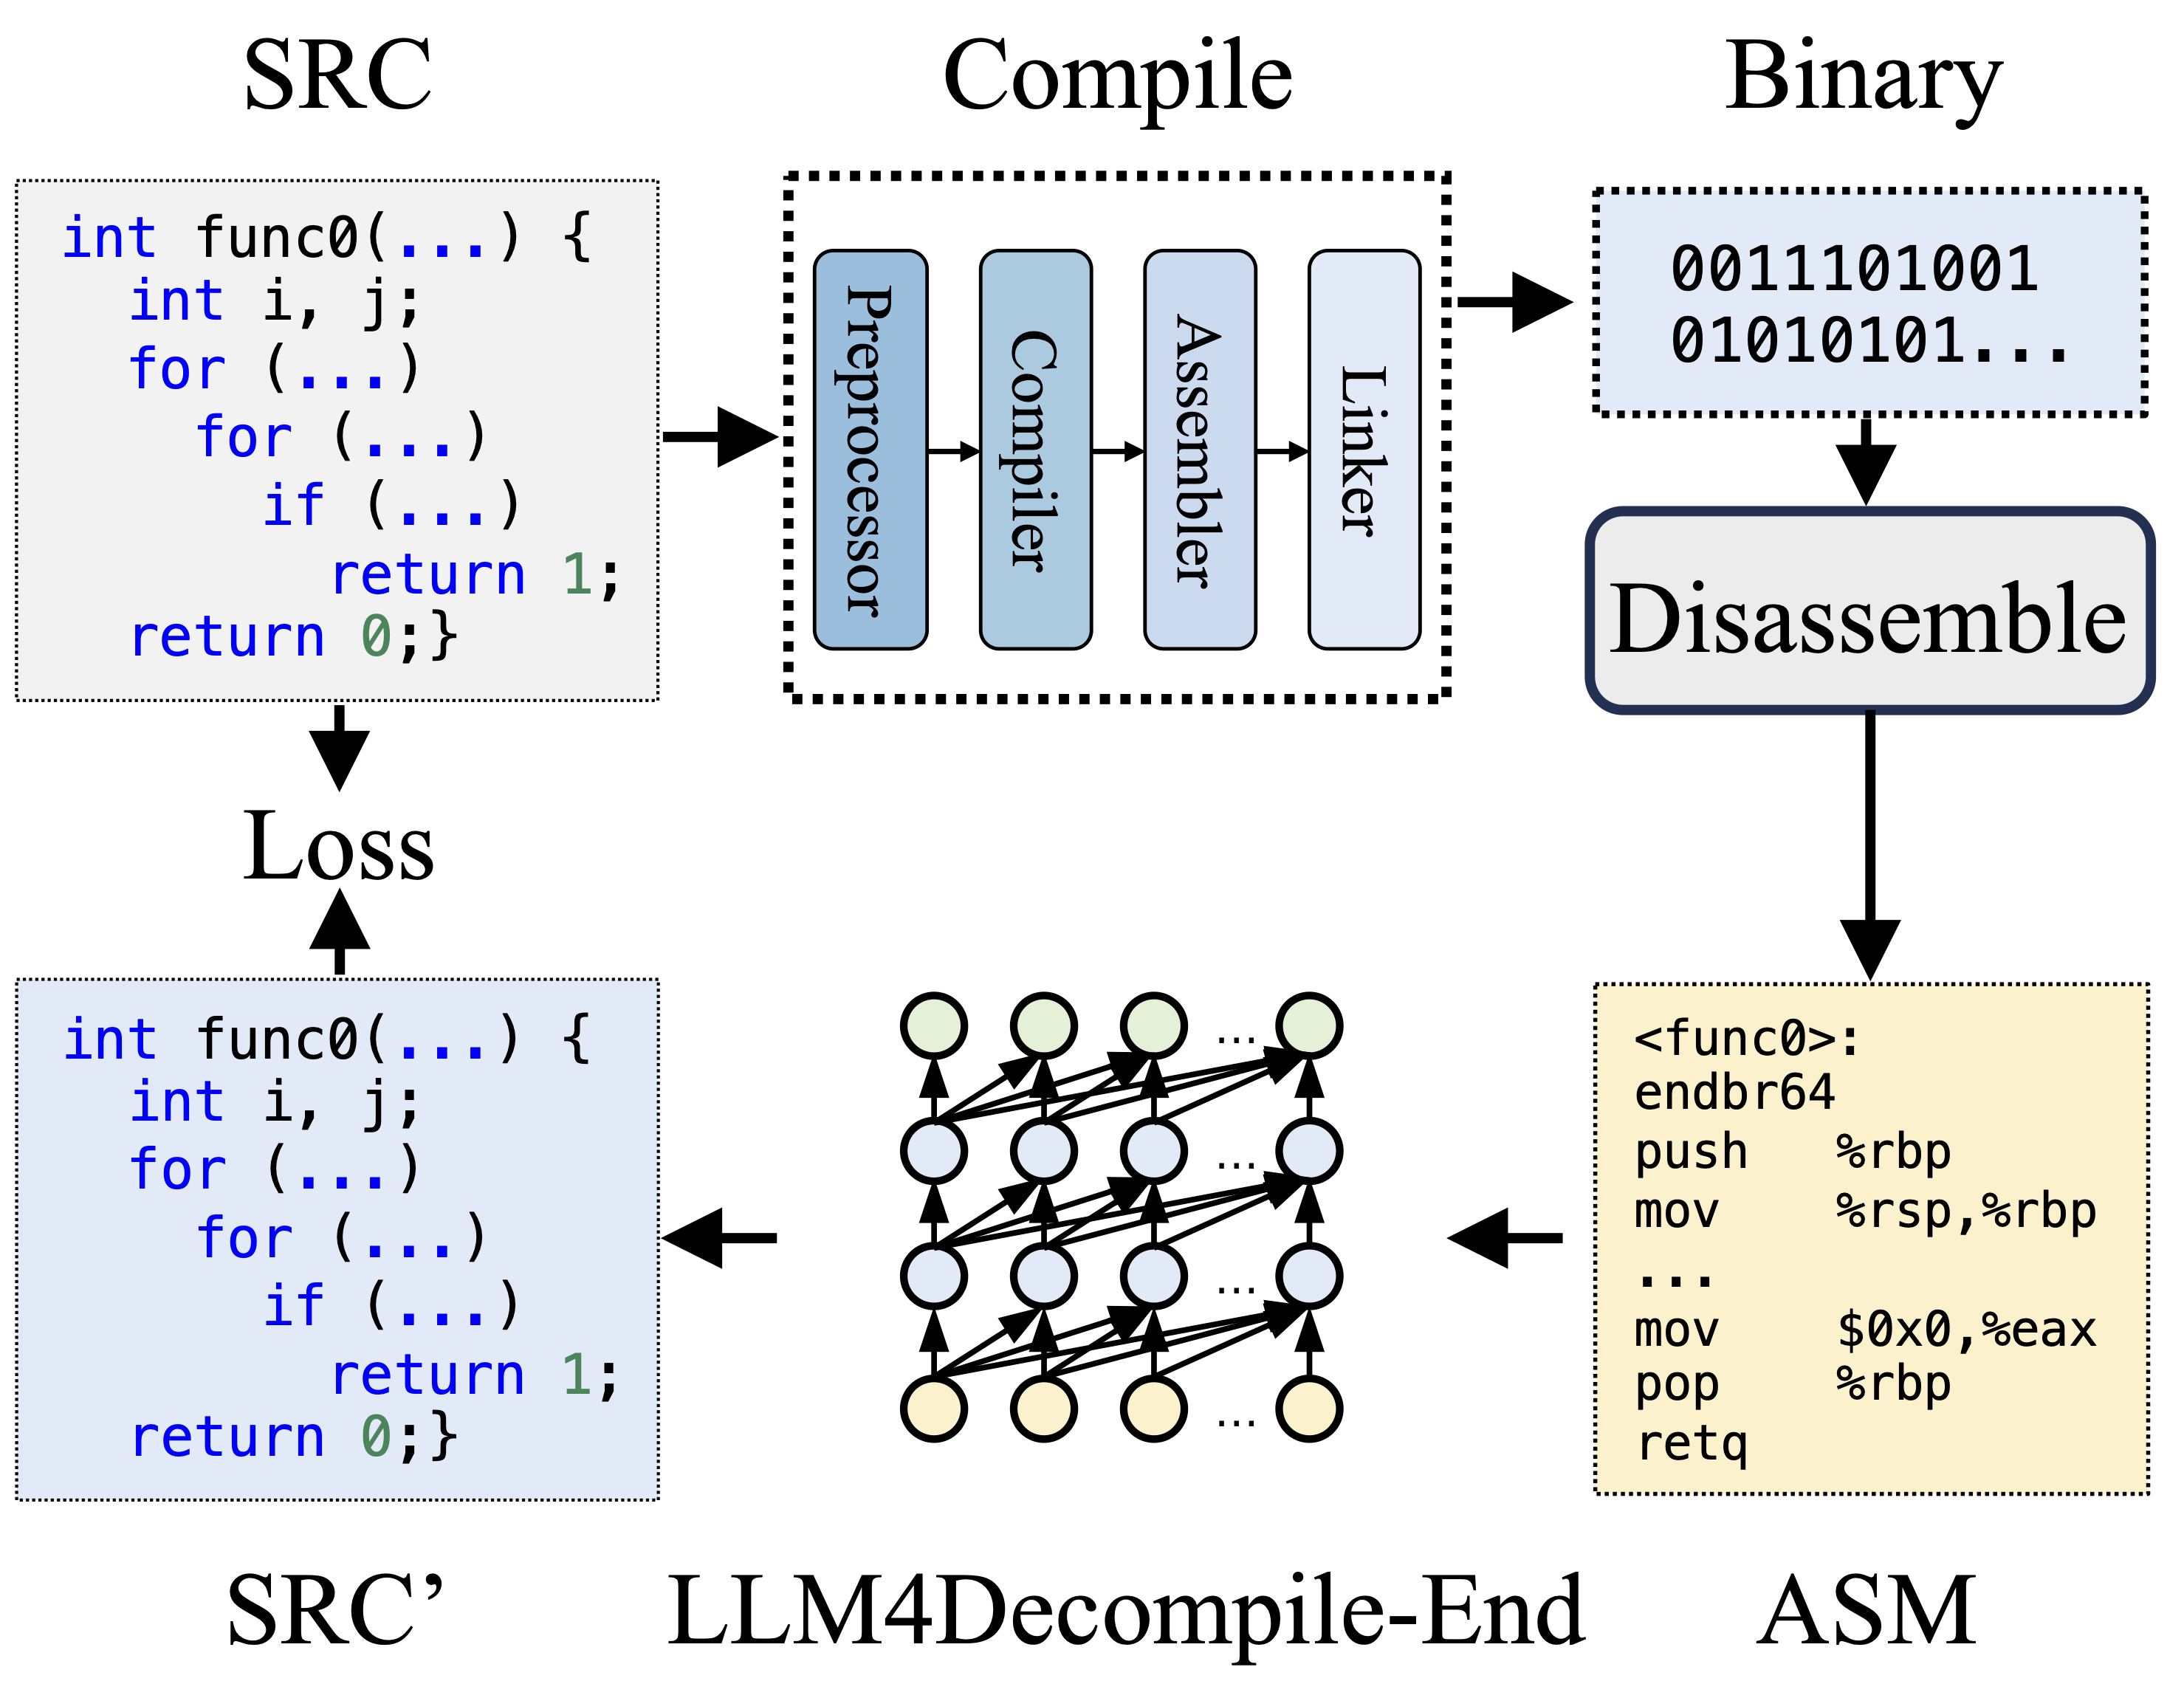 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 secfigo/awesome-fuzzing
A curated list of fuzzing resources ( Books, courses - free and paid, videos, tools, tutorials and vulnerable applications to practice on ) for…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)






