
 #1
 ethicalhackingplayground/ssrf-king
SSRF plugin for burp Automates SSRF Detection in all of the Request
 codewatchorg/sqlipy
SQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
 bbva/apicheck
The DevSecOps toolset for REST APIs
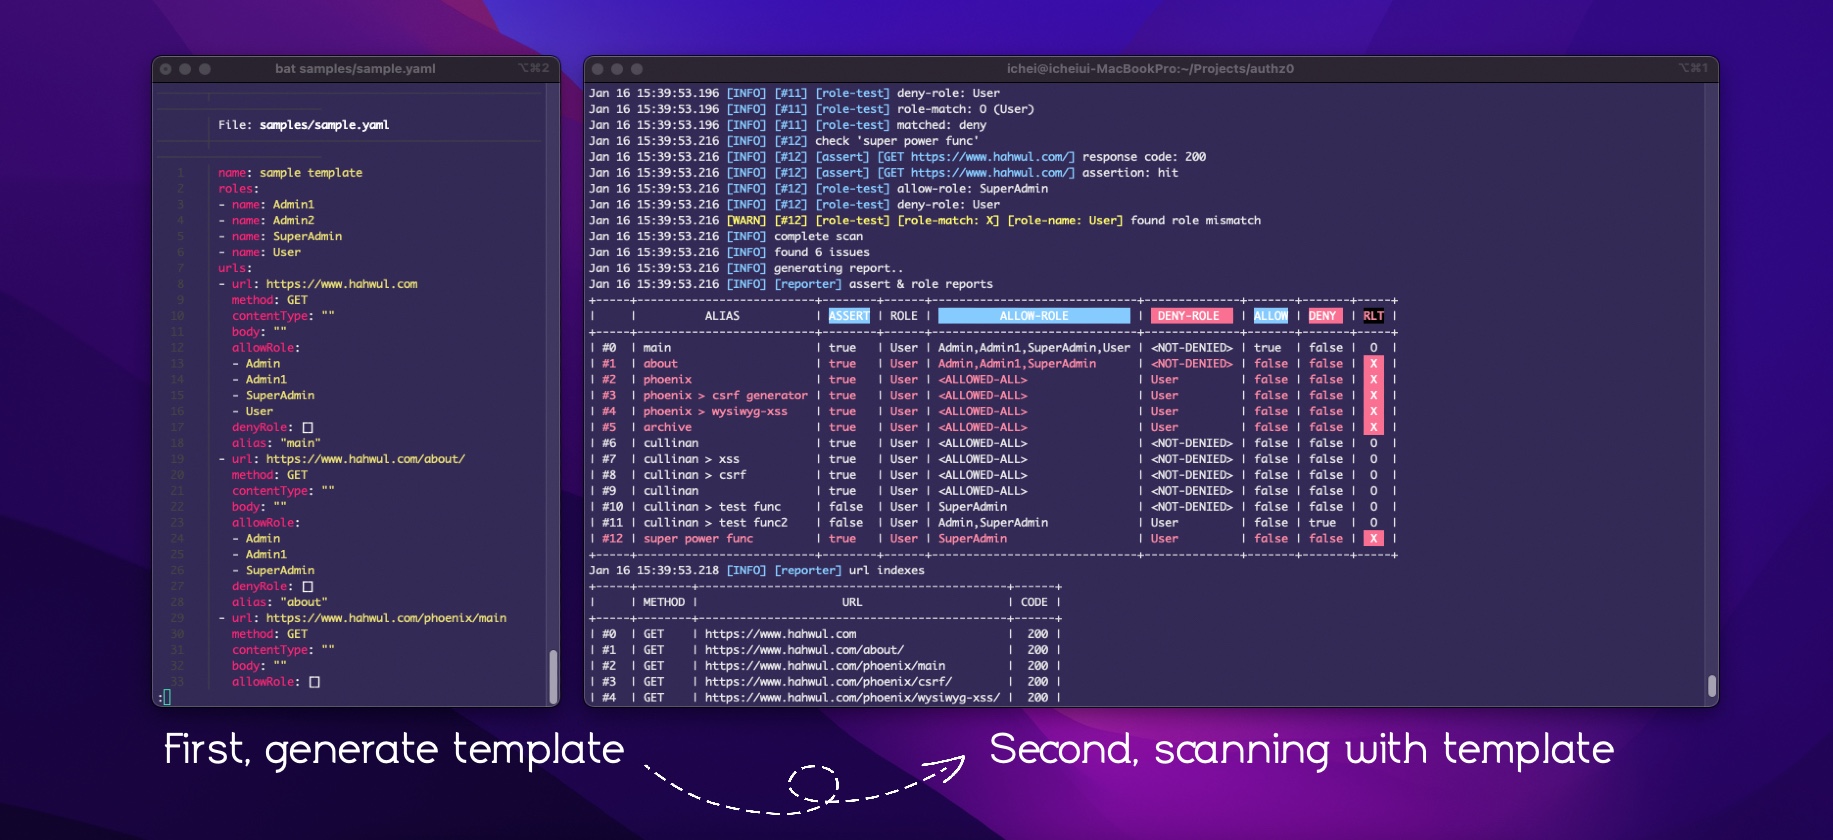 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
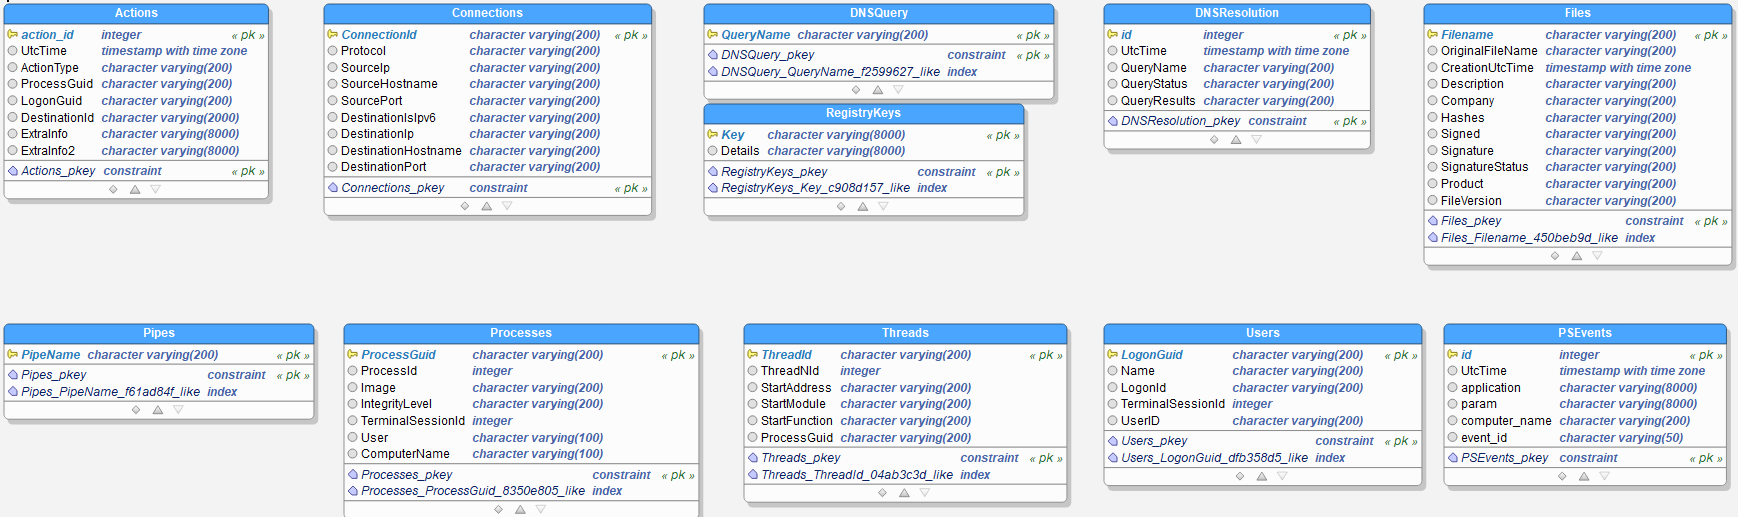 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 subgraph/vega
Subgraph Vega
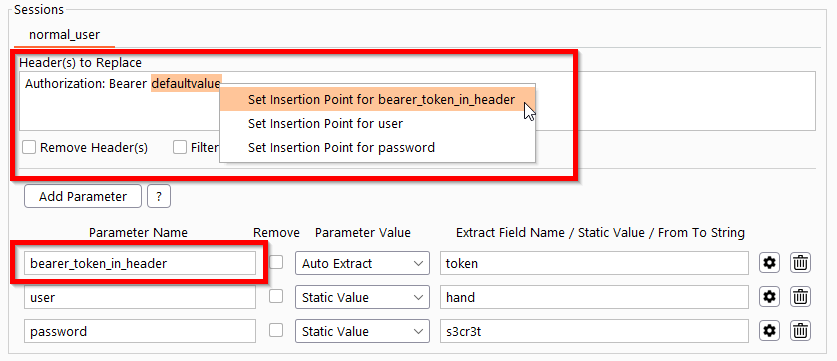 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 ngalongc/openapi_security_scanner
Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…
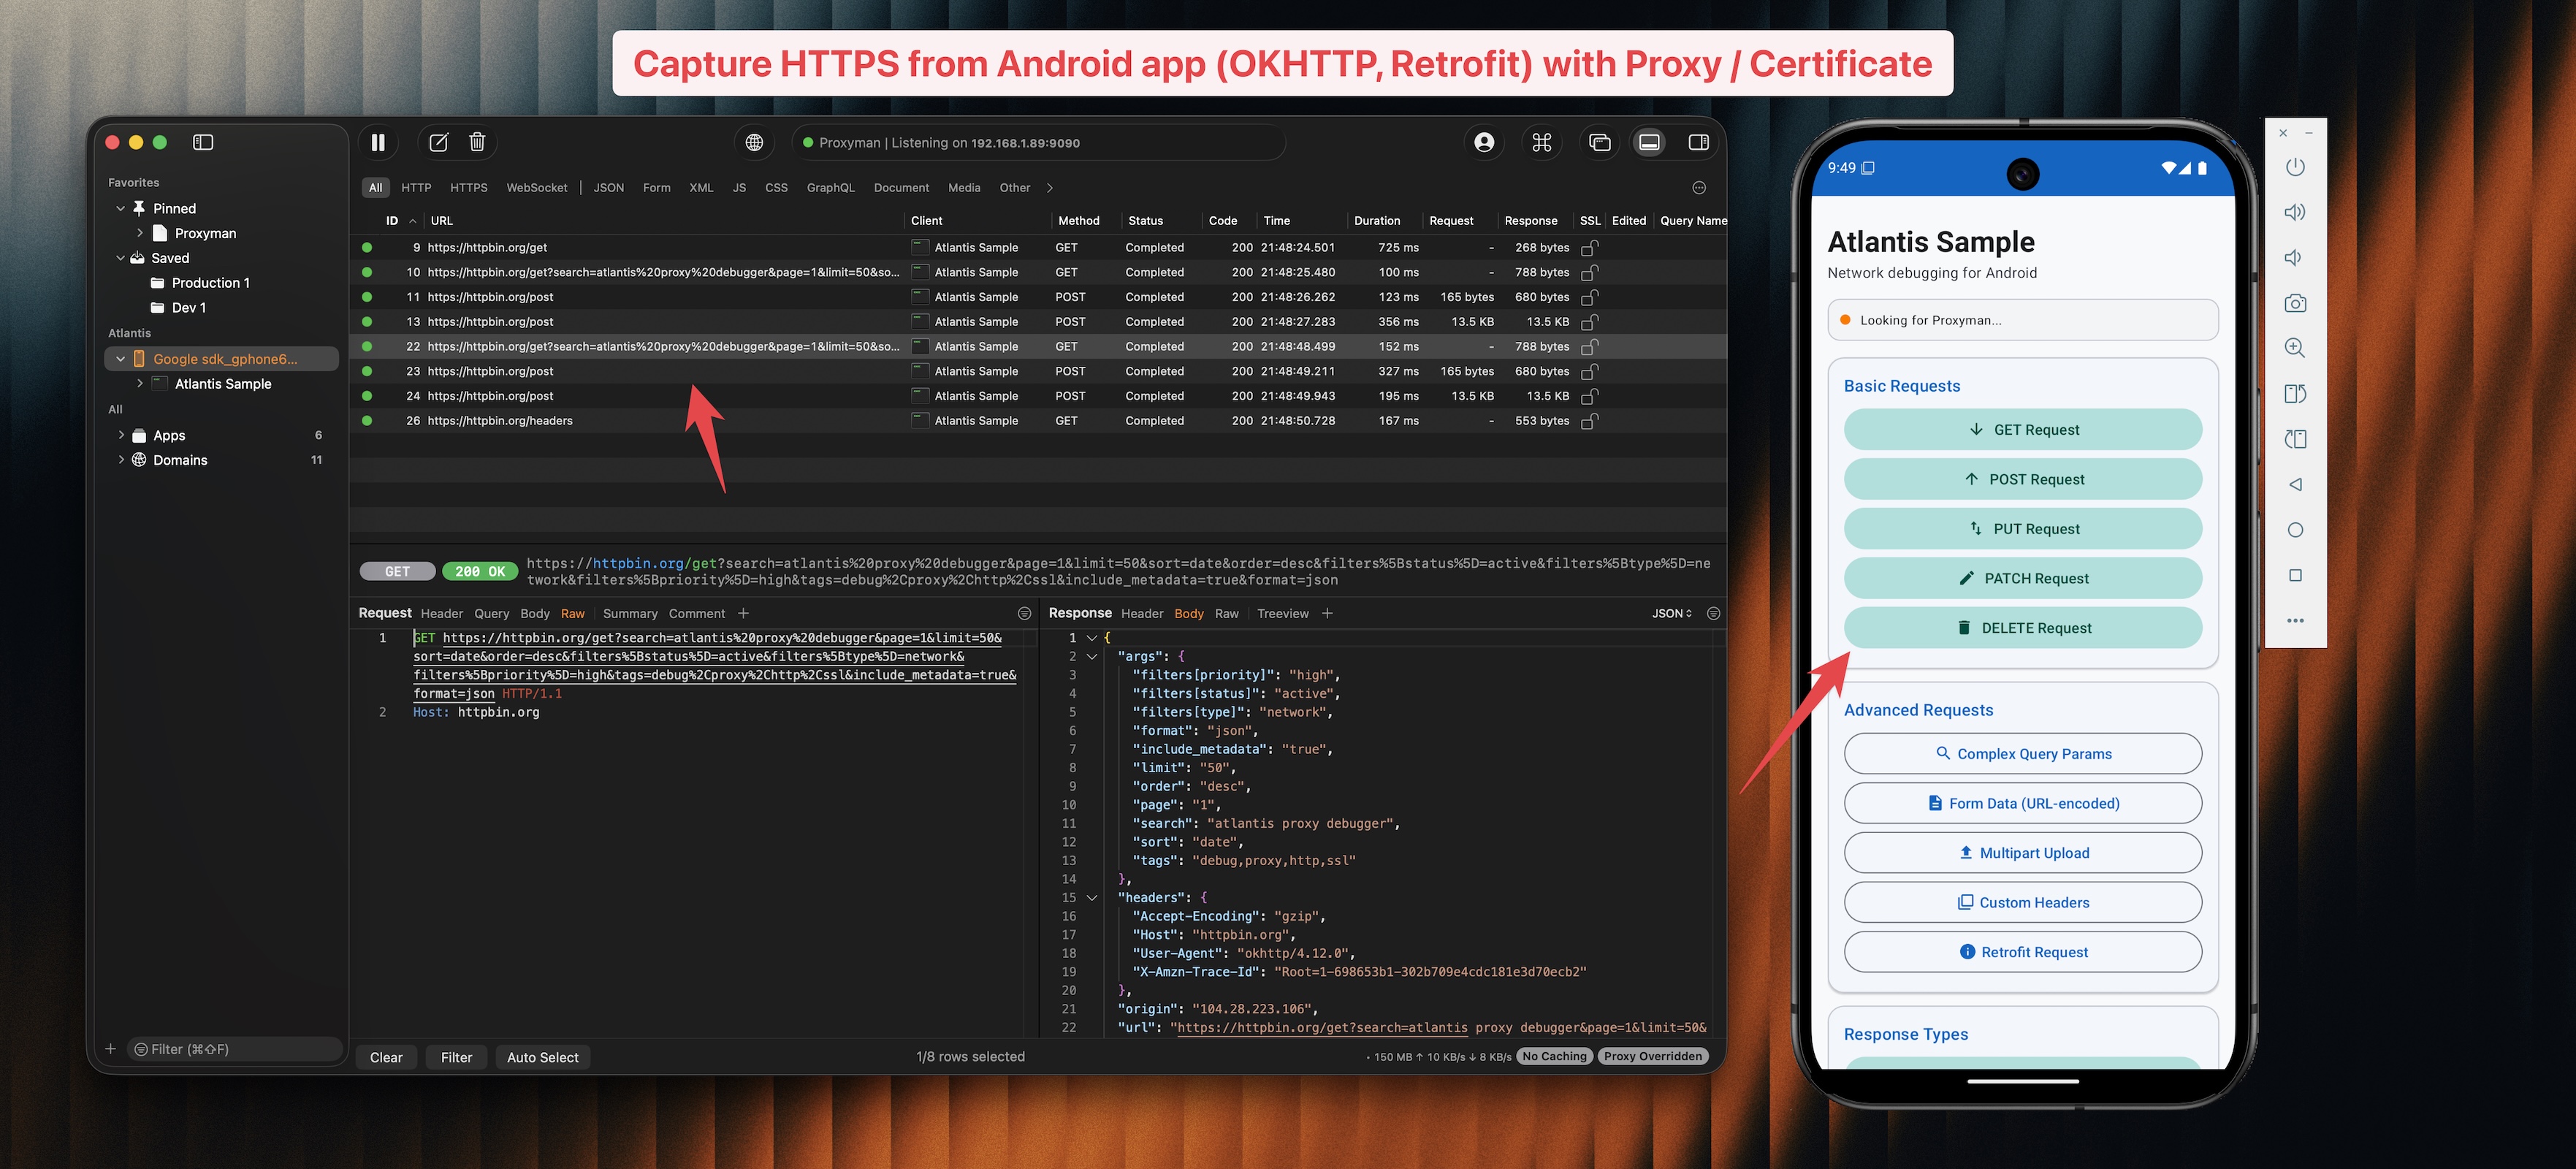 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice









