
 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended

 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 ayush-parab/sentinel-gpt
Automated threat hunting pipeline that ingests Azure logs, uses LLM reasoning to detect suspicious activity, assess risk, and generate remediation…
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
 gosuda/ssh-chatter
ssh-chat in modern c
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 prime-radiant-inc/superpowers-evals
Behavioral eval lab (Quorum) for the superpowers project that drives real coding-agent CLIs (Claude, Codex, Gemini, Kimi, and more) through a QA…
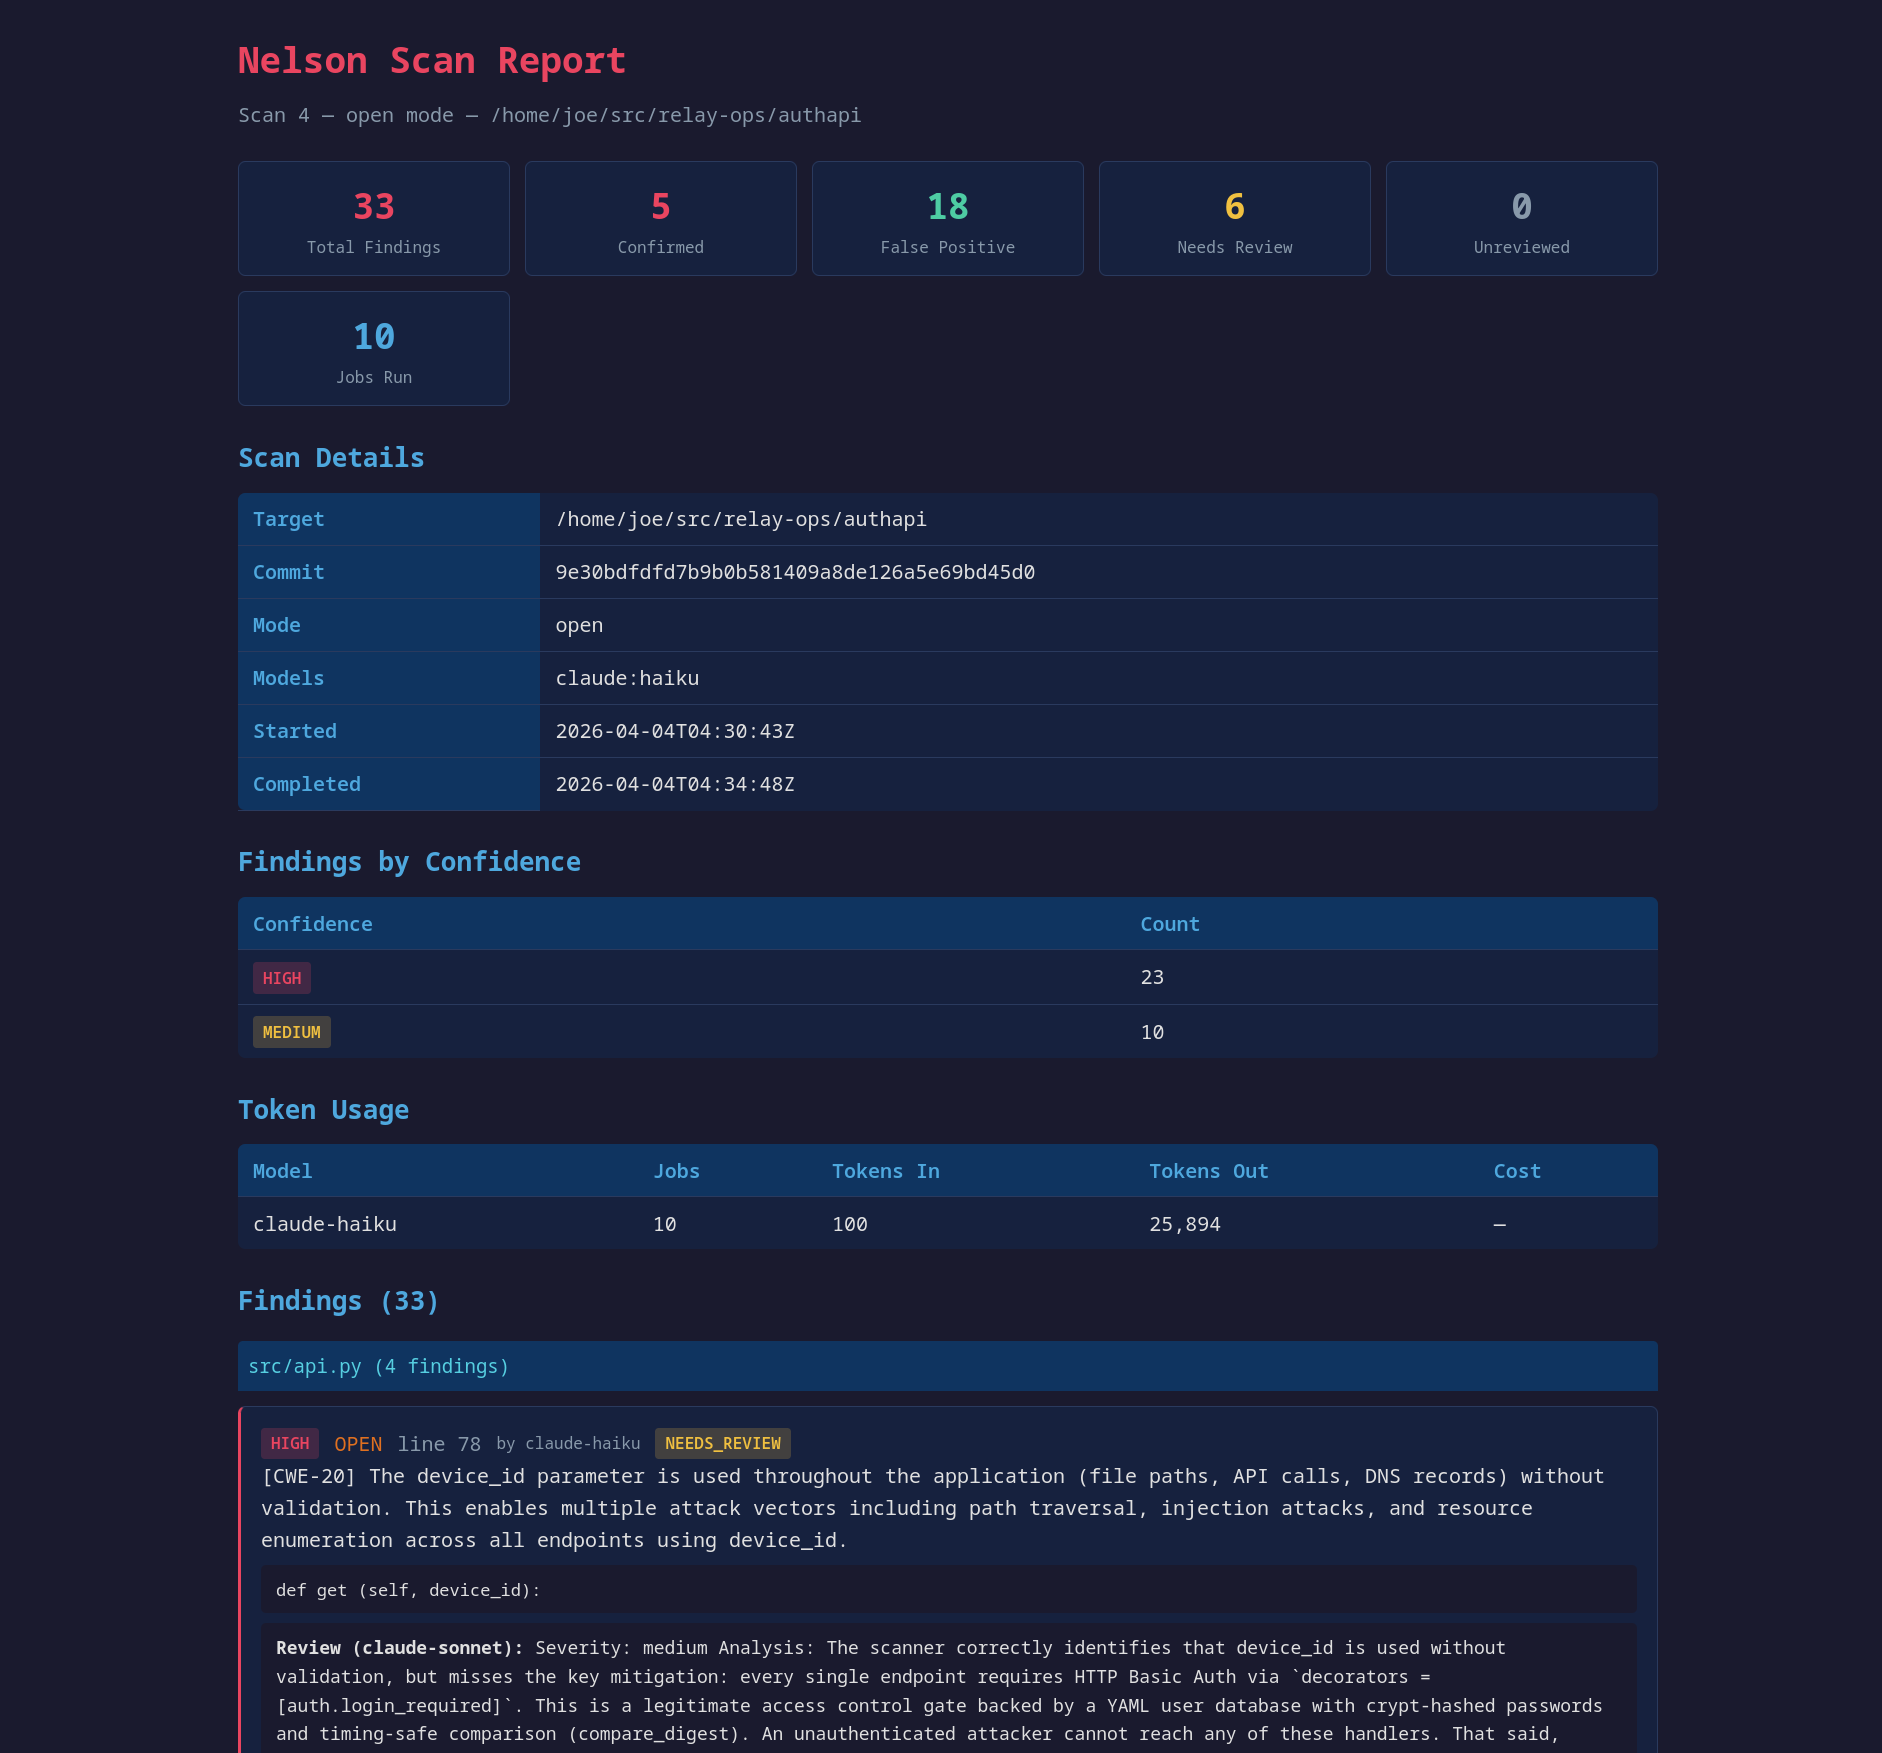 swelljoe/nelson
Finding vulnerabilities through dumb brute force
 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 golab-arch/synaptic-sentinel
The vibe-coding security sentinel. Apache-2.0 agentic security toolkit for AI-assisted projects: 5 deterministic scouts + LLM Brain Layer (BYOK…
 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 swe-agent/swe-agent
LLM-powered agent that autonomously fixes GitHub issues, finds cybersecurity vulnerabilities, and solves CTF challenges using configurable tool-use…
 xu-xiang/awesome-security-vul-llm
本项目通过大模型联动爬虫,检索Github上所有存有有价值漏洞信息与漏洞POC或规则信息的项目,并自动识别项目的目录结构、Readme信息后进行总结分析并分类,所汇总的项目可以帮助安全行业从业者收集漏洞信息、POC信息、规则等。








