Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SWE-agent — LLM-powered agent that autonomously fixes GitHub issues, finds cybersecurity vulnerabilities, and solves CTF challenges using configurable tool-use and state-of-the-art AI models. | Kitploit
Tools/GitHubGitHub/swe-agent/swe-agent
Exploit FrameworksVulnerability AnalysisCTFPenetration TestingPapers & ResearchLearning & EducationAI Security
GitHubswe-agent/swe-agent

SWE-agent

LLM-powered agent that autonomously fixes GitHub issues, finds cybersecurity vulnerabilities, and solves CTF challenges using configurable tool-use and state-of-the-art AI models.

View Repository
20.0k2.2k1034 months agoReviewed by Kitploit
Website
Share

swe-agent.com

Docs Slack arxiv 2405.15793

mini-swe-agent.com

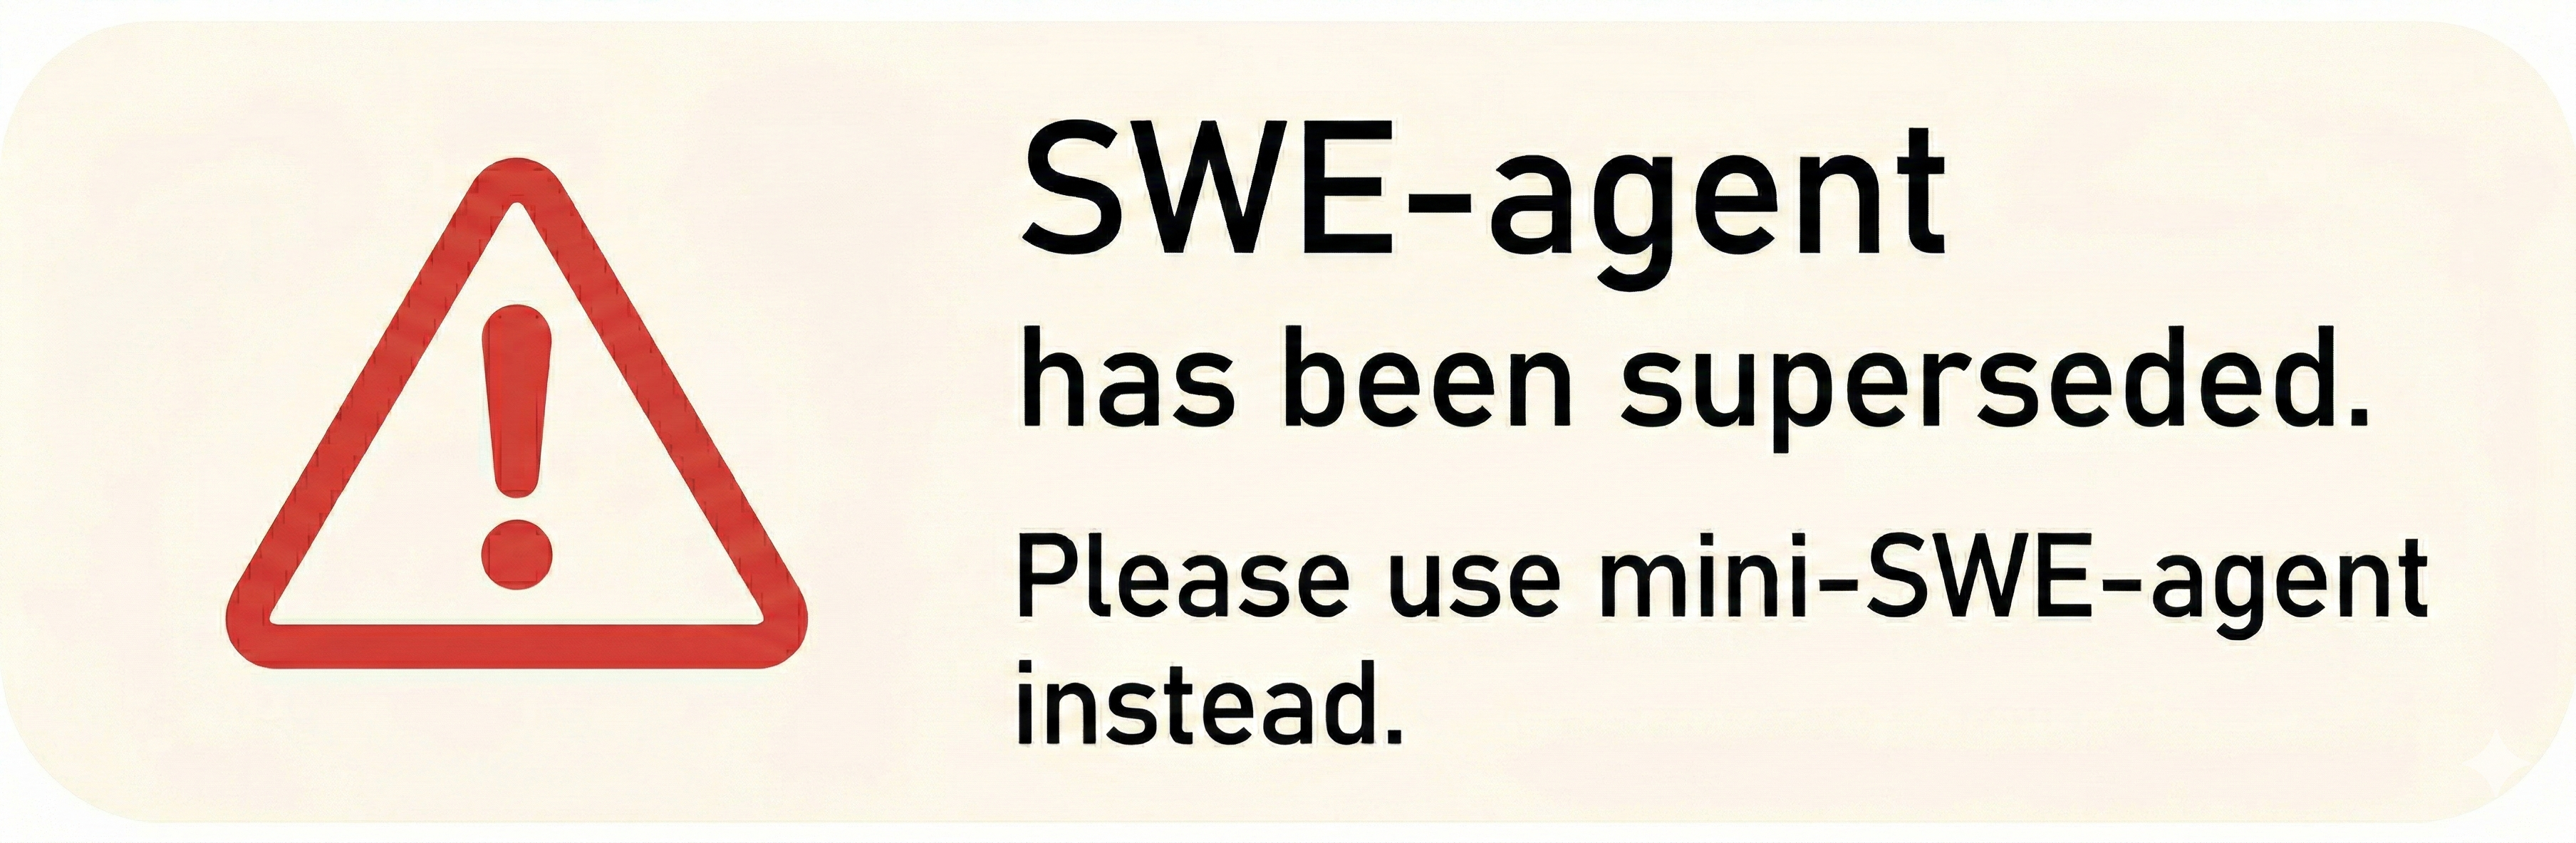
[!warning] Most of our current development effort is on mini-swe-agent, which has superseded SWE-agent. It matches the performance performance of SWE-agent, while being much simpler. See the FAQ for more details about the differences. Our general recommendation is to use mini-SWE-agent instead of SWE-agent going forward.

SWE-agent enables your language model of choice (e.g. GPT-4o or Claude Sonnet 4) to autonomously use tools to fix issues in real GitHub repositories, find cybersecurity vulnerabilities, or perform any custom task.

  • ✅ State of the art on SWE-bench among open-source projects
  • ✅ Free-flowing & generalizable: Leaves maximal agency to the LM
  • ✅ Configurable & fully documented: Governed by a single yaml file
  • ✅ Made for research: Simple & hackable by design

SWE-agent is built and maintained by researchers from Princeton University and Stanford University.

📣 News

  • July 24: Mini-SWE-Agent achieves 65% on SWE-bench verified in 100 lines of python!
  • May 2: SWE-agent-LM-32b achieves open-weights SOTA on SWE-bench
  • Feb 28: SWE-agent 1.0 + Claude 3.7 is SoTA on SWE-Bench full
  • Feb 25: SWE-agent 1.0 + Claude 3.7 is SoTA on SWE-bench verified
  • Feb 13: Releasing SWE-agent 1.0: SoTA on SWE-bench light & tons of new features
  • Dec 7: An interview with the SWE-agent & SWE-bench team

🚀 Get started!

👉 Try SWE-agent in your browser: Open in GitHub Codespaces (more information)

Read our documentation to learn more:

  • Installation
  • Hello world from the command line
  • Benchmarking on SWE-bench
  • Frequently Asked Questions

SWE-agent for offensive cybersecurity (EnIGMA)

SWE-agent: EnIGMA is a mode for solving offensive cybersecurity (capture the flag) challenges. EnIGMA achieves state-of-the-art results on multiple cybersecurity benchmarks (see leaderboard). Please use SWE-agent 0.7 while we update EnIGMA for 1.0.

In addition, you might be interested in our other projects:

Mini-SWE-Agent    SWE-ReX    SWE-bench    SWE-smith    sb-cli

Contributions

If you'd like to contribute to the codebase, we welcome issues and pull requests! For larger code changes, we always encourage discussion in issues first.

Citation & contact

SWE-agent is an academic project started at Princeton University by John Yang*, Carlos E. Jimenez*, Alexander Wettig, Kilian Lieret, Shunyu Yao, Karthik Narasimhan, and Ofir Press. Contact person: John Yang, Carlos E. Jimenez, and Kilian Lieret (Email: [email protected], [email protected], [email protected]).

If you found this work helpful, please consider citing it using the following:

SWE-agent citation
@inproceedings{yang2024sweagent,
  title={{SWE}-agent: Agent-Computer Interfaces Enable Automated Software Engineering},
  author={John Yang and Carlos E Jimenez and Alexander Wettig and Kilian Lieret and Shunyu Yao and Karthik R Narasimhan and Ofir Press},
  booktitle={The Thirty-eighth Annual Conference on Neural Information Processing Systems},
  year={2024},
  url={https://arxiv.org/abs/2405.15793}
}

If you used the summarizer, interactive commands or the offensive cybersecurity capabilities in SWE-agent, please also consider citing:

EnIGMA citation
@misc{abramovich2024enigmaenhancedinteractivegenerative,
      title={EnIGMA: Enhanced Interactive Generative Model Agent for CTF Challenges},
      author={Talor Abramovich and Meet Udeshi and Minghao Shao and Kilian Lieret and Haoran Xi and Kimberly Milner and Sofija Jancheska and John Yang and Carlos E. Jimenez and Farshad Khorrami and Prashanth Krishnamurthy and Brendan Dolan-Gavitt and Muhammad Shafique and Karthik Narasimhan and Ramesh Karri and Ofir Press},
      year={2024},
      eprint={2409.16165},
      archivePrefix={arXiv},
      primaryClass={cs.AI},
      url={https://arxiv.org/abs/2409.16165},
}

🪪 License

MIT. Check LICENSE.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →