

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Kategorien

Webanwendungs-Exploitation

Speziell entwickelte Tools zur Ausnutzung gängiger Webanwendungs-Schwachstellen (z. B. SQL-Injection, XSS).

Kitploit empfohlen
Top-Tools

10 ausgewählt
sqlmap preview#1

sqlmap

GitHubsqlmapproject/sqlmap
38.2kvor 1 Tag
beef preview#2

beef

GitHubbeefproject/beef
11.0kvor 3 Tagen
nuclei preview#3

nuclei

GitHubprojectdiscovery/nuclei
30.4kvor 13h 2m
zaproxy preview#4

zaproxy

GitHubzaproxy/zaproxy
15.6kvor 17h 25m
XSStrike preview#5

XSStrike

GitHubs0md3v/xsstrike
15.1kvor 1 Jahr
ffuf preview#6

ffuf

GitHubffuf/ffuf
16.5kvor 1 Monat
dirsearch preview#7

dirsearch

GitHubmaurosoria/dirsearch
14.6kvor 17 Tagen
feroxbuster preview#8

feroxbuster

GitHubepi052/feroxbuster
8.0kvor 8 Tagen
nikto preview#9

nikto

GitHubsullo/nikto
10.6kvor 3 Monaten
wpscan preview#10

wpscan

GitHubwpscanteam/wpscan
9.7kvor 1 Tag
NeuesteRelevanzBeliebtesteKürzlich aktualisiert
14979 Ergebnisse
dlink-dir610-exploits preview

dlink-dir610-exploits

GitHubrenatoalencar/dlink-dir610-exploits

Exploits für CVE-2020-9376 und CVE-2020-9377
authentication-authorizationvulnerability-analysisexploitation+2
4vor 6 Jahren
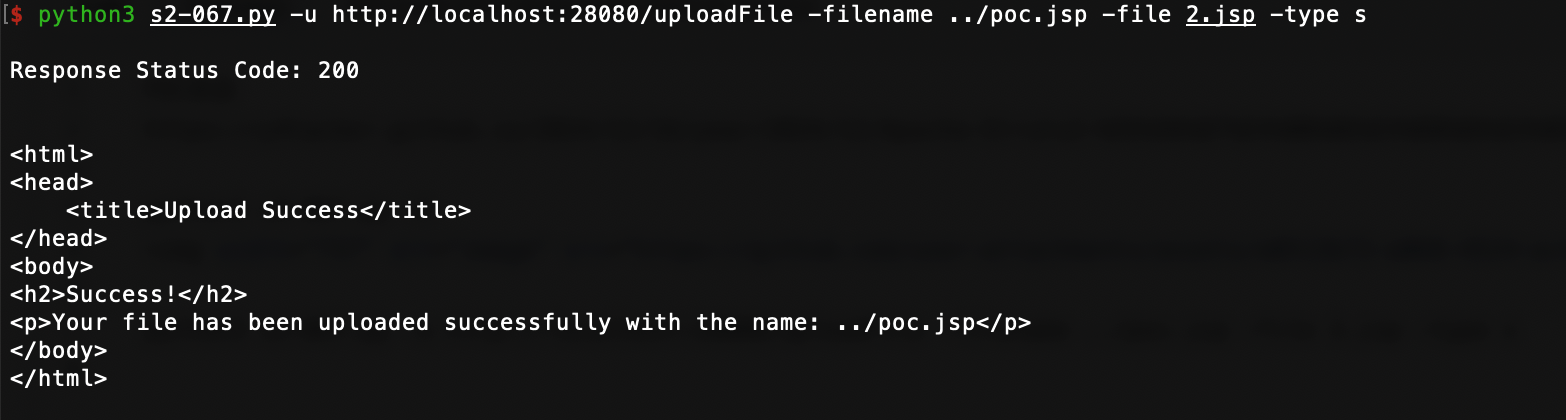
CVE-2024-53677 preview

CVE-2024-53677

GitHubyangyanglo/cve-2024-53677

Proof-of-Concept-Exploit für CVE-2024-53677 (S2-067), einen Apache Struts2 Datei-Upload-Logik-Bypass, der Remote-Codeausführung über manipulierte…

payload-generationvulnerability-analysisexploitation+2
3vor 1 Jahr
CVE-2021-33044 preview

CVE-2021-33044

GitHubspy0x7/cve-2021-33044

Dahua IPC/VTH/VTO Geräte Authentifizierungsumgehungs-Exploit
authentication-authorizationiot-securityvulnerability-analysis+2
3vor 5 Jahren
Apache-Struts-2-CVE-2017-5638-Exploit- preview

Apache-Struts-2-CVE-2017-5638-Exploit-

GitHubr4v3nbl4ck/apache-struts-2-cve-2017-5638-exploit-

Exploit erstellt von: R4v3nBl4ck und Pacman

vulnerability-analysisexploitationweb-application-exploitation+3
3vor 9 Jahren
Metinfo-6.1.2-SQL-injection preview

Metinfo-6.1.2-SQL-injection

GitHubianxtianxt/metinfo-6.1.2-sql-injection

Metinfo 6.1.2 SQL注入脚本
vulnerability-analysisexploitationweb-application-exploitation+1
2vor 7 Jahren
CVE-2015-1635-POC preview

CVE-2015-1635-POC

GitHubh3x0v3rl0rd/cve-2015-1635-poc

Proof-of-Concept-Exploit für CVE-2015-1635 (MS15-034), der die Remote-Code-Ausführung in HTTP.sys durch manipulierte HTTP-Anfragen auf anfälligen…
vulnerability-analysisexploitationweb-application-exploitation+2
2vor 2 Jahren
CVE-2026-10104-POC preview

CVE-2026-10104-POC

GitHubravi-lk/cve-2026-10104-poc

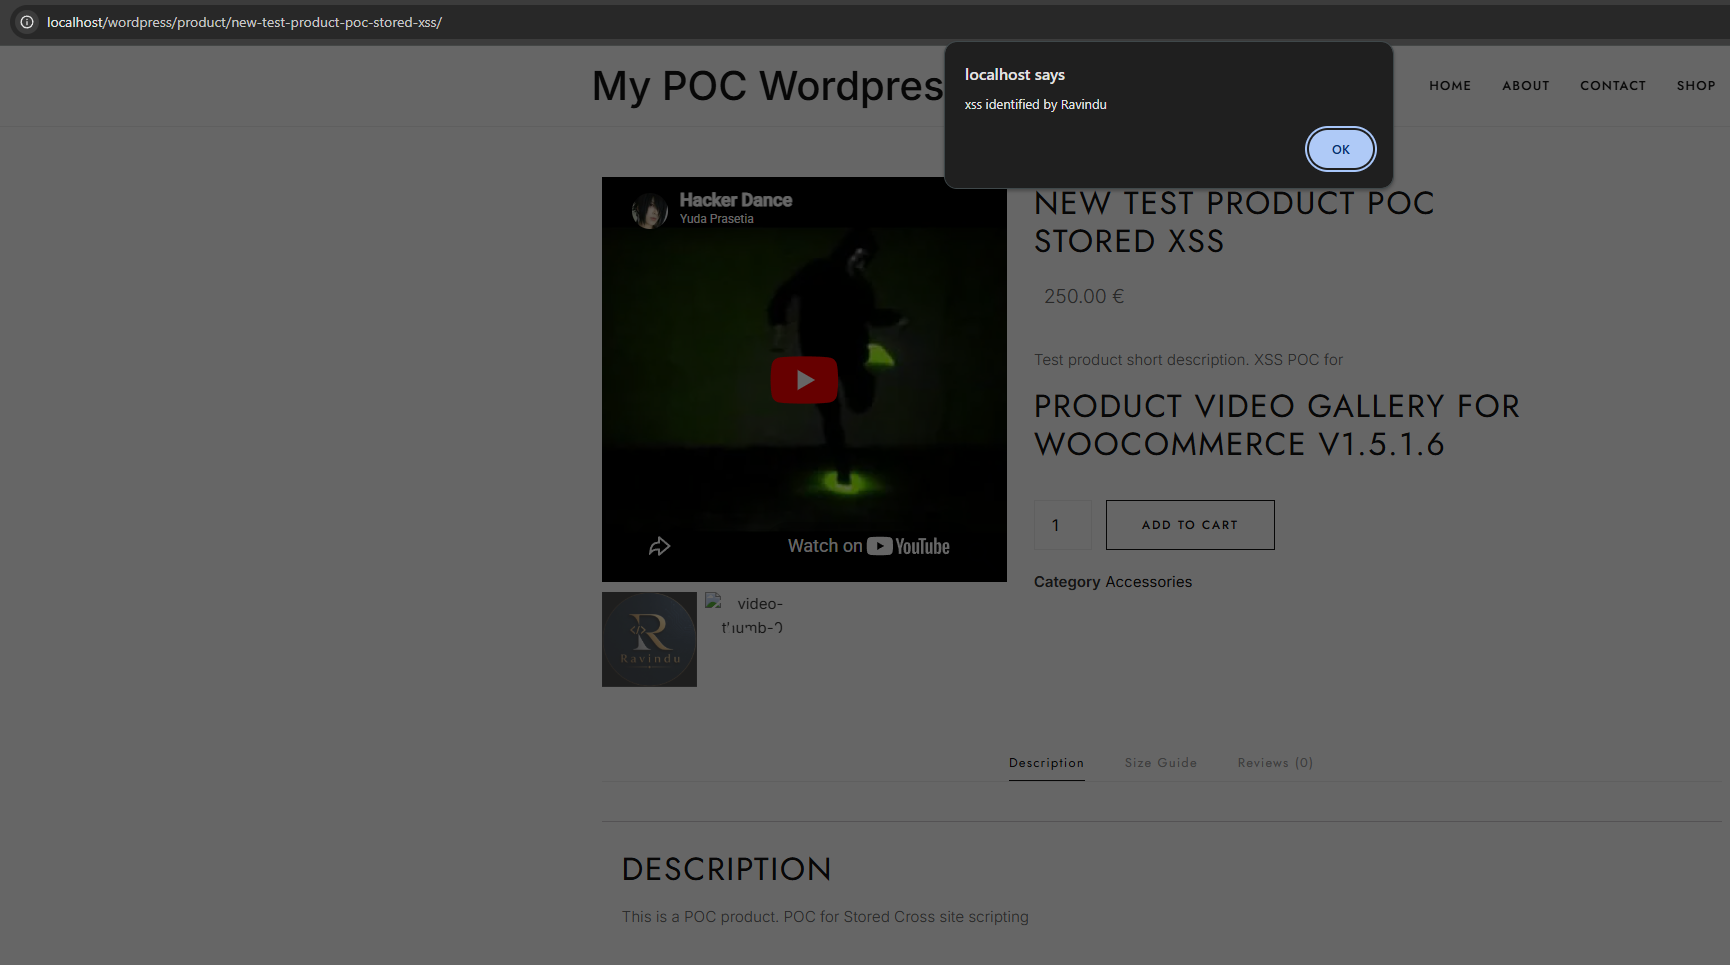
Product Video Gallery für Woocommerce <= 1.5.1.8 - Authentifiziertes gespeichertes Cross-Site-Scripting Proof of Concept
vulnerability-analysisexploitationweb-application-exploitation+3
2vor 4 Monaten
vBulletin_Routestring-RCE preview

vBulletin_Routestring-RCE

GitHubludy-dev/vbulletin_routestring-rce

PoC-Exploit für CVE-2019-16759, das Remote-Code-Ausführung auf vBulletin 5.0.0–5.6.2 über eine bösartige POST-Anfrage aufgrund eines…
payload-generationvulnerability-analysisexploitation+2
1vor 6 Jahren
Oracle-WebLogic-CVE-2017-10271-master preview

Oracle-WebLogic-CVE-2017-10271-master

GitHublonehand/oracle-weblogic-cve-2017-10271-master

Exploit für Oracle WebLogic CVE-2017-10271 (wls-wsat RCE-Bypass) mit PoC-Skripten für Remote-Befehlsausführung und Erhalt einer Cmd-Shell auf…

vulnerability-analysisexploitationweb-application-exploitation+3
1vor 8 Jahren
CVE-2019-1221 preview

CVE-2019-1221

GitHubedxsh/cve-2019-1221

Proof-of-Concept-Exploit für CVE-2019-1221, der auf Internet Explorer 11 32-Bit unter Windows 10 x64 bis RS5 abzielt, unter Verwendung von…

payload-generationvulnerability-analysisexploitation+1
1vor 5 Jahren
poc-CVE-2026-64638- preview

poc-CVE-2026-64638-

GitHubmohwahyudi/poc-cve-2026-64638-

PoC-Exploit-Kette für WordPress-Pre-Auth-XSS zu RCE über DOM-Clobbering, REST-JSONP/SOME und Plugin-Upload, mit Docker-Lab-Verifizierung und…

phishing-toolspayload-generationvulnerability-analysis+5
vor 3 Monaten
CVE-2026-63030-CVE-2026-60137 preview

CVE-2026-63030-CVE-2026-60137

GitHubgiangdurian/cve-2026-63030-cve-2026-60137

Pre-auth RCE-Exploit für WordPress (CVE-2026-63030 + CVE-2026-60137), das Routenverwirrung und SQL-Injection zu vollem Shell-Zugriff verknüpft.…

vulnerability-analysisexploitationweb-application-exploitation+4
vor 3 Monaten
CVE-2023-42793 preview

CVE-2023-42793

GitHubflojboj/cve-2023-42793

TeamCity CVE-2023-42793 RCE (Remotecodeausführung)
vulnerability-analysisexploitationweb-application-exploitation+3
vor 2 Jahren
CVE-2023-44765_ConcreteCMS-Stored-XSS---Associations preview

CVE-2023-44765_ConcreteCMS-Stored-XSS---Associations

GitHubsromanhu/cve-2023-44765_concretecms-stored-xss---associations

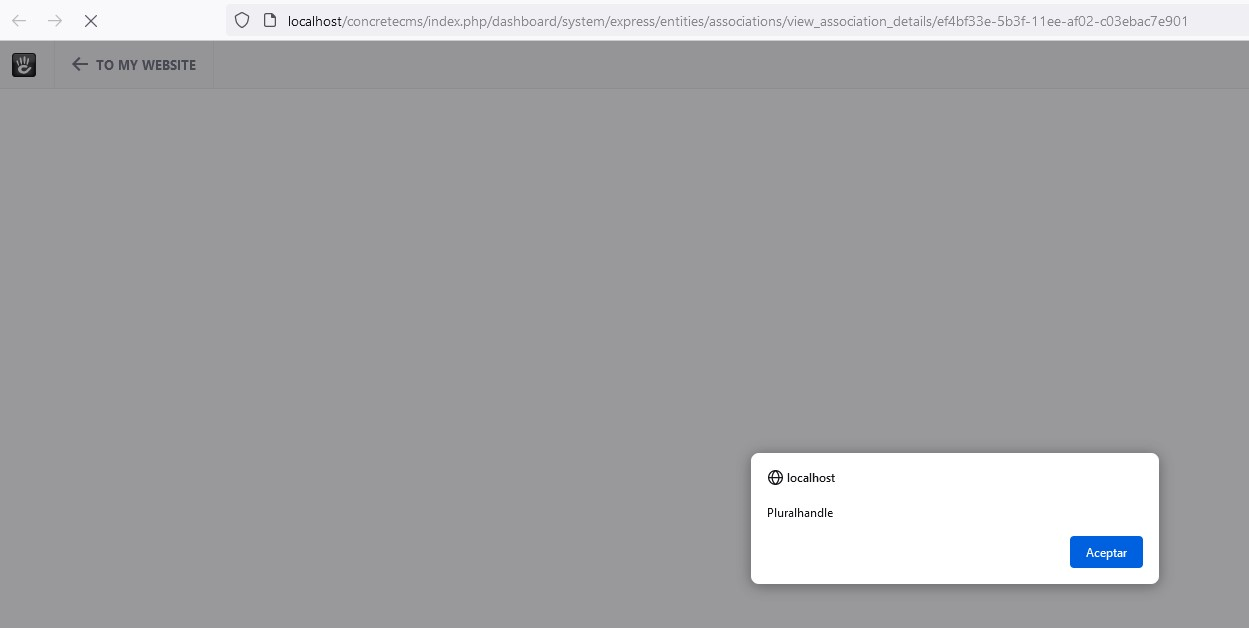
Eine Cross-Site-Scripting-Schwachstelle in ConcreteCMS v.9.2.1 ermöglicht es einem lokalen Angreifer, über ein manipuliertes Skript beliebigen Code…

vulnerability-analysiscode-analysisexploitation+3
vor 3 Jahren
Camera-Dahua-Research-l-h-ng-CVE-2021-33044 preview

Camera-Dahua-Research-l-h-ng-CVE-2021-33044

GitHublitndat/camera-dahua-research-l-h-ng-cve-2021-33044

# DAHUA_AUTH-BYPASS-CVE-2021-33044
authentication-authorizationiot-securityvulnerability-analysis+5
vor 4 Monaten
CVE-2026-22557-Path-Traversal-Ubiquti-UniFi preview

CVE-2026-22557-Path-Traversal-Ubiquti-UniFi

GitHubgagaltotal/cve-2026-22557-path-traversal-ubiquti-unifi

CVE-2026-22557 Pfadüberquerung Ubiquti UniFi Network Application
vulnerability-analysisexploitationweb-application-exploitation+3
1vor 4 Monaten
CVE-2025-6220 preview

CVE-2025-6220

GitHubd0n601/cve-2025-6220

Ultimate Addons für Contact Form 7 <= 3.5.12 - Authentifiziert (Administrator+) Beliebiger Datei-Upload über 'save_options'

payload-generationvulnerability-analysiscode-analysis+3
vor 1 Jahr
cve-2025-29927-lab preview

cve-2025-29927-lab

GitHubswapnildeshpande/cve-2025-29927-lab

Reproduktionslabor für CVE-2025-29927 — Next.js Middleware Autorisierungsumgehung (CVSS 9.1)

vulnerability-analysisweb-application-exploitationpenetration-testing+3
vor 5 Monaten
Zurück1…363738…100Weiter








