#1
Tools und Bibliotheken zur Automatisierung von Sicherheitsaufgaben, Workflows und zur Entwicklung benutzerdefinierter Tools.
Kitploit empfohlen

 brutelogic/unkover
Bash-Tester für die Umgehung von 403/401-Zugriffsbeschränkungen, der eine URL mit Header-Spoofing, Methodenmanipulation, Pfadnormalisierung und…
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.

 roccoammon/active-directory-health-check
PowerShell GUI tool that runs 54 best-practice health and security checks against Active Directory, flagging Kerberoasting, DCSync, delegation and…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
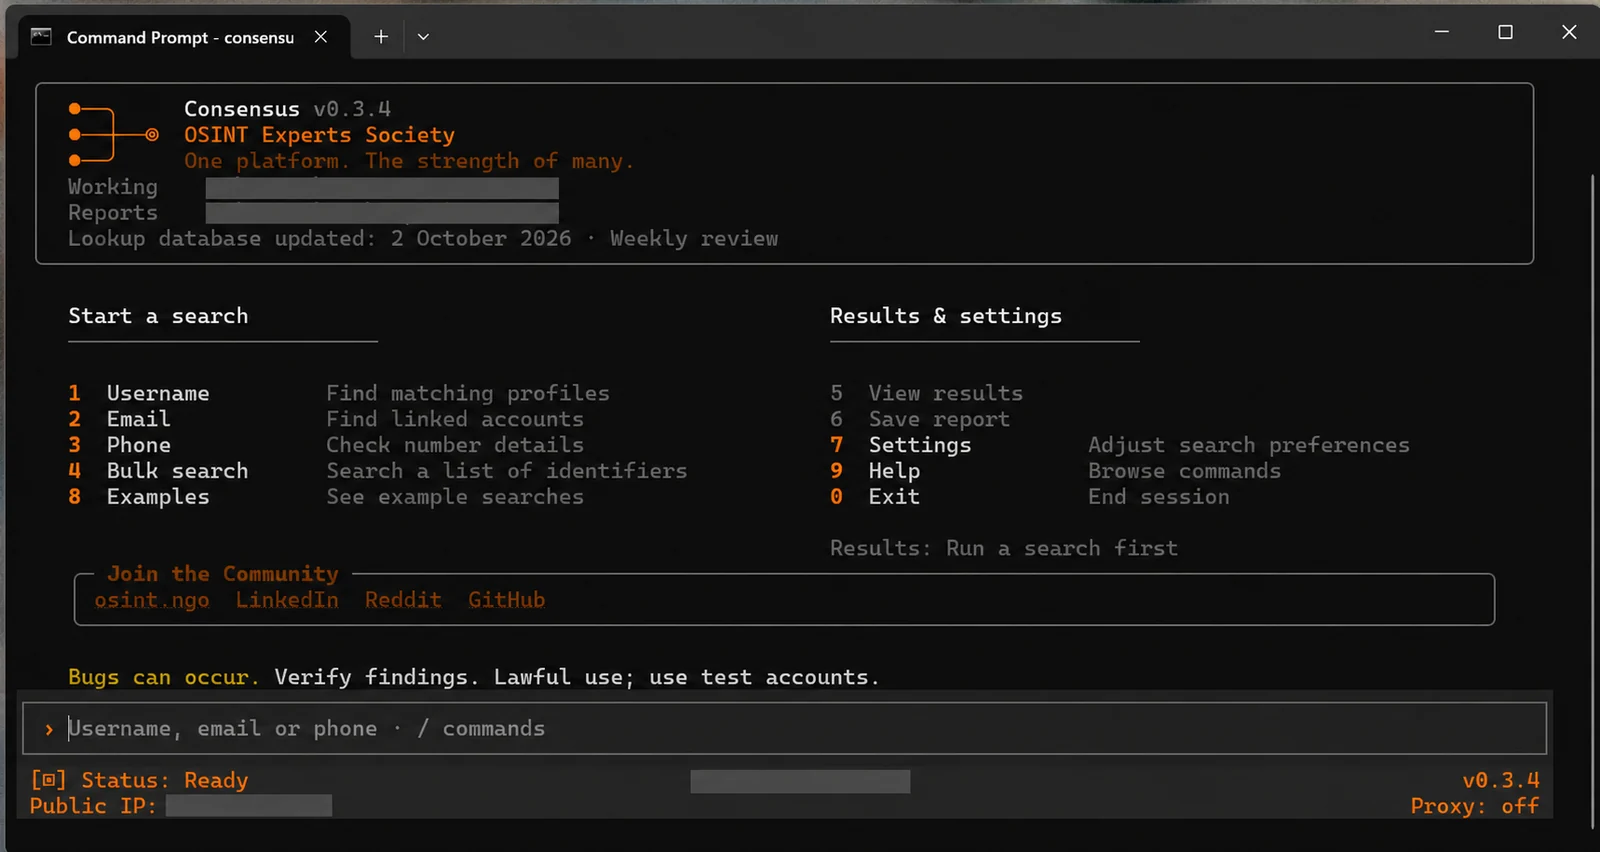 osint-experts-society/consensus-osint
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…
 gmh5225/logineo-scraper
Schnelles Skript zum Scrapen persönlicher Informationen aus Logineo-Instanzen
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
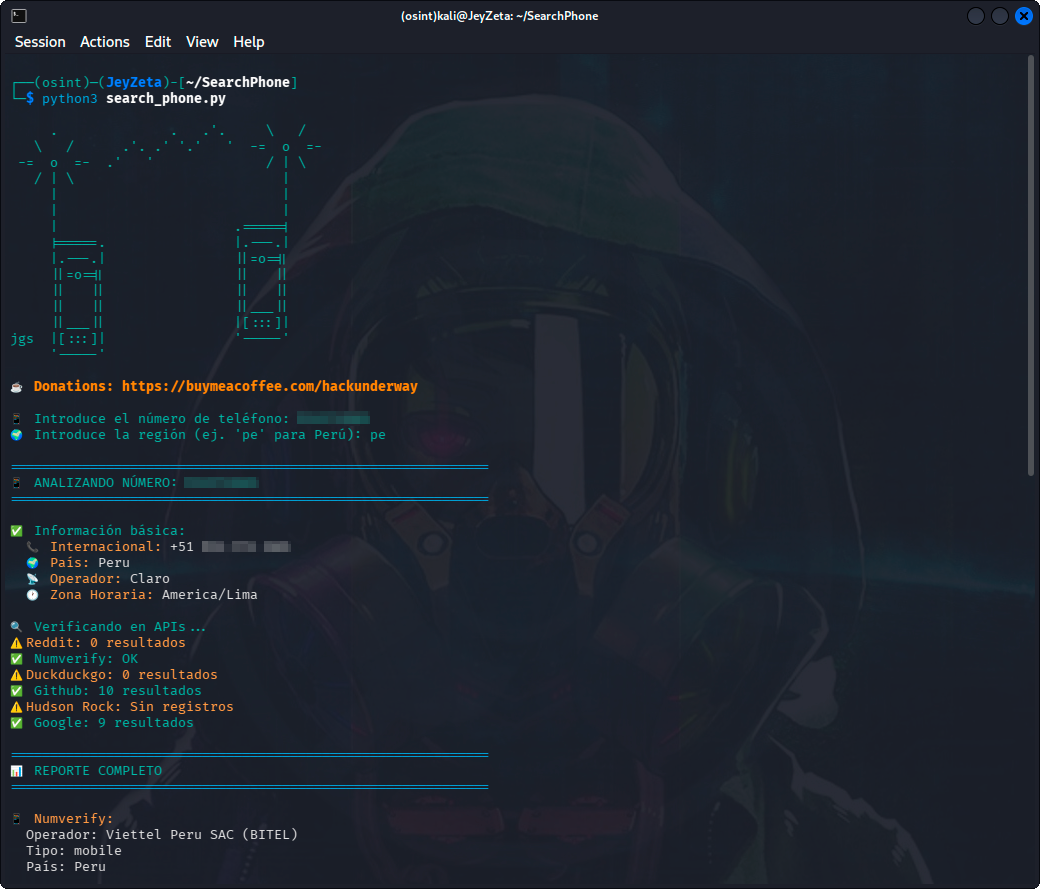 hackunderway/searchphone
Telefonnummern-OSINT-Toolkit mit Multi-API-Suche (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock Infostealer Intelligence und…
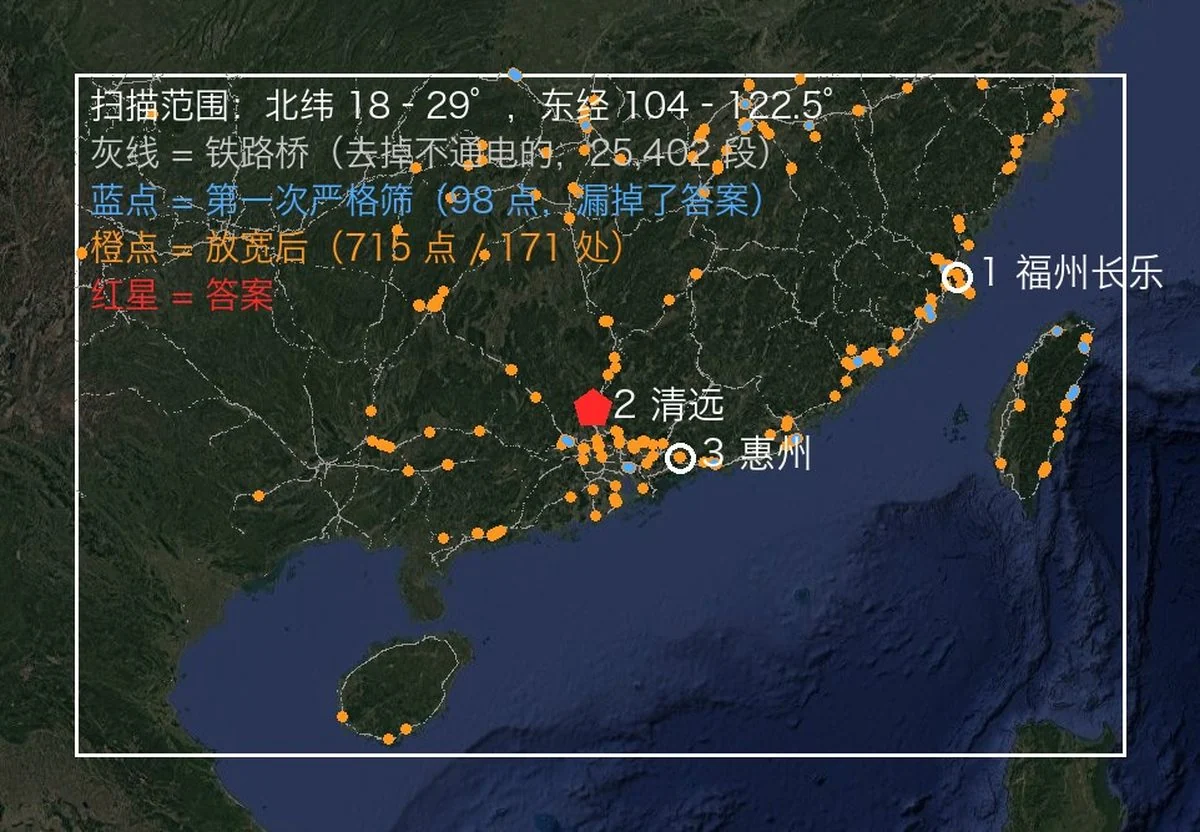 oldcircle/geo-sleuth
Ein Agent-Skill, der herausfindet, wo ein Foto aufgenommen wurde — OpenStreetMap-Geometrie, Höhenprofile, Satellitenbilder und Street View — und…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 luftwaffe66/gobfuscator
Verschleiert Go-Quellcode durch AES-256-String-Verschlüsselung mit Laufzeitentschlüsselung, Umbenennung von Bezeichnern und Entfernung von…
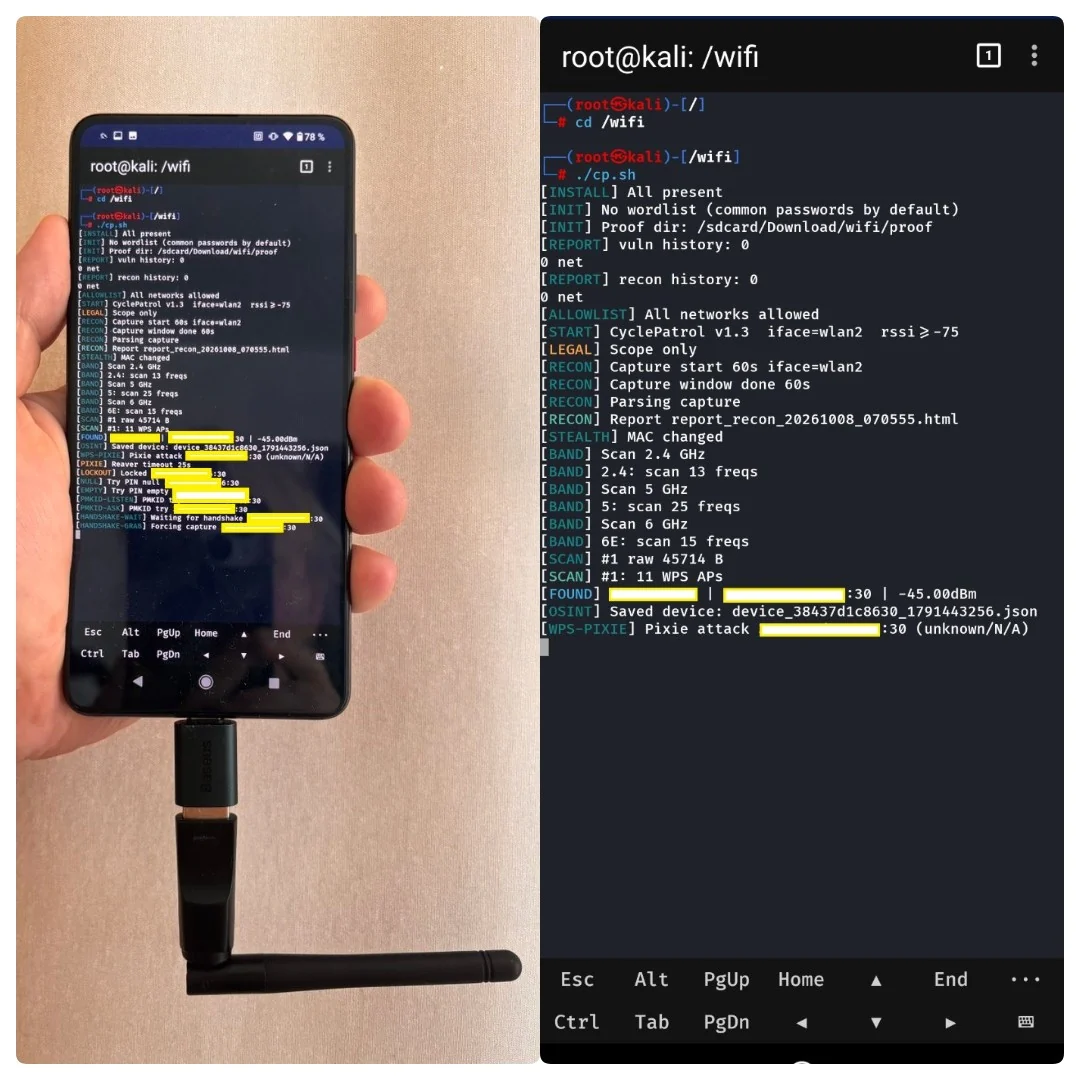 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports. (re-invented wifi WarDriving)
 lifting-bits/sleigh
CMake-Build von Ghidras SLEIGH-Prozessorspezifikationsbibliothek, die eigenständige Disassemblierungs- und P-Code-Lifting-Engines für…
 githubsecuritylab/seclab-taskflow-agent
MCP-fähiges Multi-Agenten-Framework für deklarative, YAML-gesteuerte agentische Workflows, verwendet für KI-gestütztes Code-Auditing,…
 sleepingbag945/dddd
Batch-Tool zur Asset-Erfassung und Schwachstellen-Scanning für Red Teams. Zieht Ziele von Hunter, Fofa und Quake, führt Fingerprinting,…
 clausing/scripts
Sammlung von Python- und Perl-Skripten für digitale Forensik, Incident Response und Netzwerkanalyse, einschließlich Hash-Signatur-Tools und…