
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Kategorien

Datenbanksicherheit

Tools für Datenbankbewertung, SQL-Injection-Tests, Audit, Verschlüsselung und Aktivitätsüberwachung.

Kitploit empfohlen
Top-Tools

10 ausgewählt
sqlmap preview#1

sqlmap

GitHubsqlmapproject/sqlmap
38.2kvor 5h 23m
openvas-scanner preview#2

openvas-scanner

GitHubgreenbone/openvas-scanner
4.8kvor 3 Tagen
nuclei preview#3

nuclei

GitHubprojectdiscovery/nuclei
30.4kvor 3h 22m
metasploit-framework preview#4

metasploit-framework

GitHubrapid7/metasploit-framework
38.8kvor 2 Tagen
nmap preview#5

nmap

GitHubnmap/nmap
13.3kvor 15h 23m
zaproxy preview#6

zaproxy

GitHubzaproxy/zaproxy
15.6kvor 6h 19m
wapiti preview#7

wapiti

GitHubwapiti-scanner/wapiti
1.9kvor 29 Tagen
semgrep preview#8

semgrep

GitHubsemgrep/semgrep
16.2kvor 4 Tagen
trivy preview#9

trivy

GitHubaquasecurity/trivy
37.4kvor 7h 28m
wazuh preview#10

wazuh

GitHubwazuh/wazuh
16.5kvor 21h 16m
NeuesteRelevanzBeliebtesteKürzlich aktualisiert
650 Ergebnisse
CVE-2026-57588-Nessus-XML-Import-SQL-Injection-PoC preview

CVE-2026-57588-Nessus-XML-Import-SQL-Injection-PoC

GitHubcerberusmrxi/cve-2026-57588-nessus-xml-import-sql-injection-poc

PoC für CVE-2026-57588 - SQL-Injection im XML-Import von Nessus 10.12.0. Generiert bösartige .nessus-Dateien, um Datenbanken aufzulisten,…

payload-generationvulnerability-analysisexploitation+7
1vor 3 Monaten
CVE-2019-20933 preview

CVE-2019-20933

GitHubhydragyrum/cve-2019-20933

Proof-of-Concept-Exploit-Client für die Authentifizierungsumgehung von InfluxDB (CVE-2019-20933). Führt beliebige Abfragen gegen anfällige…

authentication-authorizationvulnerability-analysisexploitation+2
2vor 5 Jahren
CVE-2026-37149 preview

CVE-2026-37149

GitHubpateldhyeyit/cve-2026-37149

CVE-2026-37149 - SQL-Injection-Schwachstelle im Parameter scost von search_products.php in GROCERY-STORE-MANAGEMENT-SYSTEM-USING-PHP-AND-MYSQL-PHPMYAD…
vulnerability-analysisweb-application-exploitationinformation-gathering+3
2vor 4 Monaten
CVE-2025-64459-Poc preview

CVE-2025-64459-Poc

GitHub0xcyberstan/cve-2025-64459-poc

Schwachstelle: SQL Injection über QuerySet und das Entpacken von Schlüsselwortargumenten von Q(). CVE-ID: CVE-2025-64459 Schweregrad: Kritisch (CVSS…
vulnerability-analysisexploitationweb-application-exploitation+3
2vor 11 Monaten
CVE-2026-77635 preview

CVE-2026-77635

GitHubabraxas/cve-2026-77635

Disclosure pack and Python PoC for CVE-2026-77635, an unauthenticated SQL injection in CakePHP's jsonValue() with PostgresDriver, including a…
vulnerability-scannersvulnerability-analysisexploitation+5
vor 4 Tagen
CVE-2016-2386 preview

CVE-2016-2386

GitHubmurataydemir/cve-2016-2386

[CVE-2016-2386] SAP NetWeaver AS JAVA UDDI Component SQL-Injection
vulnerability-analysisexploitationweb-application-exploitation+3
2vor 6 Jahren
CVE-2025-14847-mongobleed preview

CVE-2025-14847-mongobleed

GitHubshokribardiya/cve-2025-14847-mongobleed

CVE-2025-14847 mongobleed Python-Datei
vulnerability-analysisexploitationpapers-research+2
2vor 4 Monaten
CVE-2021-42670 preview

CVE-2021-42670

GitHub0xdeku/cve-2021-42670

CVE-2021-42670 – SQL-Injection-Schwachstelle im Online-Portal-System der Ingenieure.
vulnerability-analysisexploitationweb-application-exploitation+3
2vor 4 Jahren
CVE-2026-34220 preview

CVE-2026-34220

GitHubeqstlab/cve-2026-34220

SQL-Injection-Schwachstelle in MikroORM

vulnerability-analysisexploitationweb-application-exploitation+3
1vor 2 Monaten
Discuz-X5.0-Authentication-Bypass-Exploit-Framework preview

Discuz-X5.0-Authentication-Bypass-Exploit-Framework

GitHubcerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework

Discuz! X5.0 Exploit-Framework zur Authentifizierungsumgehung (CVE-2026-49952) - Kritische Schwachstelle, die nicht authentifizierten Zugriff auf…
authentication-authorizationexploit-frameworksvulnerability-analysis+4
1vor 3 Monaten
CVE-2026-22003-Redis-Lua-Sandbox-Escape-via-debug.sethook- preview

CVE-2026-22003-Redis-Lua-Sandbox-Escape-via-debug.sethook-

GitHubgeorge0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-

Proof-of-Concept-Exploit für CVE-2026-22003, der die Redis-Lua-Sandbox-Umgehung über debug.sethook demonstriert, um beliebige Systembefehle…

privilege-escalationvulnerability-analysisexploitation+2
1vor 3 Monaten
CVE-2023-49954.github.io preview

CVE-2023-49954.github.io

GitHubcve-2023-49954/cve-2023-49954.github.io

SQL Injection in der 3CX CRM Integration
vulnerability-analysisweb-application-exploitationapi-security-testing+3
2vor 2 Jahren
CVE-2026-26980 preview

CVE-2026-26980

GitHubyym8538/cve-2026-26980

Python-PoC und Docker-Lab, das unauthifizierte SQL-Injection im Slug-Filter der Content-API von TryGhost Ghost CMS demonstriert und Datenbankwerte…
vulnerability-analysisexploitationweb-application-exploitation+5
1vor 2 Monaten
CVE-2026-30951 preview

CVE-2026-30951

GitHubeqstlab/cve-2026-30951

Sequelize JSON Cast SQL-Injektion
static-analysisvulnerability-analysiscode-analysis+3
1vor 2 Monaten
CVE-2026-69084-PoC preview

CVE-2026-69084-PoC

GitHubboreas37/cve-2026-69084-poc

CVE-2026-69084/69085 — SiYuan beliebige SQL-Ausführung über searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verifiziert auf v3.7.2, zurückgewiesen auf…
vulnerability-analysisexploitationweb-application-exploitation+3
1vor 2 Monaten
CVE-2024-30896 preview

CVE-2024-30896

GitHubxenom0rph97/cve-2024-30896

Proof-of-Concept-Exploit für CVE-2024-30896, eine Privilegieneskalations-Schwachstelle in InfluxDB, die es Inhabern von allAccess-Tokens ermöglicht,…
authentication-authorizationprivilege-escalationvulnerability-analysis+3
2vor 1 Jahr
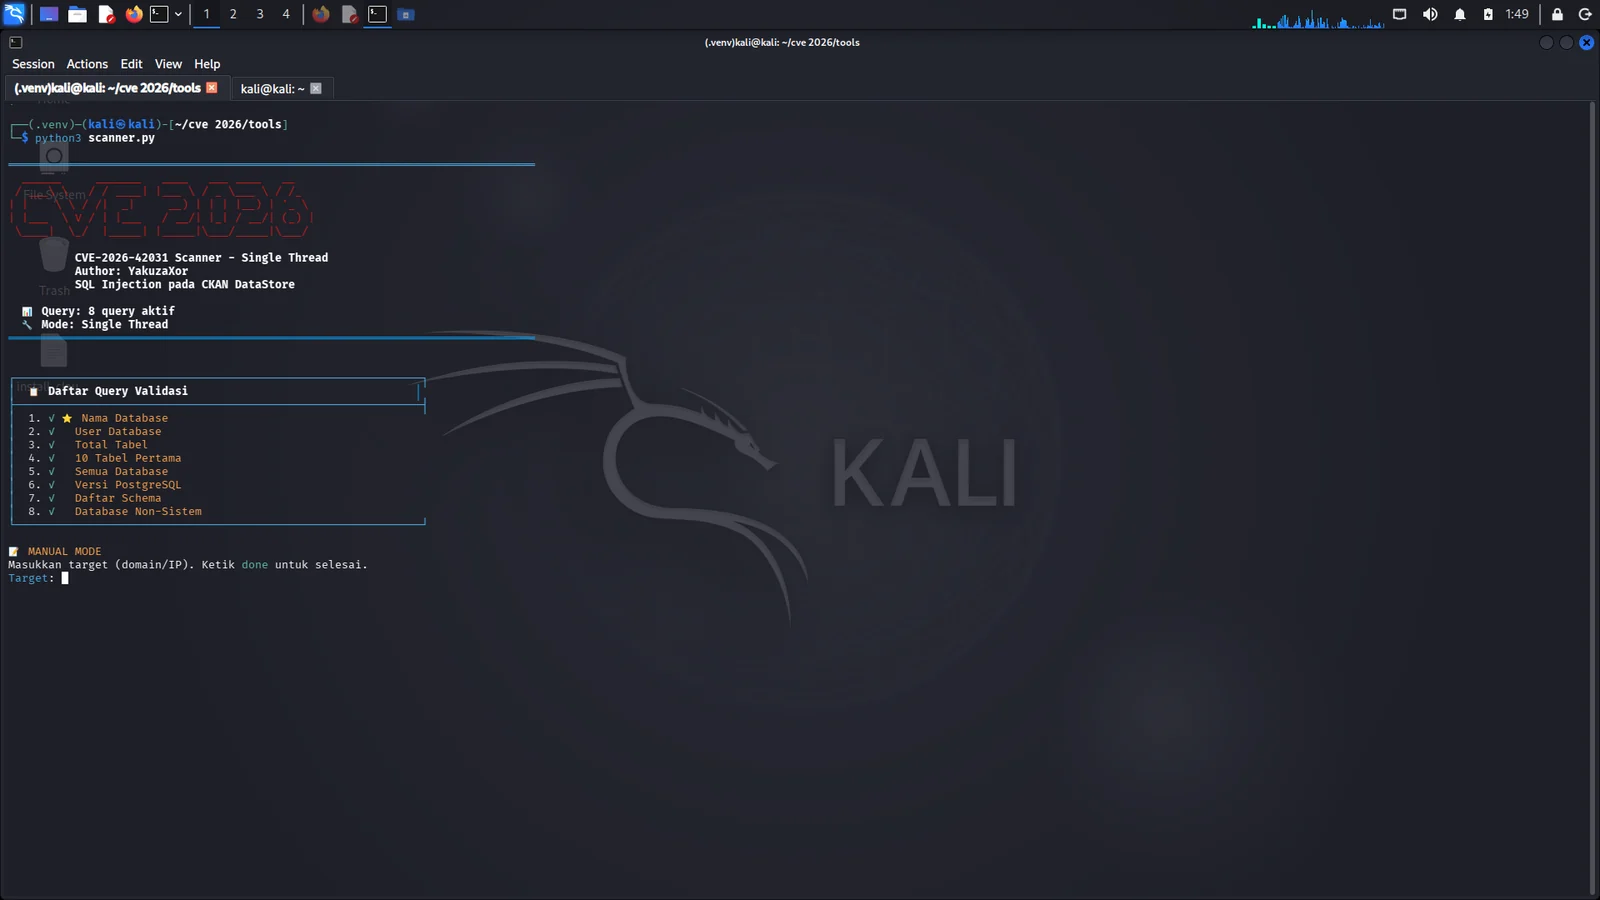
CVE-2026-42031-SQL-Injection-Scanner preview

CVE-2026-42031-SQL-Injection-Scanner

GitHubddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner

Automatisierter SQL-Injection-Scanner für CKAN DataStore, der CVE-2026-42031 erkennt und validiert, mit Multi-Target-Scanning, Daten-Dumping und…
vulnerability-scannersexploitationinformation-gathering+3
1vor 1 Monat
CVE-2026-25243 preview

CVE-2026-25243

GitHubcaptain-woof/cve-2026-25243

Stable POC für CVE-2026-25243 (Redis RESTORE double-free -> Remote Code Execution)

vulnerability-analysisexploitationpost-exploitation+4
1vor 2 Monaten
Zurück1…181920…37Weiter








