
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Authentifizierung & Autorisierung — Seite 26 | Kitploit
Kategorien

Authentifizierung & Autorisierung

Tools zum Testen und Implementieren von Authentifizierungsmechanismen (z.B. MFA, SSO) und Autorisierungsrichtlinien.

Kitploit empfohlen
Top-Tools

10 ausgewählt
keycloak preview#1

keycloak

GitHubkeycloak/keycloak
37.7kvor 9h 48m
hydra preview#2

hydra

GitHubory/hydra
17.6kvor 3 Monaten
kratos preview#3

kratos

GitHubory/kratos
13.8kvor 3 Monaten
authentik preview#4

authentik

GitHubgoauthentik/authentik
26.2kvor 8h 11m
zitadel preview#5

zitadel

GitHubzitadel/zitadel
15.5kvor 1 Tag
dex preview#6

dex

GitHubdexidp/dex
11.2kvor 1 Tag
authelia preview#7

authelia

GitHubauthelia/authelia
28.5kvor 1 Stunde
oauth2-proxy preview#8

oauth2-proxy

GitHuboauth2-proxy/oauth2-proxy
15.3kvor 1 Monat
pomerium preview#9

pomerium

GitHubpomerium/pomerium
5.1kvor 7h 23m
opa preview#10

opa

GitHubopen-policy-agent/opa
12.4kvor 17h 50m
NeuesteRelevanzBeliebtesteKürzlich aktualisiert
864 Ergebnisse
CVE-2026-66750-Insufficient-Access-Controls-Allow-for-Unauthorized-File-Downloads-Let-s-Chat- preview

CVE-2026-66750-Insufficient-Access-Controls-Allow-for-Unauthorized-File-Downloads-Let-s-Chat-

GitHubtheopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-

Sicherheitshinweis: Unzureichende Zugriffskontrollen ermöglichen nicht autorisierte Dateidownloads (Let's Chat)
authentication-authorizationvulnerability-analysisweb-security+2
vor 3 Monaten
CVE-2025-65856 preview

CVE-2025-65856

GitHubluismirandaacebedo/cve-2025-65856

Xiongmai XM530 IP Kamera ONVIF Vollständige Authentifizierungsumgehung
authentication-authorizationiot-securityvulnerability-analysis+2
3vor 10 Monaten
milvus-auth-audit preview

milvus-auth-audit

GitHubqianlijaingshan/milvus-auth-audit

Milvus-Authentifizierungs-Sicherheitsprüfungsskript: CVE-2025-64513 (sourceid-Backdoor) / CVE-2026-26190 (/expr schwaches Token) / interner Port 53100
authentication-authorizationvulnerability-scannersexploitation+4
vor 3 Monaten
CVE-2025-32433-PoC-Analysis preview

CVE-2025-32433-PoC-Analysis

GitHubliam-worsley/cve-2025-32433-poc-analysis

Dies ist eine Analyse zu CVE-2025-32433 (Sicherheitslücke in Erlang OTP SSH). Ich habe keinen Teil des Codes geschrieben, ich habe lediglich…
authentication-authorizationvulnerability-analysisexploitation+4
vor 2 Monaten
CVE-2026-8239 preview

CVE-2026-8239

GitHubaj2108/cve-2026-8239

Sicherheitsbericht über eine IDOR in Concrete CMS, die Konversationsbewertungen durch fehlende Autorisierung am get_rating-Endpunkt offenlegt, mit…
authentication-authorizationvulnerability-analysisweb-application-exploitation+3
vor 3 Monaten
CVE-2026-66751-Insufficient-Access-Controls-Allow-for-Unauthorized-Room-Deletion-Let-s-Chat- preview

CVE-2026-66751-Insufficient-Access-Controls-Allow-for-Unauthorized-Room-Deletion-Let-s-Chat-

GitHubtheopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-

Sicherheitshinweis: Unzureichende Zugriffskontrollen ermöglichen das unbefugte Löschen von Räumen (Let's Chat)
authentication-authorizationvulnerability-analysiscode-analysis+2
vor 3 Monaten
CVE-2026-8347 preview

CVE-2026-8347

GitHubaj2108/cve-2026-8347

CVE-2026-8347 ist eine Schwachstelle durch Insecure Direct Object Reference (IDOR) in Kombination mit einer falschen Autorisierungsebene in Concrete…
authentication-authorizationvulnerability-analysisweb-application-exploitation+1
vor 3 Monaten
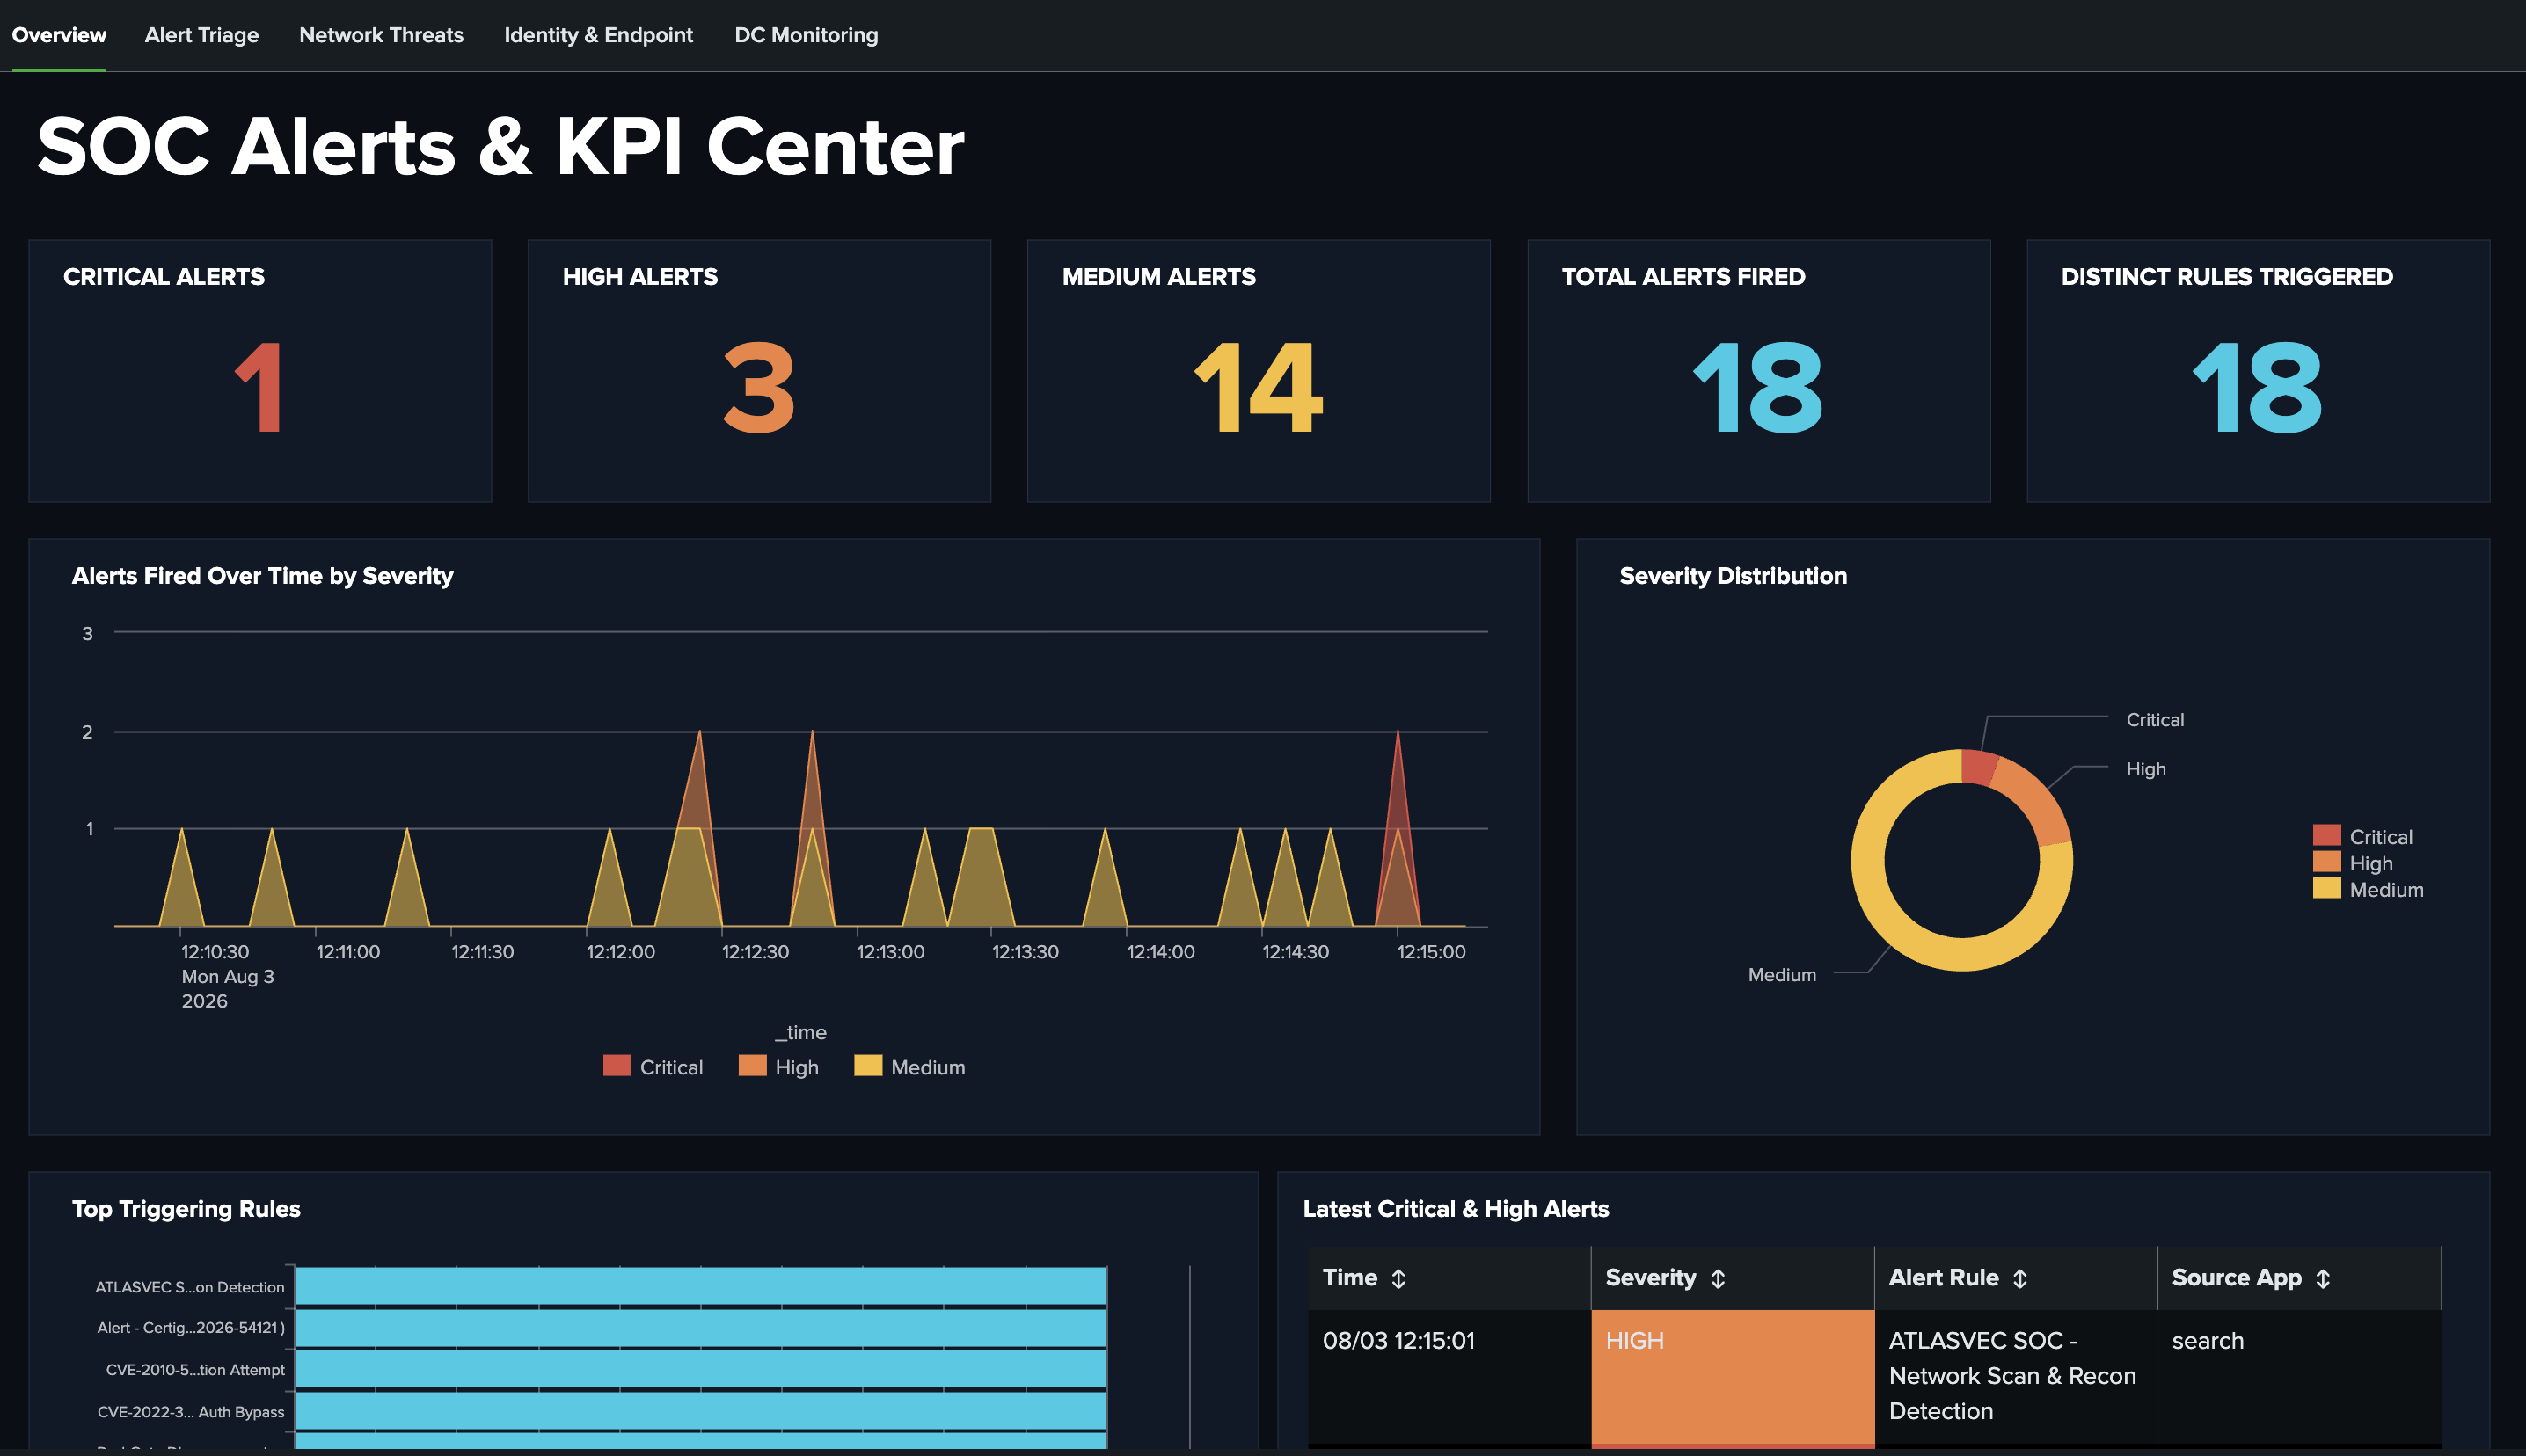
Certighost-CVE-2026-54121 preview

Certighost-CVE-2026-54121

GitHubatlasvector/certighost-cve-2026-54121

Splunk-Erkennungsbericht für CVE-2026-54121 (CertiGhost): Missbrauch der AD-CS-Zertifikatsverfolgung, der zur vollständigen Domänenkompromittierung…
authentication-authorizationdefensive-toolsvulnerability-analysis+3
vor 2 Monaten
wordpress-cve-2024-10924-exploit preview

wordpress-cve-2024-10924-exploit

GitHubh8su/wordpress-cve-2024-10924-exploit

Ein Proof-of-Concept (PoC) Exploit für CVE-2024-10924, eine Schwachstelle im Really Simple SSL WordPress-Plugin, die das Umgehen der…
authentication-authorizationvulnerability-analysisexploitation+4
2vor 1 Jahr
Zabbix-CVE-2022-23131 preview

Zabbix-CVE-2022-23131

GitHubvulnmachines/zabbix-cve-2022-23131

Zabbix-SAML-Bypass: CVE-2022-23131
authentication-authorizationvulnerability-analysisexploitation+2
2vor 4 Jahren
CVE-2025-29972 preview

CVE-2025-29972

GitHubthemehackers/cve-2025-29972

CVE-2025-29927 ist eine kritische Sicherheitslücke, die Next.js betrifft, ein beliebtes React-Framework zur Entwicklung von…

authentication-authorizationvulnerability-analysisexploitation+2
2vor 1 Jahr
secdim-assurance-drift-challenge preview

secdim-assurance-drift-challenge

GitHubfranklincg/secdim-assurance-drift-challenge

SecDim Challenge Builder Repro inspiriert von CVE-2026-88861: AAL1-MFA-Bypass an der privilegierten Credential-Grenze
authentication-authorizationvulnerability-analysisweb-security+5
vor 1 Monat
CVE-2022-23131 preview

CVE-2022-23131

GitHub1mxml/cve-2022-23131

Nutzt die Umgehung der Zabbix-SAML-SSO-Authentifizierung (CVE-2022-23131) aus und enthält eine FOFA-Abfrage, um verwundbare Zabbix-Instanzen zu…

authentication-authorizationvulnerability-analysisexploitation+2
3vor 4 Jahren
The Vault by Focused Hunts preview

The Vault by Focused Hunts

GitLabfocused.hunts/the.vault

Datenschutzorientierter Passwortmanager mit lokalem Speicher und Bring-Your-Own-Cloud-Synchronisation über Google Drive, Microsoft OneDrive und…
authentication-authorizationpassword-crackingencryption-decryption-tools+3
vor 2 Monaten
wp-allowed-hosts preview

wp-allowed-hosts

GitHubalash3al/wp-allowed-hosts

Ein Plugin, das Ihre WP-Site vor der Sicherheitslücke CVE-2017-8295 schützt.
authentication-authorizationdefensive-toolsvulnerability-analysis+2
2vor 9 Jahren
wordpress-skelersecurity-core-security-CVE-2026-63030 preview

wordpress-skelersecurity-core-security-CVE-2026-63030

GitHubskelersecurity/wordpress-skelersecurity-core-security-cve-2026-63030

Temporäres WordPress-Plugin, das Authentifizierung für den Core REST Batch API-Endpunkt erfordert, um die wp2shell-Schwachstellenkette…

authentication-authorizationdefensive-toolsvulnerability-analysis+3
vor 3 Monaten
CVE-2026-50751---Check-Point-IKEv1-Authentication-Bypass-Exploit preview

CVE-2026-50751---Check-Point-IKEv1-Authentication-Bypass-Exploit

GitHubfevar54/cve-2026-50751---check-point-ikev1-authentication-bypass-exploit

Schwachstelle: Logikschwäche im Remote Access und Mobile Access
authentication-authorizationvulnerability-scannersvulnerability-analysis+3
1vor 4 Monaten
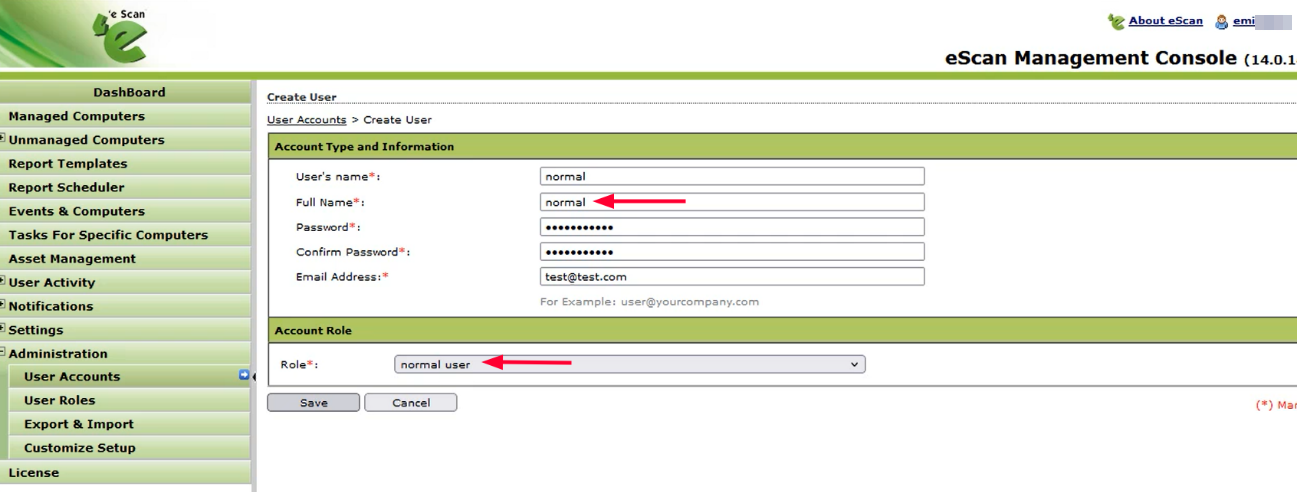
CVE-2023-33730 preview

CVE-2023-33730

GitHubsahiloj/cve-2023-33730

eScan Management Console Version 14.0.1400.2281 enthält eine Rechteausweitung über die `GetUserCurrentPwd`-Funktion, die es Angreifern ermöglicht,…


authentication-authorizationprivilege-escalationreconnaissance+8
1vor 8 Monaten
Zurück1…252627…48Weiter







