 teler-sh/teler-waf
teler-waf هو وسيط HTTP مكتوب بلغة Go يحمي خدمات الويب المحلية من تهديدات OWASP Top 10، والثغرات المعروفة، والجهات الخبيثة، والبوتنتات، والزواحف غير المرغوب فيها، وهجمات القوة العمياء.


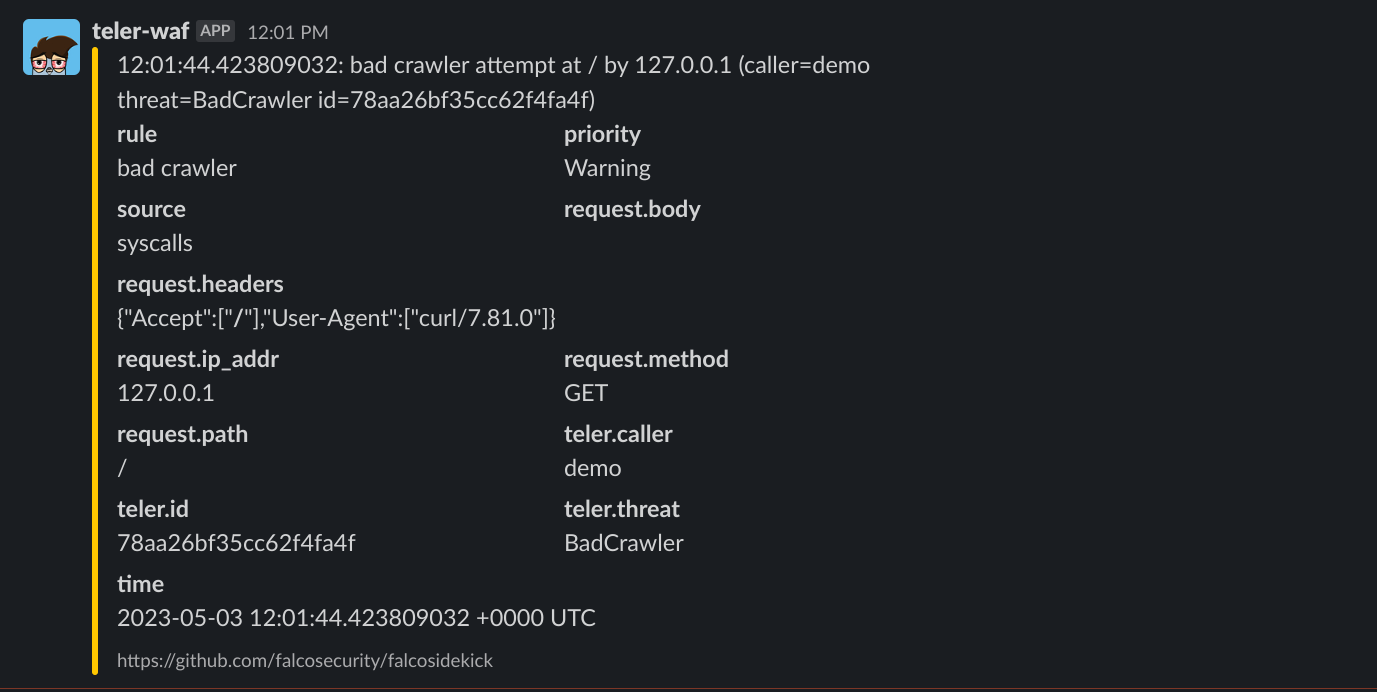
teler-waf هو حل أمني شامل لتطبيقات الويب المبنية بلغة Go. يعمل كوسيط HTTP، ويوفر واجهة سهلة الاستخدام لدمج وظائف نظام كشف التسلل (IDS) مع teler IDS في تطبيقات Go الحالية. باستخدام teler-waf، يمكنك المساعدة في الحماية من مجموعة متنوعة من الهجمات المستندة إلى الويب، مثل البرمجة النصية عبر المواقع (XSS) وحقن SQL.
تأتي الحزمة مع معالج net/http.Handler قياسي، مما يسهل دمجها في توجيه التطبيق الخاص بك. عندما يقدم العميل طلبًا إلى مسار محمي بواسطة teler-waf، يتم أولاً فحص الطلب مقابل teler IDS للكشف عن أنماط ضارة معروفة. إذا لم يتم اكتشاف أي أنماط ضارة، يتم تمرير الطلب لمزيد من المعالجة.
بالإضافة إلى توفير الحماية ضد الهجمات المستندة إلى الويب، يمكن أن يساعد teler-waf أيضًا في تحسين الأمان والنزاهة الكلية لتطبيقك. وهو قابل للتكوين بدرجة كبيرة، مما يسمح لك بتخصيصه ليناسب الاحتياجات المحددة لتطبيقك.
انظر أيضًا:
يقدم teler-waf مجموعة من الميزات القوية المصممة لتعزيز أمان تطبيقات الويب بلغة Go:
بشكل عام، يوفر teler-waf حلاً أمنيًا شاملاً لتطبيقات الويب بلغة Go، مما يساعد في الحماية من الهجمات المستندة إلى الويب وتحسين الأمان والنزاهة الكلية لتطبيقك.
المتطلبات الأساسية:
لتثبيت teler-waf في تطبيق Go الخاص بك، قم بتشغيل الأمر التالي لتنزيل وتثبيت حزمة teler-waf:```console go get github.com/teler-sh/teler-waf
## الاستخدام

> [!WARNING]
> **إشعار إهمال**: سيتم إهمال استثناءات التهديدات (`Excludes`) في الإصدار القادم (**v2**). انظر [#73](https://github.com/teler-sh/teler-waf/discussions/73) & [#64](https://github.com/teler-sh/teler-waf/issues/64).

فيما يلي مثال على كيفية استخدام teler-waf في تطبيق Go:

1. استيراد حزمة teler-waf في كود Go الخاص بك:```go
import "github.com/teler-sh/teler-waf"
New لإنشاء نسخة جديدة من النوع Teler. تأخذ هذه الدالة مجموعة متنوعة من المعاملات الاختيارية التي يمكن استخدامها لتكوين teler-waf بما يتناسب مع الاحتياجات المحددة لتطبيقك.```go
waf := teler.New()3. استخدم طريقة `Handler` من مثيل `Teler` لإنشاء معالج `net/http.Handler`. يمكن بعد ذلك استخدام هذا المعالج في توجيه HTTP لتطبيق إجراءات الأمان الخاصة بـ teler-waf على مسارات محددة.```go
handler := waf.Handler(http.HandlerFunc(yourHandlerFunc))
handler في توجيه HTTP لتطبيق إجراءات أمان teler-waf على مسارات محددة.```go
http.Handle("/path", handler)ذلك كل شيء! لقد قمت بتكوين teler-waf في تطبيق Go الخاص بك.
**الخيارات:**
للاطلاع على قائمة الخيارات المتاحة لتخصيص teler-waf، راجع بنية [`teler.Options`](https://pkg.go.dev/github.com/teler-sh/teler-waf#Options).
### أمثلة
فيما يلي مثال على كيفية تخصيص الخيارات والقواعد لـ teler-waf:```go
// main.go
package main
import (
"net/http"
"github.com/teler-sh/teler-waf"
"github.com/teler-sh/teler-waf/request"
"github.com/teler-sh/teler-waf/threat"
)
var myHandler = http.HandlerFunc(func(w http.ResponseWriter, r *http.Request) {
// This is the handler function for the route that we want to protect
// with teler-waf's security measures.
w.Write([]byte("hello world"))
})
var rejectHandler = http.HandlerFunc(func(w http.ResponseWriter, r *http.Request) {
// This is the handler function for the route that we want to be rejected
// if the teler-waf's security measures are triggered.
http.Error(w, "Sorry, your request has been denied for security reasons.", http.StatusForbidden)
})
func main() {
// Create a new instance of the Teler type using the New function
// and configure it using the Options struct.
telerMiddleware := teler.New(teler.Options{
// Exclude specific threats from being checked by the teler-waf.
Excludes: []threat.Threat{
threat.BadReferrer,
threat.BadCrawler,
},
// Specify whitelisted URIs (path & query parameters), headers,
// or IP addresses that will always be allowed by the teler-waf
// with DSL expressions.
Whitelists: []string{
`request.Headers matches "(curl|Go-http-client|okhttp)/*" && threat == BadCrawler`,
`request.URI startsWith "/wp-login.php"`,
`request.IP in ["127.0.0.1", "::1", "0.0.0.0"]`,
`request.Headers contains "authorization" && request.Method == "POST"`
},
// Specify file path or glob pattern of custom rule files.
CustomsFromRule: "/path/to/custom/rules/**/*.yaml",
// Specify custom rules for the teler-waf to follow.
Customs: []teler.Rule{
{
// Give the rule a name for easy identification.
Name: "Log4j Attack",
// Specify the logical operator to use when evaluating the rule's conditions.
Condition: "or",
// Specify the conditions that must be met for the rule to trigger.
Rules: []teler.Condition{
{
// Specify the HTTP method that the rule applies to.
Method: request.GET,
// Specify the element of the request that the rule applies to
// (e.g. URI, headers, body).
Element: request.URI,
// Specify the pattern to match against the element of the request.
Pattern: `\$\{.*:\/\/.*\/?\w+?\}`,
},
},
},
{
// Give the rule a name for easy identification.
Name: `Headers Contains "curl" String`,
// Specify the conditions that must be met for the rule to trigger.
Rules: []teler.Condition{
{
// Specify the DSL expression that the rule applies to.
DSL: `request.Headers contains "curl"`,
},
},
},
},
// Specify the file path to use for logging.
LogFile: "/tmp/teler.log",
})
// Set the rejectHandler as the handler for the telerMiddleware.
telerMiddleware.SetHandler(rejectHandler)
// Create a new handler using the handler method of the Teler instance
// and pass in the myHandler function for the route we want to protect.
app := telerMiddleware.Handler(myHandler)
