
Skip to content
KitploitKITPLOIT
أدواتعمليات الاستغلالالمدونة
Log in
إرسال
أدواتعمليات الاستغلالالمدونة
إرسال

أدوات الاختراق واختبار الاختراق والأمن السيبراني لترسانتك الأمنية!

Kitploit هو دليل لأدوات الاختراق والأمن السيبراني واختبار الاختراق. اكتشف آخر تحديثات المشاريع للعثور على الثغرات وتحليل الأنظمة وأتمتة الاختبارات وتعزيز أمنك.

الخلاصاتاتصالالخصوصية© 2026 Kitploit

دليل الأدوات

الفئات

عرض جميع الفئات
Loading categories
OsintCase — An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence. | Kitploit
أدوات/GitHubGitHub/emrekybs/osintcase
Indicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)ForensicsInformation GatheringData RecoveryDigital ForensicsPrivacyThreat IntelligenceCurated Resources
GitHubemrekybs/osintcase

OsintCase

An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

عرض المستودعالموقع الإلكتروني
5120منذ 16 أياملم تتم المراجعة بعد

الأكثر شعبية

عرض الكل →

اكتشف الأدوات الأكثر استخدامًا من قبل مجتمعنا.

استكشف جميع الأدوات

تصفح مجموعتنا من الأدوات

عرض جميع الأدوات →
مشاركة
المحتوى غير متوفر باللغة المطلوبة. عرض النسخة الإنجليزية.

OSINTCase

OSINT Case

Based on OSINTMapper by Geistnigma.

This project is a modified and extended version of OSINTMapper with additional features and changes focused on investigation case management, intelligence analysis and evidence handling.

A browser-based OSINT investigation and case mapping tool.

Organize subjects, identifiers, relationships, locations, timelines and evidence in a single case file.
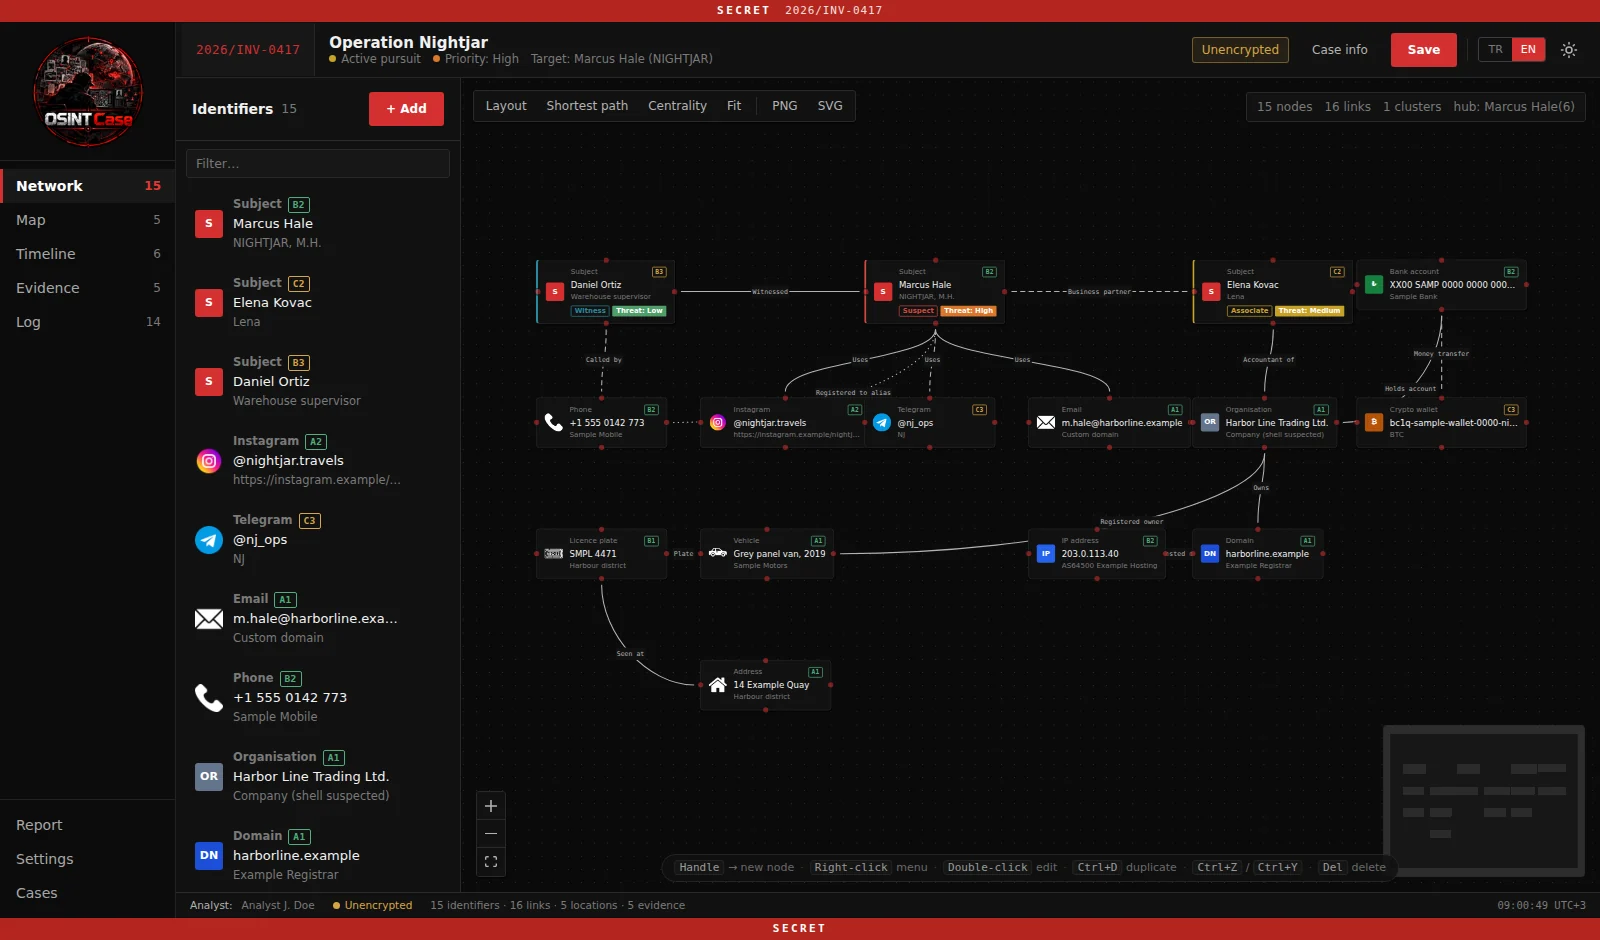
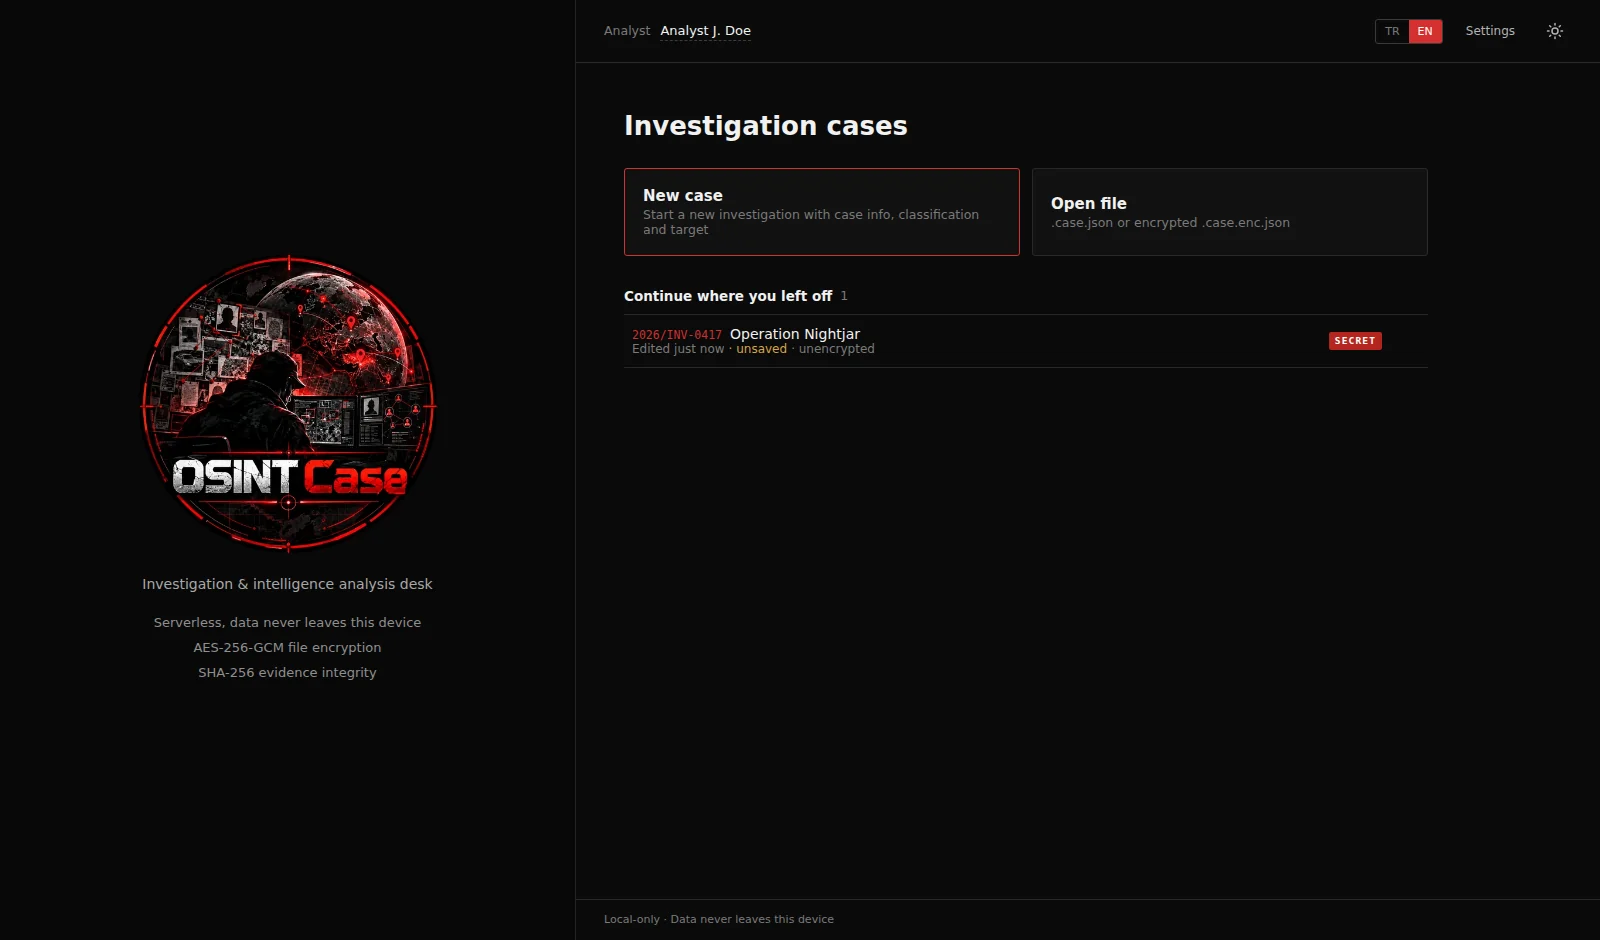
Network View

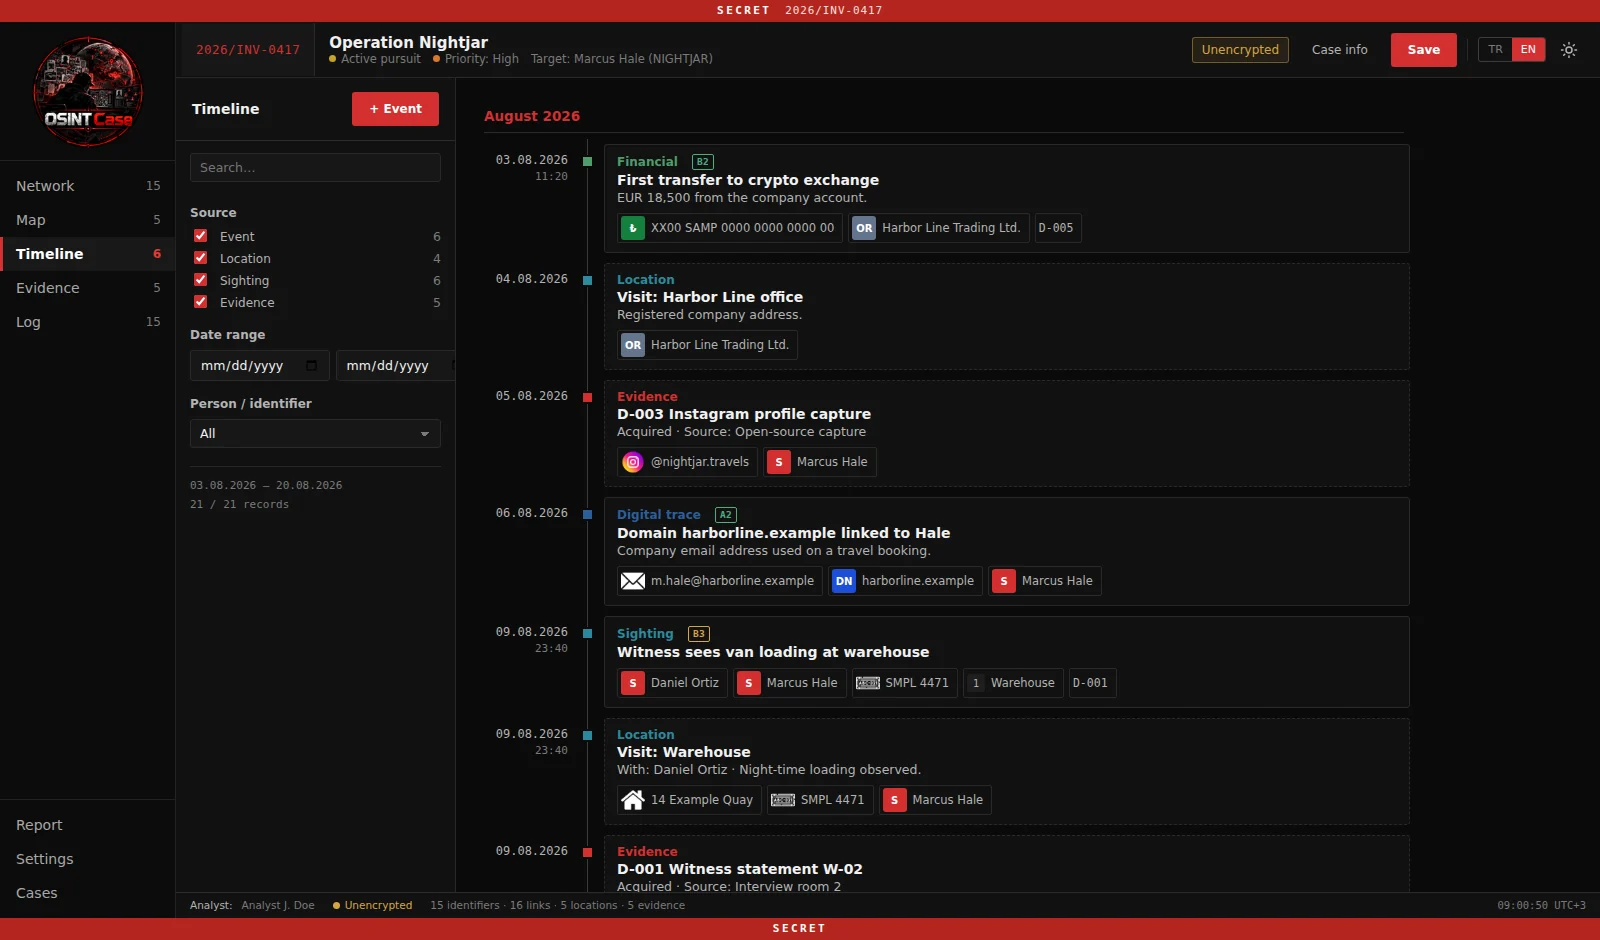
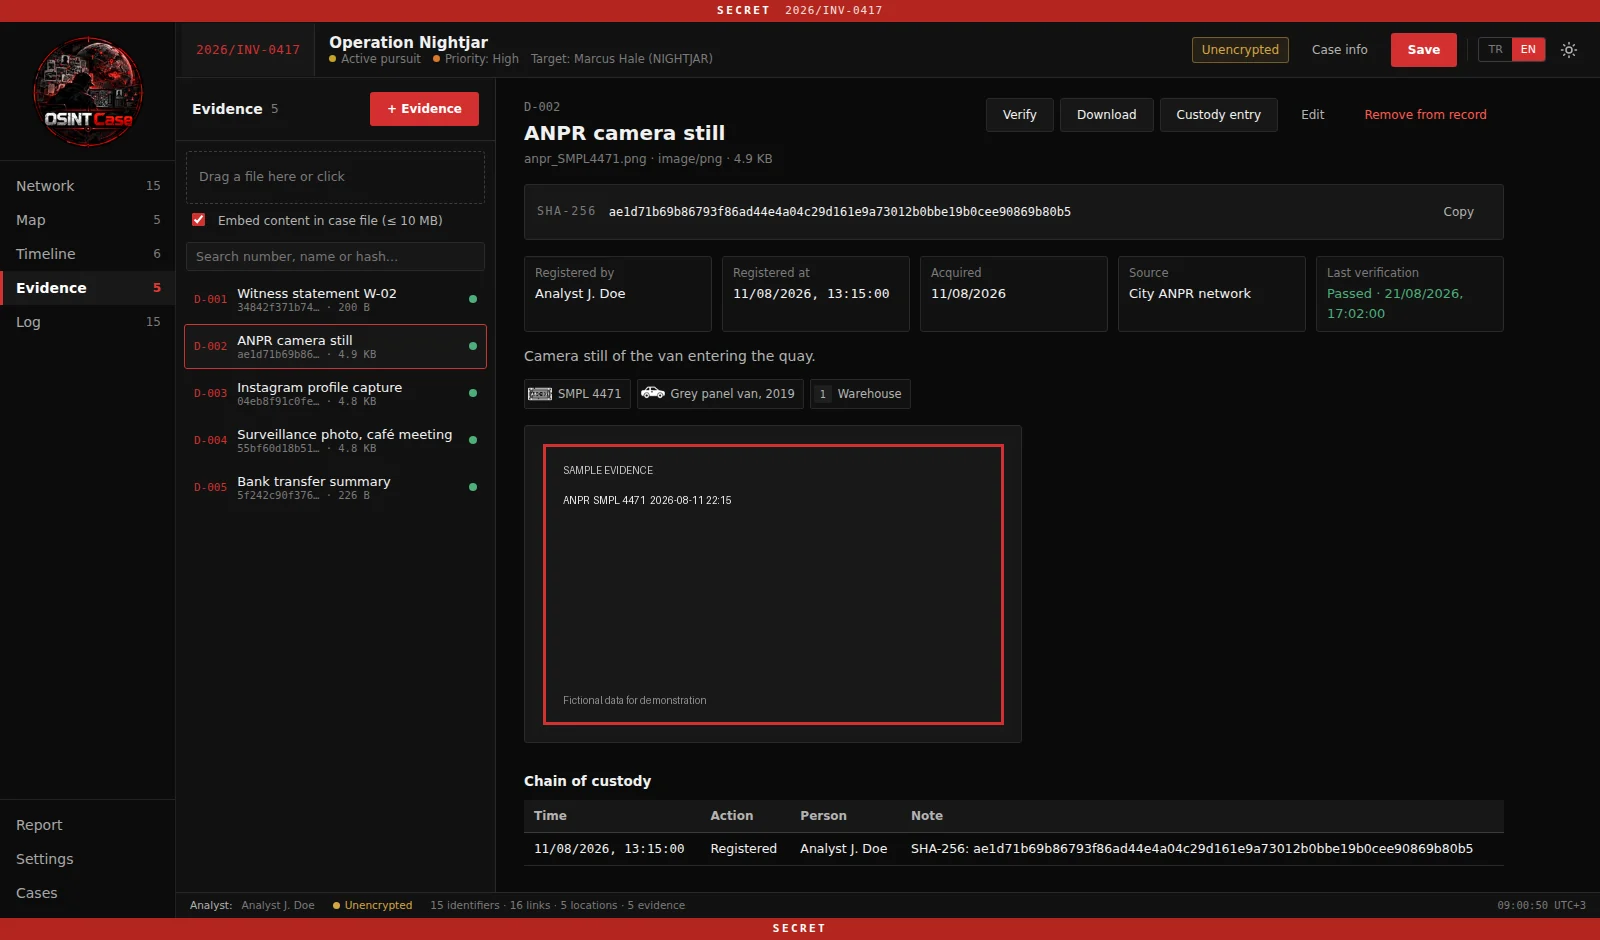
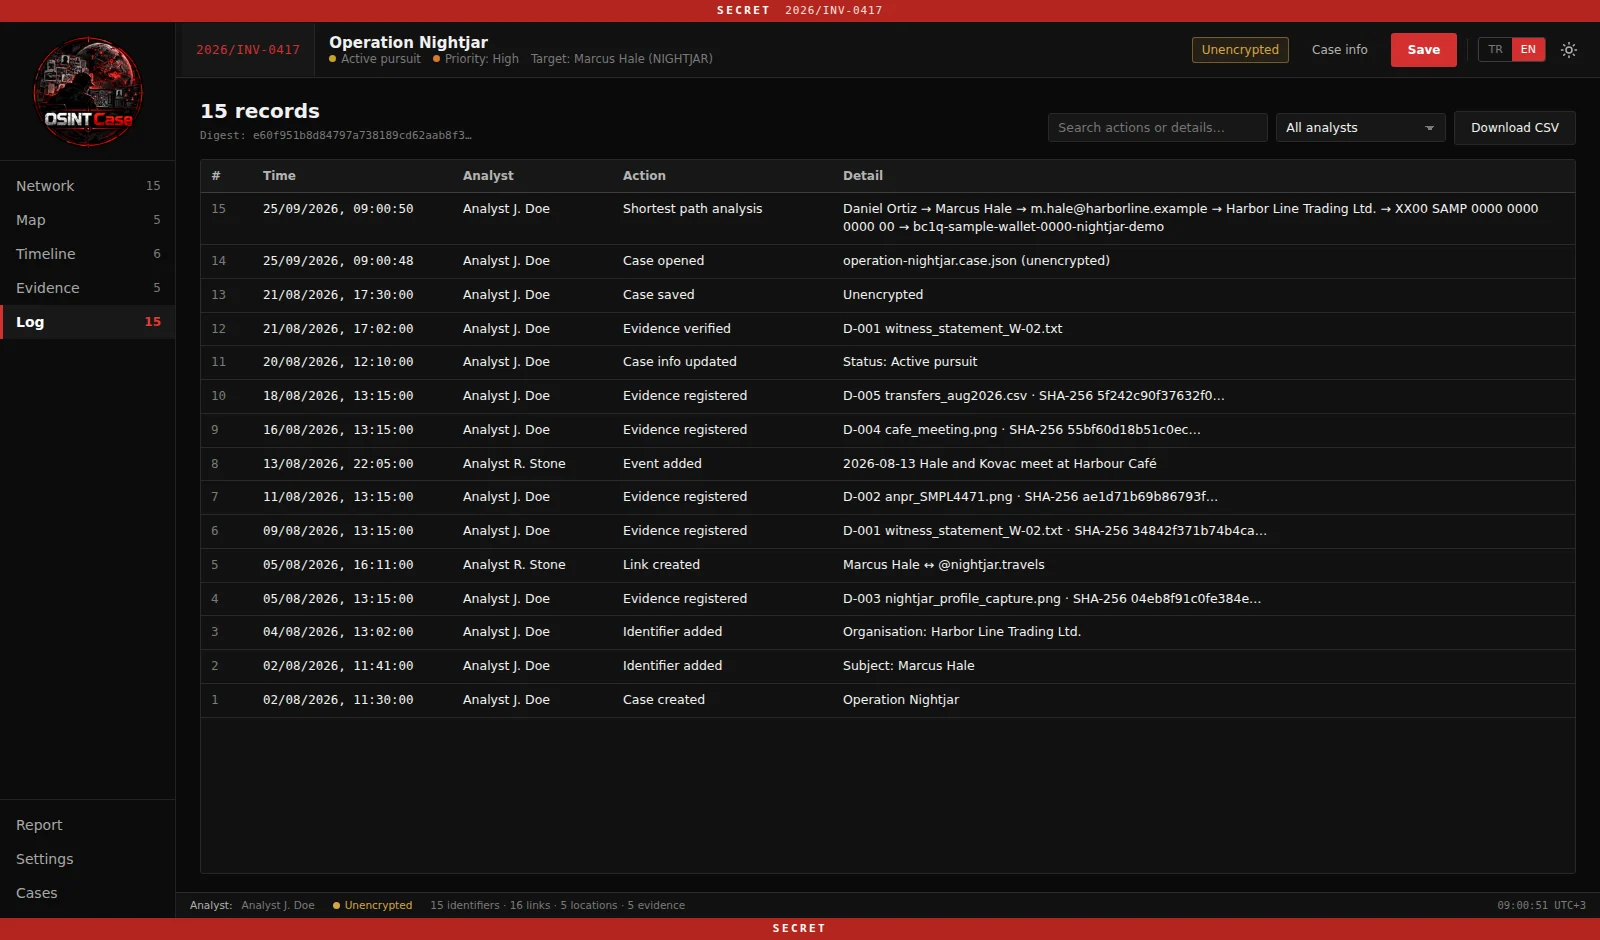
Screenshots

HomeNetwork
HomeNetwork
TimelineEvidence
TimelineEvidence
Audit LogReport
Audit LogReport

Features

  • Investigation case management
  • Entity and identifier mapping (50+ types: people, acquaintances, employment, education, 25+ social platforms, breach records…)
  • Subject photos: multiple main and additional photos per person, SHA-256 of each original
  • Relationship and link analysis
  • Location mapping
  • Investigation timeline
  • Evidence management
  • SHA-256 evidence hashing
  • Chain of custody
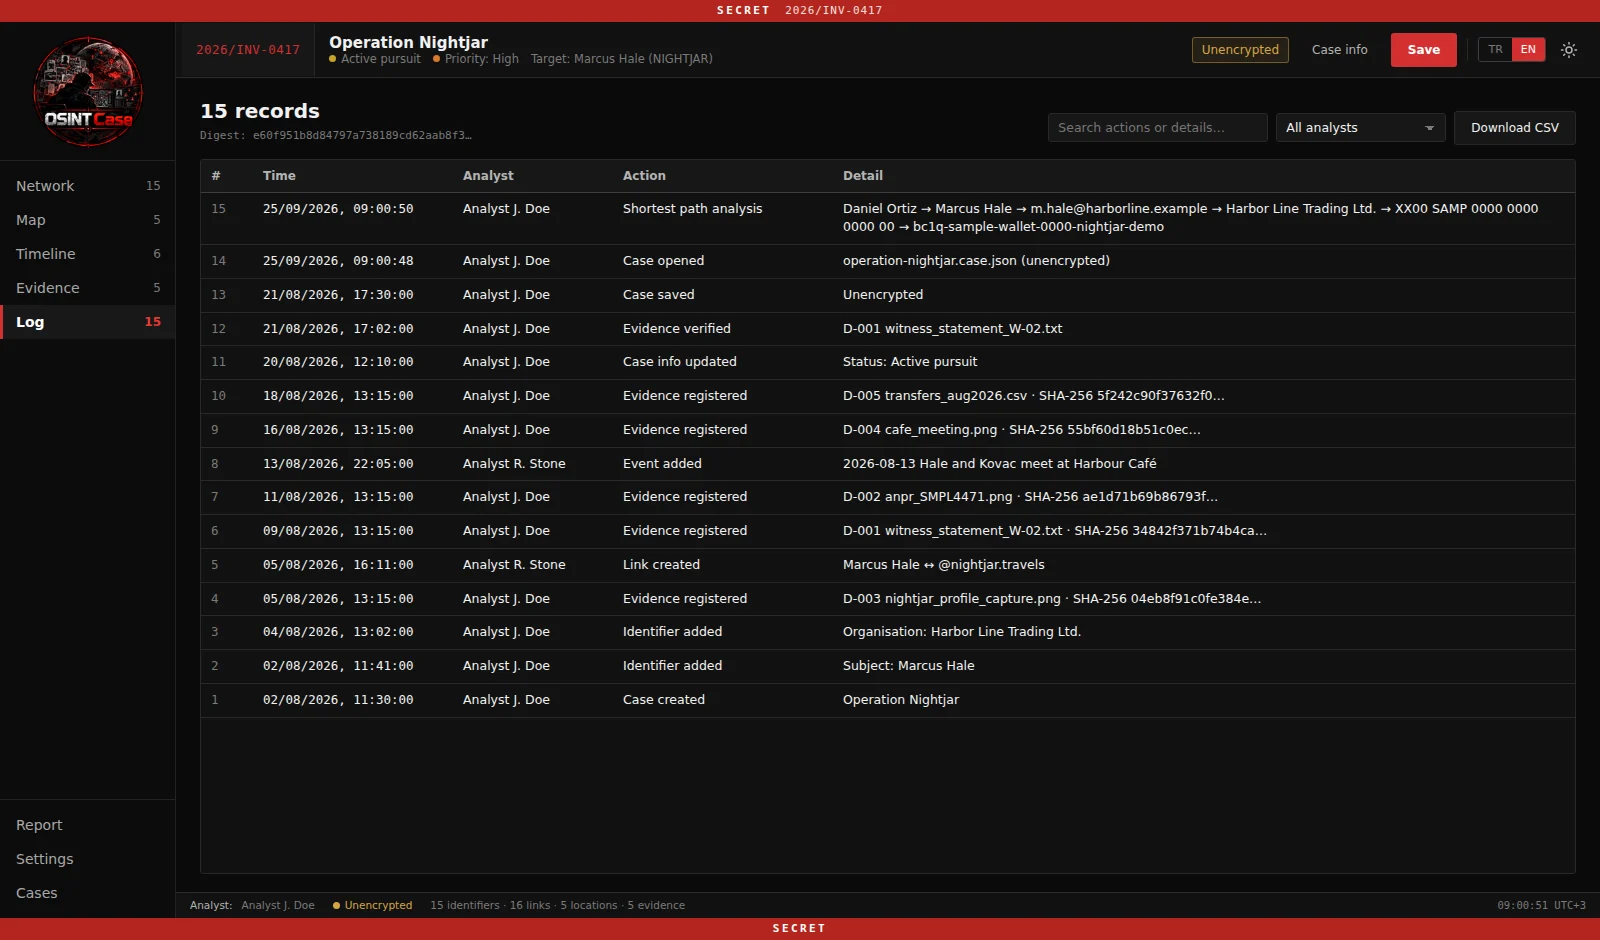
  • Audit log
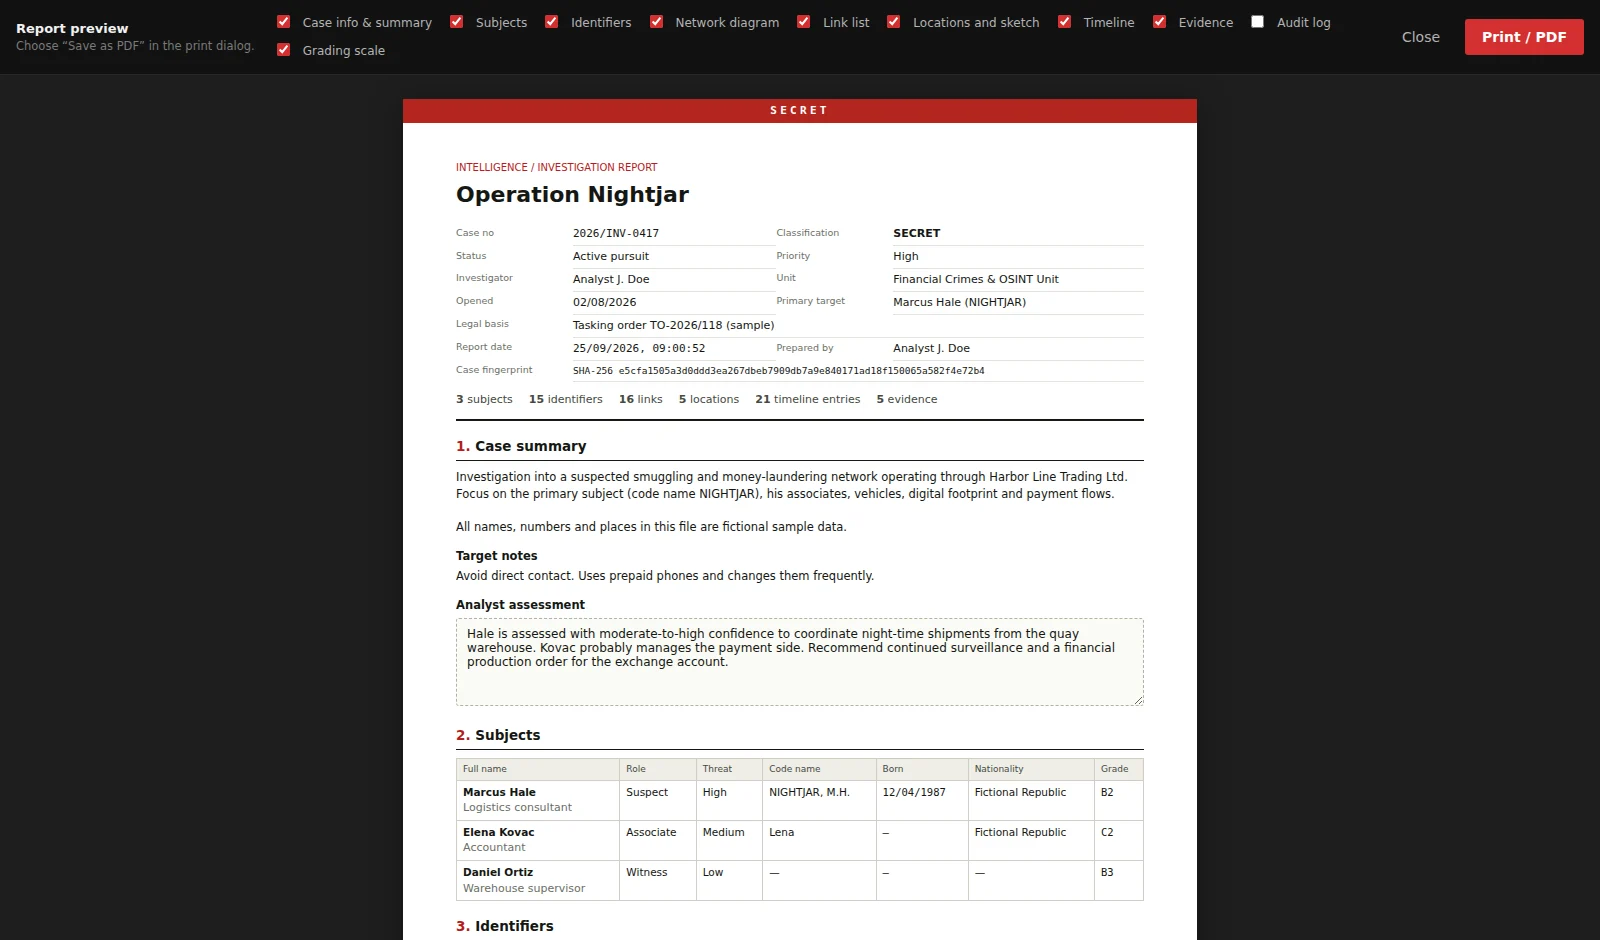
  • Intelligence report generation: dark / light themes, subject profiles, redaction, watermark
  • Report export as PDF (print engine, page numbers, classification band) and single-file HTML
  • Case file import and export
  • Optional AES-256-GCM encryption
  • Turkish and English interface
  • Dark and light themes
  • Fully client-side

Quick Start

Requires Node.js 18+.

npm install
npm run dev

Open http://localhost:5173.

Docker

docker compose up --build

Then open http://localhost:5173.

Sample Case

A fictional investigation is included:

example/operation-nightjar.case.json

Open the file from the application to explore the sample investigation.

More samples in example/ (all people, organisations, numbers and places are fictional; photos are synthetic silhouettes, not real people):

FileLanguageContent
operasyon-kara-sahin.case.jsonTRCounter-terrorism style case with subject photos, new identifier types, map, timeline, evidence
operation-nightjar-photos.case.jsonENOperation Nightjar with subject photos and the new identifier types
example-reports/tr/TRDark PDF, light PDF (redacted + watermarked), single-file HTML reports
example-reports/en/ENThe same outputs in English

The report follows the interface language: switch TR / EN before exporting. The sample files can be regenerated with python3 tools/ornek-dosya-uret.py (needs Pillow).

Privacy

OSINT Case runs entirely in the browser.

No server, analytics or telemetry is used. Case data and evidence remain on the local device.

License

GPL-3.0

تنزيل الأداة