Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
APTs-Adversary-Simulation — This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks . | Kitploit
工具/GitHubGitHub/s3n4t0r-0x0/apts-adversary-simulation
Privilege EscalationReconnaissancePersistence MechanismsExploitationLateral MovementPost-ExploitationPenetration TestingCommand and ControlLearning & EducationRed TeamingPayload DevelopmentAdversarial Attack
1.1k190412天前Kitploit 审核通过

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →

关于

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks .

分享
GitHubs3n4t0r-0x0/apts-adversary-simulation
APTs-Adversary-Simulation

查看仓库
内容在请求的语言中不可用。显示英文版本。

APTs Adversary Simulation

Adversary Simulation APT Simulation MITRE ATT&CK TTPs Red Team

A comprehensive collection of simulated Advanced Persistent Threat (APT) attacks based on real world tactics, techniques, and procedures (TTPs) used by state sponsored APT Groups from Russia, China, Iran, and North Korea
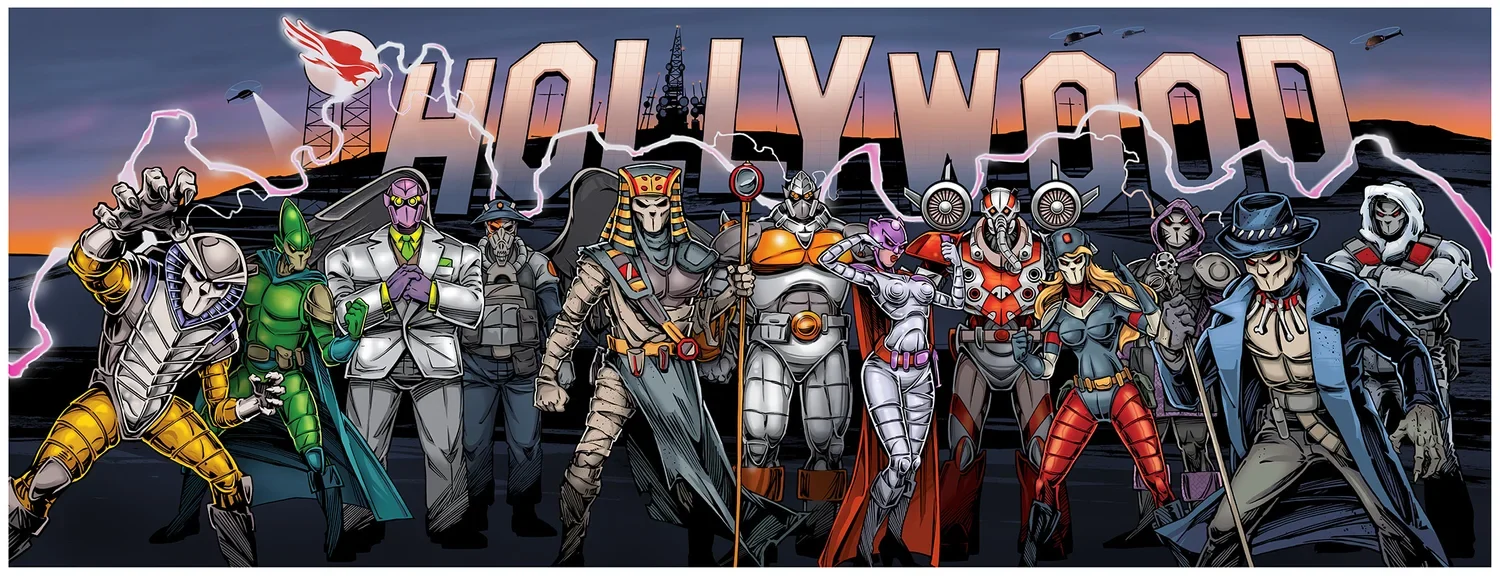
hollywood-Comp-02

[!CAUTION] Important Notice: This project is strictly for educational, research, and defensive security purposes only. Unauthorized use of these techniques may violate laws and result in serious legal consequences.

🧠 Overview

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, command and control (C2) servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks. The simulations are based on extensive research from leading cybersecurity firms, including PaloAlto Unit42, Kaspersky, Microsoft, Cisco, Trellix, CrowdStrike, and WithSecure.

Learn More About the Importance and Outcomes of the Experience:

  • Why Adversary Simulation? - Understanding the strategic value of simulating advanced threats
  • Adversary Simulation VS Adversary Emulation - Key differences and when to use each approach
  • How do I simulate an APT - Adversary Simulation Is Not a Methodology It's the Outcome of Experience

🎯 Simulated APT Groups

Note: APT group names in this repository follow the naming conventions used by different security vendors. The same APT group may have different names depending on the vendor (e.g., Mandiant, CrowdStrike, Microsoft, Kaspersky, etc.).
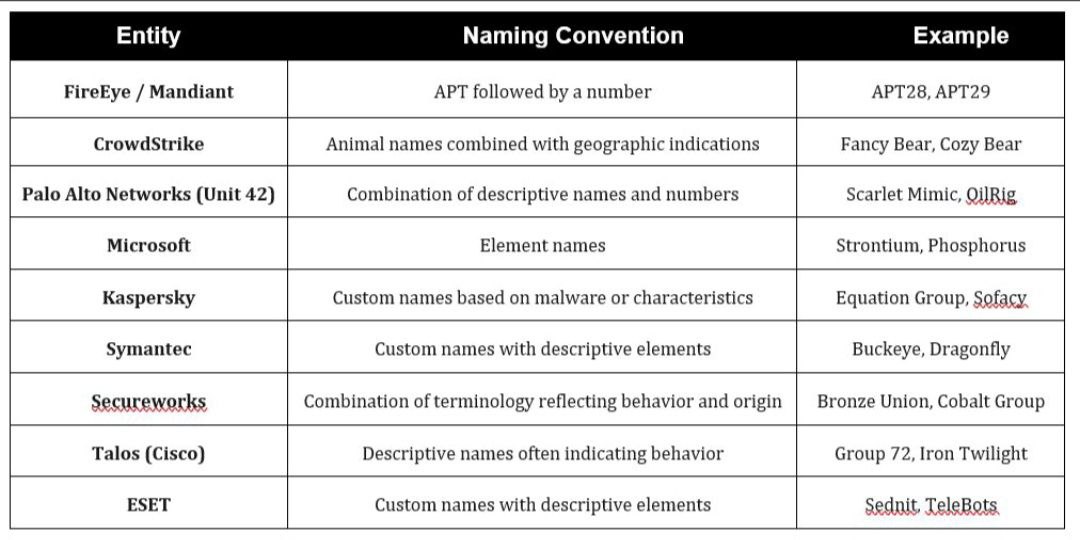
photo_2025-11-09_04-26-38

Below is the complete list of simulated APT Groups:

Country
of Origin
Russia 🇷🇺 China 🇨🇳 North Korea 🇰🇵 Iran 🇮🇷
APT Groups

Cozy Bear
Voodoo Bear
Fancy Bear
Energetic Bear
Berserk Bear
Gossamer Bear
Primitive Bear
Ember Bear
Venomous Bear

Mustang Panda
Wicked Panda
Goblin Panda
Deep Panda
Glacial Panda
Anchor Panda
Samurai Panda
Phantom Panda
Sunrise Panda
Ethereal Panda

Lazarus
Labyrinth Chollima
Velvet Chollima
Famous Chollima
Ricochet Chollima
Silent Chollima

Helix Kitten
Charming Kitten
Static Kitten
Muddy Water
Tracer Kitten
Pioneer Kitten
Nemesis Kitten
Clever Kitten
Pulsar Kitten
Remix Kitten
Haywire Kitten

🛠️ Adversary Framework

All adversary simulations are powered by BEAR-C2 a custom command and control framework designed for realistic threat simulation.
image psd(1)

📫 Contact

Telegram Twitter/X LinkedIn Reddit
下载工具