 pennacle-security/summit
开源 Web 安全测试平台:集代理、扫描器和模糊测试器于一体的 CLI 工具。由 Pennacle Security 开发。


一个用于 Web 安全测试的可脚本化 CLI:扫描器、代理、模糊测试器、授权测试、WAF 分析、链接劫持检测和侦察。
在同类工具收费的领域免费提供 - 由 Pennacle Security 打造。
我们每天都在使用 Burp 和 ZAP。我们也一直想要三样它们不具备的东西:一个可以在 CI 中编写脚本调用的扫描器、能告诉我们其确信程度的发现结果,以及一个小到可以一口气读完的代码库。Summit 就是这样的工具 - v0.5,MIT 许可,仅一个依赖(requests),公开构建。
完整文档: pennacle-security.github.io/summit
通常需要付费工具才能获得的能力,外加扫描核心:
| 能力 | Summit | 常见做法 |
|---|---|---|
| 失效的访问控制测试(BOLA/IDOR) | summit authorize | Autorize 风格插件 / 付费工作流 |
| 隐藏参数发现 | summit mine | Param Miner 风格插件 |
| OpenAPI 驱动扫描 | summit scan --openapi | 插件 |
| WAF 指纹识别 + 绕过探测 | 内置 | 部分支持 / 插件 |
| 失效链接劫持检测 | 内置 | 付费扩展 |
| SQLi、XSS、重定向、目录遍历、接管、主机头、CORS | 内置 | 核心扫描器(免费) |
| 侦察链:subfinder -> httpx -> nmap | summit recon | 手动拼接 |
| 速率限制、重试、JWT/编码器工具包 | 内置 | 插件 / 付费 |
| 面向 CI、带置信度标签的发现结果 | 这正是核心所在 | 付费自动化 |
每个发现结果都带有置信度标签:confirmed(已观察到的事实)或 potential(启发式判断)。这一区分贯穿整个工具。
git clone https://github.com/pennacle-security/summit.git
cd summit
pip install -e .
Python 3.10+。然后观察它针对一个故意设置的本地易受攻击目标运行:
python examples/vuln_app.py        # terminal 1 - the target (127.0.0.1 only)
summit scan http://127.0.0.1:8765  # terminal 2 - the scan
对真实项目进行更全面的处理如下所示:
summit recon target.com --json recon.json                 # subdomains -> hosts -> ports
summit scan https://target.com --depth 2 --rate 10        # crawl + all checks
summit scan --openapi api-spec.json                       # API: scan what the spec admits to
summit authorize https://target.com/admin?user=1 \
  --role 'admin=Cookie: session=abc' \
  --role 'user=Cookie: session=xyz'                       # BOLA/IDOR testing
本页面上的每一项声明都由 examples/evidence.py 复现——它实时运行演示目标,测量每项功能,并打印带有真实数字的 PASS/FAIL。CI 在每次推送时都会执行它;一旦某项声明不再成立,构建就会失败。
python examples/evidence.py)[PASS] full scan: 16 seeded check families detected, zero false positives
53 findings in 22.9s (344 requests), missing=none, control link flagged=no, 19 finding(s) carry confidence=confirmed
[PASS] resource takeover fingerprint detected on the target's own 404
Possible AWS S3 resource takeover | AWS S3: 'nosuchbucket'
[PASS] host header injection: marker domain echoed back by the app
Host: summit-host-probe.example -> reflected (reset-link poisoning surface)
[PASS] CORS reflects an arbitrary origin with credentials allowed
ACAO: https://summit-cors-probe.example; ACAC: true
[PASS] WAF bypass: naive filter blocks, tampered payload lands decoded
raw payload -> HTTP 403 (blocked); URL-encoded once -> HTTP 200, payload reflected decoded: True
[PASS] CAPTCHA challenge detected (reported, not solved)
/login -> reCAPTCHA via marker 'recaptcha/api.js'
[PASS] rate limiting: --rate 5 paces 12 requests to ~2.2s; unlimited runs free
12 requests at rate 5 -> 2.20s (theoretical floor: 2.2s); 12 requests unlimited -> 0.02s
[PASS] concurrency on a latency-bearing target: 8 workers vs serial
40 requests x 25ms latency: serial 1.33s -> parallel 0.18s (7.3x speedup)
[PASS] smart prioritizer ranks known-injectable parameters first
probing starts with: [('query', 'search?query=laptop'), ('id', 'user?id=1'), ('url', 'example.com')]
[PASS] toolkit decodes JWT header/payload and states the signature is unverified
signature NOT verified - decoding only
[PASS] update check compares versions numerically (0.3 < 0.10)
is_outdated('0.3.0', '0.10.0') -> True; is_outdated('1.0.0', '0.9.9') -> False
[PASS] broken access control: admin panel served identically to a low-privilege role
verdict=broken; finding=Broken access control (BOLA/IDOR candidate)
[PASS] hidden parameter mining finds the undocumented debug parameter, zero noise
1 finding(s): ['debug'] (all confirmed reflections)
[PASS] openapi-driven scan: spec alone leads the engine to seeded SQLi and XSS
2 spec target(s) scanned -> 10 findings, sqli-error=yes, xss-reflection=yes
[PASS] OS command injection: marker executed and echoed by the server
semicolon: exec marker x2, control marker x1 | CWE-78
[PASS] server-side template injection: {{7*7}} came back as 49
Jinja2/Twig: {{7*7}} -> 49 | CWE-1336
[PASS] CRLF injection: X-Summit-CRLF header materialized in the response
X-Summit-CRLF: injected | CWE-113
[PASS] sensitive file exposure: /.env confirmed by content signature
content signature: 'APP_KEY=' | CWE-538
[PASS] CVE detection: Apache/2.4.49 banner maps to known CVEs
detect_cves('Apache/2.4.49') -> ['CVE-2021-41773', 'CVE-2021-42013']
evidence summary: 19/19 claims verified
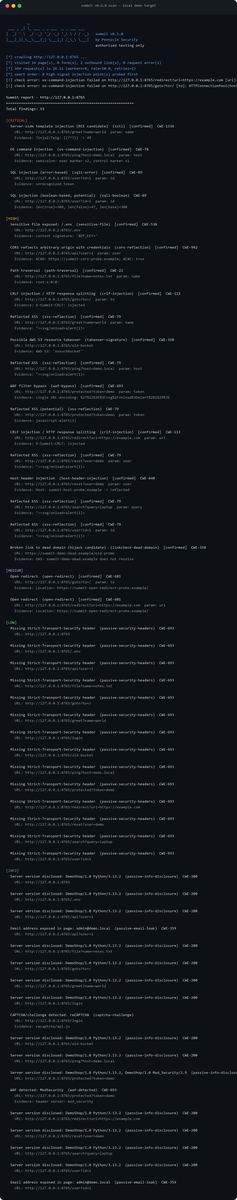
针对演示目标进行真实扫描的可视化效果:
自行复现全部内容:
python examples/vuln_app.py    # terminal 1 - the target
summit scan http://127.0.0.1:8765
python examples/evidence.py    # re-verify every claim above
演示会植入一个健康的出站链接(https://example.com)作为阴性对照——它绝不应被报告,CI 会连同植入的检测项一起对此进行断言。还是发现了问题?报告它。
| 命令 | 作用 |
|---|---|
summit scan <url> | 爬取,然后进行被动 + 主动检查、链接健康检查、WAF 分析。--openapi 扫描规范而非爬取。--json / --html 报告。 |
summit authorize <url...> | BOLA/IDOR 测试:比较两个角色之间的响应。 |
summit mine <url> | 隐藏参数发现(约 70 个候选,基于标记)。 |
summit fuzz <url> | 带通配符基线过滤的目录暴力破解。 |
summit recon <domain> | 将 subfinder -> httpx -> nmap 串联成一份报告。 |
summit tls <host> | 证书过期 / 自签名 / 旧版 TLS 版本审计。 |
summit proxy | 带 SQLite 站点地图的拦截式 HTTP 代理。 |
summit repeater <file> | 发送原始请求文件(Burp 风格)。 |
summit encode / summit decode | base64、URL、hex、JWT(仅解码,如实说明未验证)。 |
summit --check-update / --auto-update / --install-tools | 版本管理和侦察工具安装器。 |


