Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
ssh-auditor — 扫描网络中弱 SSH 密码的最佳方式 | Kitploit
工具/GitHubGitHub/ncsa/ssh-auditor
漏洞扫描器密码攻击网络安全
GitHubncsa/ssh-auditor

ssh-auditor

扫描网络中弱 SSH 密码的最佳方式

查看仓库
62086305年前Kitploit 审核通过
分享

Build Status

SSH Auditor

功能特性

ssh-auditor 将自动:

  • 重新检查所有已知主机,当新凭证添加时。它只会检查新凭证。
  • 对任何发现的新主机排队进行完整凭证扫描。
  • 对任何 SSH 版本或密钥指纹发生变化的已知主机排队进行完整凭证扫描。
  • 尝试执行命令,并尝试隧道 TCP 连接。
  • 使用每个凭证的 scan_interval(默认为 14 天)重新检查每个凭证。

它的设计使得你可以每小时从 cron 运行 ssh-auditor discover + ssh-auditor scan 来进行持续审计。
演示

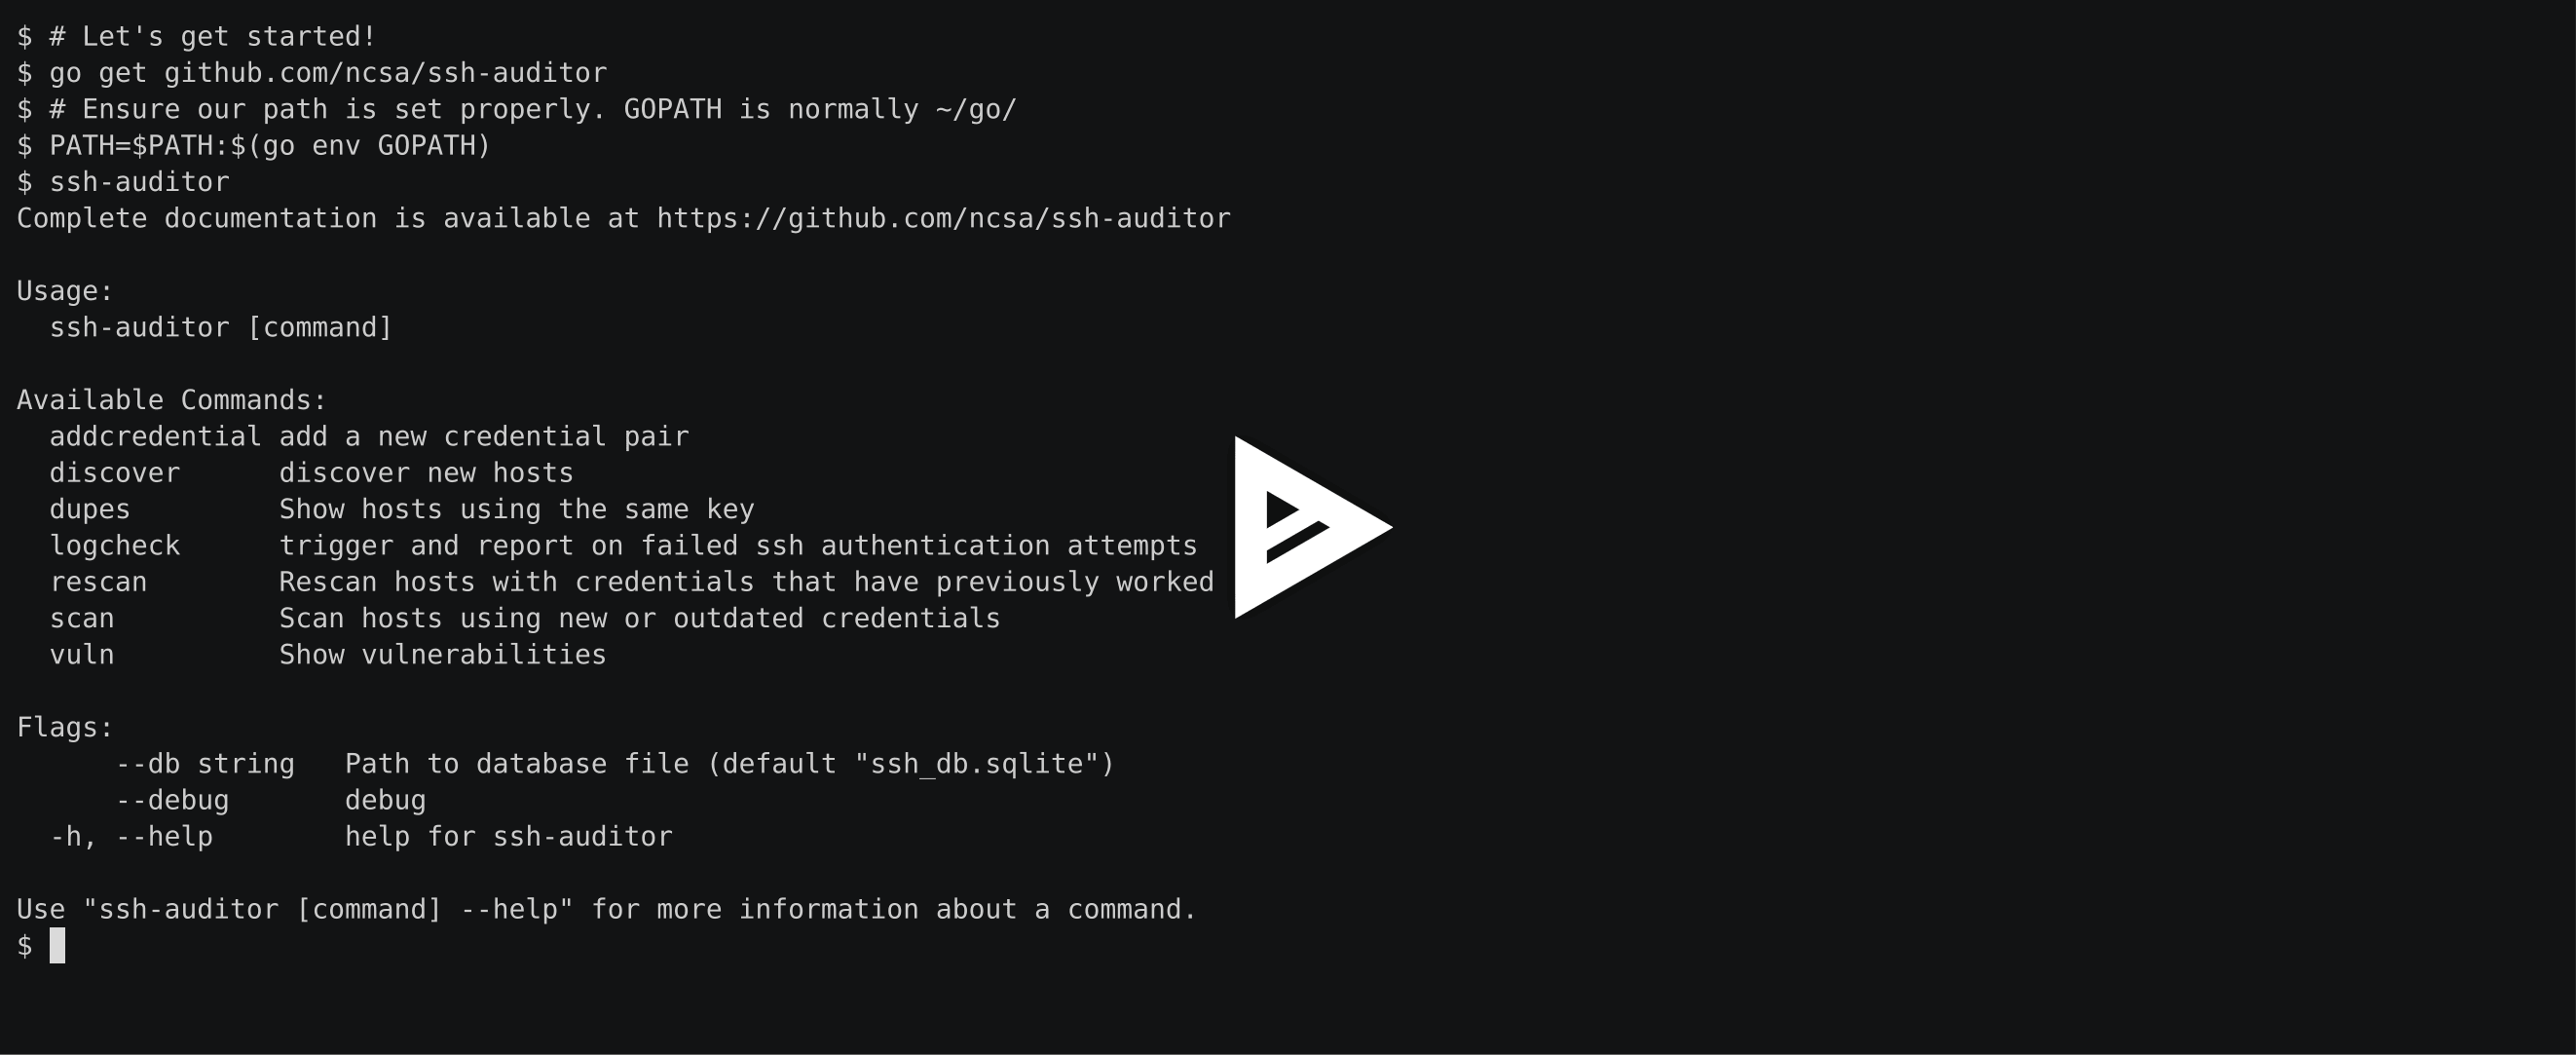
早期演示展示所有功能

demo

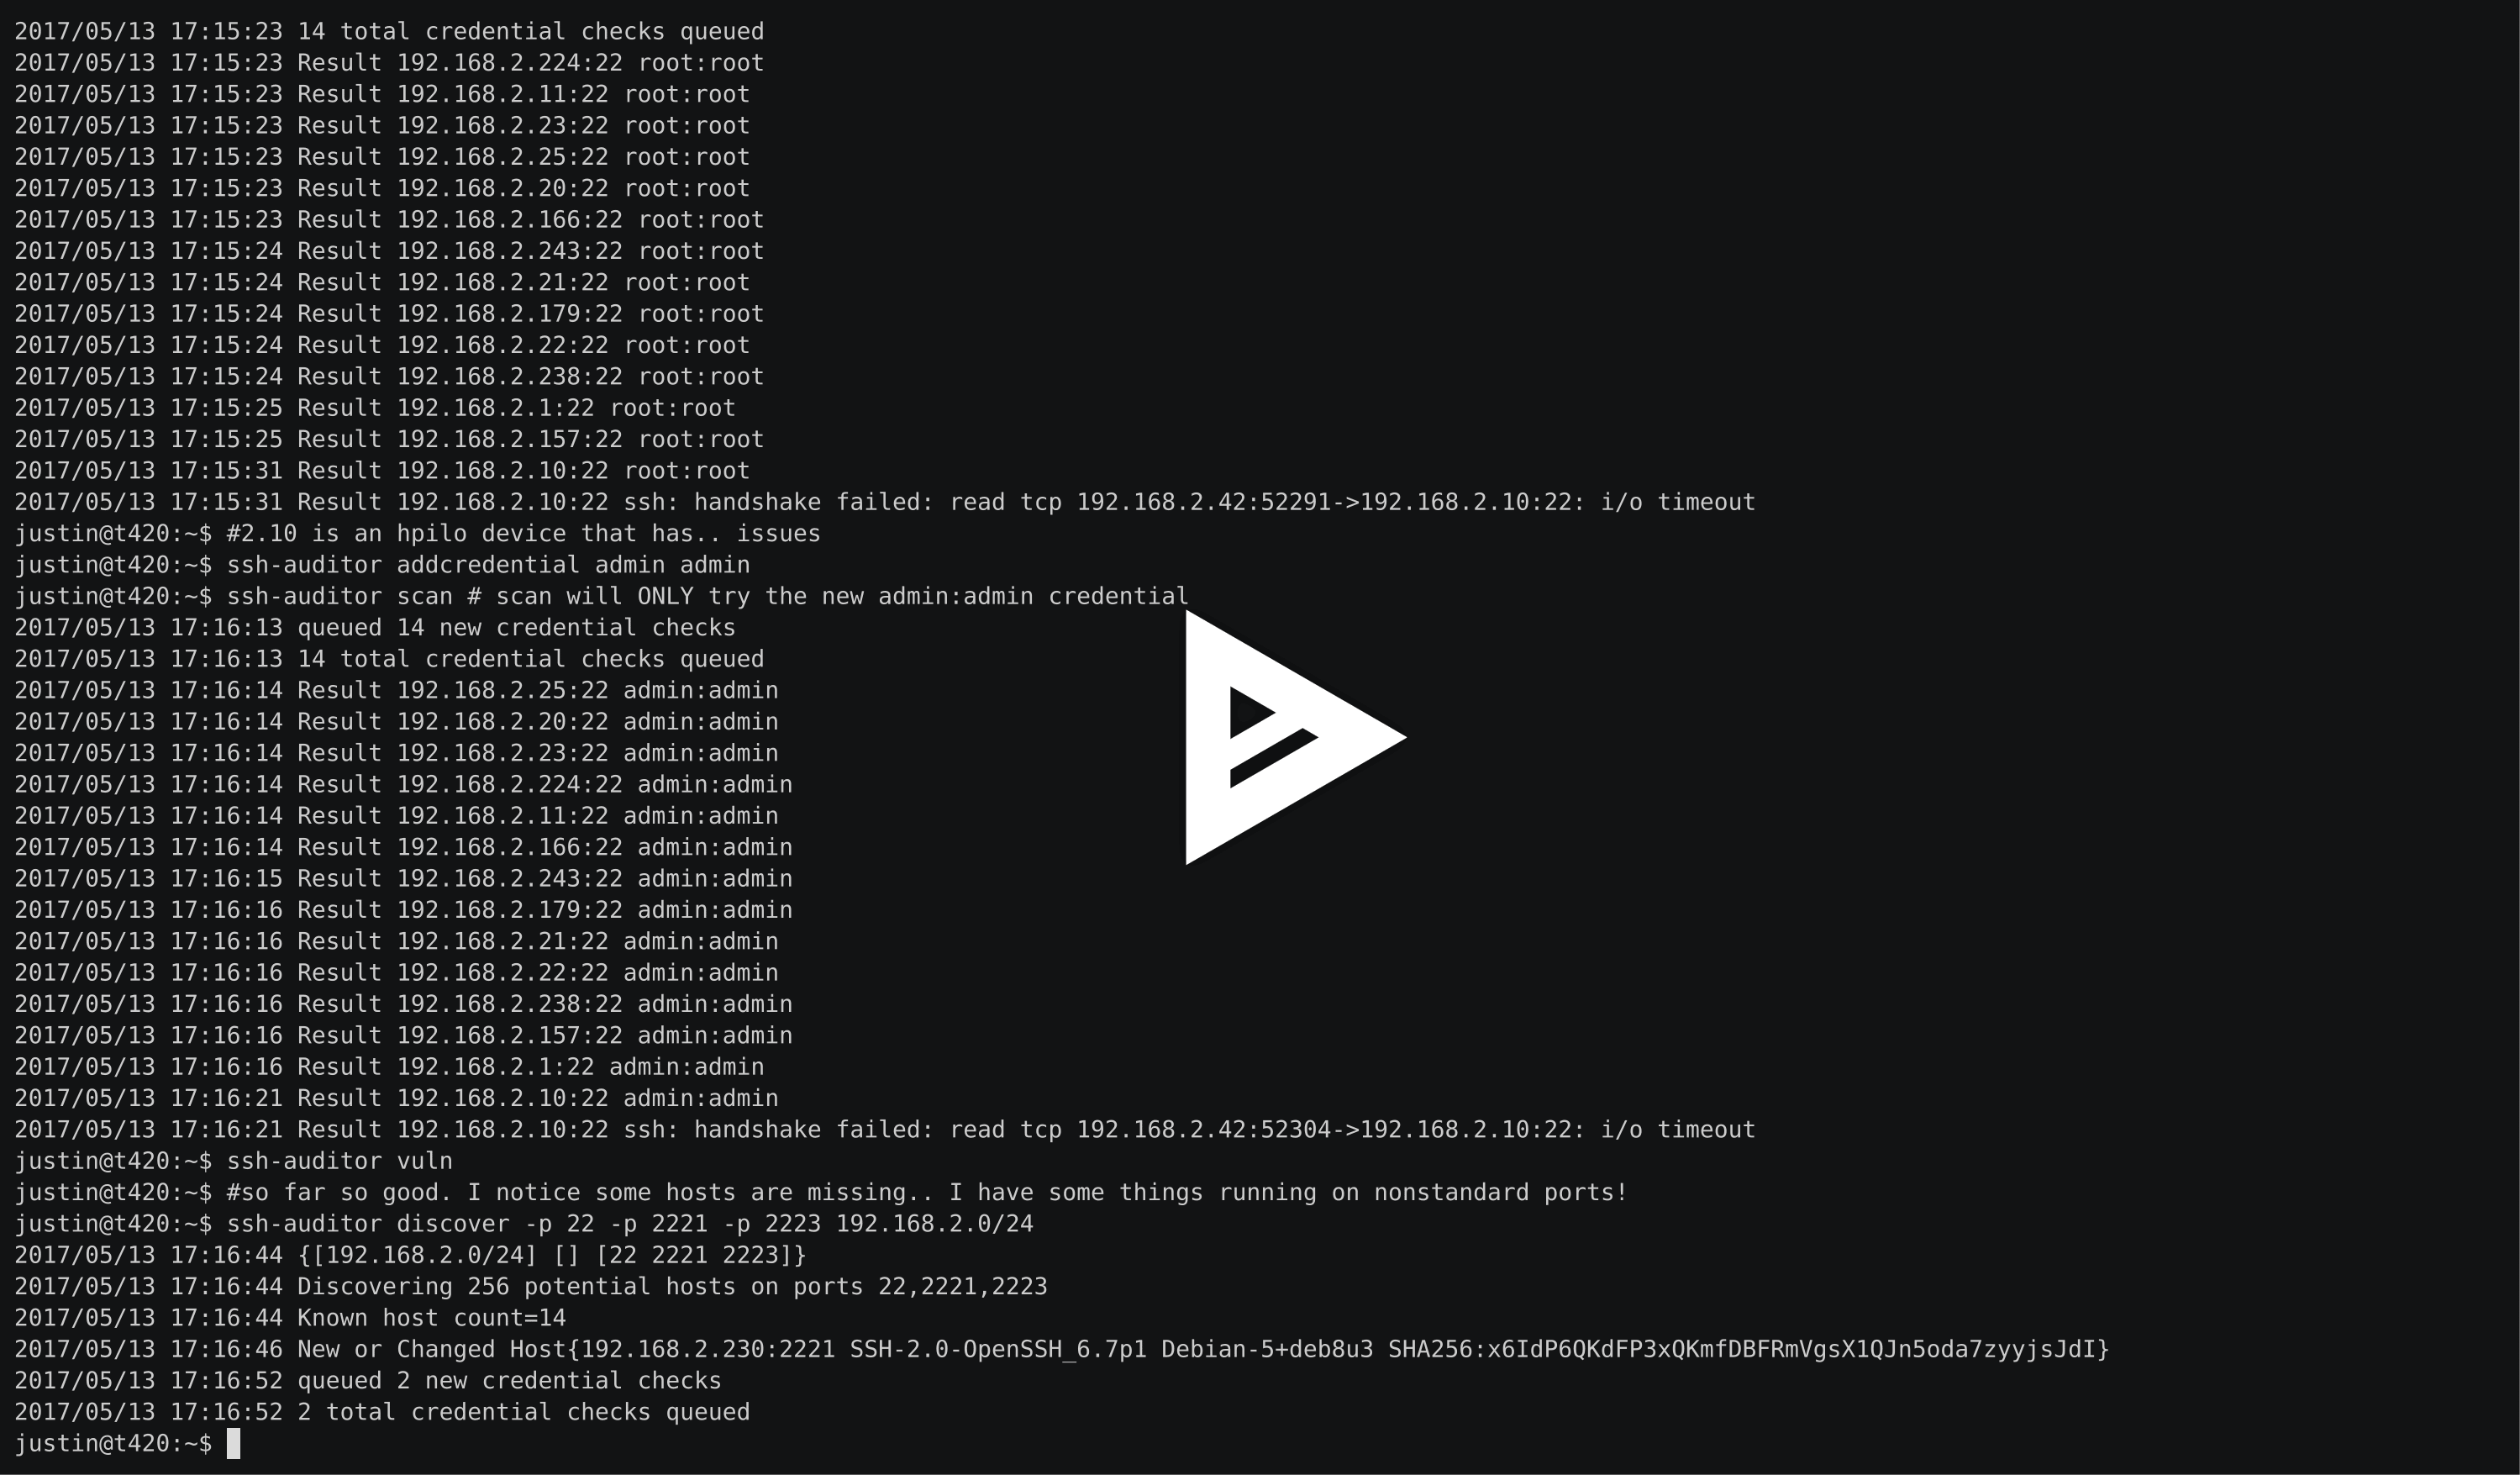
演示展示改进的日志输出

demo

用法

安装

$ brew install go # or however you want to install the go compiler
$ go get github.com/ncsa/ssh-auditor

或者从 git 克隆构建

$ go build

构建包含 sqlite 的静态二进制文件

$ make static

确保你可以使用足够的文件描述符

$ ulimit -n 4096

创建初始数据库并发现 SSH 服务器

$ ./ssh-auditor discover -p 22 -p 2222 192.168.1.0/24 10.0.0.1/24

添加要检查的凭证对

$ ./ssh-auditor addcredential root root
$ ./ssh-auditor addcredential admin admin
$ ./ssh-auditor addcredential guest guest --scan-interval 1 #check this once per day

尝试对发现的主机使用凭证

$ ./ssh-auditor scan

输出报告,显示哪些凭证有效

$ ./ssh-auditor vuln

重新检查有效的凭证

$ ./ssh-auditor rescan

输出重复密钥使用报告

$ ./ssh-auditor dupes

待办事项

  • 更新“主机变更”表
  • 处理来自不使用 SSH 密码认证而改用 shell 进行认证的设备的误报。
  • 可变重检时间 - 每个凭证都有一个以天为单位的 scan_interval
  • 更好地支持非标准端口 - 只需要更新 discover,其余部分不需关心。
  • 可能作为守护进程运行,并添加一个 API 供 bro 钩子使用,以便在检测到新 SSH 服务器时立即启动 discover。
  • 使存储可插拔(mysql, postgresql)。
  • 区分密码尝试失败与连接失败或超时。基本完成。像 fail2ban 这样的东西会使情况复杂化。
  • 为报告 sqlite3 命令添加 Go 实现。

报告查询。

ssh-auditor vuln 运行的查询是

select
        hc.hostport, hc.user, hc.password, hc.result, hc.last_tested, h.version
 from
        host_creds hc, hosts h
 where
        h.hostport = hc.hostport
 and    result!='' order by last_tested asc

下载工具

最受欢迎

查看全部 →

发现我们社区最常用的工具。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 终极 OSINT 工具包:调查图谱、置信度评分、别名家族、地图、时间线和报告。49 个模块、400+ 个站点,无需 API 密钥。

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock 一键执行应用(CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    基于LLM的多智能体自主渗透测试平台,具备规划器/执行器智能体、资产与探索图谱、MITM流量记录以及漏洞复测功能。

    415
  • 4

    redforge

    cybersecurity91/redforge

    浏览器端红队工具包,包含 102 个离线工具,用于侦察、载荷生成、凭据攻击、加密、编码和交战报告。

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。

    258

探索所有工具

浏览我们的工具集合

查看所有工具 →