IATelligence 是一个 Python 脚本,用于从 PE 文件中提取导入地址表(IAT),并利用 OpenAI 的 GPT-3 模型提供该文件导入的每个 Windows API 的详细信息。该脚本还会搜索相关的 MITRE ATT&CK 技术,并解释攻击者可能如何利用这些 API。
它还会显示文件哈希,并估算 GPT-3 请求的成本。IATelligence 是使用 GPT-3 进行恶意软件分析并根据 IAT 快速评估恶意软件行为的概念验证。
以下是结果的一个简单示例。请注意,根据 IAT 的大小,请求可能需要更长时间。
要运行此工具,你需要访问 OpenAI API,然后需要修改脚本以添加你自己的 API。
# Authenticate with the OpenAI API
openai.api_key = ""
你还需要安装依赖项。
pip install -r requirements.txt
要运行该工具,只需将 PE 文件作为参数指定给脚本即可。
python iatelligence.py sample.exe
该脚本还会计算哈希值以及请求的估算成本。
[+] IAT Request from the file: .\sample.exe
[+] 33 functions will be requested to GPT!
[+] MD5: 2f82623f9523c0d167862cad0eff6806
[+] SHA1: 5d77804b87735e66d7d1e263c31c4ef010f16153
[+] SHA256: 9c2c8a8588fe6db09c09337e78437cb056cd557db1bcf5240112cbfb7b600efb
[+] Imphash: 8eeaa9499666119d13b3f44ecd77a729
[!] Estimated cost of requests: $0.0693
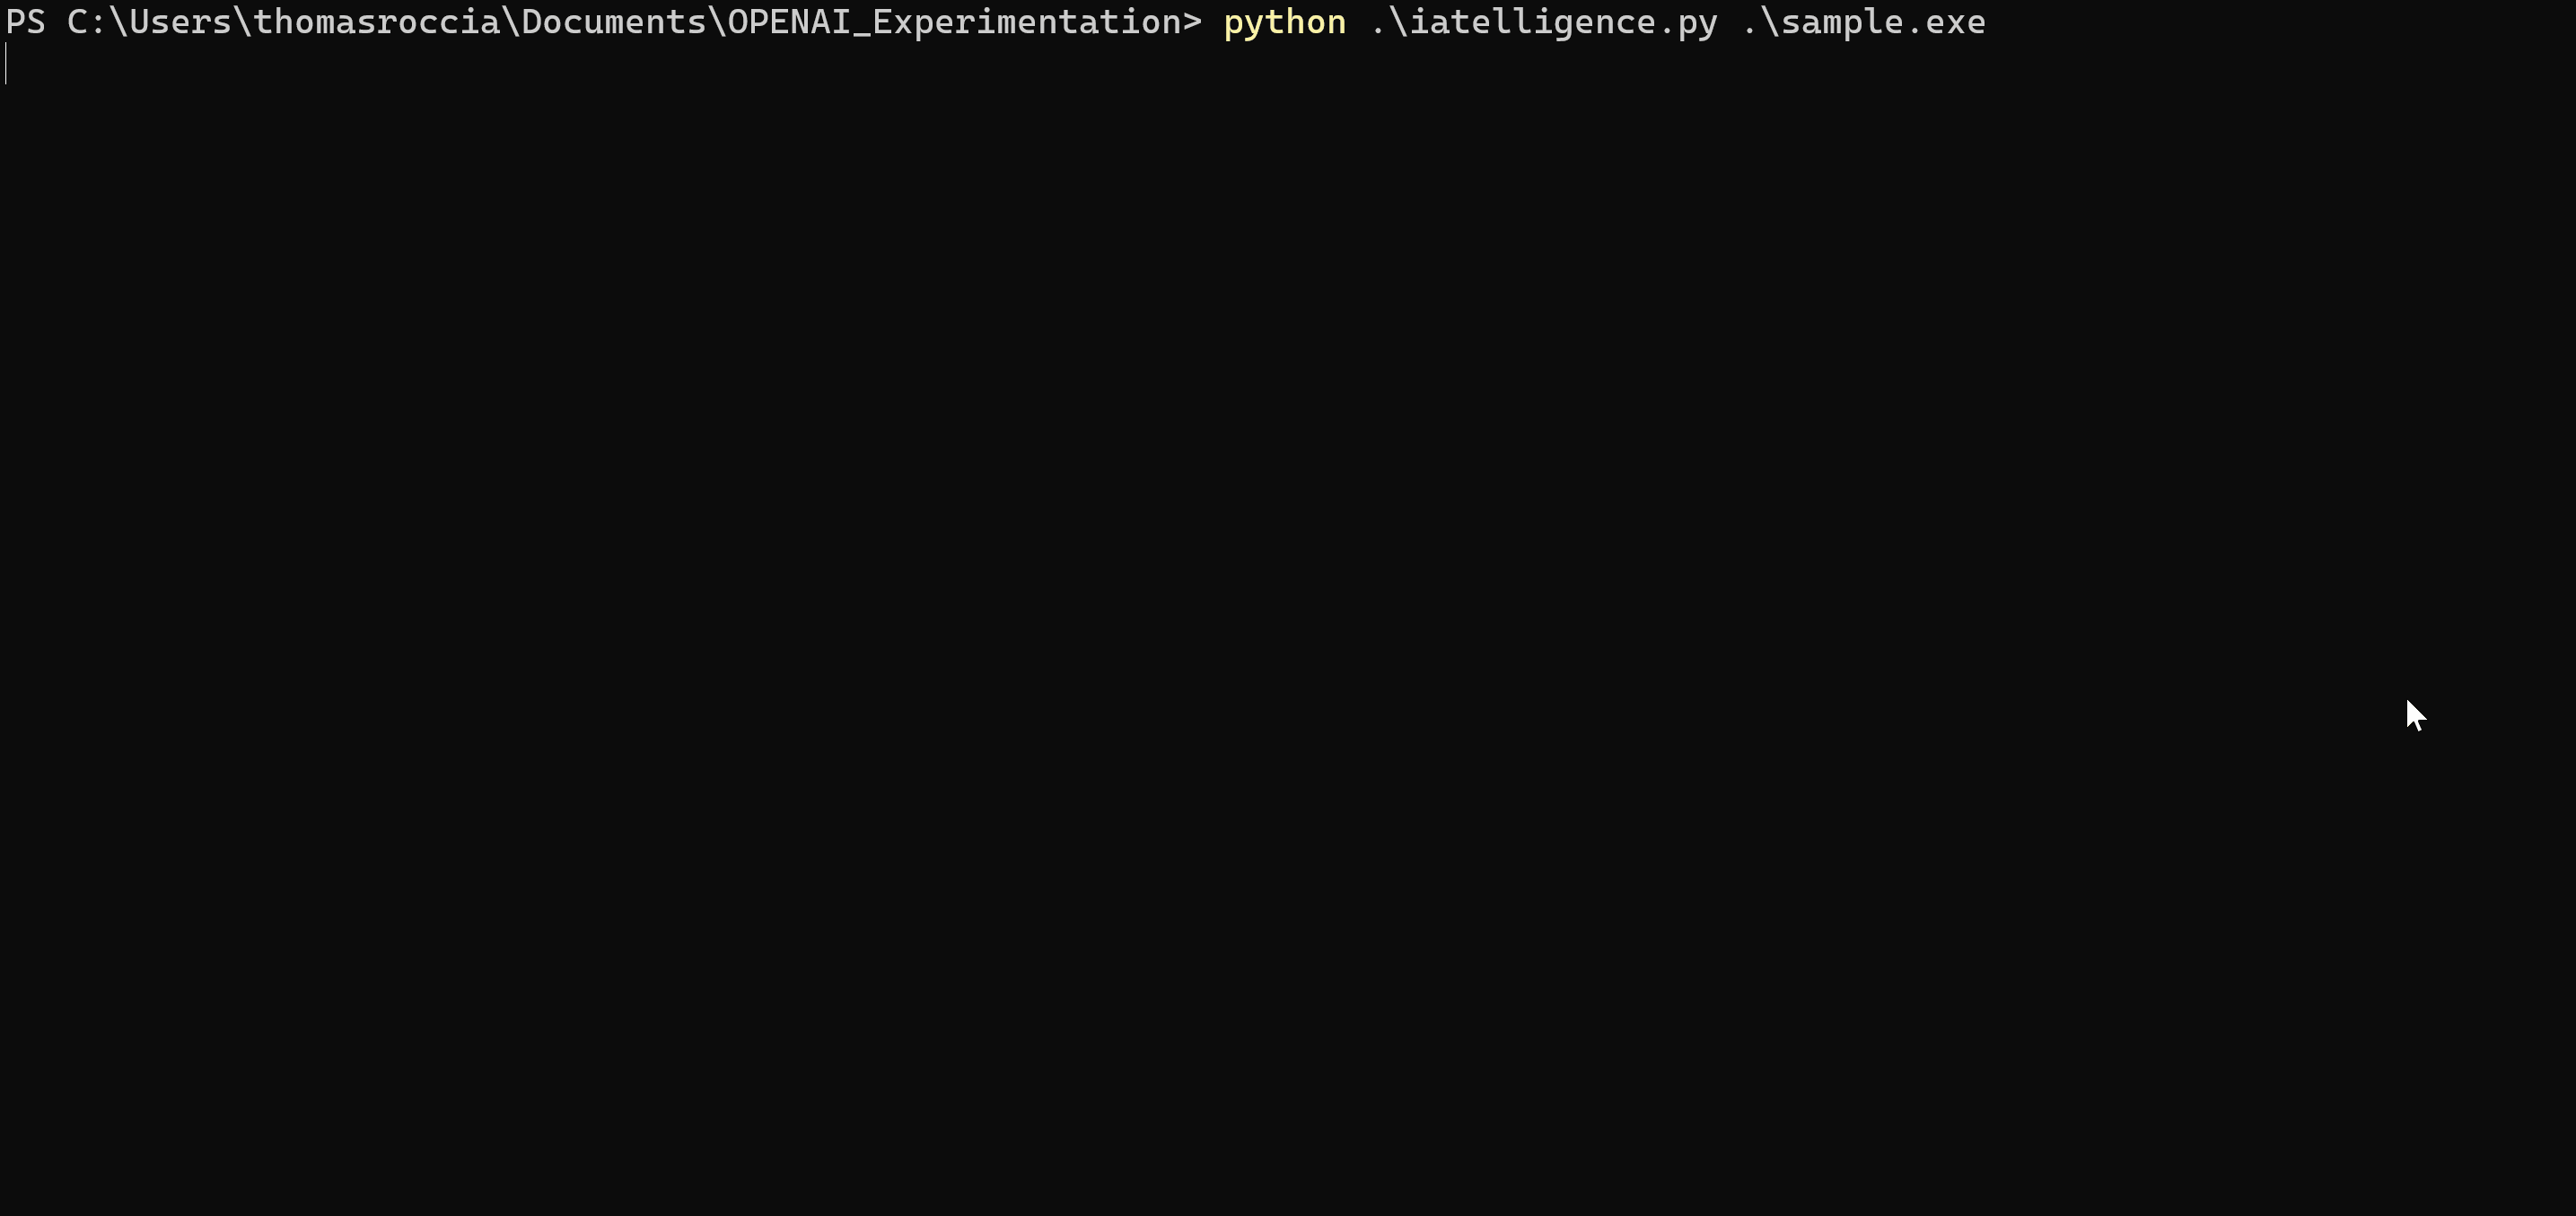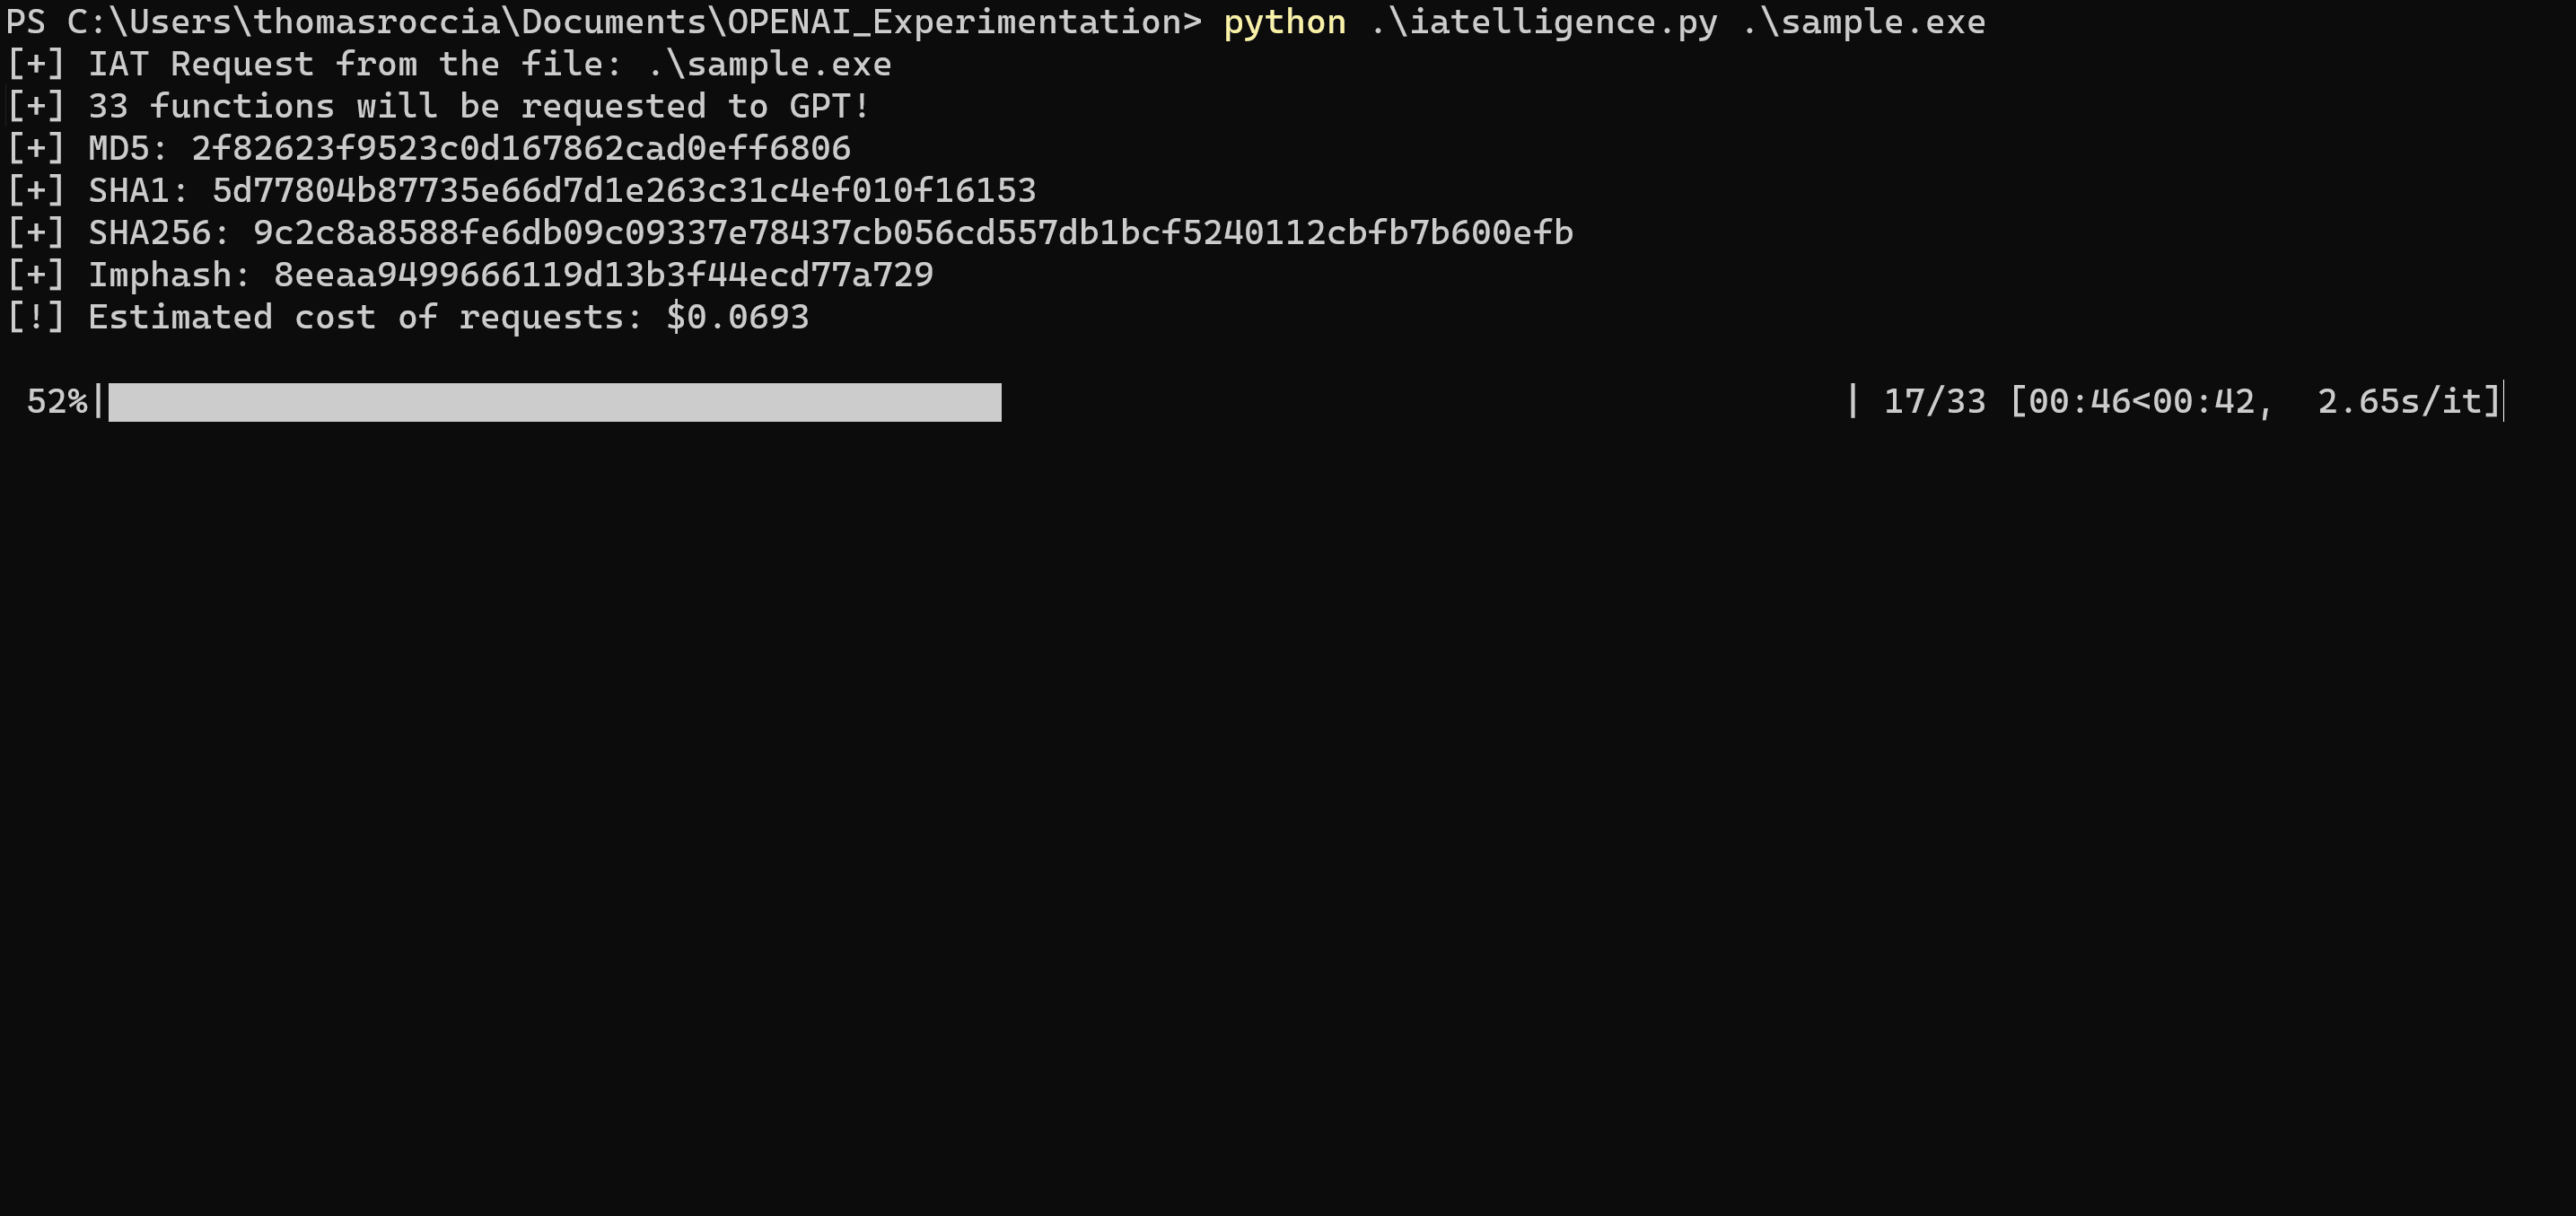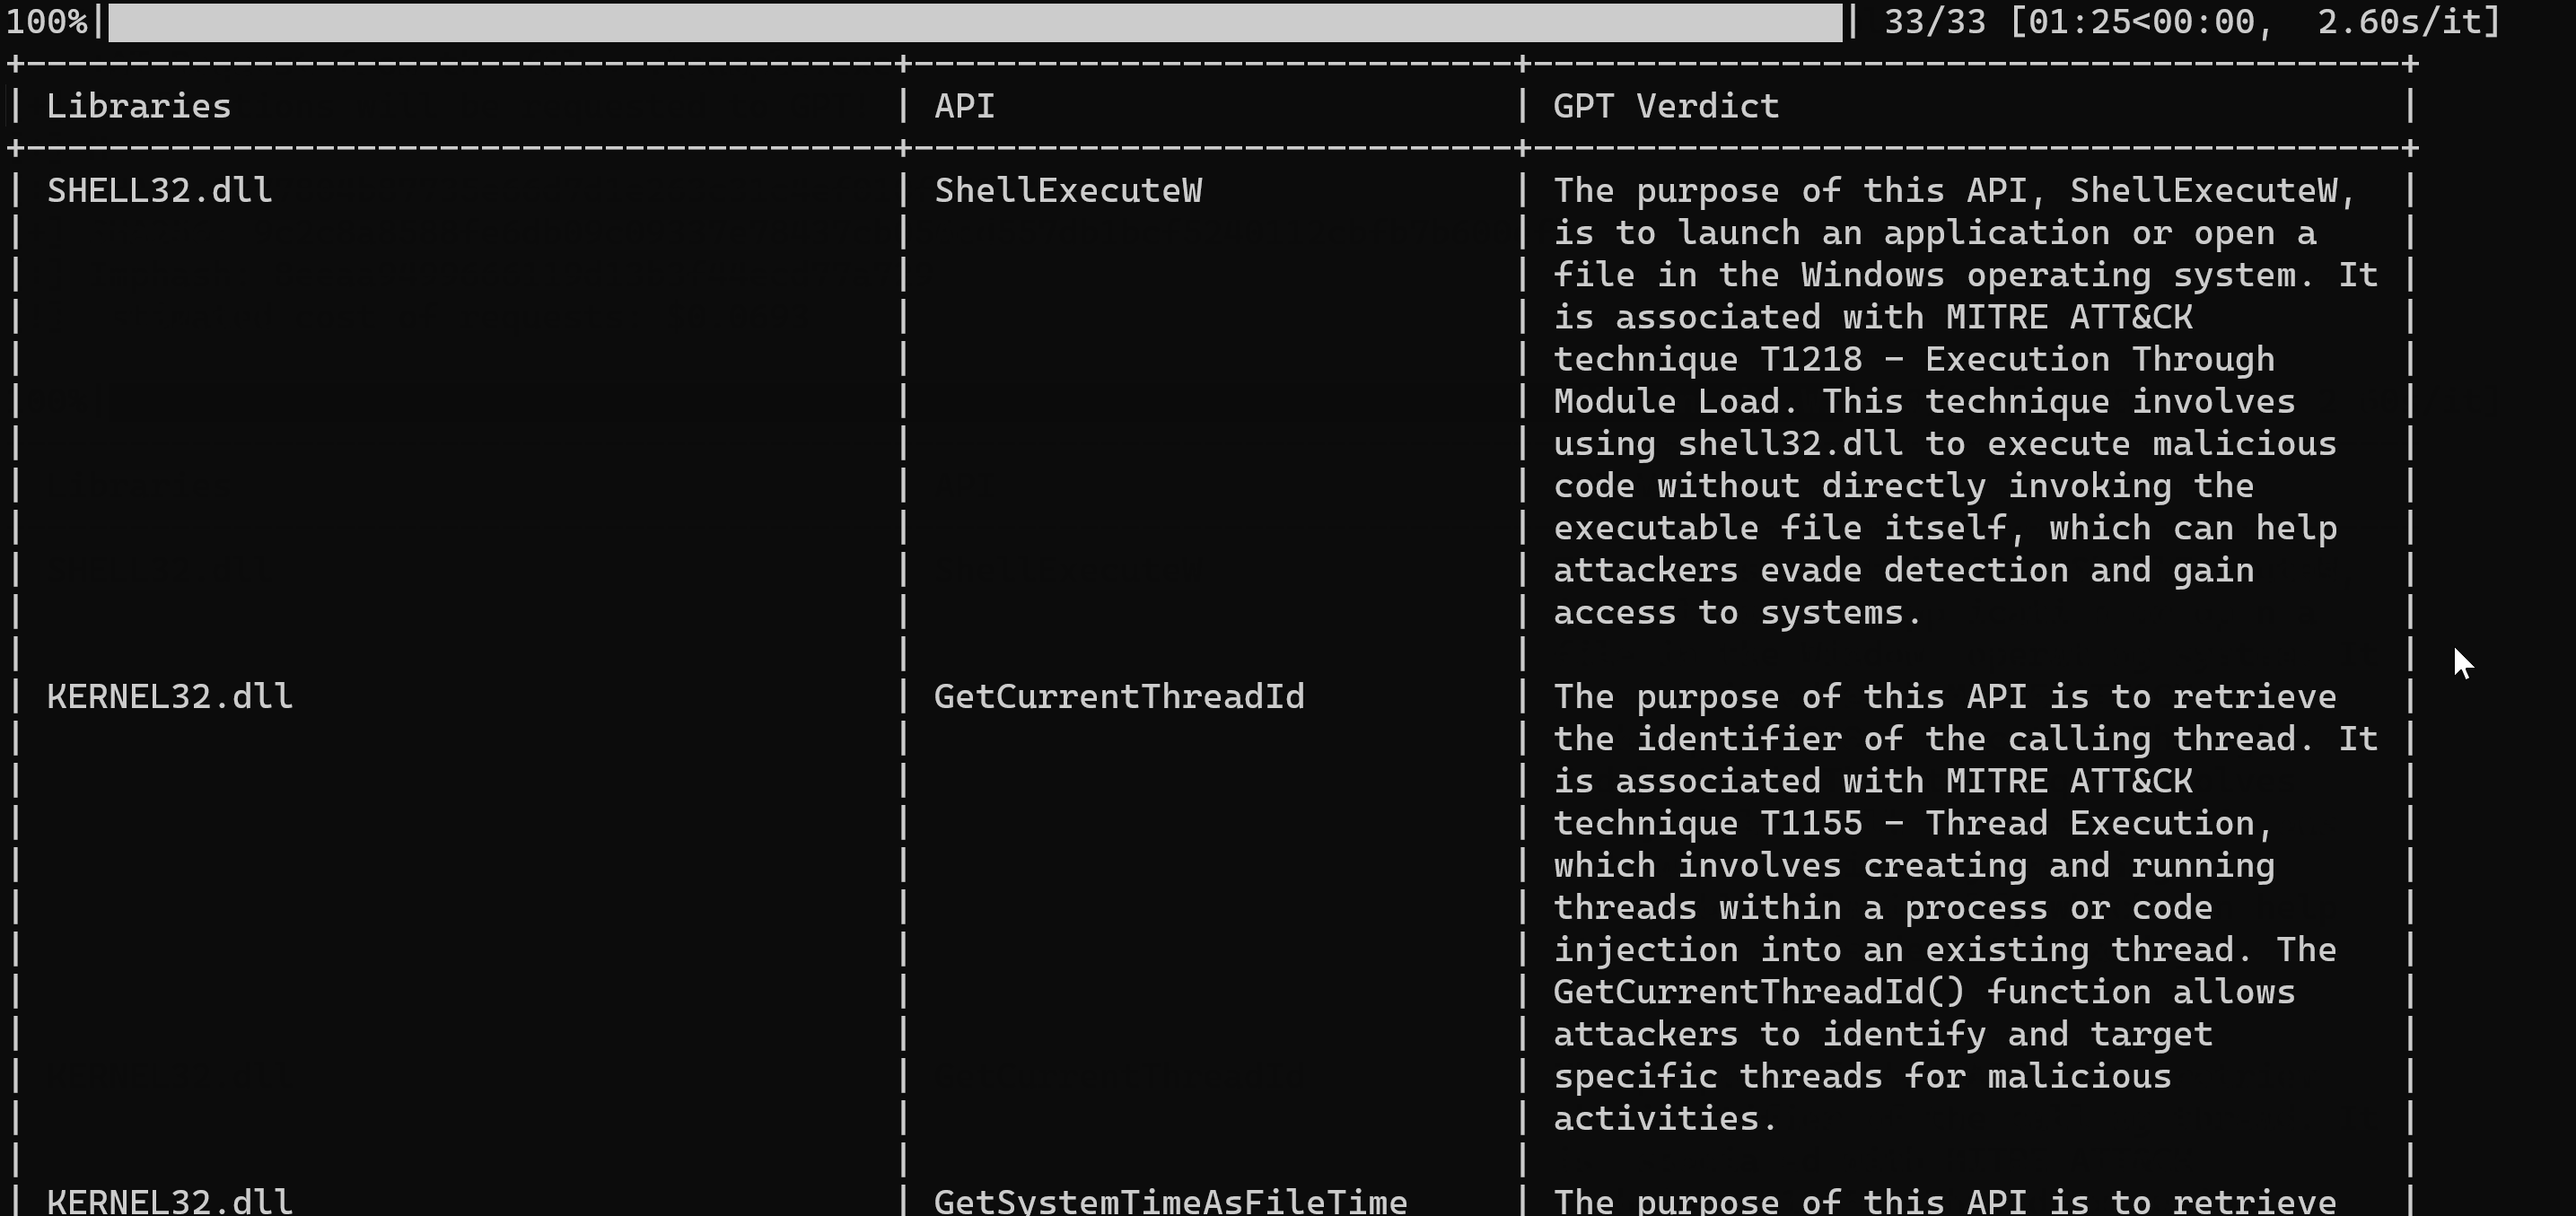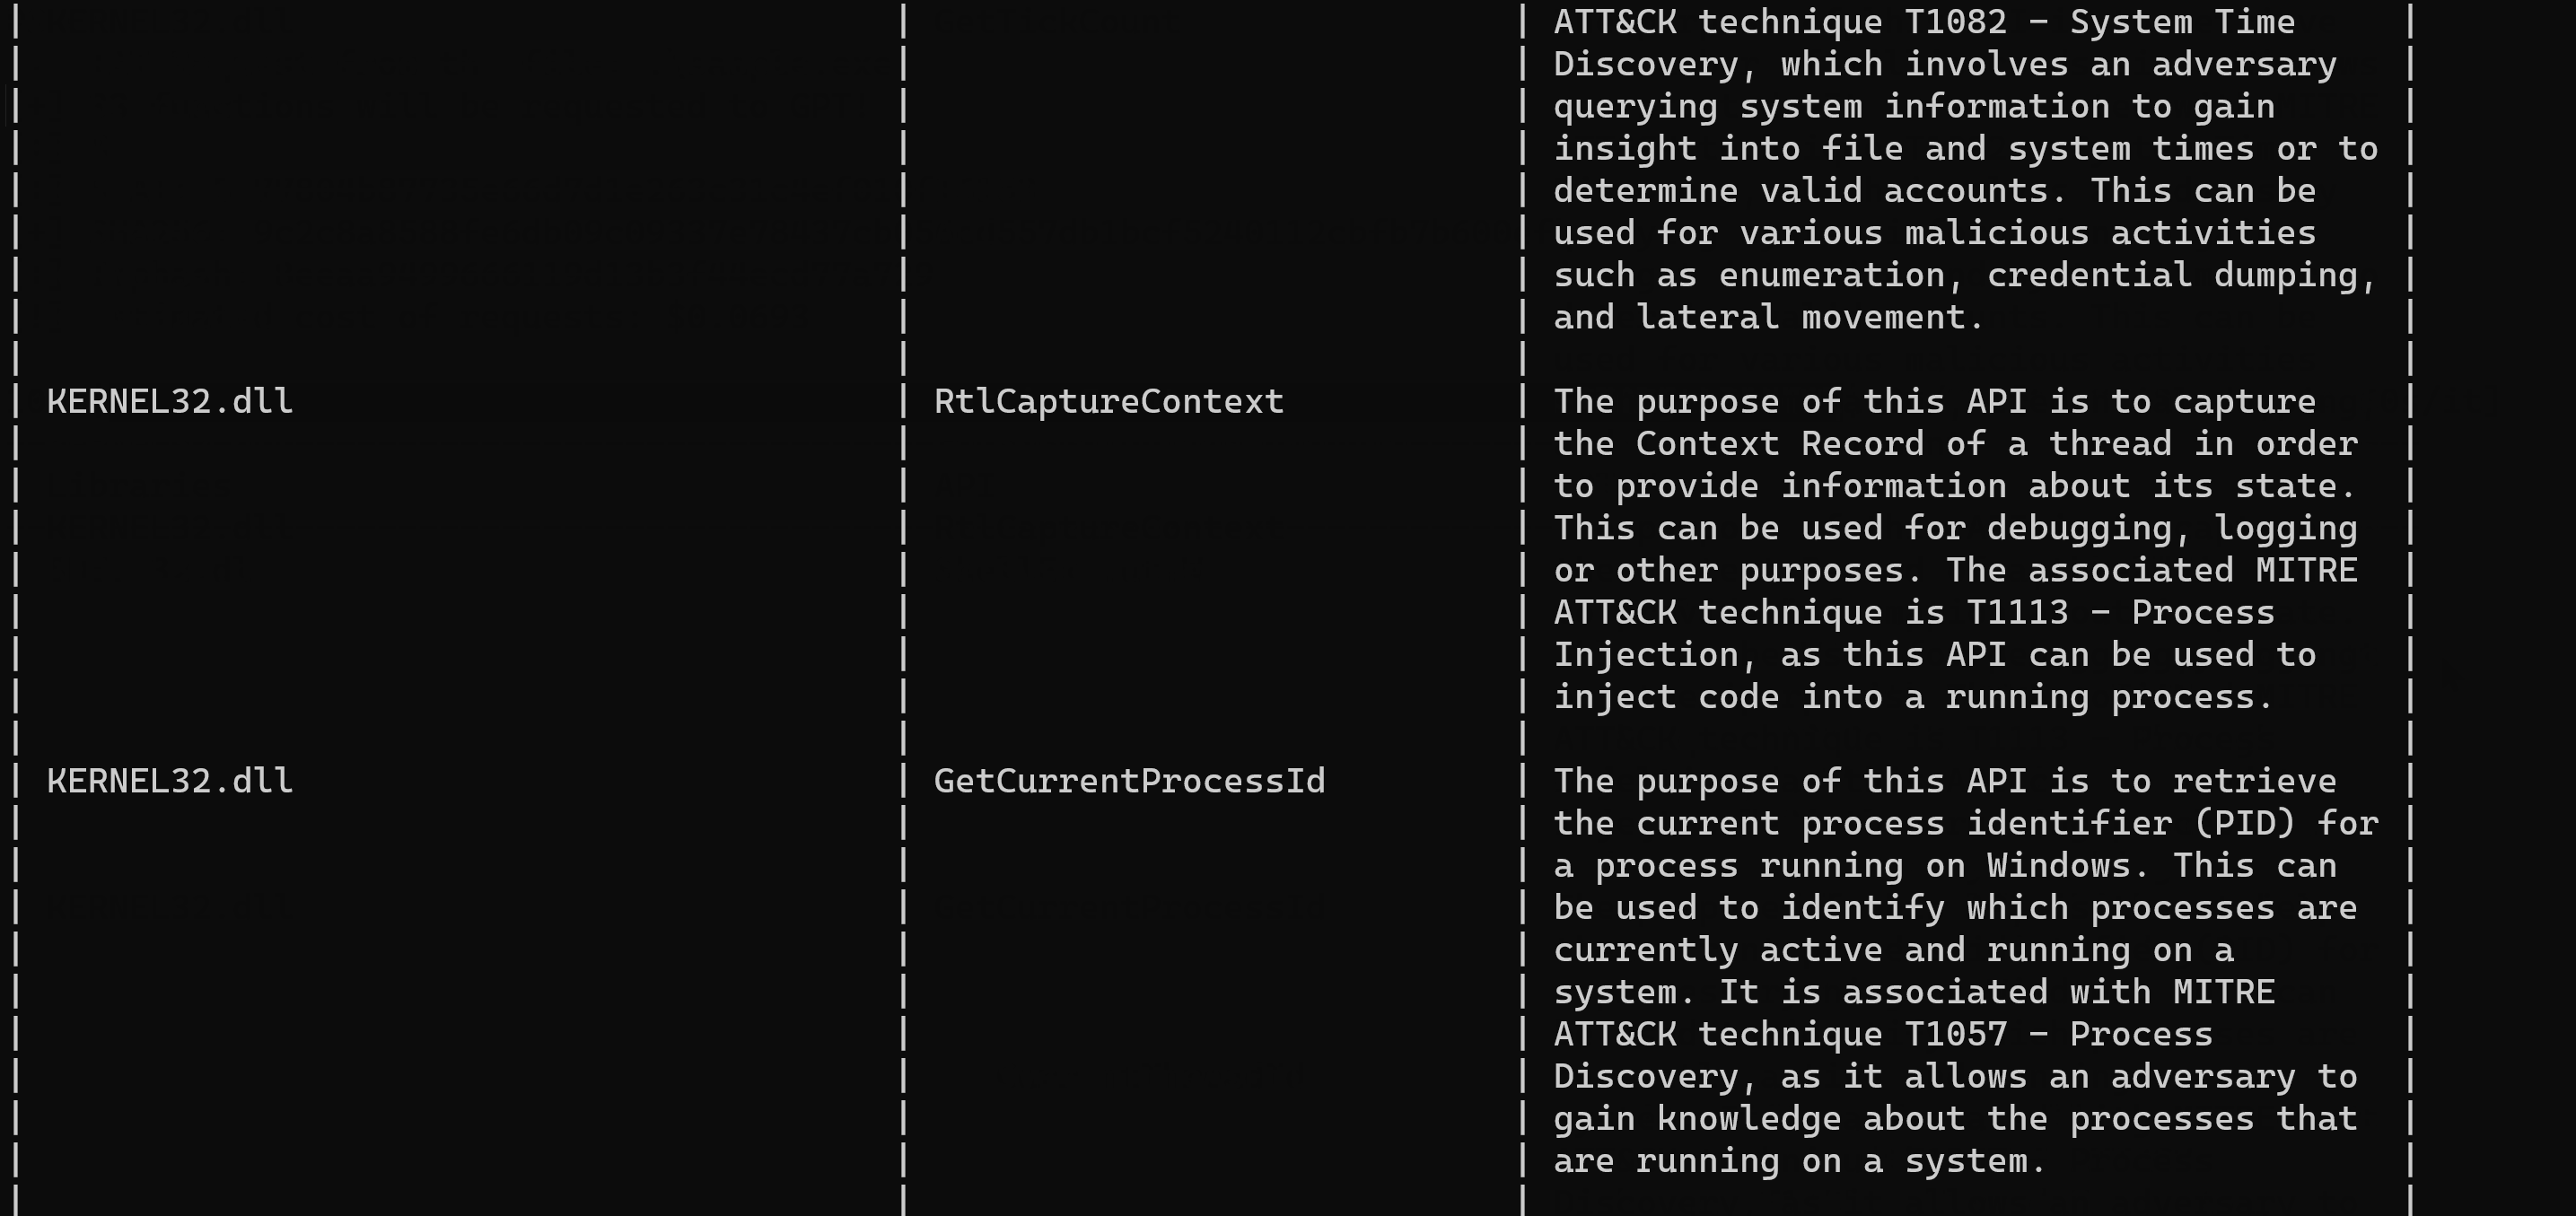
结果可以在表格中查看。以下是截断的摘录。
+------------------------------------------+-----------------------------+------------------------------------------+
| Libraries                                | API                         | GPT Verdict                              |
+------------------------------------------+-----------------------------+------------------------------------------+
| SHELL32.dll                              | ShellExecuteW               | The purpose of this API, ShellExecuteW,  |
|                                          |                             | is to launch an application or open a    |
|                                          |                             | file in the Windows operating system. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1218 - Execution Through      |
|                                          |                             | Module Load. This technique involves     |
|                                          |                             | using shell32.dll to execute malicious   |
|                                          |                             | code without directly invoking the       |
|                                          |                             | executable file itself, which can help   |
|                                          |                             | attackers evade detection and gain       |
|                                          |                             | access to systems.                       |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetCurrentThreadId          | The purpose of this API is to retrieve   |
|                                          |                             | the identifier of the calling thread. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1155 - Thread Execution,      |
|                                          |                             | which involves creating and running      |
|                                          |                             | threads within a process or code         |
|                                          |                             | injection into an existing thread. The   |
|                                          |                             | GetCurrentThreadId() function allows     |
|                                          |                             | attackers to identify and target         |
|                                          |                             | specific threads for malicious           |
|                                          |                             | activities.                              |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetSystemTimeAsFileTime     | The purpose of this API is to retrieve   |
|                                          |                             | the current system time as a file time   |
|                                          |                             | format. It is associated with the MITRE  |
|                                          |                             | ATT&CK technique T1124 - System Time     |
|                                          |                             | Discovery, which is used by adversaries  |
|                                          |                             | to gain insight into when certain        |
|                                          |                             | activities occurred or are scheduled to  |
|                                          |                             | occur. This allows them to perform       |
|                                          |                             | timing-based attacks and evade           |
|                                          |                             | detection.                               |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetTickCount                | The purpose of this API is to retrieve   |
|                                          |                             | the number of milliseconds since Windows |
|                                          |                             | was started. It is associated with MITRE |
|                                          |                             | ATT&CK technique T1082 - System Time     |
|                                          |                             | Discovery, which involves an adversary   |
|                                          |                             | querying system information to gain      |
|                                          |                             | insight into file and system times or to |
|                                          |                             | determine valid accounts. This can be    |
|                                          |                             | used for various malicious activities    |
|                                          |                             | such as enumeration, credential dumping, |
|                                          |                             | and lateral movement.                    |
|                                          |                             |                                          |
| KERNEL32.dll                             | RtlCaptureContext           | The purpose of this API is to capture    |
|                                          |                             | the Context Record of a thread in order  |
|                                          |                             | to provide information about its state.  |
|                                          |                             | This can be used for debugging, logging  |
|                                          |                             | or other purposes. The associated MITRE  |
|                                          |                             | ATT&CK technique is T1113 - Process      |
|                                          |                             | Injection, as this API can be used to    |
|                                          |                             | inject code into a running process.      |









