Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
CVE-2026-31431 — CVE-2026-31431 的漏洞利用程序,通过修改用户 ID 提升权限,附带验证脚本以及针对 algif_aead 漏洞的缓解措施说明。 | Kitploit
工具/GitHubGitHub/exploiteoom/cve-2026-31431
权限提升漏洞利用框架漏洞分析漏洞利用二进制分析
GitHubexploiteoom/cve-2026-31431

CVE-2026-31431

CVE-2026-31431 的漏洞利用程序,通过修改用户 ID 提升权限,附带验证脚本以及针对 algif_aead 漏洞的缓解措施说明。

查看仓库
21356个月前尚未审核
分享

CVE-2026-31431

Offensive

CopyFail 标准二进制文件

在 https://exploitroom.com 获取所有新的 CVE 警报


mail :: ~/Desktop/CVE-2026 » file *
exploit:            ELF 64-bit LSB executable, x86-64, version 1 (GNU/Linux), statically linked, BuildID[sha1]=9454dbdde0ac2d1a8981c06db89f24a4753ec3b7, for GNU/Linux 3.2.0, not stripped
payload:            ELF 64-bit LSB executable, x86-64, version 1 (SYSV), statically linked, BuildID[sha1]=9b0f16503767336bc8a821482933c1111aafa23a, stripped
verify_vulneurable: ELF 64-bit LSB executable, x86-64, version 1 (GNU/Linux), statically linked, BuildID[sha1]=a79c6ab7e9d14e60af8d7dfc1c102e3bc93a910b, for GNU/Linux 3.2.0, not stripped
mail :: ~/Desktop/CVE-2026 » 

使用方法

git clone https://github.com/ExploitEoom/CVE-2026-31431.git
cd CVE-2026-31431
chmod +x *
./verify_vulneurable
./exploit 

https://github.com/user-attachments/assets/27e0f28e-0cb8-438d-9fe4-ebd56035adad
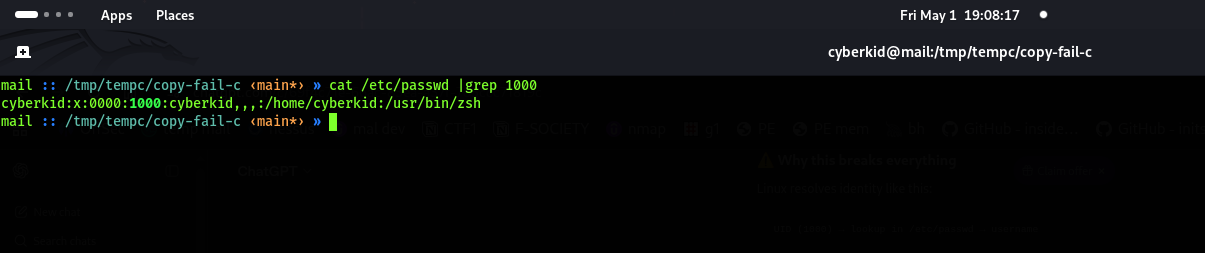
理解被利用的部分

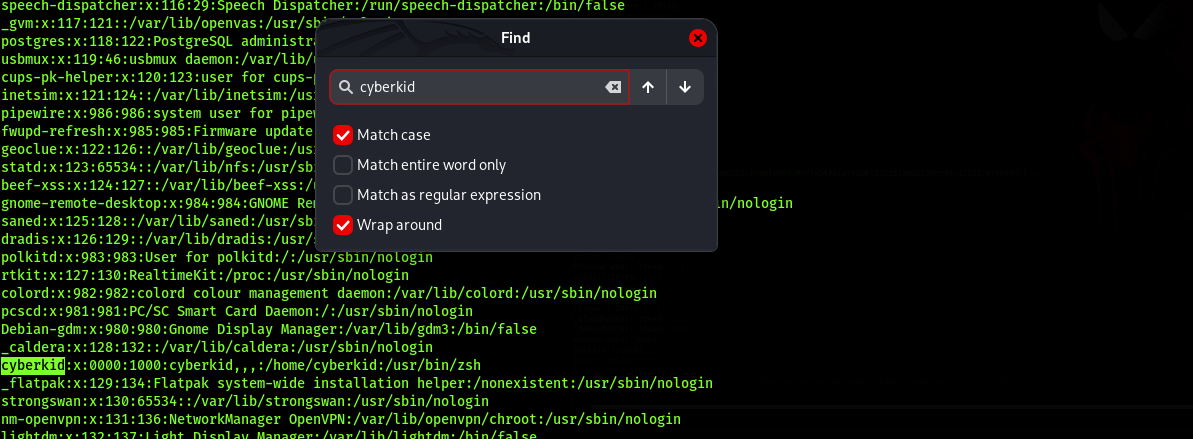
image id 从 1000 变为了 0000

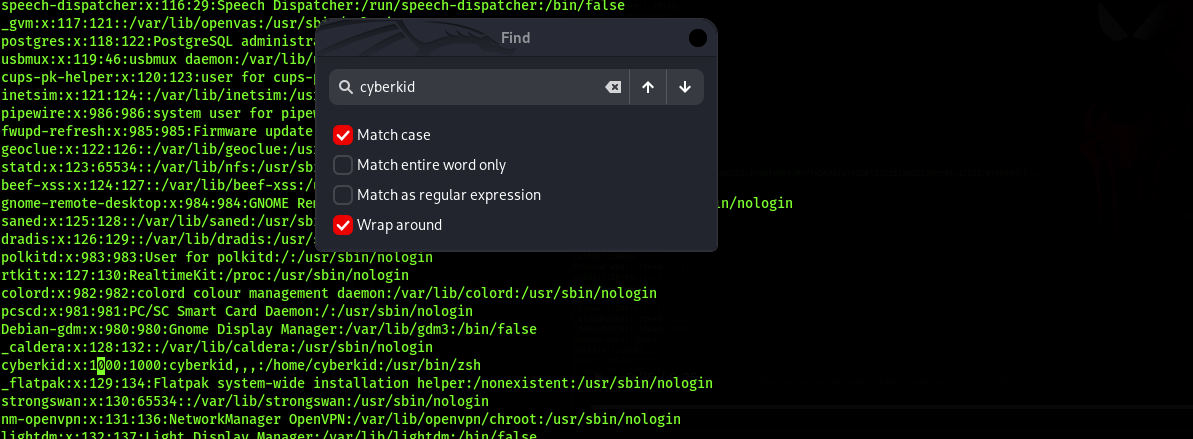
意外造成损害后如何恢复

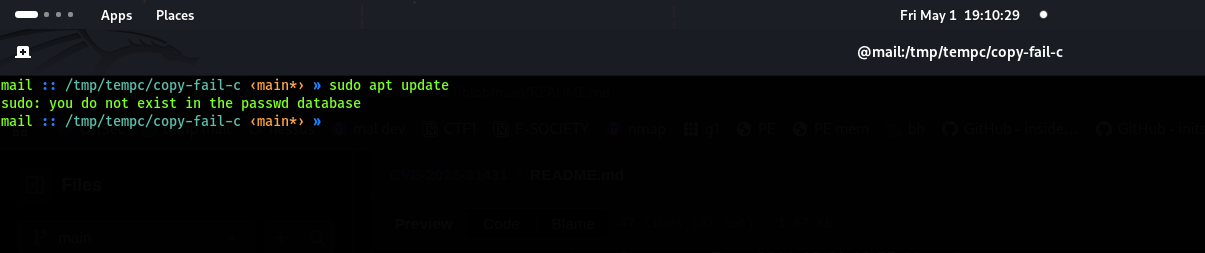
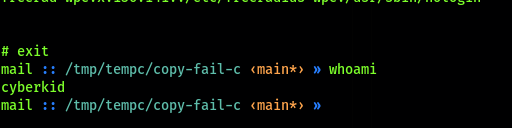
Screenshot From 2026-05-01 19-11-25 我们无法操作某些系统命令 Screenshot From 2026-05-01 19-10-30 使用 sudo su 以 root 身份进入,或使用 ./exploit 然后搜索你运行该 exploit 的用户 Screenshot From 2026-05-01 19-11-41 将 0000 替换为 1000 Screenshot From 2026-05-01 19-11-57 这样你就恢复了自己的用户
需要立即采取的措施:

  1. 临时缓解措施 –(检查 algif_aead 是否正在使用) 运行:
 lsmod | grep algif_aead

无输出(未在使用)→ 运行下面的禁用命令

echo "install algif_aead /bin/false" | sudo tee /etc/modprobe.d/disable-algif-aead.conf
sudo rmmod algif_aead 2>/dev/null || true
  1. 永久修复(执行前请仔细评估业务兼容性)

Debian/Ubuntu: sudo apt update && sudo apt upgrade -y CentOS/RHEL/Rocky/Alma: sudo dnf update -y 补丁:https://git.kernel.org/stable/c/a664bf3d603dc3bdcf9ae47cc21e0daec706d7a5


下载工具

最受欢迎

查看全部 →

发现我们社区最常用的工具。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 终极 OSINT 工具包:调查图谱、置信度评分、别名家族、地图、时间线和报告。49 个模块、400+ 个站点,无需 API 密钥。

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock 一键执行应用(CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    基于LLM的多智能体自主渗透测试平台,具备规划器/执行器智能体、资产与探索图谱、MITM流量记录以及漏洞复测功能。

    441
  • 4

    redforge

    cybersecurity91/redforge

    浏览器端红队工具包,包含 102 个离线工具,用于侦察、载荷生成、凭据攻击、加密、编码和交战报告。

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT 平台,可将 Shadowserver 报告导入 MongoDB,并将其重放为交互式地图、分析、发现、公告和高管仪表板。

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。

    264

探索所有工具

浏览我们的工具集合

查看所有工具 →