
go-http-proxy-to-socks v1.15.6
CLI MITM代理,将SOCKS4/SOCKS5转换为HTTP/HTTPS/HTTP2/HTTP3代理,具有透明TCP/UDP重定向、ARP/NDP/DNS欺骗、流量嗅探和数据包捕获功能。纯Go实现,无需libpcap。
GoHPTS - 用 Go 编写的 HTTP(S) 和 TCP/UDP 透明代理到 SOCKS4/SOCKS5 代理(链)



目录
- 简介
- 特性
- 安装
- 用法
- 透明代理
- 流量嗅探
- HTTP2 和 HTTP3 支持
- IPv4 和 IPv6 支持
- ARP 欺骗
- NDP 欺骗
- DNS 欺骗
- 数据包捕获
- 网络命名空间
- 混合服务器
- 链接
- 贡献
- 许可证
简介
GoHPTS CLI 工具是 HTTP 客户端与 SOCKS5 代理服务器或多个服务器(链)之间的桥梁。它在本地作为 HTTP 代理监听,接受标准 HTTP
或 HTTPS(通过 CONNECT)请求,并通过 SOCKS5 代理转发连接。灵感来自 http-proxy-to-socks 和 Proxychains
可能的用例:你需要通过 Postman 连接到外部 API,但该 API 只能从某个远程服务器访问。 以下命令将帮助你完成这样的任务:
通过 ssh 创建 SOCKS5 代理服务器:```shell
ssh -D 1080 -Nf
使用 `gohpts` 创建 HTTP 到 SOCKS5 的连接```shell
gohpts -s :1080 -l :8080
在 Postman 的代理配置中指定 http 服务器
功能特性
-
代理链功能
支持 SOCKS4/SOCKS5 代理的strict、dynamic、random、round_robin链 -
透明代理
支持redirect(SO_ORIGINAL_DST) 和tproxy(IP_TRANSPARENT) 模式 -
IPv4 和 IPv6 支持
可在IPv4-only、IPv6-only或dual stack模式下运行 -
TCP 和 UDP 透明代理
tproxy和tlocal(IP_TRANSPARENT) 处理 TCP 和 UDP 流量 -
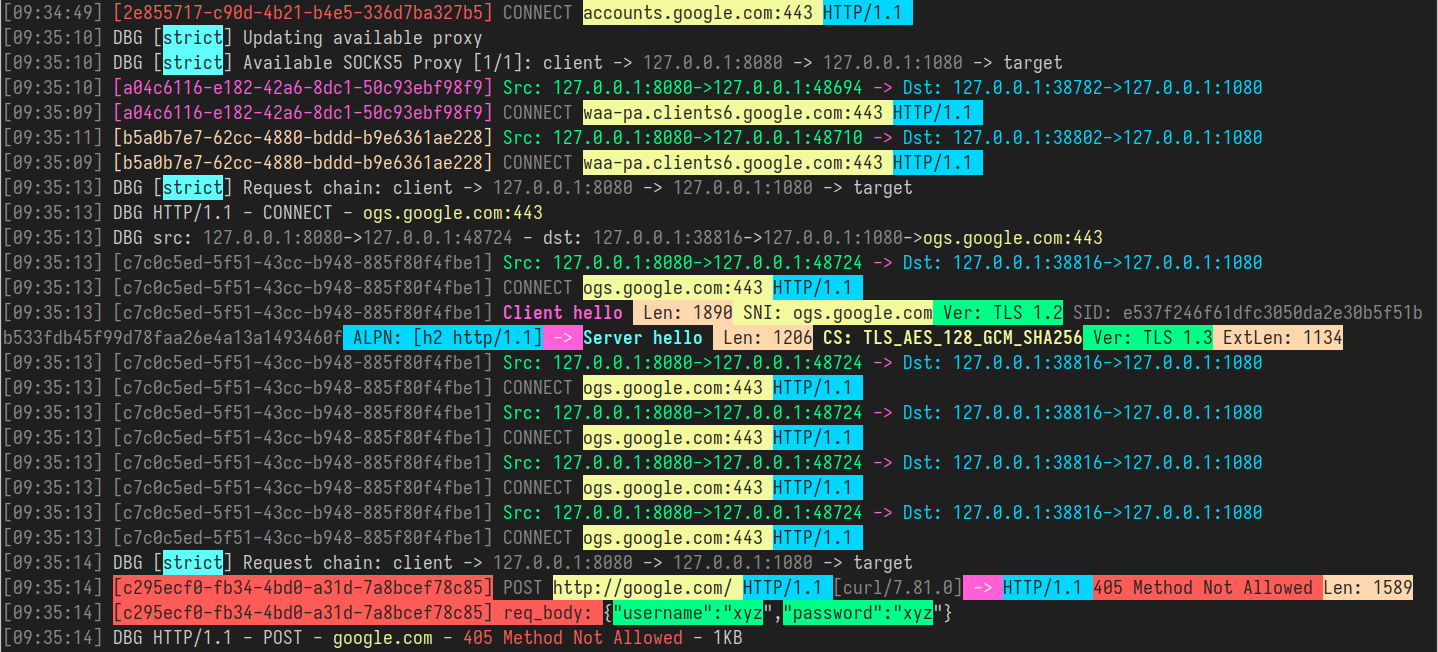
流量嗅探
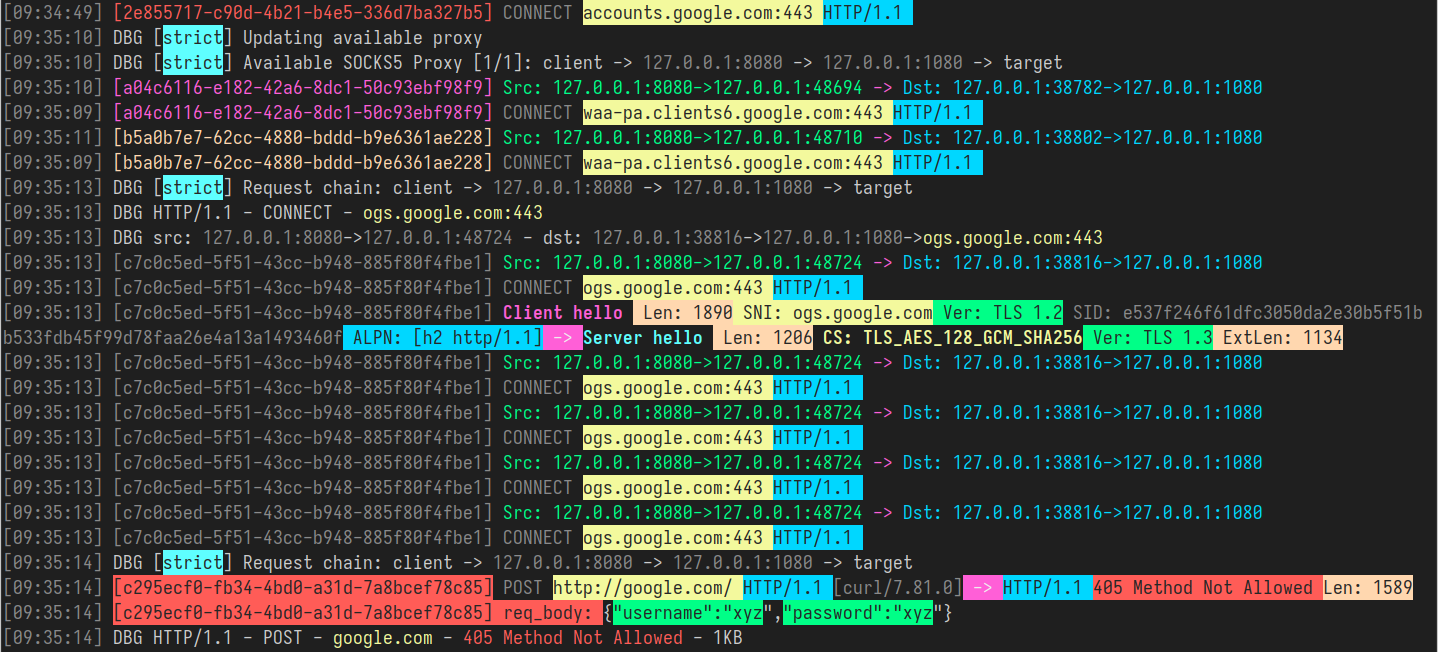
代理能够解析 HTTP 头、TLS 握手、DNS 消息等 -
ARP 欺骗
使用 ARP 欺骗方法代理整个子网 -
NDP 欺骗
使用路由器/邻居通告和 RDNSS 注入代理 IPv6 连接。 -
DNS 欺骗
通过 DNS 记录操纵将客户端重定向到任意域 -
数据包捕获
将流量捕获到 txt/pcap/pcapng 文件并使用 Wireshark 分析 -
DNS 泄漏保护
DNS 解析在 SOCKS5 服务器端进行。 -
CONNECT 方法支持
支持 HTTP CONNECT 隧道,启用 HTTPS 和其他基于 TCP 的协议。 -
HTTP2/HTTP3 支持
支持现代 HTTP/2 和 HTTP/3 传输,通过 TLS 1.3 实现高效的多路复用连接 -
网络命名空间支持
支持用于监听套接字和出站连接的自定义 Linux 网络命名空间 -
尾部标头支持
处理 HTTP 尾部标头 -
分块传输编码
处理分块和流式响应 -
SOCKS5 身份验证支持
支持 SOCKS5 代理的用户名/密码身份验证。 -
HTTP 身份验证支持
支持 HTTP 代理服务器的用户名/密码身份验证。 -
轻量且快速
以最小开销和高效请求处理为设计目标。 -
跨平台
兼容所有主流操作系统。
安装
- Arch Linux/CachyOS/EndeavourOS ```shell
yay -S gohpts
或使用 paru: ```shell
paru -S gohpts
- 从 [Releases](https://github.com/shadowy-pycoder/go-http-proxy-to-socks/releases) 页面下载适用于你平台的二进制文件:  ```shell
GOHPTS_RELEASE=v1.15.6; wget -v https://github.com/shadowy-pycoder/go-http-proxy-to-socks/releases/download/$GOHPTS_RELEASE/gohpts-$GOHPTS_RELEASE-linux-amd64.tar.gz -O gohpts && tar xvzf gohpts && mv -f gohpts-$GOHPTS_RELEASE-linux-amd64 gohpts && ./gohpts -h
- 使用
go install命令安装(需要 Go 1.26 或更高版本): ```shell CGO_ENABLED=0 go install -ldflags "-s -w" -trimpath github.com/shadowy-pycoder/go-http-proxy-to-socks/cmd/gohpts@latest
这会将 gohpts 二进制文件安装到你的 $GOPATH/bin 目录中。
- 从源码构建: ```shell
git clone https://github.com/shadowy-pycoder/go-http-proxy-to-socks.git
cd go-http-proxy-to-socks
make build
./bin/gohpts
- 在 docker 中运行: ```shell
docker run -it --privileged --network host -v "$PWD/gohpts.yaml:/config.yaml" shadowypycoder/gohpts:latest -f config.yaml
用法
[返回]```shell gohpts -h
/ | | | | | __ _ / ____|
| | __ ___ | || | |) | | | | (__
| | |_ |/ _ | __ | / | | _
| |__| | () | | | | | | | ) |
_|_/|| ||| || |___/
GoHPTS: HTTP(S) Proxy to SOCKS4/SOCKS5 proxy by shadowy-pycoder GitHub: https://github.com/shadowy-pycoder/go-http-proxy-to-socks Codeberg: https://codeberg.org/shadowy-pycoder/go-http-proxy-to-socks
Usage: gohpts [OPTIONS] OPTIONS: General: -h Show this help message and exit -v Show version and build information -D Run as a daemon (provide -logfile to see logs) -I Display list of network interfaces and exit -f Path to proxy configuration file in YAML format
Proxy: -l Address of HTTP proxy server (Default: "127.0.0.1:8080" for IPv4, "[::1]:8080" for IPv6) -s Address of SOCKS proxy server (Default: "127.0.0.1:1080" for IPv4 "[::1]:1080" for IPv6) -c Path to certificate PEM encoded file -k Path to private key PEM encoded file -U User for HTTP proxy (basic auth). This flag invokes prompt for password (not echoed to terminal) -u User for SOCKS proxy authentication. This flag invokes prompt for password (not echoed to terminal) -i Bind proxy to specific network interface (either by interface name or index) -4 Force IPv4 stack for TCP and UDP (Default: dual stack) -6 Force IPv6 stack for TCP and UDP (Default: dual stack) -socks4 Use SOCKS4/SOCKS4a protocol for upstream proxy and mixed server (default: SOCKS5/SOCKS5h) -nohttp Disable HTTP proxy server -nosocks Disable SOCKS upstream proxy -dns Use custom DNS server (Example: "8.8.8.8" or "2001:4860:4860::8888") -mixed Accept SOCKS connections on HTTP proxy server address
Logs: -d Show logs in DEBUG mode -j Show logs in JSON format -logfile Log file path (Default: stdout) -nocolor Disable colored output for logs (no effect if -j flag specified) -pprof Address of pprof server with profiling data
Sniffing: -sniff Enable traffic sniffing for HTTP and TLS -snifflog Sniffed traffic log file path (Default: the same as -logfile) -body Collect request and response body for HTTP traffic (credentials, tokens, etc)