
新发布Aug 23, 2026
vex8s v0.5.0
将Kubernetes上下文应用于扫描以抑制漏洞
Vex8s
 (此 logo 并非 AI 生成)
Vex8s 通过将容器漏洞与 Kubernetes 设置相关联,生成 VEX 文档,以确定哪些 CVE 在您的集群中实际可被利用。
请注意,这是一个实验性项目。情况可能会迅速变化。
工作原理
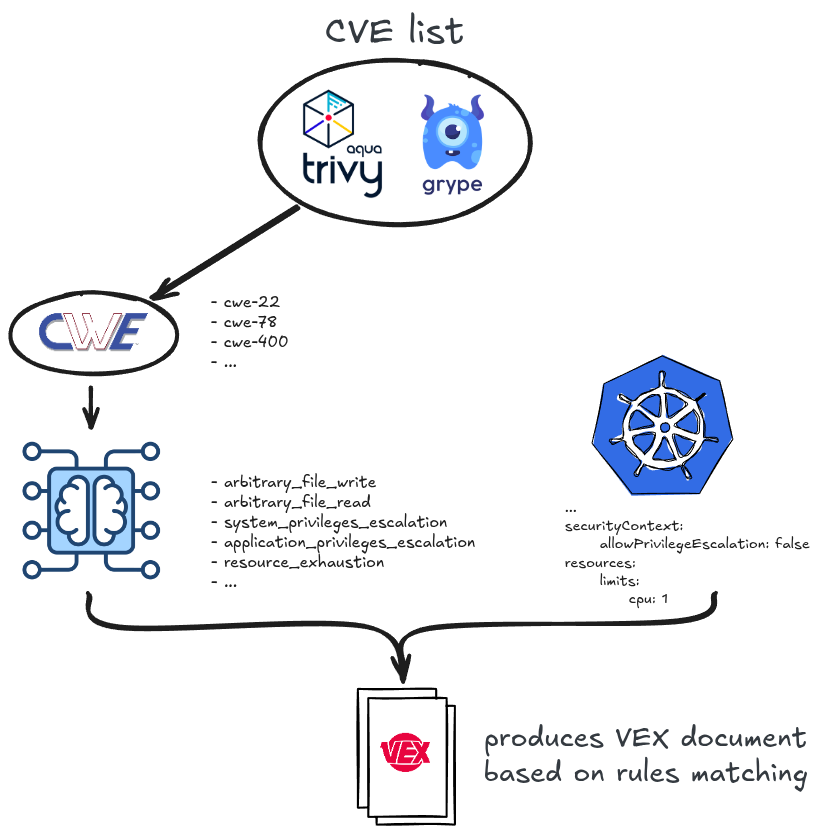
该项目旨在通过结合漏洞分类和 securityContext 分析,评估 Kubernetes 工作负载中已知 CVE 的可利用性。
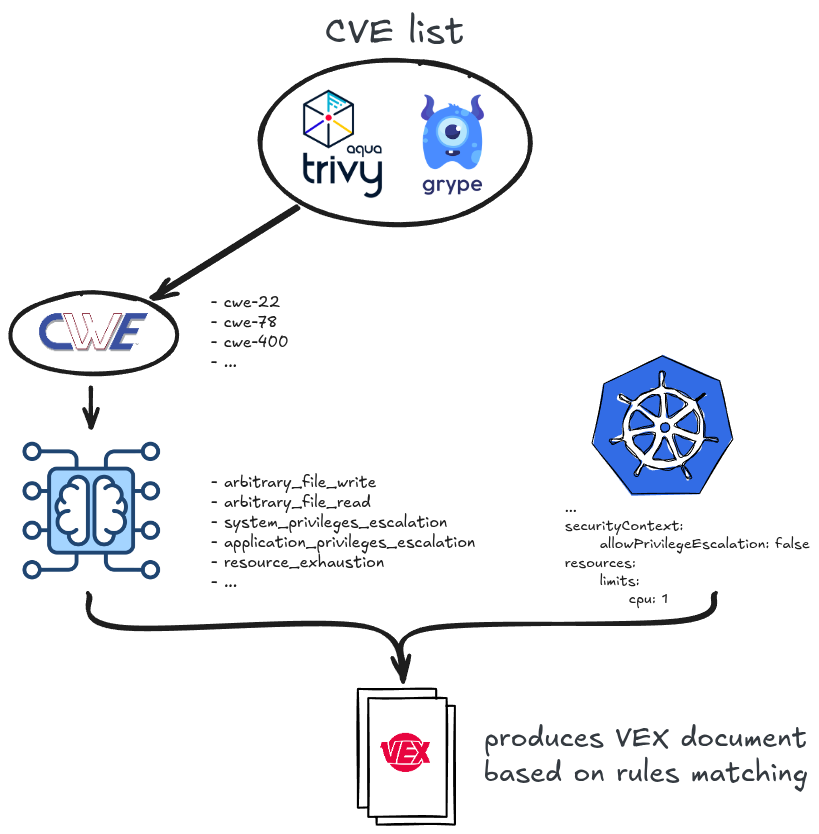
它基于以下概念:
- 每个 CVE 被归类为一个或多个漏洞类别(CWE)
- CVE 描述由嵌入式 ML 模型处理,以预测其利用类别。
- 将 CWE 和预测的利用类别结合起来,以确定该 CVE 是否可被缓解。
- 每个利用类别映射到一组可以阻止或减轻影响的 Kubernetes 设置。
- 通过解析 Kubernetes 清单,我们可以检查容器设置,以评估相关设置是否到位。
- 结合这两种分析,系统可以确定在给定的工作负载配置中,某个 CVE 是否可被利用。
- 如果结果为 CVE 缓解,我们会将其添加到最终的 VEX 文档中。
如需更深入的阅读,您可以查阅这篇论文:Environment-Aware Vulnerability Suppression Using Kubernetes Security Contexts and VEX
安装
您可以从 release 页面下载最新的二进制文件。
或者您可以手动构建:
make build
用法
vex8s 目前支持 2 种生成 VEX 文档的方式:
-
passive-mode:传入由
trivy或grype生成的漏洞报告。 -
active-mode:使用
trivy或grype引擎主动扫描镜像,然后根据结果生成文档。
被动模式(推荐)
使用 trivy:
# generate vulnerability report.
trivy image --format json --output nginx.trivy.json nginx:1.21.0

# generate VEX document by processing vulnerability report.
vex8s generate --manifest examples/nginx.yaml --report nginx.trivy.json --output nginx.vex.json

# scan again with VEX document to suppress vulnerabilities.
trivy image --vex nginx.vex.json --show-suppressed nginx:1.21.0
使用 grype 也可以实现同样的效果:
# generate sbom report.
grype --output cyclonedx-json --file nginx.grype.json nginx:1.21.0

# generate vulnerability report.
grype sbom:./nginx.grype.json --output json --file nginx.grype-vr.json

# generate VEX document by processing vulnerability report.
vex8s generate --manifest examples/nginx.yaml --report nginx.grype-vr.json --output nginx.vex.json

# scan sbom with VEX document to suppress vulnerabilities.
grype sbom:./nginx.grype.json --output table --vex nginx.vex.json --show-suppressed
主动模式
使用 trivy:
# scan the image and automatically generate VEX document.
vex8s generate --manifest examples/nginx.yaml --scan.engine trivy --output nginx.vex.json

# scan again with VEX document to suppress vulnerabilities.
trivy image --vex nginx.vex.json --show-suppressed nginx:1.21.0
使用 grype 也可以实现同样的效果:
# generate sbom report.
grype --output cyclonedx-json --file nginx.grype.json nginx:1.21.0

# scan the image and automatically generate VEX document.
vex8s generate --manifest examples/nginx.yaml --scan.engine grype --output nginx.vex.json

# scan sbom with VEX document to suppress vulnerabilities.
grype sbom:./nginx.grype.json --output table --vex nginx.vex.json --show-suppressed
分类器
每个 CVE 被归类为一个或多个利用类别,这些类别驱动缓解决策。vex8s 通过 --classifier 支持三种分类器引擎:
embedded(默认):一个离线 ONNX ML 模型,捆绑在二进制文件中。无需网络访问。gemini:使用 Google 的 Gemini LLM 对 CVE 描述进行分类。需要GEMINI_API_KEY环境变量(可选GEMINI_MODEL)。ollama:使用本地运行的 Ollama 服务器对 CVE 描述进行分类。请先拉取一个模型,例如qwen2.5:3b-instruct(可选设置OLLAMA_HOST/OLLAMA_MODEL)。
export GEMINI_API_KEY="your-api-key"

vex8s generate --manifest examples/nginx.yaml --report nginx.trivy.json \
  --output nginx.vex.json --classifier ollama
请参阅文档,特别是用户指南,以获取完整演练、Gemini 和 Ollama 分类器设置以及完整的标志参考。
参考资料
本项目受 Akihiro Suda 的项目 vexllm 启发。