


Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
分类

权限提升

用于在受损系统上获取更高级别权限或未经授权访问的工具。

Kitploit 推荐

精选工具

10 已选择
PEASS-ng preview#1

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k18小时41分前
PrivescCheck preview#2

PrivescCheck

GitHubitm4n/privesccheck
3.9k25天前
LinEnum preview#3

LinEnum

GitHubrebootuser/linenum
8.0k6年前
linux-smart-enumeration preview#4

linux-smart-enumeration

GitHubdiego-treitos/linux-smart-enumeration
4.0k6个月前
WinPwn preview#5

WinPwn

GitHubs3cur3th1ssh1t/winpwn
3.7k1年前
wesng preview#6

wesng

GitHubbitsadmin/wesng
4.9k21小时32分前
BeRoot preview#7

BeRoot

GitHubalessandroz/beroot
2.6k2年前
PowerUpSQL preview#9

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
Seatbelt preview#10

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
SharpUp preview#11

SharpUp

GitHubghostpack/sharpup
1.5k3年前
最新相关性最受欢迎最近更新
4622 结果
DirCreate2System preview

DirCreate2System

GitHubbinderlabs/dircreate2system

武器化利用 Windows 错误报告中的特权目录创建漏洞以获取 NT SYSTEM 权限

privilege-escalationexploitationpost-exploitation+4
3643年前
impersonate preview

impersonate

GitHubsensepost/impersonate

一个Windows令牌模拟工具

privilege-escalationimpersonation-toolslateral-movement+3
3273年前
Mind-Maps preview

Mind-Maps

GitHubimran-parray/mind-maps

思维导图:若干事物的梳理

privilege-escalationreconnaissancevulnerability-analysis+9
2.7k3年前
HENlo preview

HENlo

GitHubtheofficialflow/henlo

适用于所有 PS Vita 固件的 WebKit+Kernel 漏洞利用链
embedded-systems-securityprivilege-escalationexploitation+2
2353年前
RazerEoP preview

RazerEoP

GitHubwh04m1001/razereop

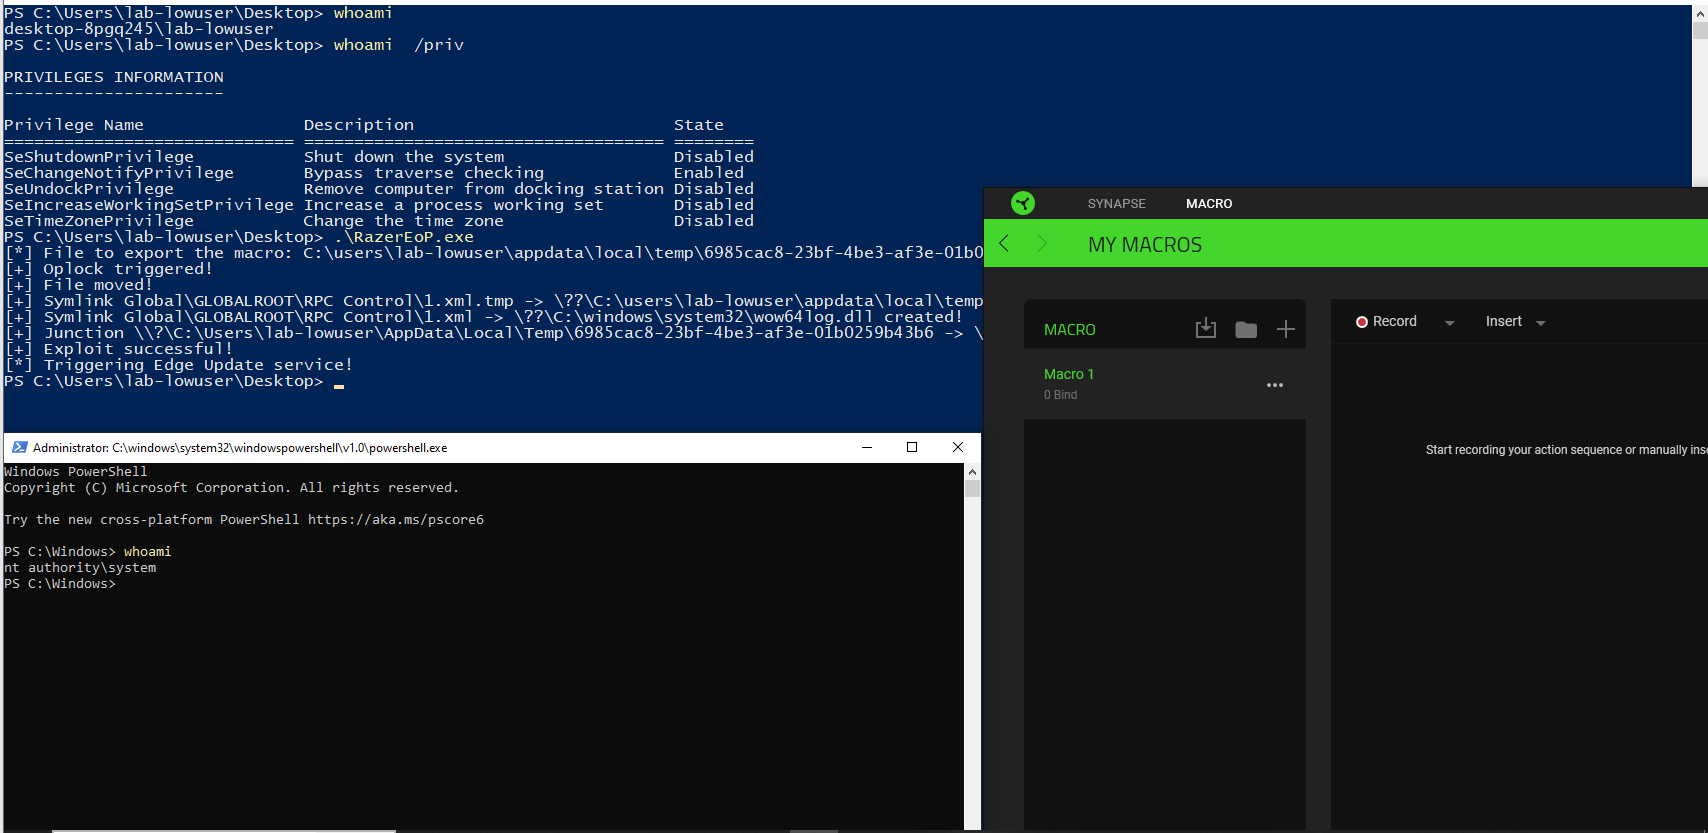
针对 Razer Synapse 3 Macro SYSTEM 服务中任意文件删除/移动漏洞的概念验证漏洞利用程序,演示受影响版本上的本地权限提升。

privilege-escalationvulnerability-analysisexploitation
293年前
RToolZ preview

RToolZ

GitHubomribaso/rtoolz

一个隐蔽的 Lsass 转储工具 - 可利用 ProcExp152.sys 驱动程序转储 PPL Lsass,不调用 dbghelp.lib。

privilege-escalationexploitationpost-exploitation+2
3263年前
SharpStartWebclient preview

SharpStartWebclient

GitHubeversinc33/sharpstartwebclient

以编程方式从非特权会话启动 WebClient,以实现诱人的权限提升。

privilege-escalationlateral-movementpost-exploitation+2
803年前
amd-ryzen-master-driver-v17-exploit preview

amd-ryzen-master-driver-v17-exploit

GitHubtijme/amd-ryzen-master-driver-v17-exploit

Cobalt Strike (CS) 信标对象文件(BOF),用于利用 AMD 的 Ryzen Master 驱动程序(版本 17)进行内核利用。

privilege-escalationexploit-frameworksexploitation+4
1603年前
SeManageVolumeExploit preview

SeManageVolumeExploit

GitHubcsenox/semanagevolumeexploit

滥用 SeManageVolumePrivilege 的 Windows 本地权限提升漏洞利用,授予对 C:\ 驱动器的完全访问权限,并通过覆盖 PrintConfig.dll 获得 SYSTEM shell。

privilege-escalationexploitationpost-exploitation+3
2033年前
RasmanPotato preview

RasmanPotato

GitHubcrisprss/rasmanpotato

滥用模拟权限,像其他 Potato 一样从服务账户提权到 SYSTEM

privilege-escalationexploitationpost-exploitation+2
4063年前
POC preview

POC

GitHubjhftss/poc

一个公开的漏洞利用代码与POC集合,涵盖我所发现的安全漏洞

privilege-escalationvulnerability-analysisexploitation+1
41610个月前
psexec_noinstall preview

psexec_noinstall

GitHubmzhmo/psexec_noinstall

该仓库包含 psexec,它将帮助利用被遗忘的管道。

privilege-escalationexploitationpost-exploitation+3
1732年前
PetitPotato preview

PetitPotato

GitHubwh0amitz/petitpotato

通过 PetitPotam 实现本地权限提升(滥用 impersonate 权限)。

privilege-escalationexploitationimpersonation-tools+3
4663年前
Elevate-System-Trusted-BOF preview

Elevate-System-Trusted-BOF

GitHubmr-un1k0d3r/elevate-system-trusted-bof

Cobalt Strike Beacon 对象文件,通过 SetThreadToken 令牌模拟将活动 Beacon 提升至 SYSTEM 并授予 TrustedInstaller 权限。

privilege-escalationpost-exploitationcommand-and-control+2
1813年前
PoC-Malware-TTPs preview

PoC-Malware-TTPs

GitHubknight0x07/poc-malware-ttps

PoC-Malware-TTPs

privilege-escalationpersistence-mechanismspost-exploitation+4
483年前
redteamguides.github.io preview

redteamguides.github.io

GitHubredteamguides/redteamguides.github.io

红队指南

privilege-escalationreconnaissanceexploitation+6
1462年前
Awesome_Malware_Techniques preview

Awesome_Malware_Techniques

GitHubfr0gger/awesome_malware_techniques

这是一个关于恶意软件技术的资源仓库。

privilege-escalationpersistence-mechanismsmalware-analysis+4
8643年前
OwnershipStealer preview

OwnershipStealer

GitHubadpunisher/ownershipstealer

适用于 Windows 的命令行工具,可启用 SeTakeOwnershipPrivilege 并将文件所有权修改为当前用户,从而授予对原本受保护文件的访问权限。

privilege-escalationpost-exploitationpenetration-testing+2
283年前
上一页1…575859…100下一页






