

Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
后渗透利用 — 第 96 页 | Kitploit
分类

后渗透利用

用于在受损系统和网络中维护访问、探索和扩大控制的工具。

Kitploit 推荐

精选工具

10 已选择
NetExec preview#1

NetExec

GitHubpennyw0rth/netexec
5.8k20小时44分前
impacket preview#2

impacket

GitHubfortra/impacket
16.0k22小时27分前
mimikatz preview#3

mimikatz

GitHubgentilkiwi/mimikatz
21.8k6个月前
PEASS-ng preview#4

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k22小时50分前
Rubeus preview#5

Rubeus

GitHubghostpack/rubeus
5.1k11个月前
Seatbelt preview#6

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
Empire preview#7

Empire

GitHubbc-security/empire
5.2k1个月前
sliver preview#8

sliver

GitHubbishopfox/sliver
11.7k12小时53分前
LaZagne preview#10

LaZagne

GitHubalessandroz/lazagne
11.0k1年前
PowerUpSQL preview#11

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
最新相关性最受欢迎最近更新
6165 结果
MSRKit preview

MSRKit

GitHubrurixis/msrkit

一种将 ROP 链与 WRMSR 原语结合使用以调用内核函数,并通过 BYOVD(AmdTools64.sys)映射未签名驱动程序的概念

privilege-escalationexploitationreverse-engineering+5
671个月前
dolos_cloak preview

dolos_cloak

GitHubfkasler/dolos_cloak

自动化802.1x绕过

lateral-movementpost-exploitationnetwork-security+3
896年前
ACEshark preview

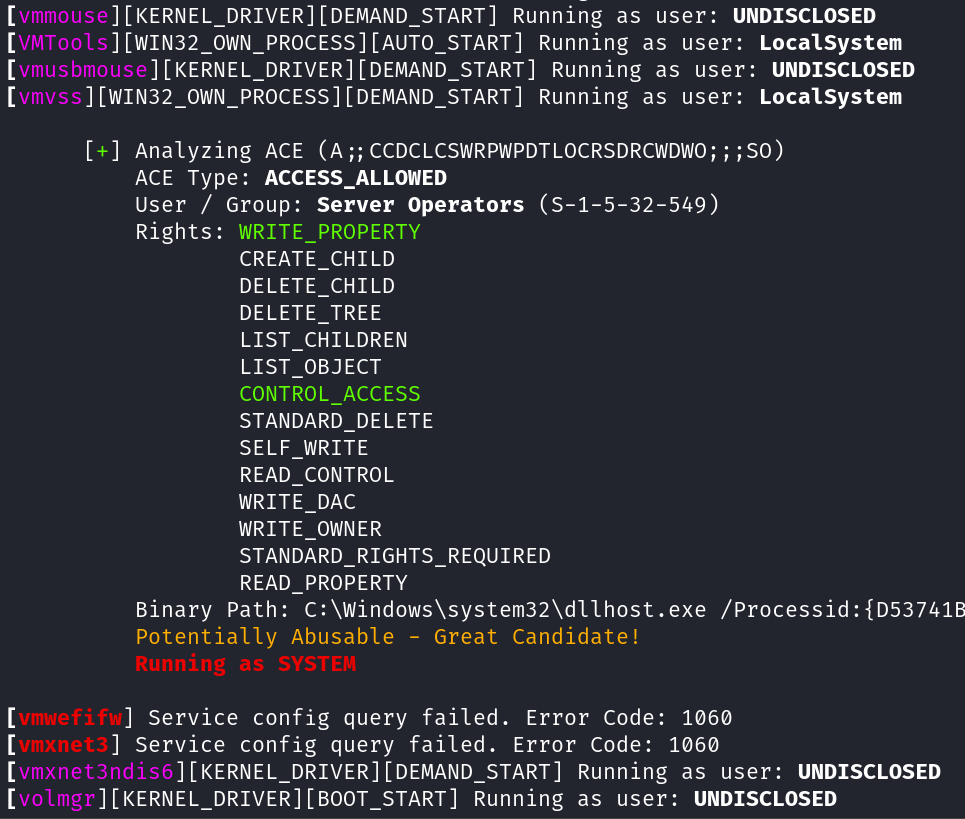
ACEshark

GitHubt3l3machus/aceshark

ACEshark 是一款用于快速提取和分析 Windows 服务配置及访问控制项(Access Control Entries)的实用工具,无需依赖 accesschk.exe 或其他非原生二进制文件。
privilege-escalationvulnerability-analysisconfiguration-auditing+4
1481年前
createdump preview

createdump

GitHubrweijnen/createdump

利用 WindowsApp 的 createdump 工具获取 lsass 转储
password-attacksimpersonation-toolspost-exploitation+1
1512年前
HiveJack preview

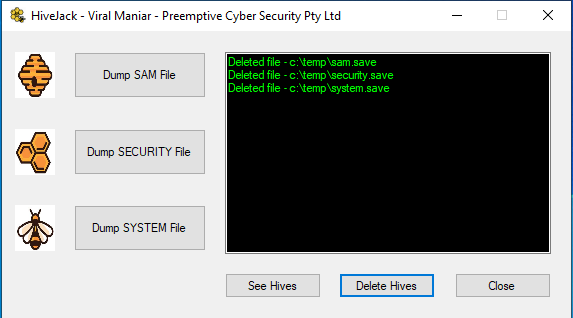
HiveJack

GitHubviralmaniar/hivejack

此工具可在内部渗透测试中使用,用于从已被攻陷的主机上转储Windows凭据。它能够转储SYSTEM、SECURITY和SAM配置单元,并且在复制到攻击者机器后,提供删除这些文件以清除痕迹的选项。
lateral-movementpost-exploitationpenetration-testing
1116年前
RegPwnBOF preview

RegPwnBOF

GitHubflangvik/regpwnbof

MDSec 的 RegPwn 的 Bof

privilege-escalationexploitationpost-exploitation+2
1277个月前
Kestrel preview

Kestrel

GitHubssteelfactor-oss/kestrel

低可观测性的 Active Directory 安全枚举工具,使用原生 ADSI/COM 接口。无需 .NET 或 PowerShell 即可枚举 ACLs、委派、信任关系、ADCS、Kerberoast 目标和攻击路径,并生成 BloodHound 兼容的输出。

defensive-toolsprivilege-escalationreconnaissance+5
951个月前
jdvrif preview

jdvrif

GitHubcleasbycode/jdvrif

JPG 图像隐写工具

encryption-decryption-toolsdata-exfiltrationforensics+3
695天前
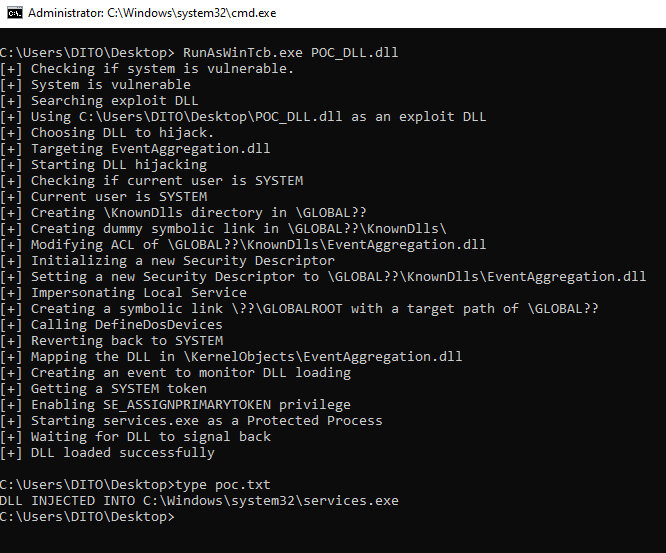
RunAsWinTcb preview

RunAsWinTcb

GitHubtastypepperoni/runaswintcb

概念验证型C漏洞利用程序,可从用户态运行带WinTcb-Light保护机制的DLL,演示Windows权限提升原语,并实现AV/Defender绕过。
privilege-escalationexploitationids-ips-evasion+2
1384年前
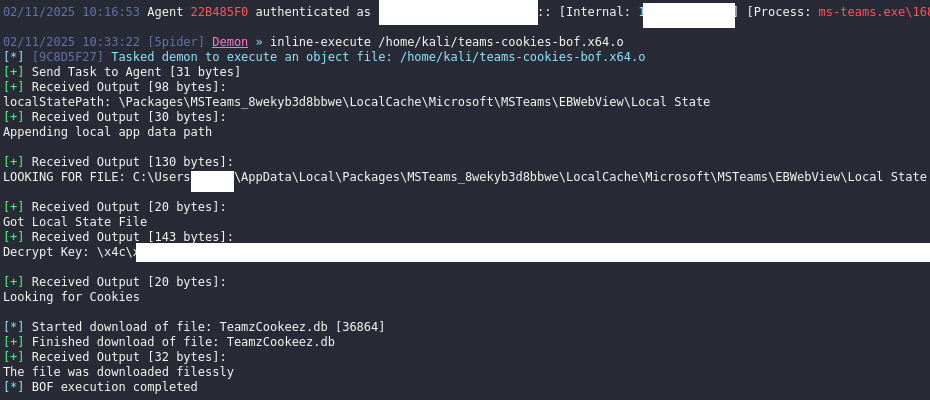
teams-cookies-bof preview

teams-cookies-bof

GitHubtierzerosecurity/teams-cookies-bof

用于窃取 Teams Cookie 的 BOF

post-exploitationred-teaming
13211个月前
GhostLock-Galaxy preview

GhostLock-Galaxy

GitHubwxxsfxyzm/ghostlock-galaxy

Root your Galaxy using CVE-2026-43499
android-securityprivilege-escalationvulnerability-analysis+6
48天前
chisel-ng preview

chisel-ng

GitHubnullsection/chisel-ng

Chisel 新一代,使用 Rust 编写。基于 WSS 的 SSH,带有一些自定义。
ids-ips-evasionlateral-movementpost-exploitation+5
1369个月前
CVE-2023-20178 preview

CVE-2023-20178

GitHubwh04m1001/cve-2023-20178

针对Cisco Secure Client和AnyConnect中任意文件删除漏洞的概念验证,可通过滥用Windows Installer实现权限提升至SYSTEM。
privilege-escalationvulnerability-analysisexploitation+2
893年前
LACheck preview

LACheck

GitHubmitchmoser/lacheck

多线程C# .NET程序集,用于通过SMB、WMI和WinRM枚举Windows主机上的本地管理员权限,集成了BloodHound以进行Active Directory侦察。
privilege-escalationreconnaissancelateral-movement+3
935年前
CVE-2025-24204 preview

CVE-2025-24204

GitHubffri/cve-2025-24204

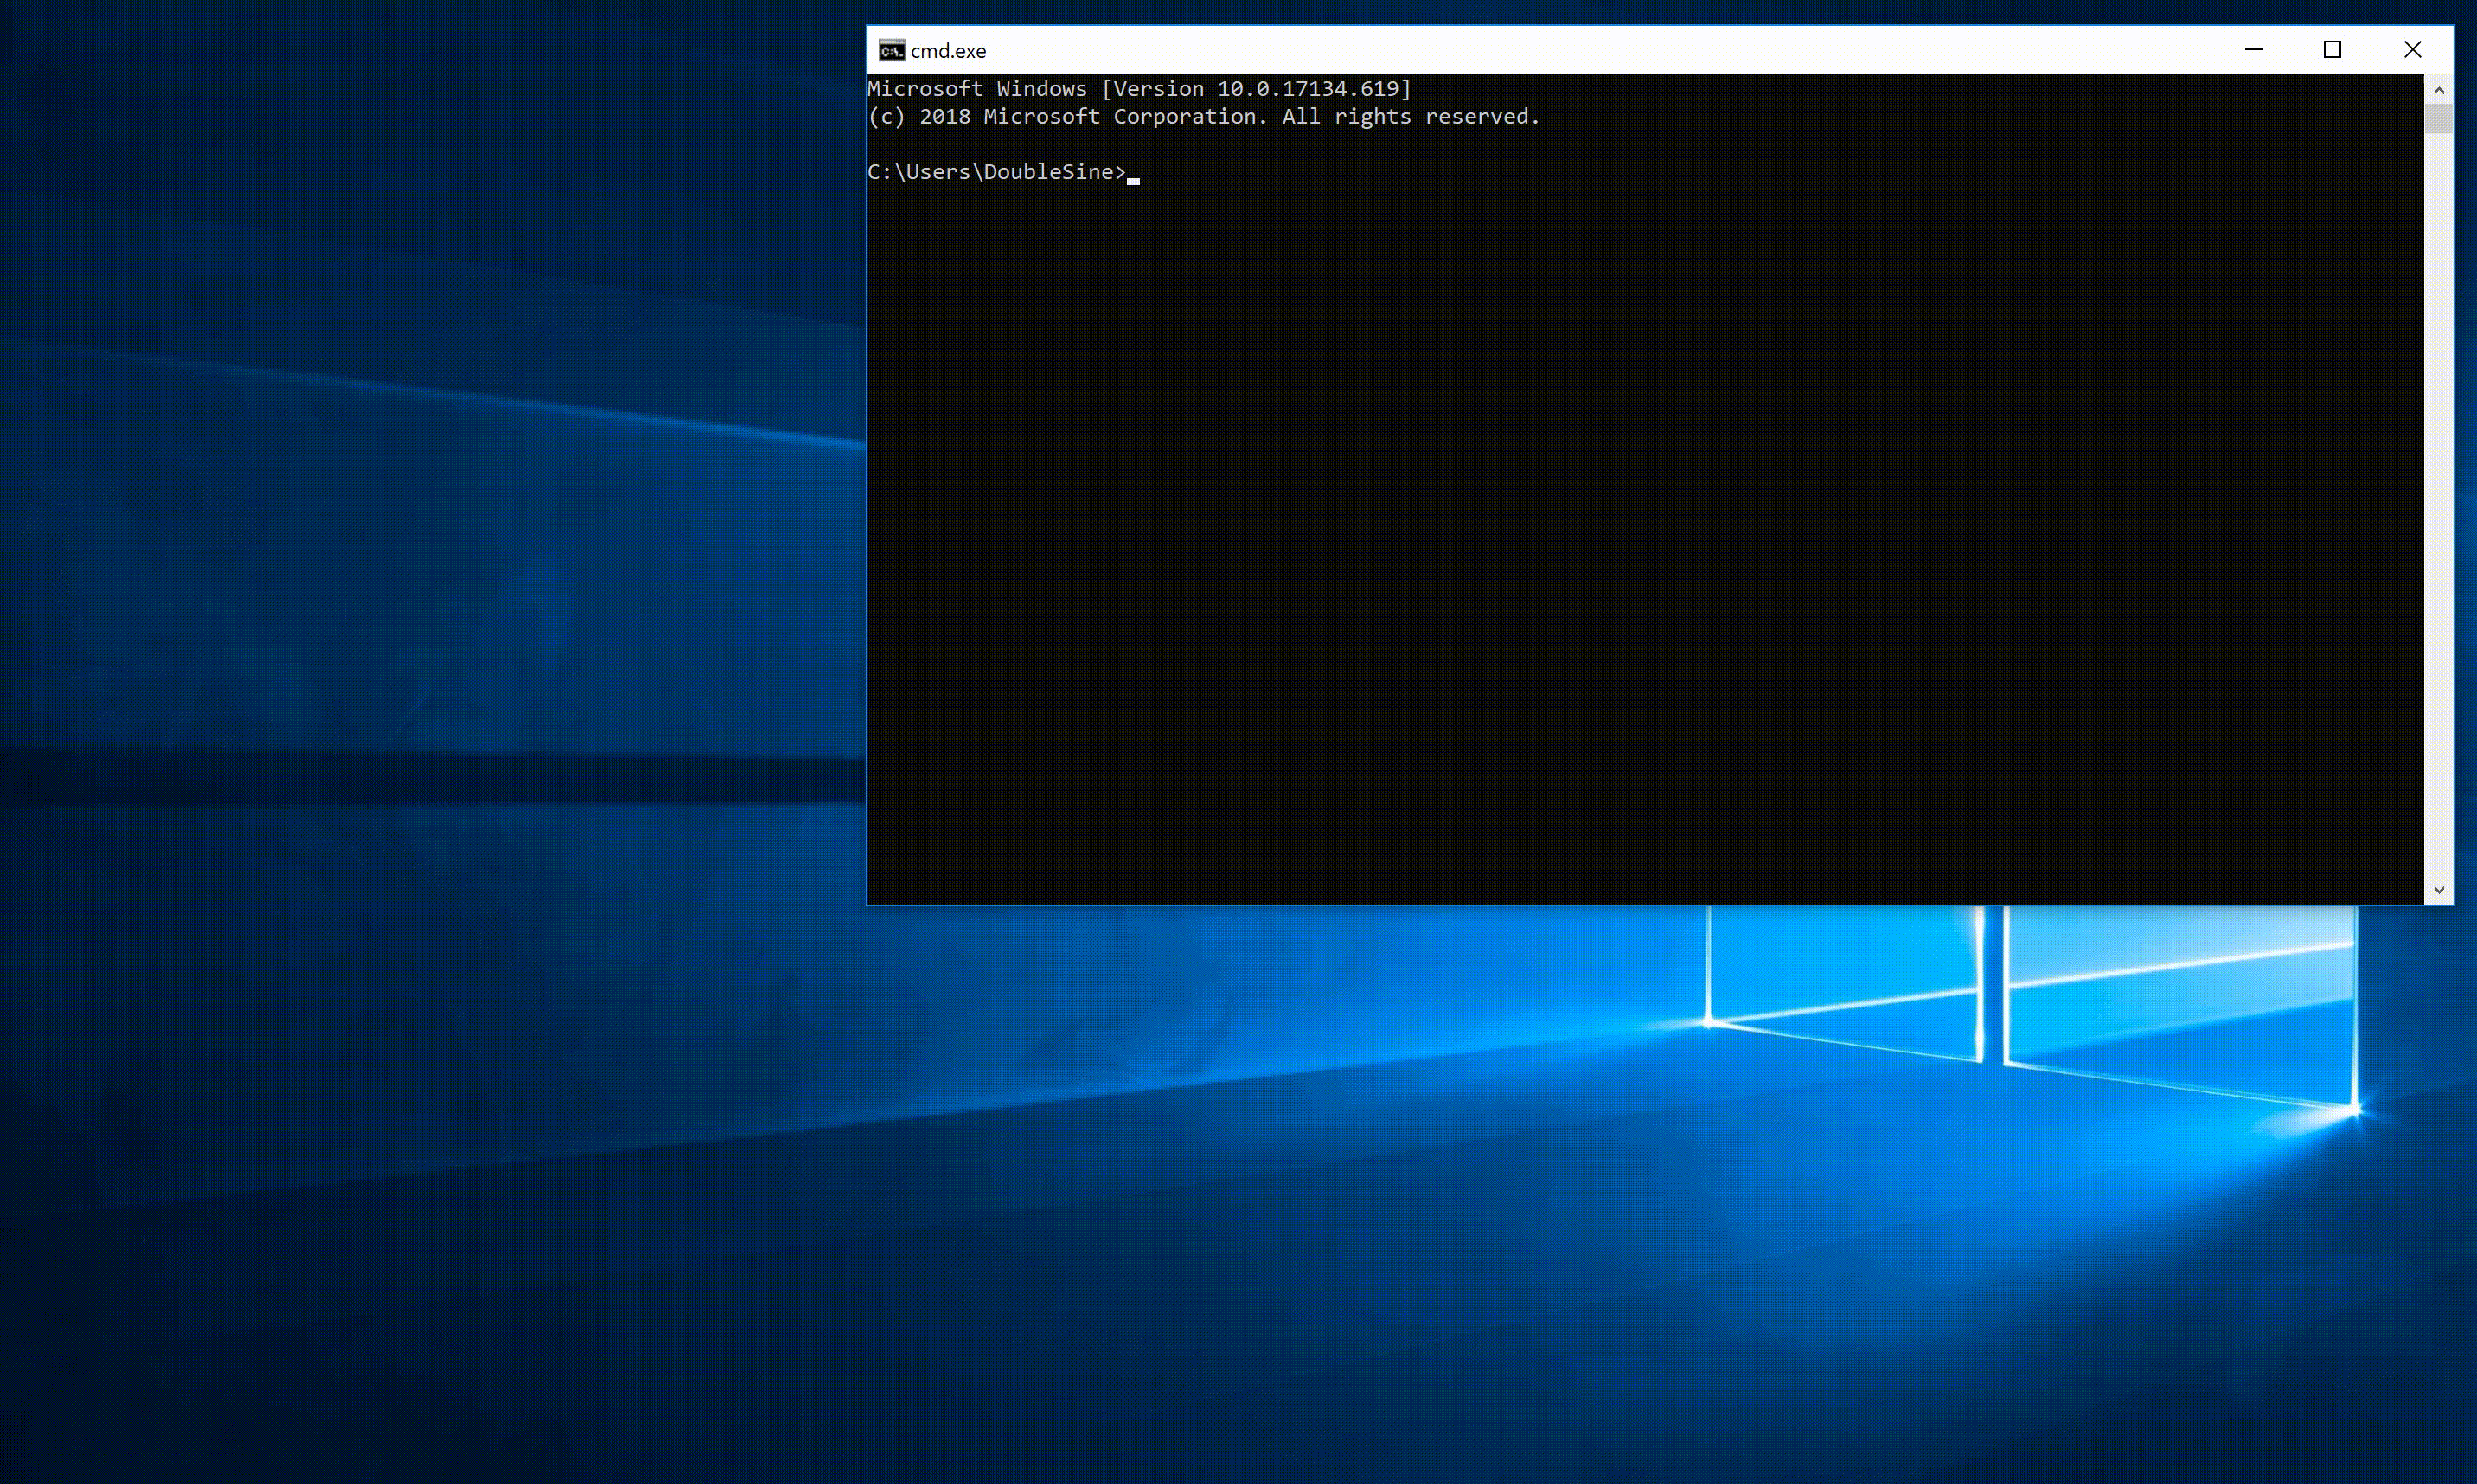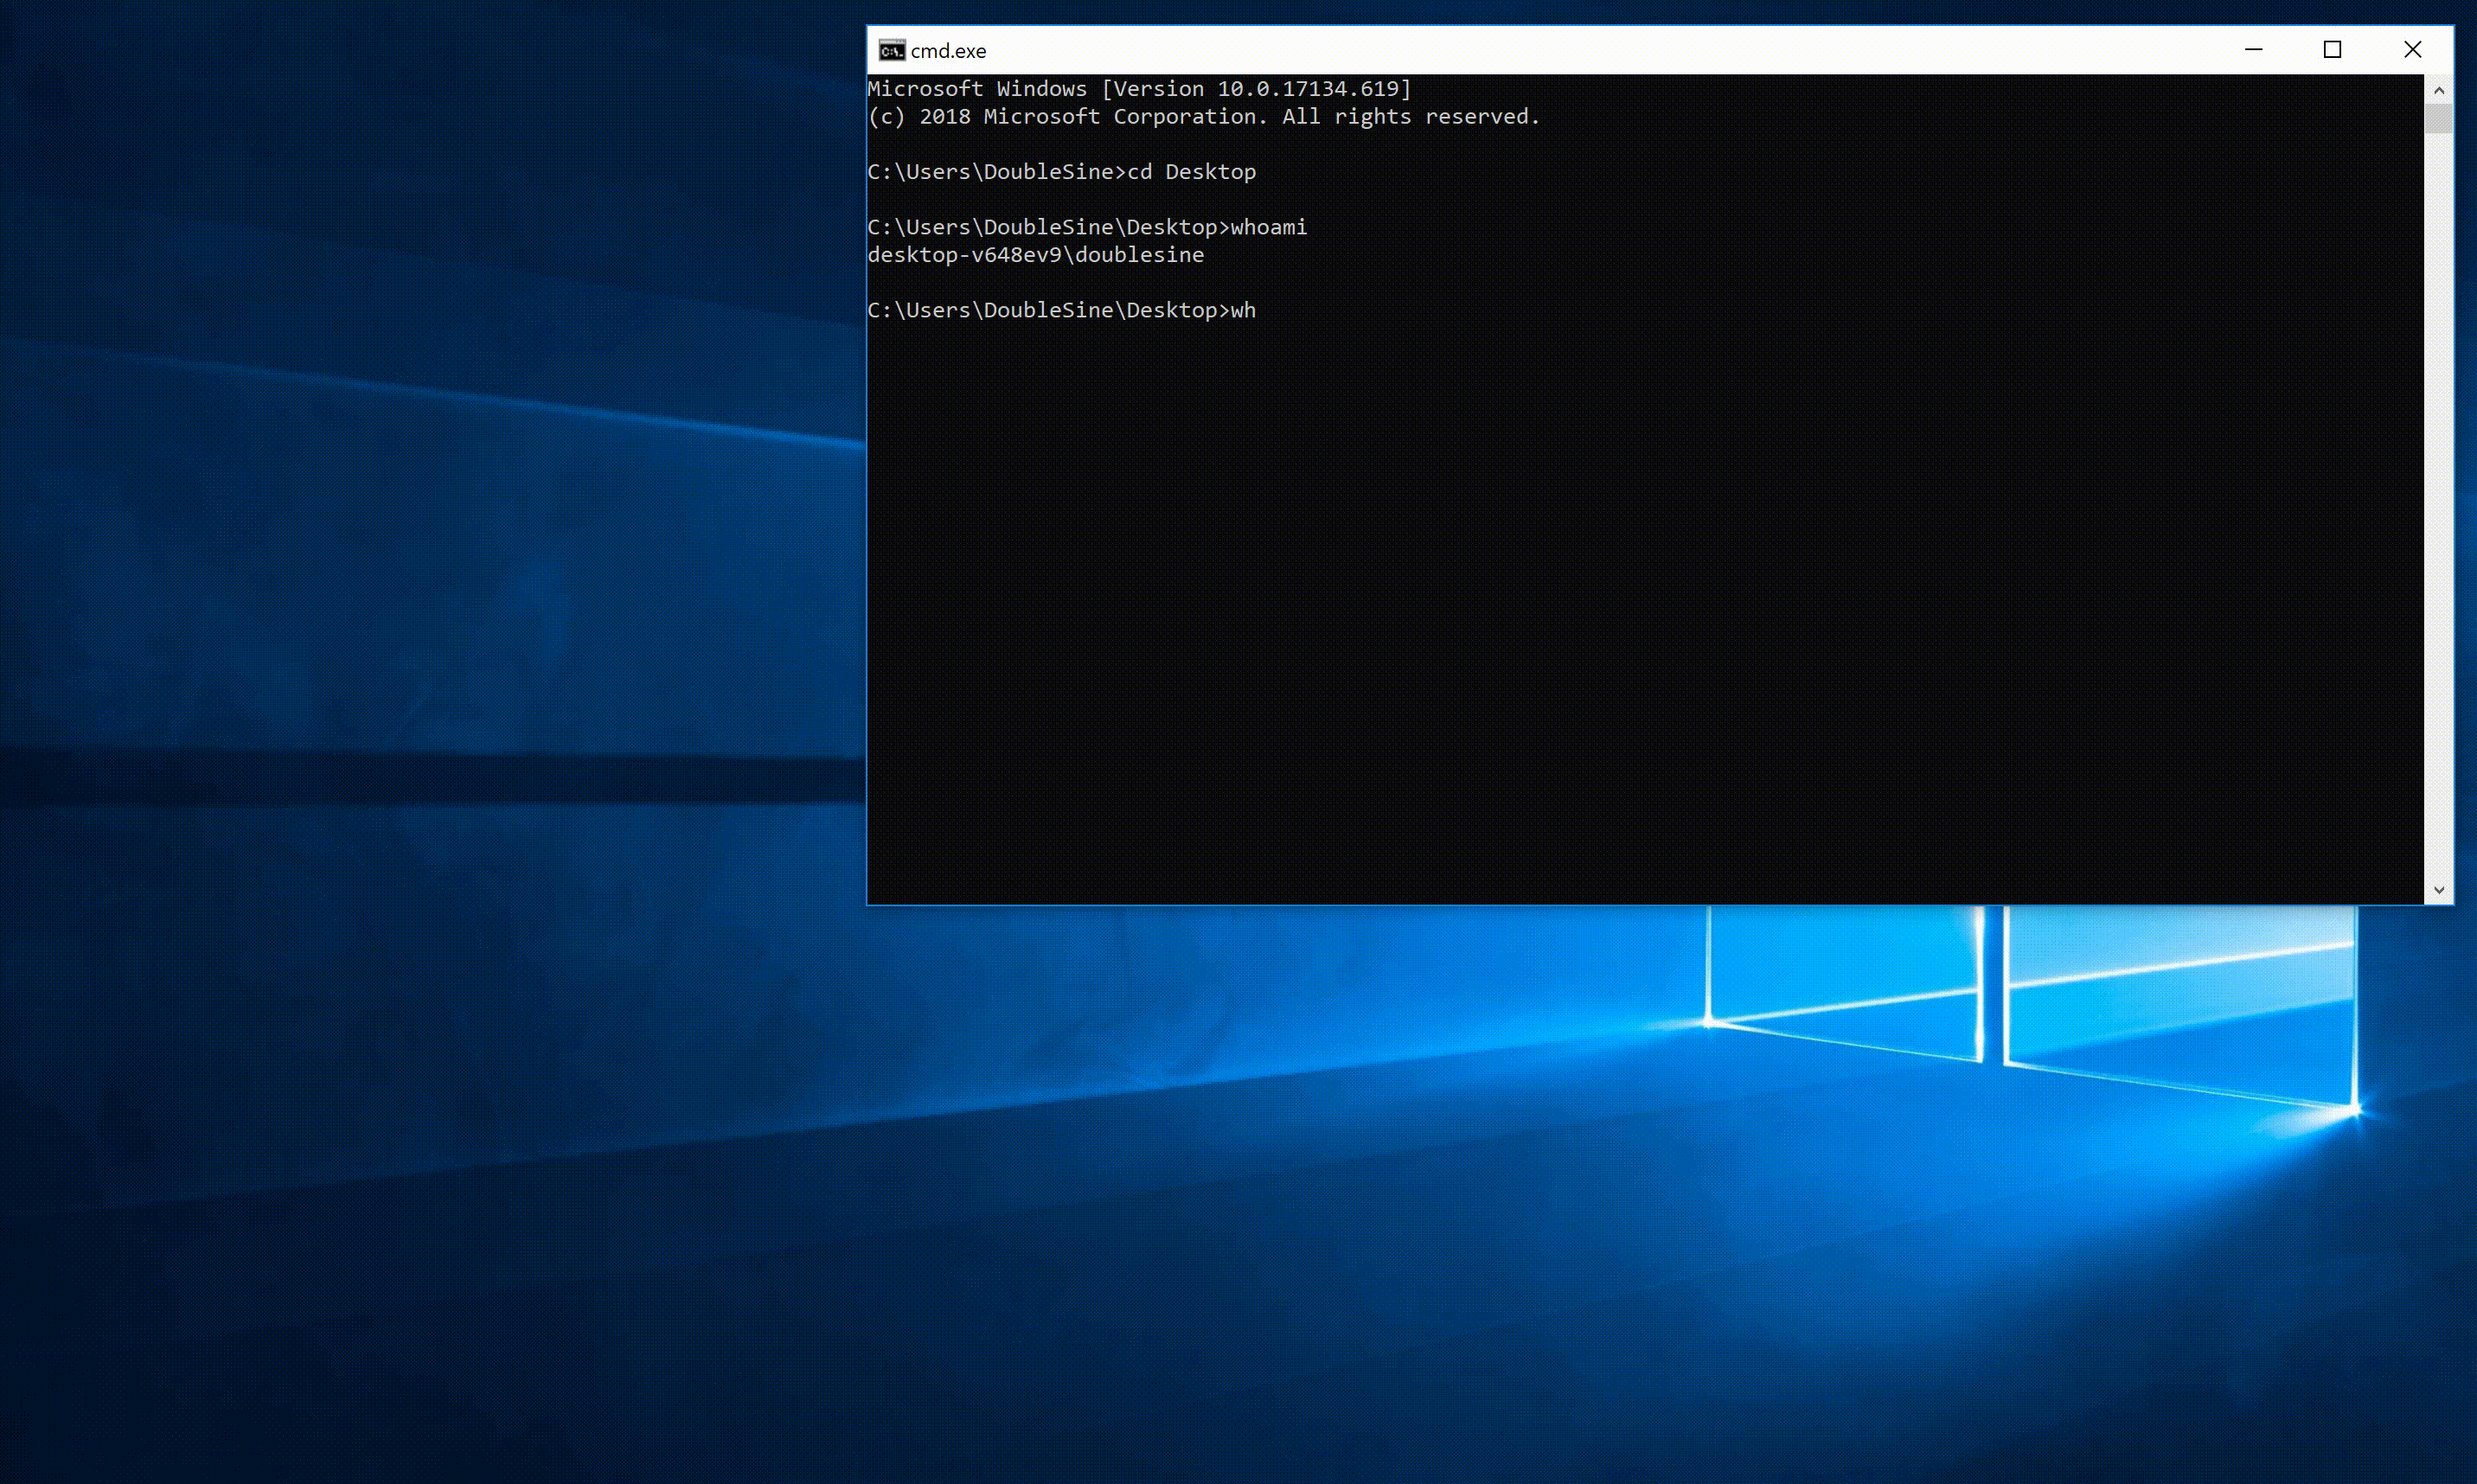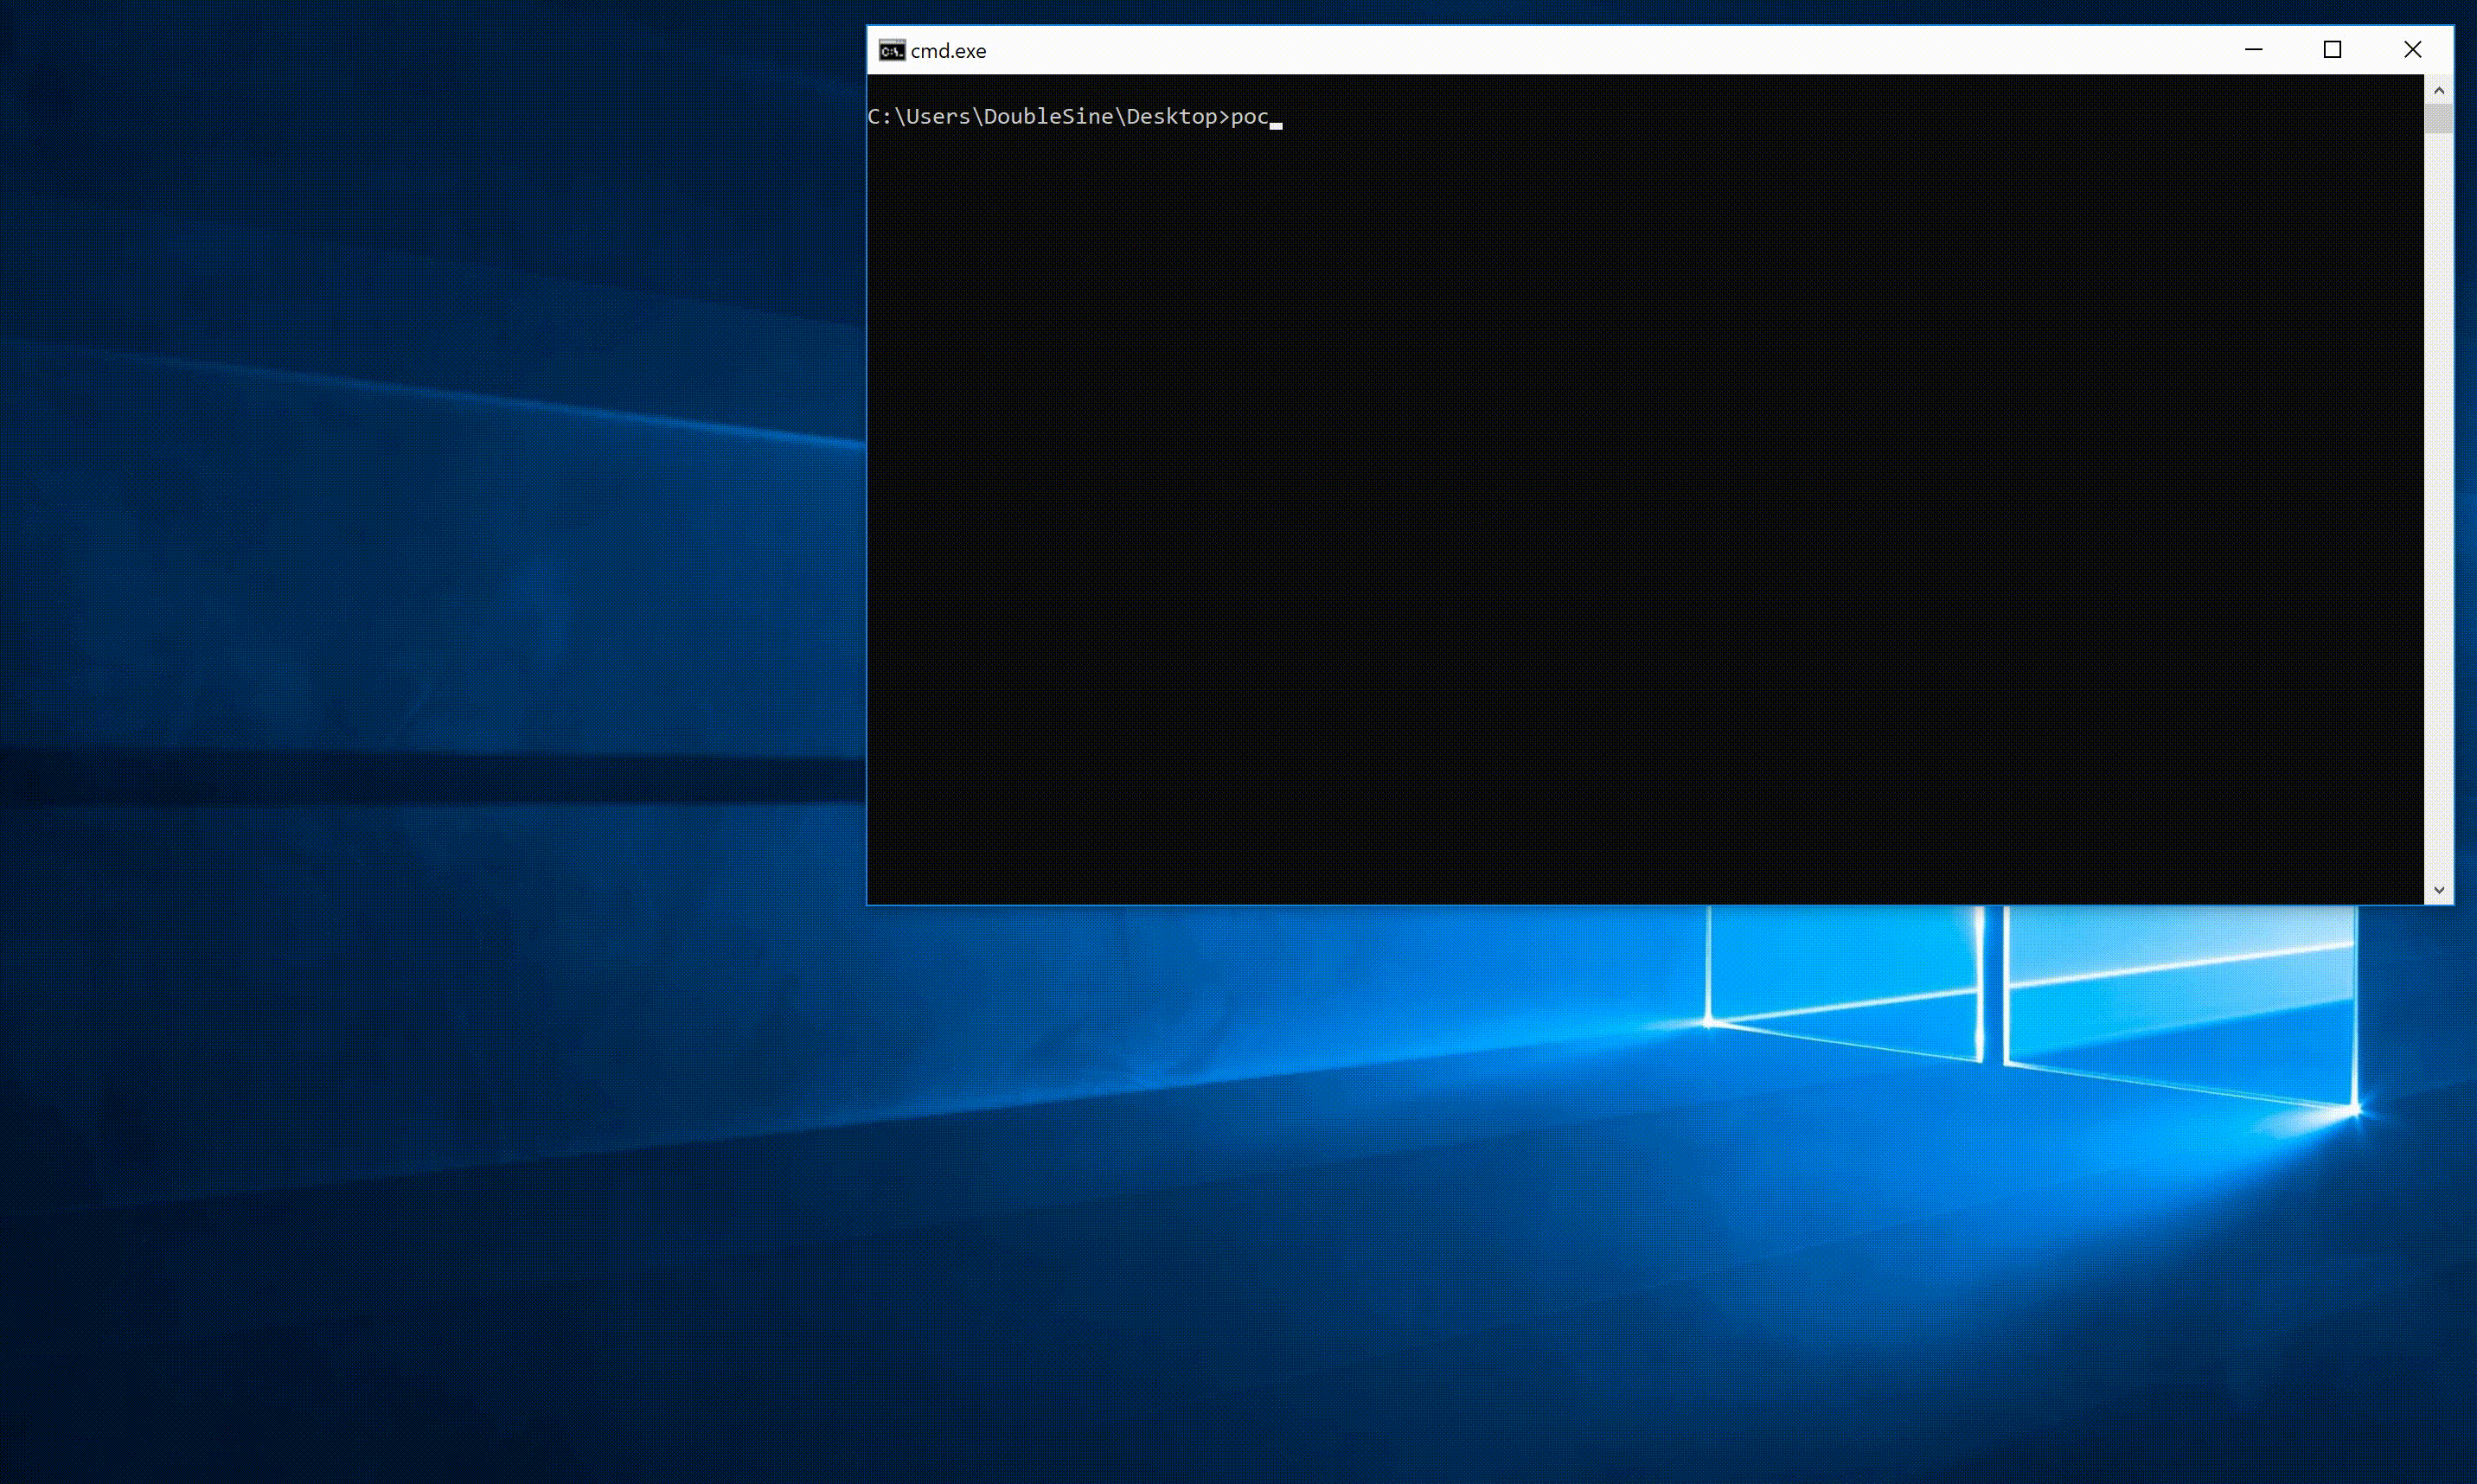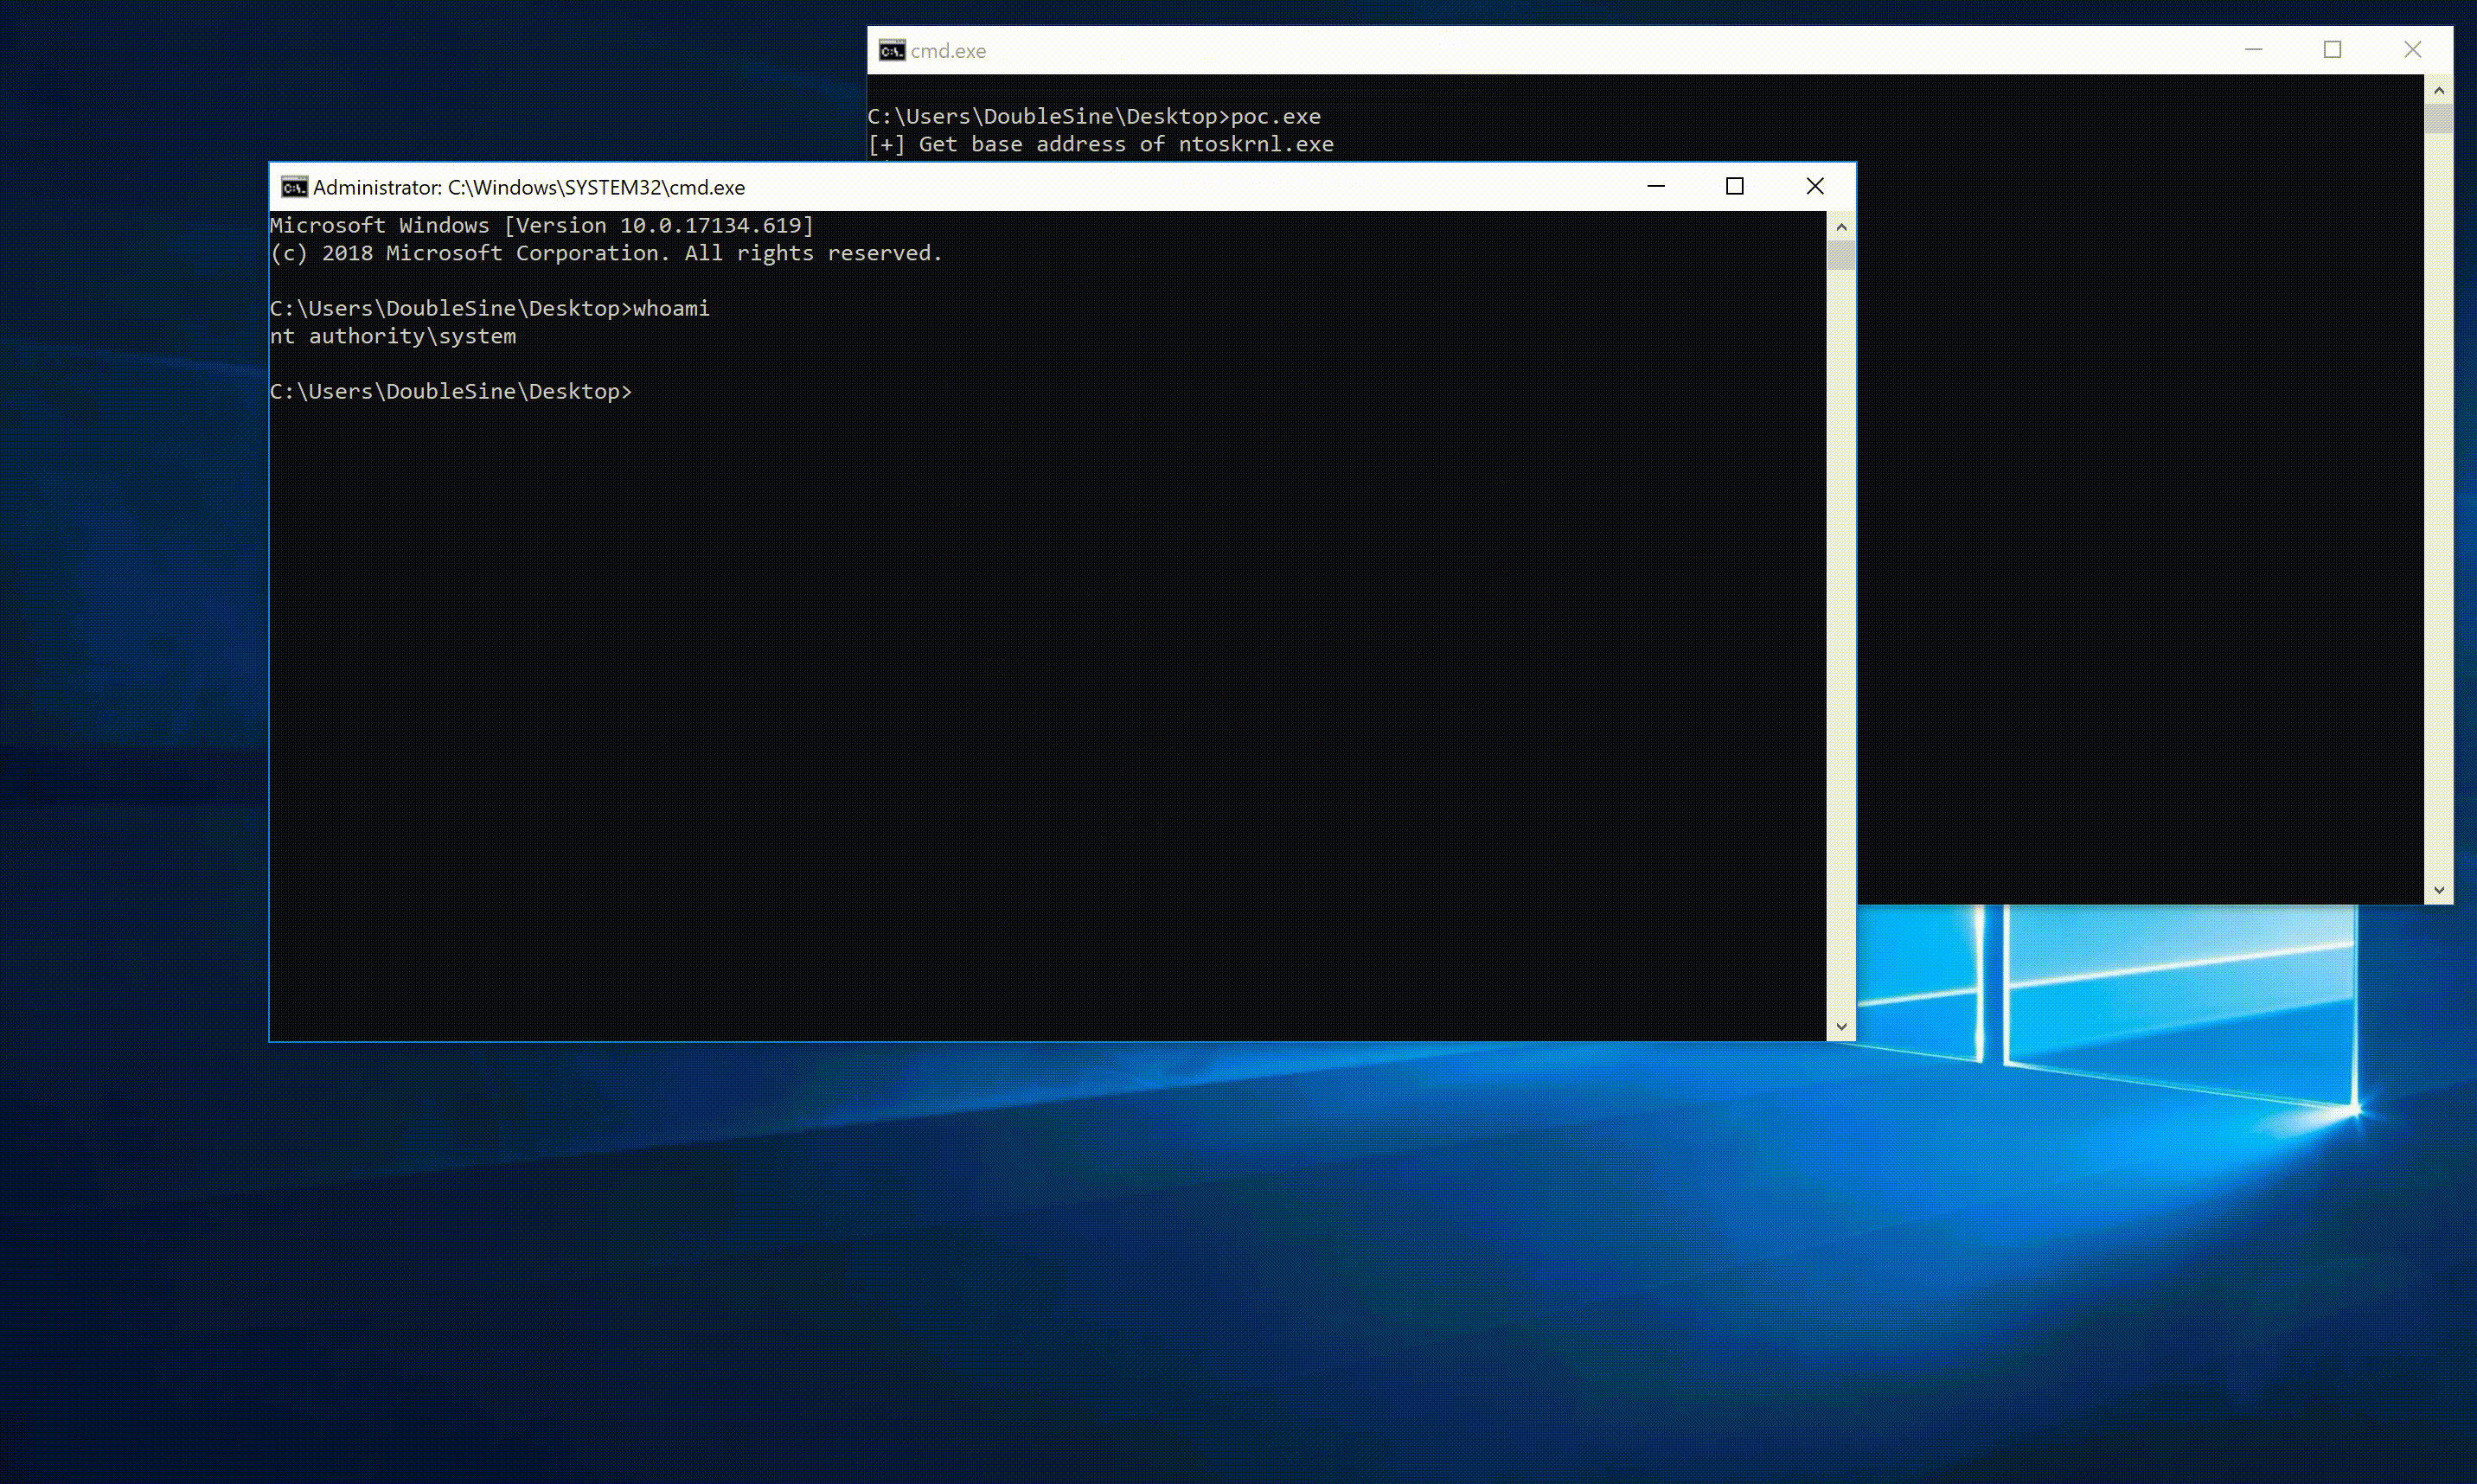
CVE-2025-24204 的 PoC 与技术细节
privilege-escalationencryption-decryption-toolsmemory-forensics+2
1131年前
SdoKeyCrypt-sys-local-privilege-elevation preview

SdoKeyCrypt-sys-local-privilege-elevation

GitHubhypersine/sdokeycrypt-sys-local-privilege-elevation

CVE-2019-9729。从https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation转移
privilege-escalationvulnerability-analysisexploitation+2
847年前
CVE-2018-8440 preview

CVE-2018-8440

GitHubsourceincite/cve-2018-8440

CVE-2018-8440 独立漏洞利用程序
privilege-escalationexploit-frameworksvulnerability-analysis+3
807年前
backup_dc_registry preview

backup_dc_registry

GitHubhorizon3ai/backup_dc_registry

一个简单的 POC,滥用 Backup Operator 权限远程导出 SAM、SYSTEM 和 SECURITY

privilege-escalationexploitationlateral-movement+3
954年前
上一页1…959697…100下一页








