
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
后渗透利用 — 第 100 页 | Kitploit
分类

后渗透利用

用于在受损系统和网络中维护访问、探索和扩大控制的工具。

Kitploit 推荐

精选工具

10 已选择
NetExec preview#1

NetExec

GitHubpennyw0rth/netexec
5.8k1天前
impacket preview#2

impacket

GitHubfortra/impacket
16.0k3天前
mimikatz preview#3

mimikatz

GitHubgentilkiwi/mimikatz
21.8k6个月前
PEASS-ng preview#4

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k1天前
Rubeus preview#5

Rubeus

GitHubghostpack/rubeus
5.1k11个月前
Seatbelt preview#6

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
Empire preview#7

Empire

GitHubbc-security/empire
5.2k1个月前
sliver preview#8

sliver

GitHubbishopfox/sliver
11.7k1天前
LaZagne preview#10

LaZagne

GitHubalessandroz/lazagne
11.0k1年前
PowerUpSQL preview#11

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
最新相关性最受欢迎最近更新
6165 结果
gogsownz preview

gogsownz

GitHubthez3ro/gogsownz

Gogs CVEs

privilege-escalationvulnerability-analysisexploitation+2
796年前
DiagTrackEoP preview

DiagTrackEoP

GitHubwh04m1001/diagtrackeop

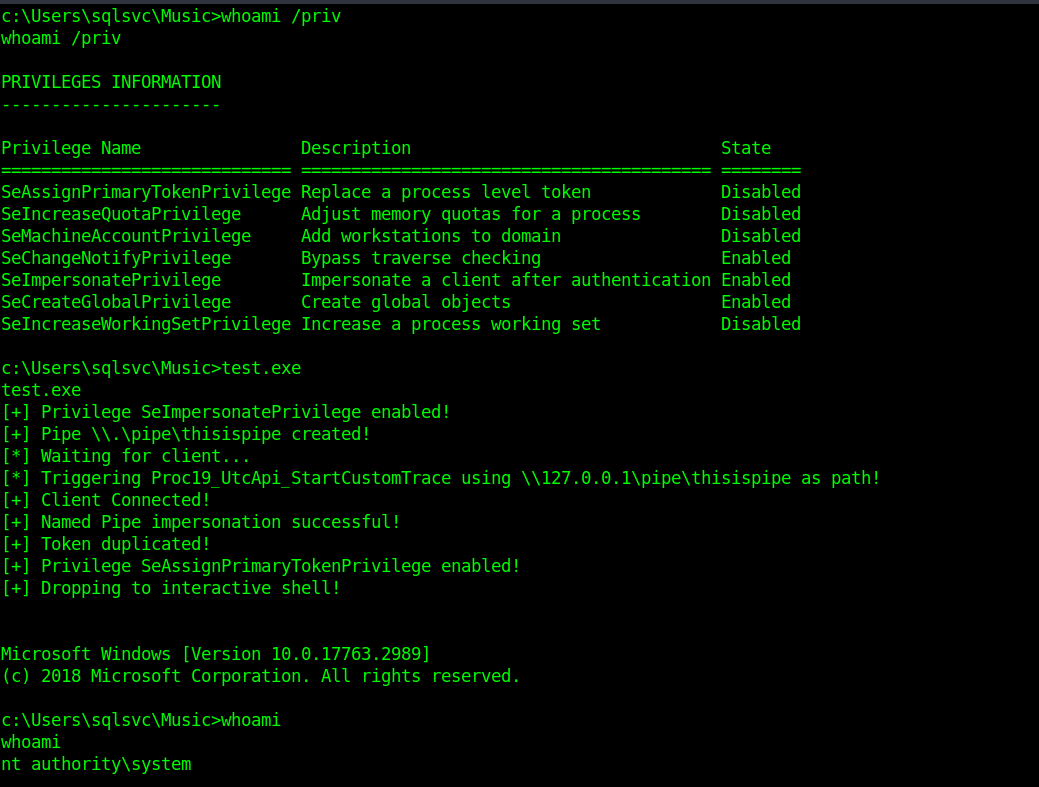
滥用 SeImpersonate 的 Windows 权限提升漏洞利用,通过 DiagTrack RPC,利用 Secondary Logon 获取 INTERACTIVE 令牌并取得 SYSTEM 权限。

privilege-escalationexploitationpost-exploitation+3
884年前
BloodfangC2 preview

BloodfangC2

GitHubzarkones/bloodfangc2

适用于 Windows 的现代 PIC 植入体(64 位与 32 位)
shellcodepost-exploitationcommand-and-control+4
1051年前
zygote-injection-toolkit preview

zygote-injection-toolkit

GitHubanonymous941/zygote-injection-toolkit

用于利用 Android Zygote 注入漏洞 (CVE-2024-31317) 的命令行工具
android-securityprivilege-escalationexploitation+5
6010个月前
Get-RBCD-Threaded preview

Get-RBCD-Threaded

GitHubfatrodzianko/get-rbcd-threaded

用于发现 Active Directory 环境中基于资源的约束委派攻击路径的工具
privilege-escalationreconnaissancepenetration-testing+1
1335年前
CVE-2018-8897 preview

CVE-2018-8897

GitHubnmulasmajic/cve-2018-8897

通过使机器触发 bugcheck(本地 DoS),实现 POP/MOV SS(CVE-2018-8897)漏洞的利用。
privilege-escalationvulnerability-analysisexploitation+3
818年前
libreoffice-remote-arbitrary-file-disclosure preview

libreoffice-remote-arbitrary-file-disclosure

GitHubjollheef/libreoffice-remote-arbitrary-file-disclosure

LibreOffice 远程任意文件泄露漏洞的概念验证
vulnerability-analysisexploitationdata-exfiltration+1
968年前
Swift-Attack preview

Swift-Attack

GitHubcedowens/swift-attack

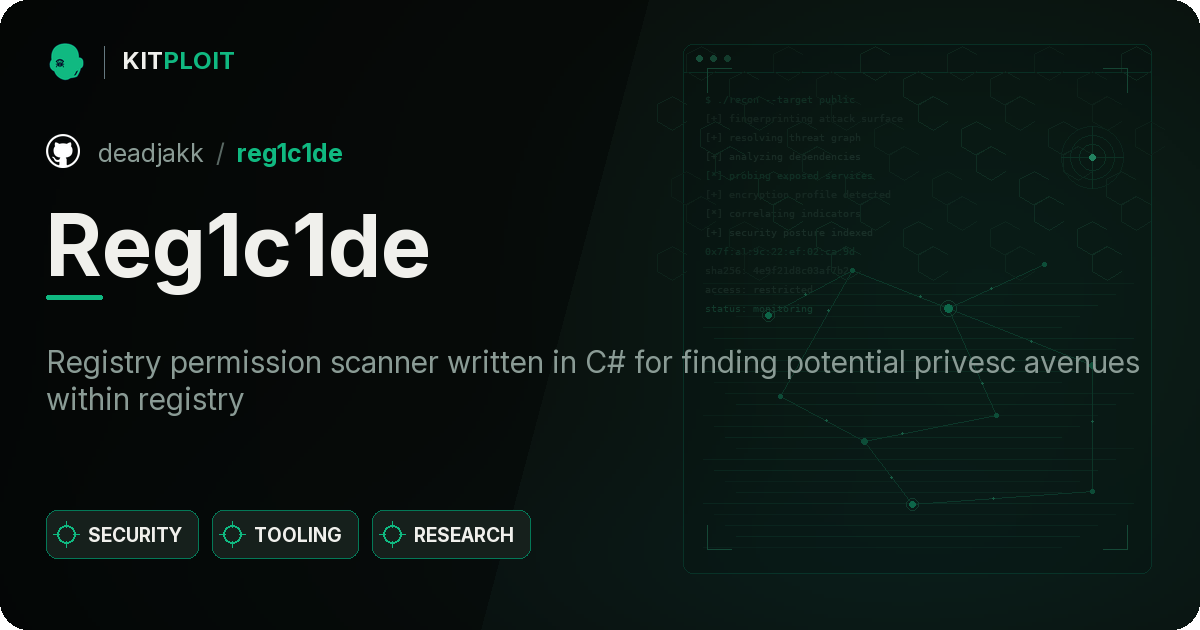
为蓝队提供单元测试,以帮助构建针对某些常见 macOS 后利用方法的检测。
post-exploitationeducationred-teaming+1
1073年前
Reg1c1de preview

Reg1c1de

GitHubdeadjakk/reg1c1de

用 C# 编写的注册表权限扫描器,用于发现注册表中的潜在权限提升途径。
privilege-escalationvulnerability-scannersconfiguration-auditing
865年前
lenovo_exec preview

lenovo_exec

GitHubestimated1337/lenovo_exec

CVE-2022-3699 具备任意内核代码执行能力
privilege-escalationvulnerability-analysisexploitation+1
723年前
NtDumpBOF preview

NtDumpBOF

GitHubdeh00ni/ntdumpbof

Cobalt Strike BOF,可在内存中创建 LSASS minidump,并通过 C2 回调将其外传,以便使用 Mimikatz 或 pypykatz 进行离线凭据解析。
data-exfiltrationpost-exploitationred-teaming
1002年前
MS16-032 preview

MS16-032

GitHubzcgonvh/ms16-032

MS16-032(CVE-2016-0099)仅限服务
privilege-escalationvulnerability-analysisexploitation+1
839年前
CIFSwitch preview

CIFSwitch

GitHubmanizada/cifswitch

CVE-2026-46243 的概念验证漏洞利用,利用伪造的 NSS 库和命名空间操作,通过 cifs.upcall 提升权限。
privilege-escalationvulnerability-analysisexploitation+3
694个月前
EasyTokens preview

EasyTokens

GitHubsecdev02/easytokens

Kali365 - EvilTokens 复制品
osint-social-engineeringinformation-gatheringpost-exploitation+7
723个月前
android_autorooter preview

android_autorooter

GitHubscs-labrat/android_autorooter

利用 CVE-2024-0044 漏洞从 Android 12 和 13 上的应用中远程窃取敏感用户数据
android-securityexploit-frameworkspayload-generation+5
762年前
process-enumeration-stealth preview

process-enumeration-stealth

GitHublloydlabs/process-enumeration-stealth

通过NtQueryInformationFile利用NTFS列出PID的隐蔽Windows进程枚举PoC,可绕过标准监控API,并在红队行动中实现EDR规避。

reconnaissanceids-ips-evasioninformation-gathering+2
842年前
badsuccessor preview

badsuccessor

GitHubcybrly/badsuccessor

利用 Windows Server 2025 的 dMSA 权限提升漏洞,枚举可写 OU,将权限提升至任意域用户,提取凭据,并在经授权的 AD 安全评估中实现域接管。

privilege-escalationreconnaissancepersistence-mechanisms+7
1223天前
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Crystal Palace 面向 Sliver C2 的 PICO 加载器:双层 AMSI 绕过、ETW 静默、AES-256-CBC 加密有效载荷、6 种投递变体

exploitationpost-exploitationmalware-analysis+4
482个月前
上一页1…99100下一页