
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
论文与研究 — 第 82 页 | Kitploit
分类

论文与研究

用于防御或授权分析的安全论文、研究项目、技术参考和可复现资料。

Kitploit 推荐

精选工具

10 已选择
security-research preview#1

security-research

GitHubgoogle/security-research
4.6k3天前
0days-in-the-wild preview#2

0days-in-the-wild

GitHubgoogleprojectzero/0days-in-the-wild
1.0k3个月前
MSRC-Security-Research preview#3

MSRC-Security-Research

GitHubmicrosoft/msrc-security-research
1.4k2年前
publications preview#4

publications

GitHubtrailofbits/publications
1.9k7天前
papers-we-love preview#5

papers-we-love

GitHubpapers-we-love/papers-we-love
111.7k23天前
criticality_score preview#6

criticality_score

GitHubossf/criticality_score
1.5k2个月前
attack-stix-data preview#7

attack-stix-data

GitHubmitre-attack/attack-stix-data
72515天前
Security-101 preview#8

Security-101

GitHubmicrosoft/security-101
6.8k2个月前
h4cker preview#9

h4cker

GitHubthe-art-of-hacking/h4cker
28.9k3天前
offensive-ai-compilation preview#10

offensive-ai-compilation

GitHubjiep/offensive-ai-compilation
1.4k19天前
最新相关性最受欢迎最近更新
2370 结果
CVE-2025-67644-LangGraph-3.0.1-SQLite-Checkpoint-SQL-Injection preview

CVE-2025-67644-LangGraph-3.0.1-SQLite-Checkpoint-SQL-Injection

GitHubmbanyamer/cve-2025-67644-langgraph-3.0.1-sqlite-checkpoint-sql-injection

CVE-2025-67644 的概念验证漏洞利用程序,该漏洞是 LangGraph SQLite Checkpoint 中的一个 SQL 注入漏洞。演示了如何通过未经净化的元数据过滤器键实现任意 SQL 注入,从而能够进行数据窃取和过滤器绕过。

vulnerability-analysisexploitationweb-application-exploitation+4
1
9个月前
Research_Successful_Errors preview

Research_Successful_Errors

GitHubvladko312/research_successful_errors

Whitepaper introducing Error-Based and Boolean Error-Based Blind techniques for SSTI and Code Injection, with universal payloads for six programming…
vulnerability-analysiscode-analysisweb-application-exploitation+6
1219个月前
CVE-2026-27199-werkzeug-safe-join-bypass-PoC preview

CVE-2026-27199-werkzeug-safe-join-bypass-PoC

GitHubalimezar/cve-2026-27199-werkzeug-safe-join-bypass-poc

针对 CVE-2026-27199 的概念验证漏洞利用程序,该漏洞为 Werkzeug safe_join() 的 Windows 设备名绕过漏洞,可演示路径遍历与静默数据丢弃。
vulnerability-analysisexploitationweb-security+2
9个月前
Talks preview

Talks

GitHubneo23x0/talks

我的公开演讲幻灯片

papers-researcheducationcurated-resources
649个月前
CVE-2023-33730 preview

CVE-2023-33730

GitHubsahiloj/cve-2023-33730

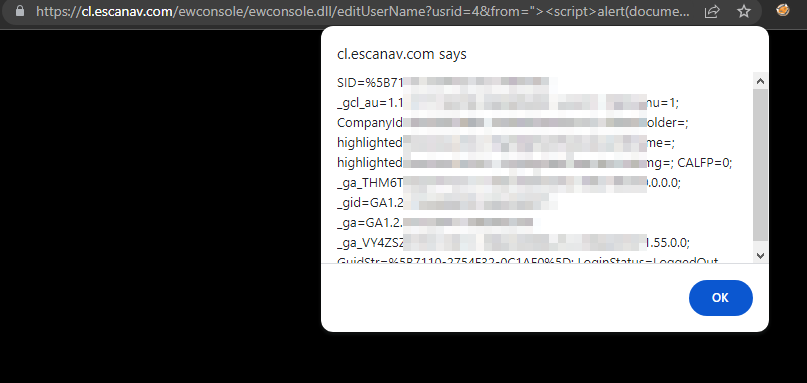
eScan Management Console 版本 14.0.1400.2281 存在权限提升漏洞,通过 `GetUserCurrentPwd` 函数,攻击者可以明文检索任意用户的密码。
authentication-authorizationprivilege-escalationreconnaissance+8
19个月前
CVE-2023-31703 preview

CVE-2023-31703

GitHubsahiloj/cve-2023-31703

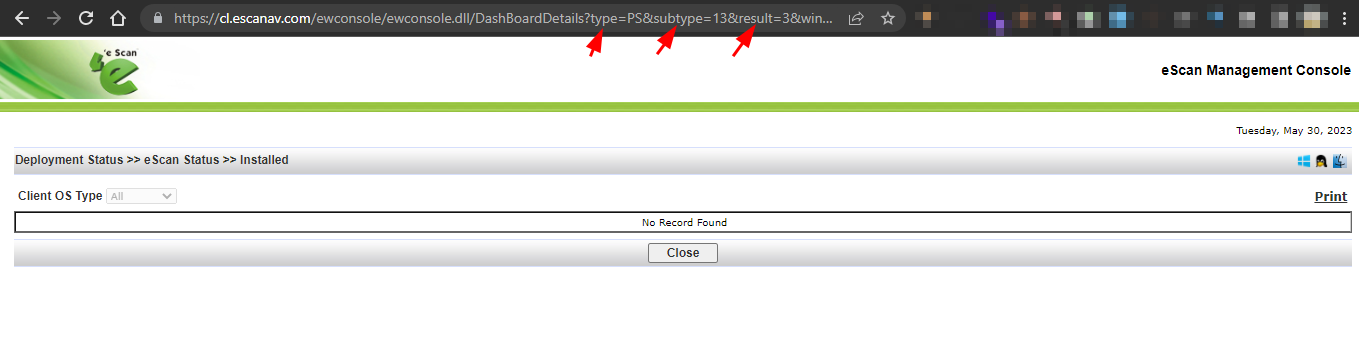
Microworld Technologies eScan Management Console(版本 14.0.1400.2281)的编辑用户功能中存在一个反射型跨站脚本(XSS)漏洞。
vulnerability-analysisweb-application-exploitationweb-security+3
49个月前
CVE-2023-33731 preview

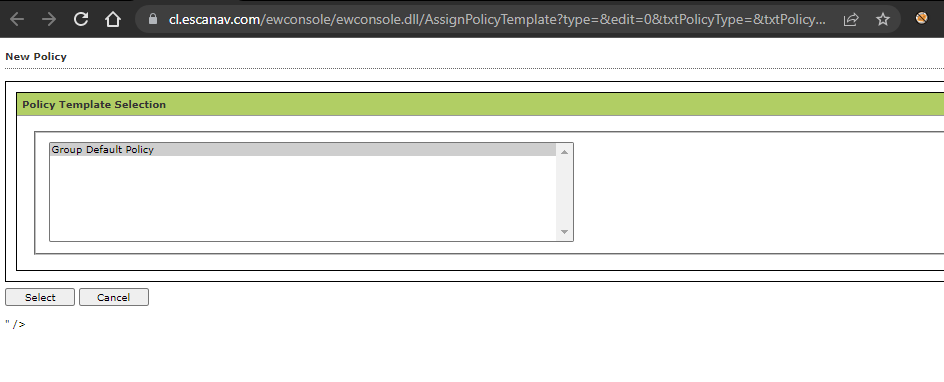
CVE-2023-33731

GitHubsahiloj/cve-2023-33731

在 MicroWorld Technologies 开发的 eScan 管理控制台(版本 14.0.1400.2281)中发现了一个反射型跨站脚本(XSS)漏洞。
vulnerability-analysisweb-application-exploitationweb-security+3
19个月前
CVE-2023-33732 preview

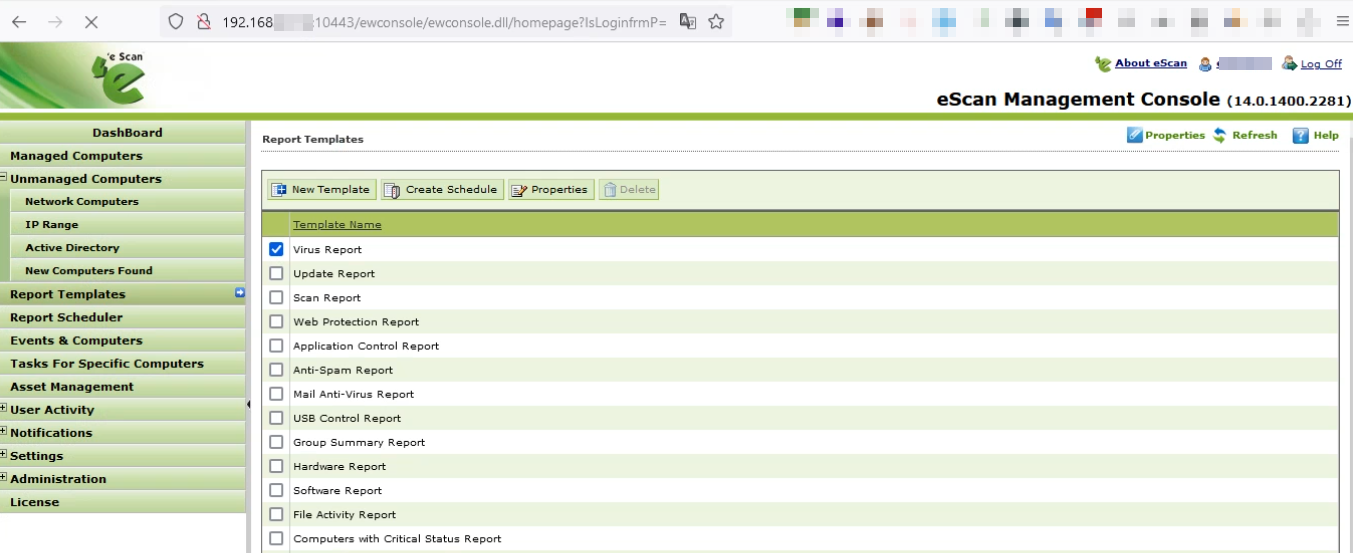
CVE-2023-33732

GitHubsahiloj/cve-2023-33732

CVE-2023-33732 是 Microworld Technologies eScan 管理控制台(版本 14.0.1400.2281)中发现的反射型跨站脚本 (XSS) 漏洞。
vulnerability-analysisweb-application-exploitationweb-security+3
19个月前
CVE-2023-34835 preview

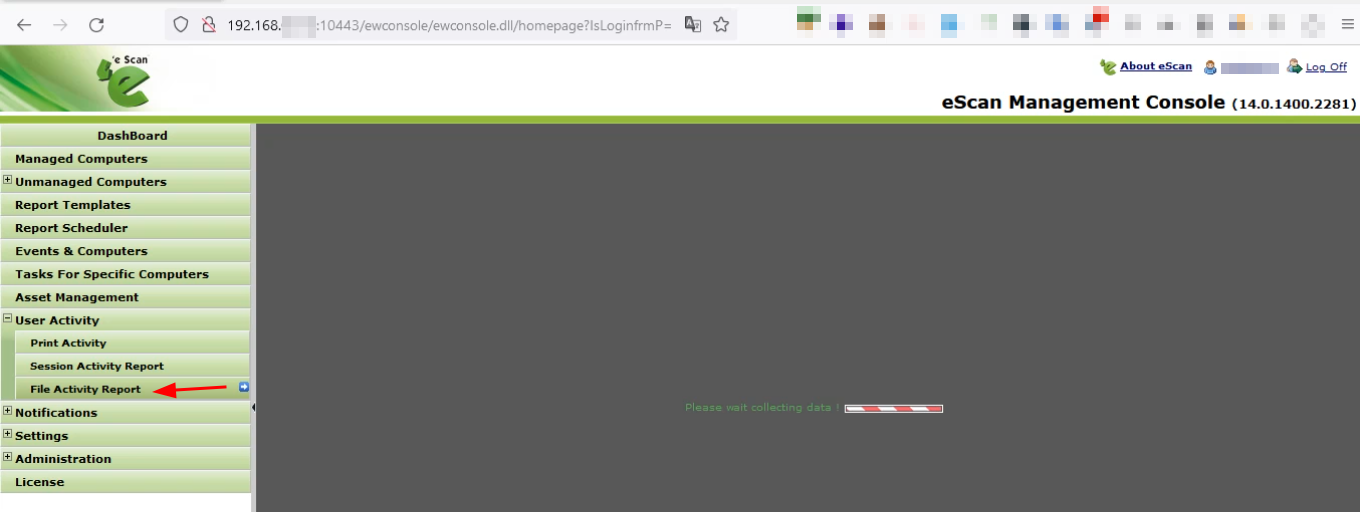
CVE-2023-34835

GitHubsahiloj/cve-2023-34835

在 Microworld Technologies eScan Management Console 版本 14.0.1400.2281 中发现了一个反射型跨站脚本(XSS)漏洞。
vulnerability-analysisweb-application-exploitationweb-security+3
19个月前
CVE-2023-34836 preview

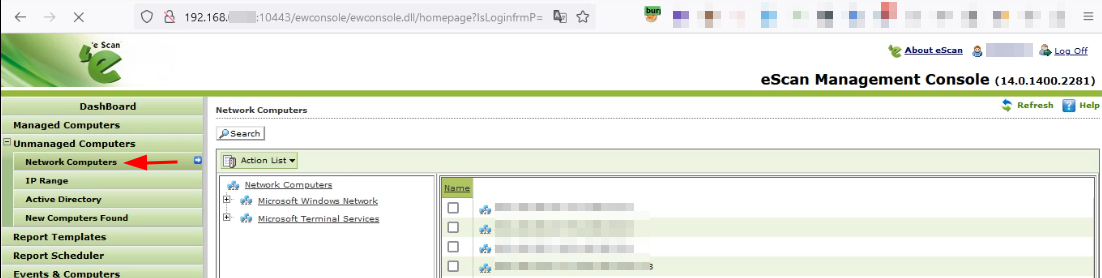
CVE-2023-34836

GitHubsahiloj/cve-2023-34836

Microworld Technologies eScan Management Console v14.0.1400.2281 中存在一个反射型跨站脚本(XSS)漏洞。受影响的参数为 Dtltyp 和 ListName,它们在“用户活动”部分下的“文件活动报告”功能中被处理。
vulnerability-analysisweb-application-exploitationpenetration-testing+2
19个月前
CVE-2023-34837 preview

CVE-2023-34837

GitHubsahiloj/cve-2023-34837

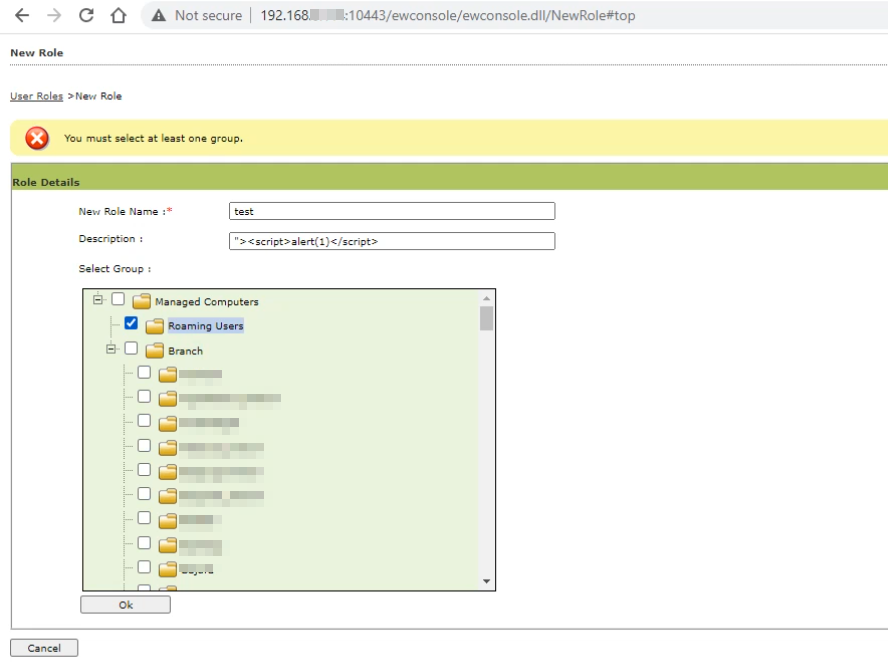
CVE-2023-34837 是在 Microworld Technologies eScan 管理控制台 14.0.1400.2281 中发现的一个反射型跨站脚本 (XSS) 漏洞。该漏洞存在于“非托管计算机 → 网络计算机”功能中的 GrpPath POST 参数中。
vulnerability-analysisweb-application-exploitationpenetration-testing+2
19个月前
CVE-2023-34838 preview

CVE-2023-34838

GitHubsahiloj/cve-2023-34838

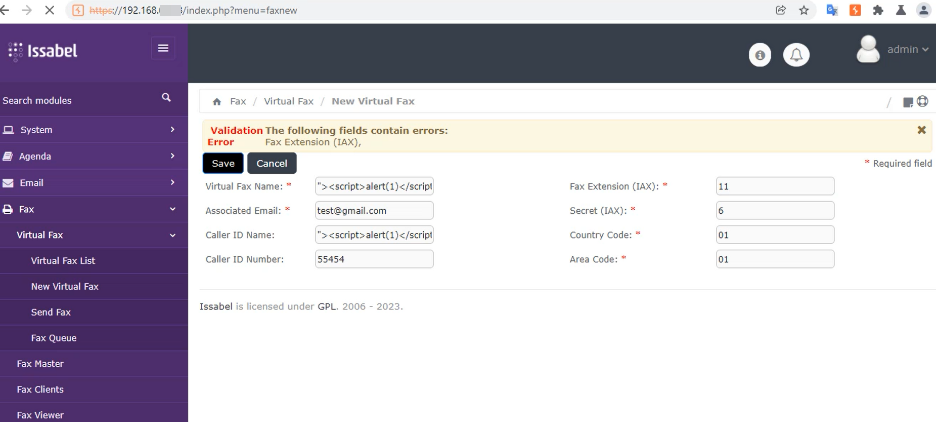
Microworld Technologies eScan Management Console 版本 14.0.1400.2281 存在存储型跨站脚本(XSS)攻击漏洞。
vulnerability-analysisweb-application-exploitationpenetration-testing+2
19个月前
CVE-2023-37190 preview

CVE-2023-37190

GitHubsahiloj/cve-2023-37190

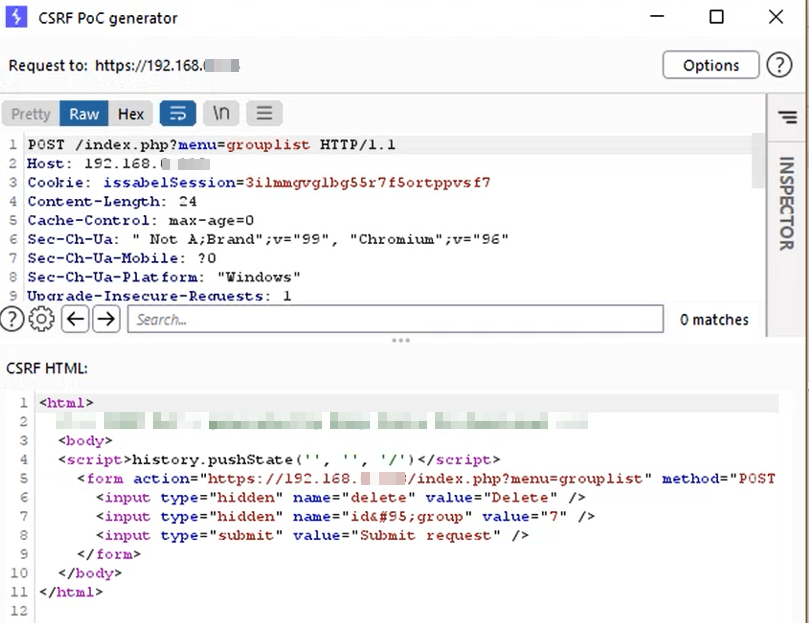
Issabel-PBX 4.0.0-6 版本中存在一个存储型跨站脚本(XSS)漏洞。该应用程序未能正确清理和编码用户提供的输入,便将其存储至数据库,并随后在 Web 界面中渲染显示。
vulnerability-analysisexploitationweb-application-exploitation+3
19个月前
CVE-2023-37597 preview

CVE-2023-37597

GitHubsahiloj/cve-2023-37597

Issabel-pbx v 4.0.0-6 在其用户组管理功能中存在跨站请求伪造(CSRF)漏洞。

vulnerability-analysisexploitationweb-application-exploitation+3
19个月前
CVE-2023-37599 preview

CVE-2023-37599

GitHubsahiloj/cve-2023-37599

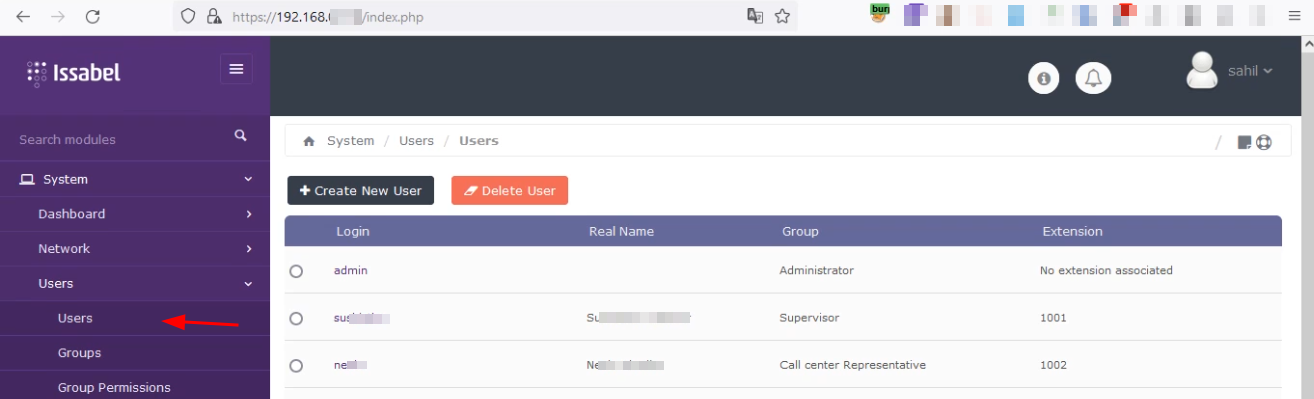
Issabel-pbx 版本 4.0.0-6 存在一个破坏访问控制漏洞,表现为 Web 界面上未经认证的目录列表。
vulnerability-analysisinformation-gatheringweb-security+3
29个月前
CVE-2023-34839 preview

CVE-2023-34839

GitHubsahiloj/cve-2023-34839

CVE-2023-34839 是在 Issabel PBX 4.0.0-6 版本中发现的一个跨站请求伪造(CSRF)漏洞,Issabel PBX 是一个广泛使用的开源统一通信平台。

vulnerability-analysisexploitationweb-application-exploitation+3
59个月前
Rubrics-as-an-Attack-Surface preview

Rubrics-as-an-Attack-Surface

GitHubzdcslab/rubrics-as-an-attack-surface

针对评分标准诱导偏好漂移(RIPD)的研究代码:进化式评分标准搜索、保持基准的选择,以及LLM评判者中的DPO策略错位评估。
machine-learningpapers-researcheducation+2
79个月前
-CVE-2026-23829-CTT-Mailpit-phase-reconstruction- preview

-CVE-2026-23829-CTT-Mailpit-phase-reconstruction-

GitHubsimoesctt/-cve-2026-23829-ctt-mailpit-phase-reconstruction-

这是 Mailpit SMTP 服务器中的一个 CRLF 注入漏洞——一个经典的数据损坏漏洞。但在 CTT 下,它不仅仅是一个 bug,更是一次相位重建的机会。

vulnerability-analysisexploitationweb-application-exploitation+2
9个月前
上一页1…818283…100下一页









