
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
分类

论文与研究

用于防御或授权分析的安全论文、研究项目、技术参考和可复现资料。

Kitploit 推荐

精选工具

10 已选择
security-research preview#1

security-research

GitHubgoogle/security-research
4.6k4天前
0days-in-the-wild preview#2

0days-in-the-wild

GitHubgoogleprojectzero/0days-in-the-wild
1.0k3个月前
MSRC-Security-Research preview#3

MSRC-Security-Research

GitHubmicrosoft/msrc-security-research
1.4k2年前
publications preview#4

publications

GitHubtrailofbits/publications
1.9k8天前
papers-we-love preview#5

papers-we-love

GitHubpapers-we-love/papers-we-love
111.7k24天前
criticality_score preview#6

criticality_score

GitHubossf/criticality_score
1.5k2个月前
attack-stix-data preview#7

attack-stix-data

GitHubmitre-attack/attack-stix-data
72716天前
Security-101 preview#8

Security-101

GitHubmicrosoft/security-101
6.8k2个月前
h4cker preview#9

h4cker

GitHubthe-art-of-hacking/h4cker
28.9k4天前
offensive-ai-compilation preview#10

offensive-ai-compilation

GitHubjiep/offensive-ai-compilation
1.4k20天前
最新相关性最受欢迎最近更新
2394 结果
CVE-2026-59230 preview

CVE-2026-59230

GitHuboscerd/cve-2026-59230

针对 Apache Camel camel-mail MimeMultipart 标头注入(CVE-2026-59230)的概念验证复现器,演示在 Spring Boot 和 Quarkus 运行时中通过 CamelHttpUri 注入实现的 SSRF。

vulnerability-analysisexploitationweb-application-exploitation+2
2个月前
Security-101 preview

Security-101

GitHubmicrosoft/security-101

8节课程,启动你的网络安全学习。

network-securitycloud-securityidentity-access-management+5
6.8k2个月前
fire-hd-ownership preview

fire-hd-ownership

GitHubericpardee/fire-hd-ownership

拿下亚马逊一直在停用的平板 — CVE-2022-38181 分析文章、四个 AI 模型和一篇博客

vulnerability-analysisexploitationreverse-engineering+5
83个月前
beacon-hunter preview

beacon-hunter

GitHubmrcord77/beacon-hunter

检测phi结构的C2信标,这些信标可逃避RITA及基于常规的检测器。

network-securitypenetration-testingcommand-and-control+5
93个月前
CyberMeowfiaNS preview

CyberMeowfiaNS

GitHubxingchenrs/cybermeowfians

CyberMeowfil 的下一阶段(CVE-2026-43499 和 43074),可能偏向 vivo 设备?

android-securityvulnerability-analysisreverse-engineering+4
93个月前
cai preview

cai

GitHubaliasrobotics/cai

网络安全人工智能(CAI),面向AI安全的框架

penetration-testing-frameworksprivilege-escalationreconnaissance+8
9.7k3个月前
cve-2024-13176-timing-analysis preview

cve-2024-13176-timing-analysis

GitHubhaomin-yu/cve-2024-13176-timing-analysis

针对 OpenSSL CVE-2024-13176 中 ECDSA 时序泄露的插桩分析与可复现性材料

vulnerability-analysiscryptographypapers-research+2
3个月前
CVE-2026-76564 preview

CVE-2026-76564

GitHubtoanln-cov/cve-2026-76564

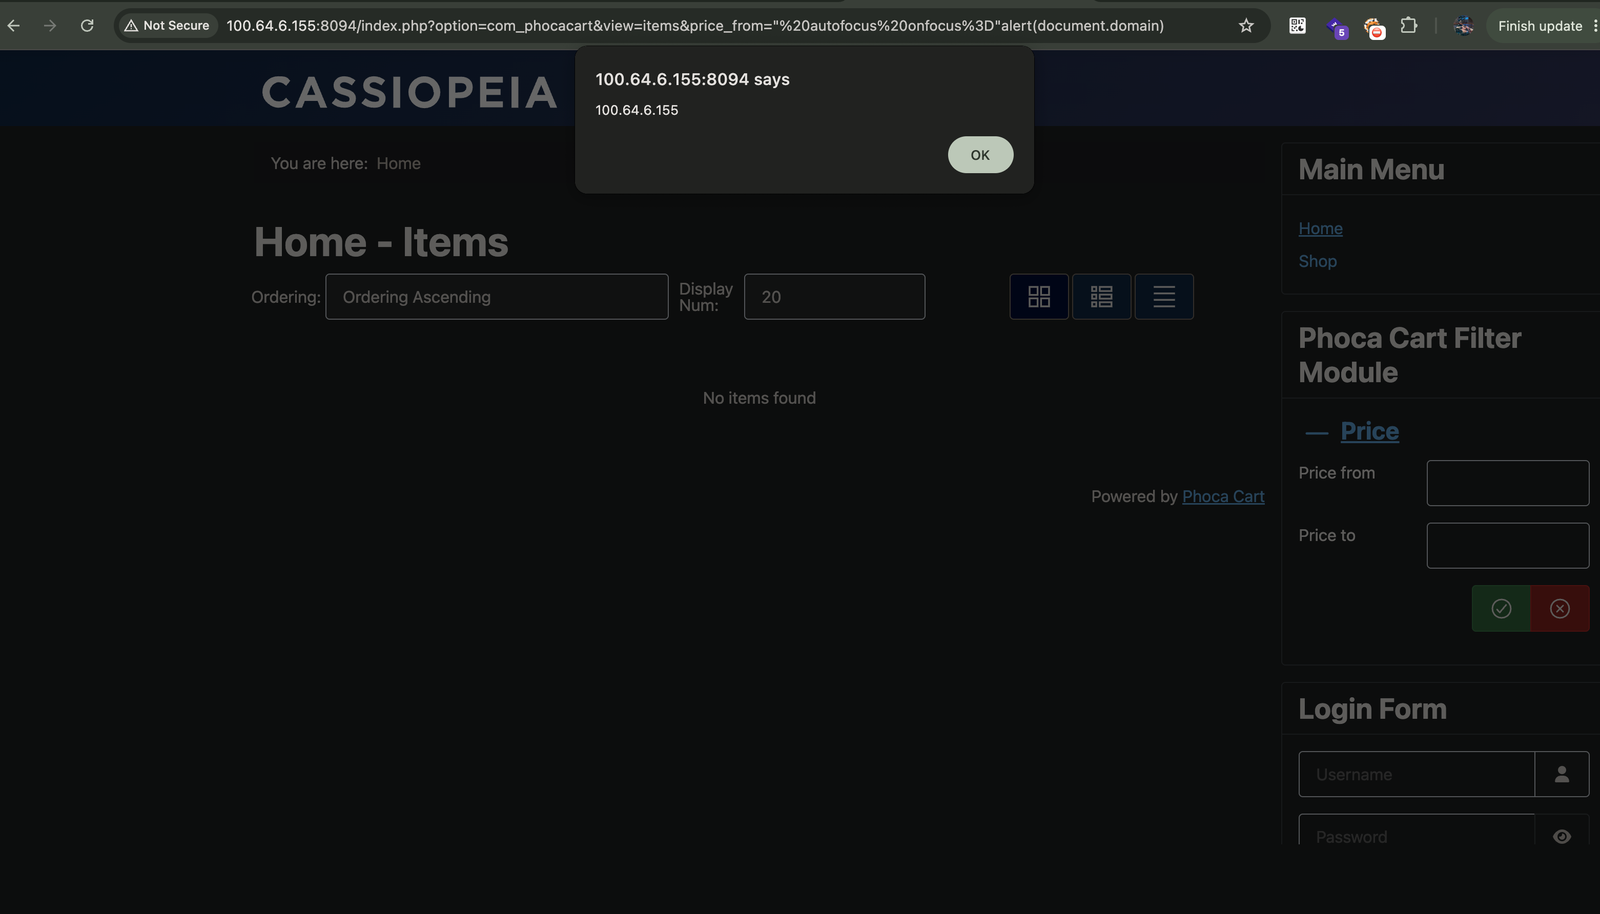
PhocaCart 管理后台订单视图中的存储型 XSS(通过 User-Agent 注入)
vulnerability-analysiscode-analysisexploitation+3
3个月前
CVE-2026-76565 preview

CVE-2026-76565

GitHubtoanln-cov/cve-2026-76565

PhocaCart 中通过 price_from 与 price_to 过滤参数导致的反射型 XSS

vulnerability-analysisexploitationweb-application-exploitation+2
3个月前
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

glibc 2.43 上 House of Apple 2 FSOP 技术的交互式 GDB 演练,附带可复现的沙箱环境,涵盖 vtable 绕过、栈迁移和 ROP。

memory-forensicsexploitationreverse-engineering+7
53个月前
rootkit-detection-ebpf-time-trace preview

rootkit-detection-ebpf-time-trace

GitHubait-aecid/rootkit-detection-ebpf-time-trace

通过分析内核函数执行时间的变化来检测rootkit文件隐藏活动。
machine-learningintrusion-detectionpapers-research+2
293个月前
CVE-2026-77113 preview

CVE-2026-77113

GitHub0xroi/cve-2026-77113

CVE-2026-77113 的技术分析:Apport 的 apport-unpack 中存在路径遍历漏洞,特制的报告键可逃逸提取目录,并在目标目录之外写入文件。

vulnerability-analysispapers-researcheducation
3个月前
Awesome-LLM4Cybersecurity preview

Awesome-LLM4Cybersecurity

GitHubtmylla/awesome-llm4cybersecurity

对756+篇关于LLM在网络安全中应用的论文进行的系统性文献综述,涵盖威胁情报、漏洞检测、模糊测试、攻击/防御以及未来研究方向。

vulnerability-analysisfuzzingpenetration-testing+6
1.7k3个月前
CVE-2024-4947-PoC preview

CVE-2024-4947-PoC

GitHubl1m3syc/cve-2024-4947-poc

针对 CVE-2024-4947 的教学概念验证,该漏洞为 V8 Maglev 类型混淆漏洞,演示了在非沙箱化的 d8 构建上从触发到任意代码执行的完整攻击链。

vulnerability-analysisexploitationweb-application-exploitation+3
3个月前
DB_Audit_Research preview

DB_Audit_Research

GitHubmthamil107/db_audit_research

Self-Defeating Audits:可复现的实验室环境,展示低权限 PostgreSQL 角色如何可逆地致盲基于触发器的审计器并污染归因(PG14/16),附带防御对策。使用合成数据;引用了 CVE-2018-1058 原语。
defensive-toolsexploitationpapers-research+4
3个月前
React2shell-Research preview

React2shell-Research

GitHubh3n1s3/react2shell-research

分析并复现 CVE-2025-55182,为安全研究人员提供技术见解和概念验证。

vulnerability-analysisexploitationpapers-research+1
3个月前
grandstream-cve-2026-2329-analysis preview

grandstream-cve-2026-2329-analysis

GitHubvivianuba/grandstream-cve-2026-2329-analysis

防御性漏洞研究项目,针对 CVE-2026-2329,比较存在漏洞和已修补的 Grandstream GXP1600 固件,使用 SquashFS 提取、Ghidra 逆向工程和 ARM ELF 跟踪来记录供应商的修复措施,而非武器化的 ex

static-analysisvulnerability-analysisreverse-engineering+4
3个月前
sudp preview

sudp

GitHubxhyumiracle/sudp

Secret-Use Delegation Protocol — 面向智能体系统的协议级密钥使用

authentication-authorizationcryptographyprivacy+5
63个月前
上一页1…515253…100下一页







