
 playb0t/mcp-remote-oauth-security
Forensic audit of mcp-remote OAuth trust boundaries: seven advisories and five CVE records covering SSRF via server-selected metadata URLs, redirect bypass and token storage, with loopback-canary reproductions.

Five published CVE records, all scored by CISA-ADP, up to 9.8 Critical.
In the 7 November 2026 loopback runs, published CLI 0.16.3, 0.16.4 and 0.16.5 reach the server-selected metadata paths of CVE-2026-51994 and CVE-2026-51995.



Research dossier, 9 October 2026 · 0.15.1 follow-up, 15 October 2026 · 0.15.2 / 0.16.0 follow-up, 3 November 2026 · 0.16.3 / 0.16.4 / 0.16.5 follow-up, 7 November 2026 · Procedure v2 and seven-version backfill, 7 November 2026 · MCP Host Matrix, 25 October 2026 · Advisory index · Impact ledger
In the static Bearer profile, published CLI 0.14.3 and 0.16.5 followed 401-selected metadata to a second loopback origin and, after the MCP POST was challenged, repeated the metadata requests carrying the configured Bearer. The no-resource_metadata controls did not contact the selected endpoints. Two-version static-header results are separate from earlier client-credentials profiles and do not change official CVE ranges.
WinCC OA revised its assessment of CVE-2026-51995, published v1.5.3 documentation and closed issue #40 after release. The bridge remains pinned to 0.14.3 until a verified upstream fix; this vendor-case closure does not mean mcp-remote is fixed. Vendor statements, release and limits.
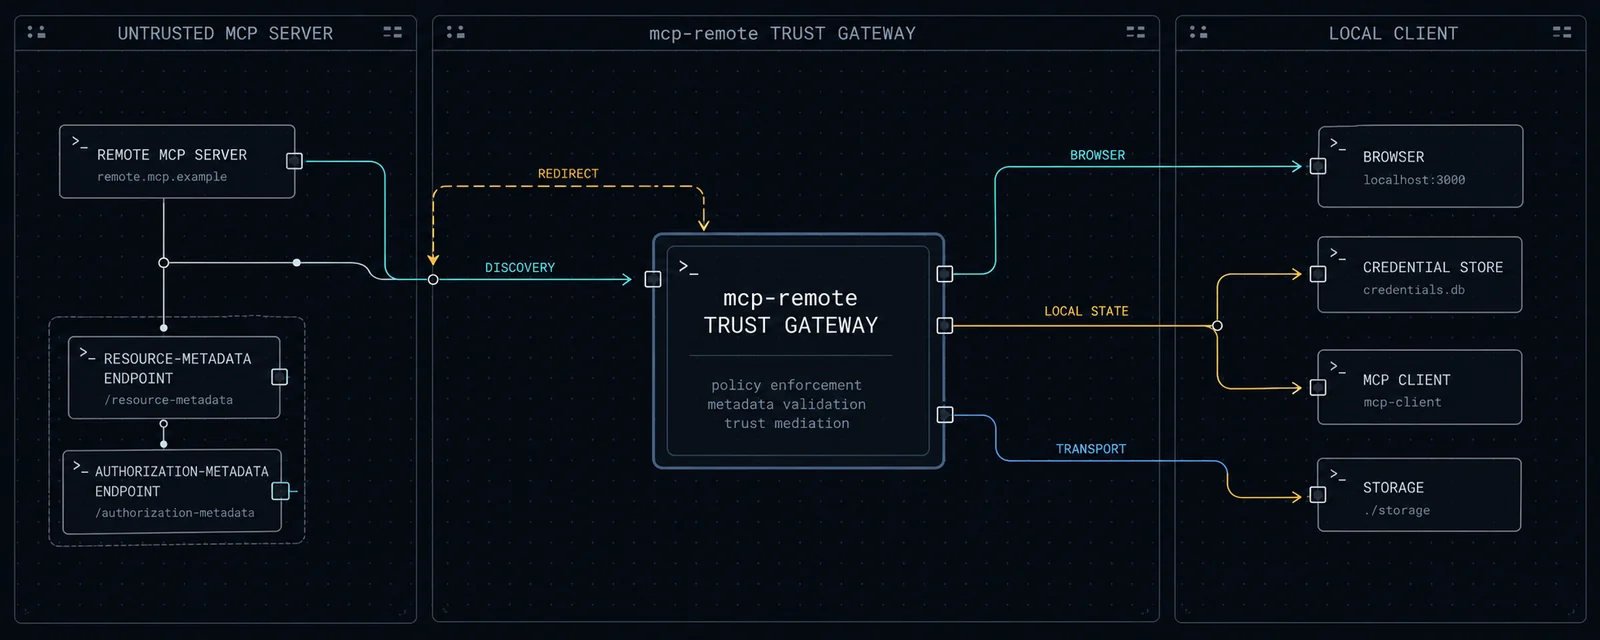
mcp-remote bridges stdio-only MCP clients to remote MCP servers and runs OAuth discovery on their behalf. That makes remote-server metadata a security boundary: a server-selected URL, redirect or credential destination must not become trusted because it appeared during discovery.
Seven advisories document the review of the release current at disclosure, 0.1.38: two localhost-canary reproductions, three bounded source reviews, two hardening records corrected in v1.0.1. The private report went to the maintainer on 17 February 2026; the public disclosure followed on 31 July after no acknowledgement; MITRE published five CVE records on 24 September 2026, and CISA-ADP scored all five. On 9 October 2026 the published 0.14.3 CLI, run in full in three local stdio scenarios, reproduced the F-01 / F-02 request path, HTTP 302 redirect included, and the discovery helpers executed in all 58 stable releases from 0.1.32 to 0.14.3. Between the private report and 7 October 2026 npm served 19,060,907 downloads of the package. The five follow-up releases 0.16.1 to 0.16.5 do not name the five records or announce a release addressing them; the ten selected first-party helpers are unchanged in the source comparisons, and 0.16.5 was compared in source/distribution and run through the original procedure, with all three CLI attempts stopping at its unchanged assertion. On 14 October 2026 the maintainer published four releases, 0.14.4 through 0.15.1; none of them names a record. On 15 October the 9 October procedure was repeated on 0.15.1. It recorded the same F-01 / F-02 request paths. In the full trace it also recorded a token request, carrying an Authorization header, to the authorization server named by the server's own metadata, as it does in 0.14.3 runs under the same environment.
From 7 November 2026, procedure v2 is the primary local regression procedure. It checks credentials against a predeclared issuer and receiver policy after the trace is settled, with OAuth client authentication separate from resource Bearer. The seven-version backfill preserves the original procedure and its stops, and records execution outcomes separately from credential-destination verdicts.
Methodology · Disclosure timeline · Corrections · Trust-boundary map
The F-* identifiers are stable research IDs. Ranges are those of the original advisories; scores are the published CISA-ADP CVSS 3.1 assessments, reported as published. The research asserts no numeric score of its own, and its evidence classes stay separate from the official severity.






