Skip to content
KitploitKITPLOIT
ИнструментыЭксплойтыБлог
Log in
Отправить
ИнструментыЭксплойтыБлог
Отправить

Инструменты для хакинга, пентеста и кибербезопасности — ваш арсенал защиты!

Kitploit — это каталог инструментов для хакинга, кибербезопасности и пентестинга. Находите последние обновления проектов для поиска уязвимостей, анализа систем, автоматизации тестирования и усиления вашей безопасности.

ЛентыКонтактыКонфиденциальность© 2026 Kitploit

Каталог инструментов

Категории

Все категории
Loading categories
kingfisher — Обнаруживайте секреты. Проверяйте их в реальном времени. Оценивайте масштаб потенциального ущерба. Быстро отзывайте. Запускайте CLI или встраивайте в Rust, Python или Node.js. | Kitploit
Инструменты/GitHubGitHub/mongodb/kingfisher
Статический анализСканеры уязвимостейБезопасность контейнеровДинамический анализ кода (DAST)Сбор информацииБезопасность облачных средDevSecOpsУтилиты и фреймворкиОбнаружение СекретовБезопасность Цепочки Поставок
GitHub
1.3k1261782 дней назадПроверено Kitploit
mongodb/kingfisher

kingfisher

Обнаруживайте секреты. Проверяйте их в реальном времени. Оценивайте масштаб потенциального ущерба. Быстро отзывайте. Запускайте CLI или встраивайте в Rust, Python или Node.js.
РепозиторийСайт
Поделиться
Контент недоступен на запрошенном языке. Показываем английскую версию.

Detect and Validate Secrets Anywhere. Map Access. Revoke Fast.

Kingfisher Logo
Apache 2.0 License Container downloads
GitHub downloads PyPI downloads

Find leaked secrets. Validate what’s live. Map the blast radius. Revoke fast.

Kingfisher is a fast, free, open-source secret scanner and credential response tool built in Rust. It detects leaked secrets with hundreds of built-in rules, validates which credentials are active, maps access for supported credential types, and revokes supported secrets—all in one Apache-2.0-licensed release:

Detect → Validate → Map → Triage → Revoke

  • scan source code, Git history, cloud storage, container images, archives, and developer platforms
  • validate which credentials are active
  • map a leaked secret's identity, permissions, and reachable resources
  • triage findings in a browser, or output as SARIF, JSON, TOON
  • send real-time alerts to Slack, Microsoft Teams, Discord, Mattermost, Google Chat, or any JSON webhook
  • revoke supported secrets

Defender workflow: Follow the end-to-end defender workflow for secret detection, validation, notifications, blast-radius mapping, and revocation.

Embed Kingfisher in Python, Node.js, or Rust

Add native secret detection, live credential validation, and explicit revocation to your Python, JavaScript/TypeScript (Node.js), or Rust application. The same Rust engine and rule catalog run in-process, with no CLI subprocess required. Kingfisher is an embeddable secret scanner that also runs as a standalone CLI.
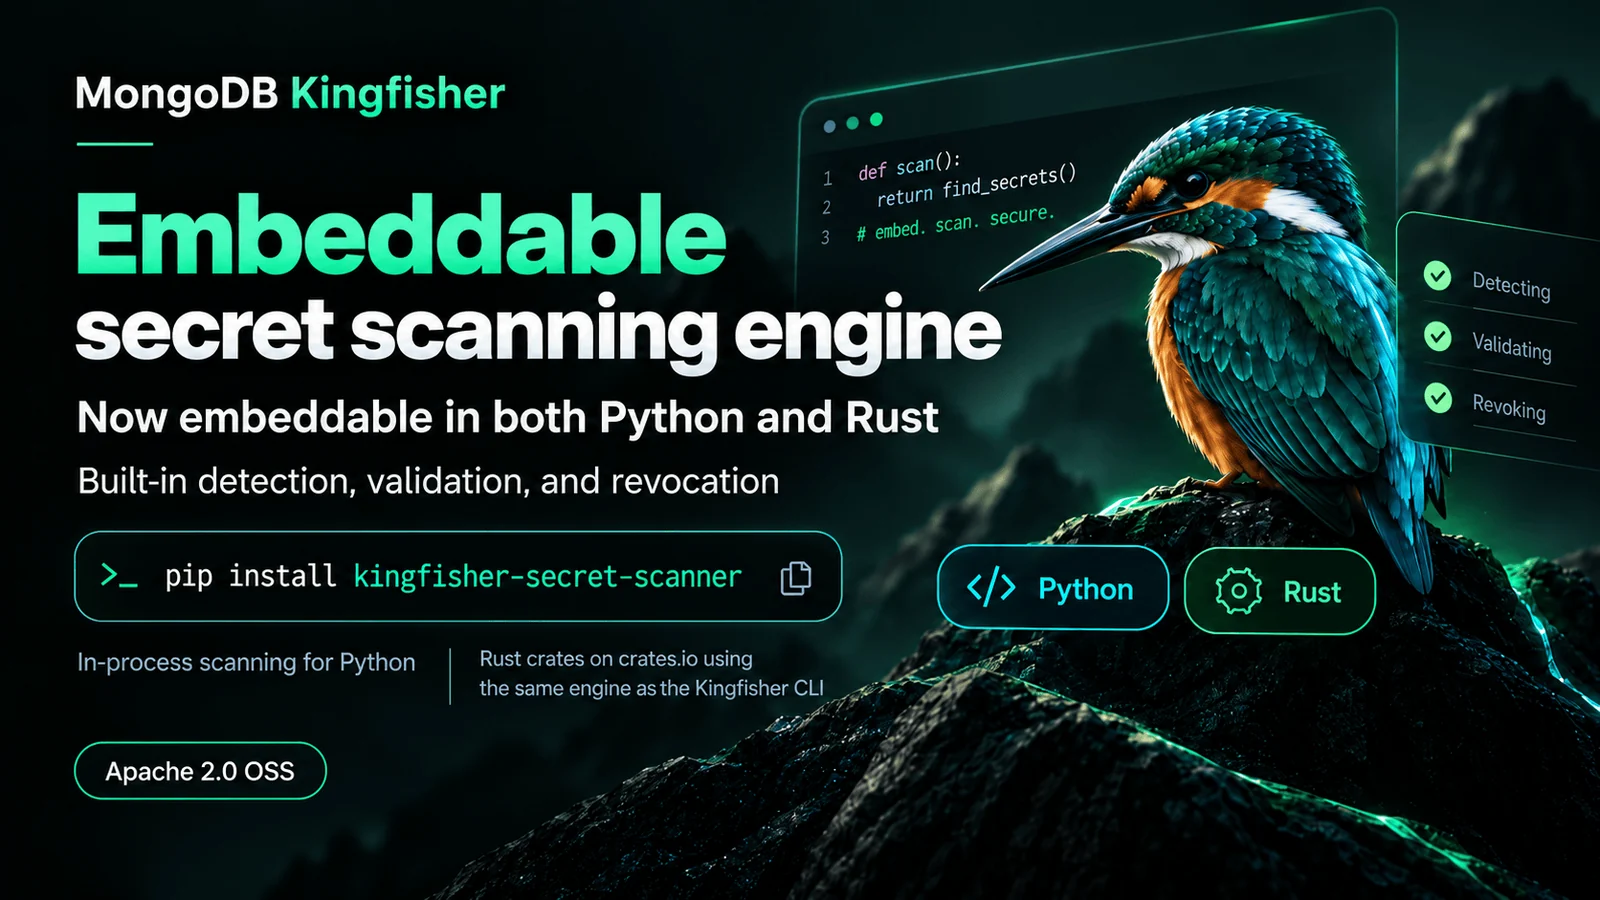
Kingfisher embeddable secret scanner: Detect Secrets → Validate → Map Blast Radius → Revoke. Native Python, Node.js/TypeScript and Rust SDK installs, plus CLI installation and HTML report commands.

Choose your language and add the SDK to your existing application:

  • Python:

    uv add kingfisher-secret-scanner
    

    Import kingfisher_sdk. See the Python SDK guide and runnable examples for scanning, validation, rule inspection, and explicit revocation.

  • Node.js / TypeScript:

    npm install kingfisher-secret-scanner
    

    The stable npm SDK 1.0.0 wraps the same Rust crates with napi-rs. See the Node SDK guide and source/examples. It targets Node.js, including VS Code workspace extensions, rather than browser/WASM runtimes. Explore Kingfisher Workbench, a commented showcase with live progress, Git-history scanning and a redacted HTML report, or start with the runnable recipe walkthrough; maintainers can follow the npm trusted-publishing setup.

  • Rust:

    cargo add kingfisher-scanner --features validation
    

    The validation feature enables live validation and revocation; omit --features validation for detection only. See the library guide, runnable examples, and revocation guide.

Or install the CLI, scan a codebase, and open the interactive HTML report:

uv tool install kingfisher-bin
kingfisher scan /path/to/code --view-report

Replace /path/to/code with your source directory. Scans validate credentials by default; add --no-validate for detection only. Add --blast-radius to map supported credentials' access when authorized. Revocation remains a separate, explicit action. See the CLI installation guide and usage guide for more options.

Scan Targets

Kingfisher handles local files and directories, Git repositories and history, compressed and office-document archives, SQLite databases, Python bytecode, Docker images, source-hosting organizations, cloud object storage, collaboration tools, and API-development platforms.

Files / DirsLocal GitGitHubGitLabAzure ReposBitbucketGiteaHugging Face
Files / Dirs
Files / Dirs
Local Git
Local Git
GitHub
GitHub
GitLab
GitLab
Azure Repos
Azure Repos
Bitbucket
Bitbucket
Gitea
Gitea
Hugging Face
Hugging Face
Скачать инструмент

Популярное

Смотреть все →

Откройте для себя самые используемые инструменты нашего сообщества.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Полный набор инструментов OSINT: граф расследования, оценка достоверности, семейства псевдонимов, карта, временная шкала и отчёты. 49 модулей, более 400 сайтов, API-ключи не требуются.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Приложение GhostLock с запуском в один клик (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Браузерный инструментарий для red team с 102 офлайн-инструментами для разведки, генерации полезной нагрузки, атак на учётные данные, криптографии, кодирования и отчётности по проектам.

    366
  • 4

    ARTEX

    baarai/artex

    Платформа автономного тестирования на проникновение на основе мультиагентной LLM с агентами-планировщиками и агентами-исполнителями, графами активов и исследования, записью MITM-трафика и повторной проверкой уязвимостей.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    Платформа CSIRT, которая загружает отчёты Shadowserver в MongoDB и воспроизводит их в виде интерактивных карт, аналитики, результатов, рекомендаций и исполнительных дашбордов.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Система действий для кибербезопасности на базе ИИ — где намерение превращается в управляемое исполнение, доказательства становятся оперативной памятью, а каждая операция улучшает следующую.

    287

Изучить все инструменты

Просмотрите нашу коллекцию инструментов

Смотреть все инструменты →