
Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
SafeGuard — CLI Encryption tool written in Go only for learning purposes and demonstration of encryption (not secure) | Kitploit
Ferramentas/GitHubGitHub/pingpongplus/safeguard
General Purpose UtilitiesEncryption/Decryption ToolsCryptographyLearning & Education
GitHubpingpongplus/safeguard

SafeGuard

CLI Encryption tool written in Go only for learning purposes and demonstration of encryption (not secure)

Ver Repositório
81103há 6 diasAinda não revisado
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

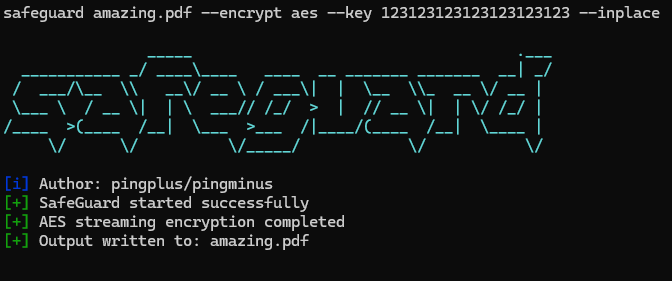
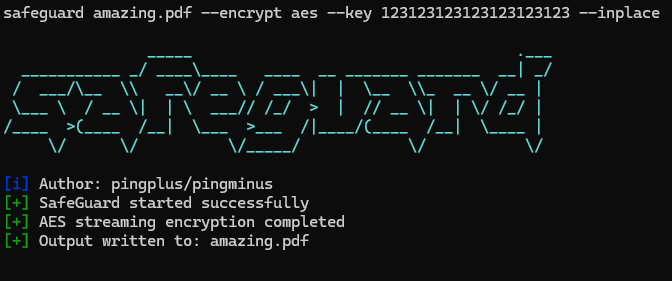
Safeguard-Terminal


Safeguard is a fast, lightweight, cross-platform command-line file encryption tool written in Go.

Security Notice

This project is a learning-oriented file encryption tool.

While it uses standard cryptographic primitives from Go’s standard library (e.g. AES-GCM for authenticated encryption), it does not use a modern, memory-hard password key derivation function such as Argon2 or scrypt.

Instead, keys are derived using a lightweight, standard-library-only method. This means:

  • The encryption is secure against casual inspection
  • Integrity and tampering are detected
  • Passwords are not strongly protected against determined brute-force or GPU-based attacks

Do NOT use this tool fr your key is in plaintext and is getting saved in your terminal history

Intended use:

  • Learning and experimentation
  • Personal or low-risk file protection
  • Open-source collaboration and improvement

Installation

Build (req. Go)

git clone https://github.com/pingplus/SafeGuard.git
cd SafeGuard
go build

Usage

General syntax:

./safeguard <file> <action> <cipher> [options]

Actions:

  • --encrypt or e Encrypt a file
  • --decrypt or d Decrypt a file
  • --decrypt-directory or de Decrypt a whole directory (decrypting directory not available yet sorry :( )

Options:

  • --inplace decrypt/encrypt a file in place (experimental)
  • --key add key
  • --output specify the output name

Supported ciphers:

./safeguard --list-ciphers
[i] Available ciphers:
  xor
  caesar
  aes

AES

Encrypt a file:

./safeguard secret.txt e aes --key "your-strong-password"
# or
./safeguard secret.txt --encrypt aes --key "your-strong-password" --output secret.txt.aes

Decrypt a file:

./safeguard secret.txt d aes --key "your-strong-password"
# or
./safeguard secret.txt --decrypt aes --key "your-strong-password" --output secret.txt.dec

More

  • Encrypt with AES and write in place:
./safeguard secrets.txt e aes --key "123123123123123123123123" --inplace
# -> creates secrets.txt but encrypted
  • Decrypt with AES and specify output file :
./safeguard secrets.txt.aes d aes --key "123123123123123123123123" --output secrets_decrypted.txt

Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingere relatórios do Shadowserver no MongoDB e os reproduz como mapas interativos, análises, descobertas, avisos e painéis executivos.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    O sistema de ação para cibersegurança nativa em IA—onde a intenção se torna execução governada, a evidência se torna memória operacional, e cada operação melhora a próxima.

    282

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →





