Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
agent-bom — AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account. | Kitploit
Ferramentas/GitHubGitHub/msaad00/agent-bom
Vulnerability ScannersContainer SecurityCloud SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityMisconfigurationAI Security
GitHubmsaad00/agent-bom

agent-bom

AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code, containers, cloud and AI. Self-host free; local scans need no account.

29788há 14h 13mRevisado pelo Kitploit
Ver RepositórioSite
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

agent-bom — AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

Build PyPI Python 3.11 through 3.14

Apache-2.0 license OpenSSF Scorecard

AI supply-chain BOM: supported agents, MCP servers and AI packages, and what each one can reach.

For AppSec teams and developers who run Claude Code, Cursor, Codex or any MCP client: see which agents, MCP servers, tools and packages are installed, which are vulnerable, and what each one can reach. Local scans need no account.

Quick start · Try in browser · Laptop → team → org · Product tour · Docs

Quick start

From the repository you want to inspect, with uv installed:

uvx agent-bom scan . -f html -o agent-bom-report.html

Open agent-bom-report.html for inventory, findings and fix guidance. Run it again later to see what changed. No MCP configuration in the project? Package findings still apply.

No project handy? uvx agent-bom scan --demo --offline scans a bundled sample. Exit 1 is expected there: the sample trips the security gate. Elsewhere, a non-zero exit can mean a security gate or incomplete assessment; inspect the report and coverage (exit codes, first-run guide).
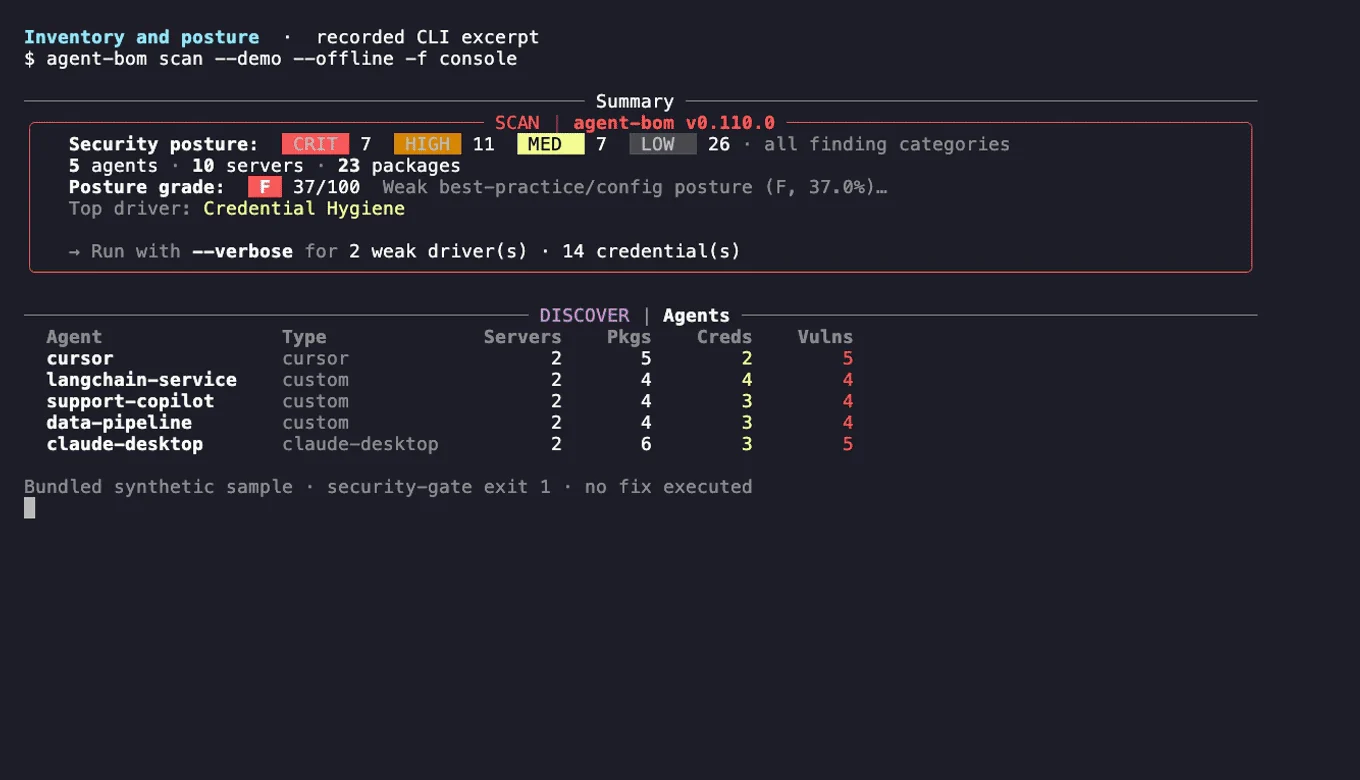
Recorded agent-bom CLI showing sample findings and remediation guidance; no fix executed

What the scan reads and what it does not establish

The scan stays inside this repository: packages, MCP configuration, secrets and personal data, skills and IaC. It does not read agent configuration elsewhere on the machine. Missing evidence is reported as partial, not clean. See what a scan does and does not establish.

From laptop to team to org

  • On your laptop: uvx agent-bom scan . for findings with fixes and a delta on every rescan; claude mcp add agent-bom -- uvx agent-bom mcp server to use agent-bom as a tool inside your coding agent (MCP server, plugins).
  • In your team: uses: koda-ai-studio/agent-bom@v0 on pull requests and a weekly schedule: for a PR gate with a findings comment, SARIF in code scanning and a weekly rescan that catches new CVEs in unchanged code (GitHub Action).
  • Across your org: agent-bom up locally, then Docker Compose or the Helm chart from oci://ghcr.io/koda-ai-studio/charts/agent-bom for retained scans, one graph of agents, MCP servers, packages and credentials, SSO and audit in your own infrastructure (self-host).

All three are free under Apache-2.0 and are adoption paths, not editions. There is no managed cloud offering today; community support runs on GitHub (deployment chooser, support model).

Why an AI supply-chain BOM

A CVE in an AI package, a poisoned tool description or an over-scoped credential matters by what the agent that loads it can reach. A package SBOM stops at packages; agent-bom records the chain, agent → MCP server → tool → package → credential → data, and keeps the evidence for every edge.

Sample production AI environment: Document Intake Agent uses a document-tools MCP server that depends on pillow 9.0.0, linked to KEV-listed CVE-2023-4863; Support Triage Agent uses a ticketing MCP server that references TICKETING_API_KEY, which can access a customer ticket archive

Sample data. What the sample shows

What it covers

Agents and MCP servers, models and AI platforms, dependencies, code, containers and IaC, cloud and data platforms, and a runtime MCP proxy and gateway. Exports are SARIF, CycloneDX, SPDX, JSON and HTML.


Coverage by area
Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    O sistema de ação para cibersegurança nativa em IA—onde a intenção se torna execução governada, a evidência se torna memória operacional, e cada operação melhora a próxima.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingere relatórios do Shadowserver no MongoDB e os reproduz como mapas interativos, análises, descobertas, avisos e painéis executivos.

    256

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →