Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
0 — Software infrastructure to build and deploy sovereign, persistent AI security agents that continuously find, prove and fix security risks. Open source. Web UI, CLI, CI and MCP. | Kitploit
Ferramentas/GitHubGitHub/0sec-labs/0
Static AnalysisVulnerability ScannersVulnerability AnalysisFuzzingPenetration TestingDevSecOpsBinary AnalysisRed TeamingAI Security
GitHub0sec-labs/0

0

Software infrastructure to build and deploy sovereign, persistent AI security agents that continuously find, prove and fix security risks. Open source. Web UI, CLI, CI and MCP.

1.4k188194há 14h 40mRevisado pelo Kitploit
Ver RepositórioSite
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

0security

Sovereign AI security agents

By the Swiss Applied AI & Cybersecurity Research Lab

Backed by Y Combinator
Latest release MIT or Apache-2.0 license GitHub stars

0security is software infrastructure to deploy sovereign, persistent AI security agents that find and fix security risks across any tech stack, work with any model, and run anywhere.

Documentation Security research Install locally Enterprise

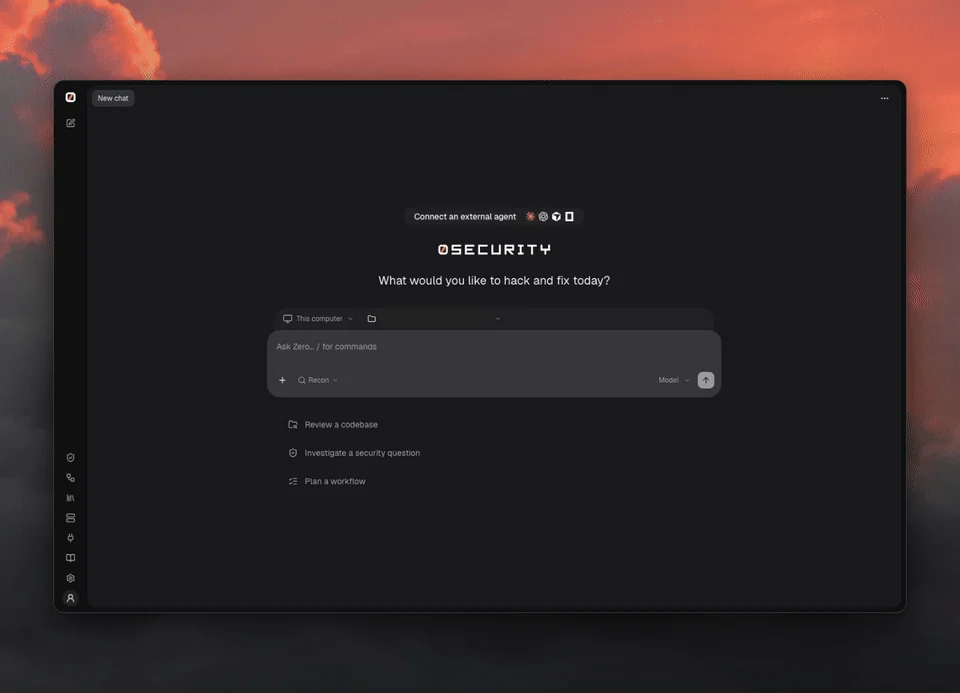
0 web UI: review a demo API, watch the investigation, then open findings with suggested fixes and verification

Quick start

curl -fsSL https://raw.githubusercontent.com/0sec-labs/0security/main/install.sh | bash
0

Prefer the terminal?

export OPENAI_API_KEY="your-api-key"
0 scan ./your-repo --runtime api --depth quick --cost-ceiling 2

Any supported provider works: set its key instead (Anthropic, OpenRouter, DeepSeek and more, see Models), or connect one in the browser with 0.

Windows, Docker and source installs
  • Windows (experimental): download 0-windows-x64.exe from Releases.
  • Docker: docker run --rm ghcr.io/0sec-labs/0security:latest --help. See the Docker guide.
  • Source: Node.js 24+ and pnpm, then pnpm install --frozen-lockfile && pnpm build.
  • install.sh supports Apple Silicon macOS and x64/ARM64 Linux. Set INSTALL_DIR to change the location.

Only scan systems you own or are authorized to test. See Scope.

What can you do with 0?

  • Find vulnerabilities in source code, web apps and APIs, MCP endpoints and packages
  • Check dependencies with 0 scan . --module deps and 0 scan . --module deps-fix for npm, pnpm, Cargo and PyPI
  • Hunt variants of a known fix across a codebase
  • Reverse engineer binaries with Ghidra, plus kernel and memory-safety fuzzing
  • Map your attack surface: domains, JavaScript, cloud and Entra ID posture
  • Verify and fix: reproduce findings, generate patches and validate each one
  • Build persistent security agents: Agents with a scope, budget and memory that run on a schedule or on every pull request, with skills, extensions and automations
  • Disclose: assemble GHSA-ready advisory drafts from saved findings
  • Test AI agents with prompt-injection campaigns
  • Automate scans in CI with JSON and SARIF output
  • Extend it with extensions and skills, or drive it from coding agents over MCP

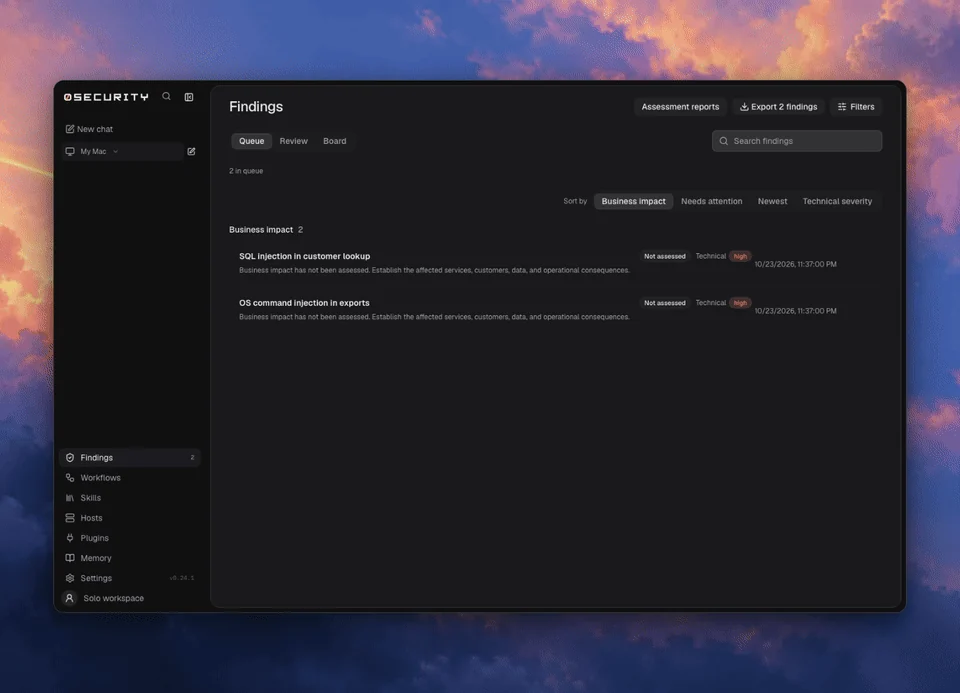
0 findings: review the queue, organize the board, and inspect source evidence

Why 0?

  • Open source: MIT or Apache-2.0, built in the open
  • Private: runs on your computer, in your CI or in a container, and only the context you send to your chosen model leaves it
  • Flexible: any provider key or local OpenAI-compatible server, from the CLI, CI or a coding agent over MCP
  • Evidence first: every finding links to its source evidence
  • Verified fixes: patches are reproduced and validated before you apply them
  • Proven in public: disclosed vulnerabilities and upstream fixes, including in the Linux kernel

CI and coding agents

0 agents run --automation --template security-research \
  --target /absolute/path/to/repo --workspace /absolute/path/to/repo
0 lab mcp-server --automations --workspace /absolute/path/to/repo

See the CI guide, extensions and MCP and the command reference.

Learn more

  • Documentation
  • Scan from the terminal
  • Models and providers
  • CI guide
  • Extensions and MCP
  • Command reference
  • Security research
  • Enterprise

Contributing

0 is built in the open. Huge thanks to everyone who has filed a bug, fixed a doc or sent a patch.

  • Report bugs in issues
  • Improve the docs
  • Write an extension or scan module
  • Found a vulnerability in 0? See SECURITY.md

Start with the contributing guide. Run pnpm install and pnpm dev to work on the engine. Open an issue before large changes.


Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    500
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    466
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    339
  • 4

    opencti

    opencti-platform/opencti

    Plataforma Aberta de Inteligência de Ameaças Cibernéticas

    317
  • 5

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    307
  • 6

    estorides

    grisuno/estorides

    Agrega mais de 99 fontes OSINT gratuitas em paralelo, resolve entidades em um grafo de conhecimento e exporta STIX 2.1, MISP ou GraphML com análise assistida por LLM.

    294

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →