

Vigil
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
penetration-testing-frameworksreconnaissancestatic-code-analysis+9
29
 knostic/openant
Knostic의 OpenAnt는 검증된 보안 결함을 사전에 찾아내고 오탐(false positive)과 미탐(false negative)을 모두 최소화하도록 방어자를 돕는 선도적인 오픈 소스 LLM 기반 취약점 발견 제품입니다. 1단계는 탐지합니다. 2단계는…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 0xdea/semgrep-rules
취약점 연구를 용이하게 하기 위한 제 Semgrep 규칙 모음입니다.
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 makenowjust-labs/recheck
정적 분석 도구로, JavaScript 및 Scala 코드베이스에서 ReDoS(정규식 서비스 거부) 취약점을 탐지하며, 신뢰할 수 있는 정규식 보안 검사를 제공합니다.
 github/codeql
CodeQL: 전 세계 보안 연구원들과 GitHub Advanced Security의 코드 스캐닝을 지원하는 라이브러리 및 쿼리 모음입니다.
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
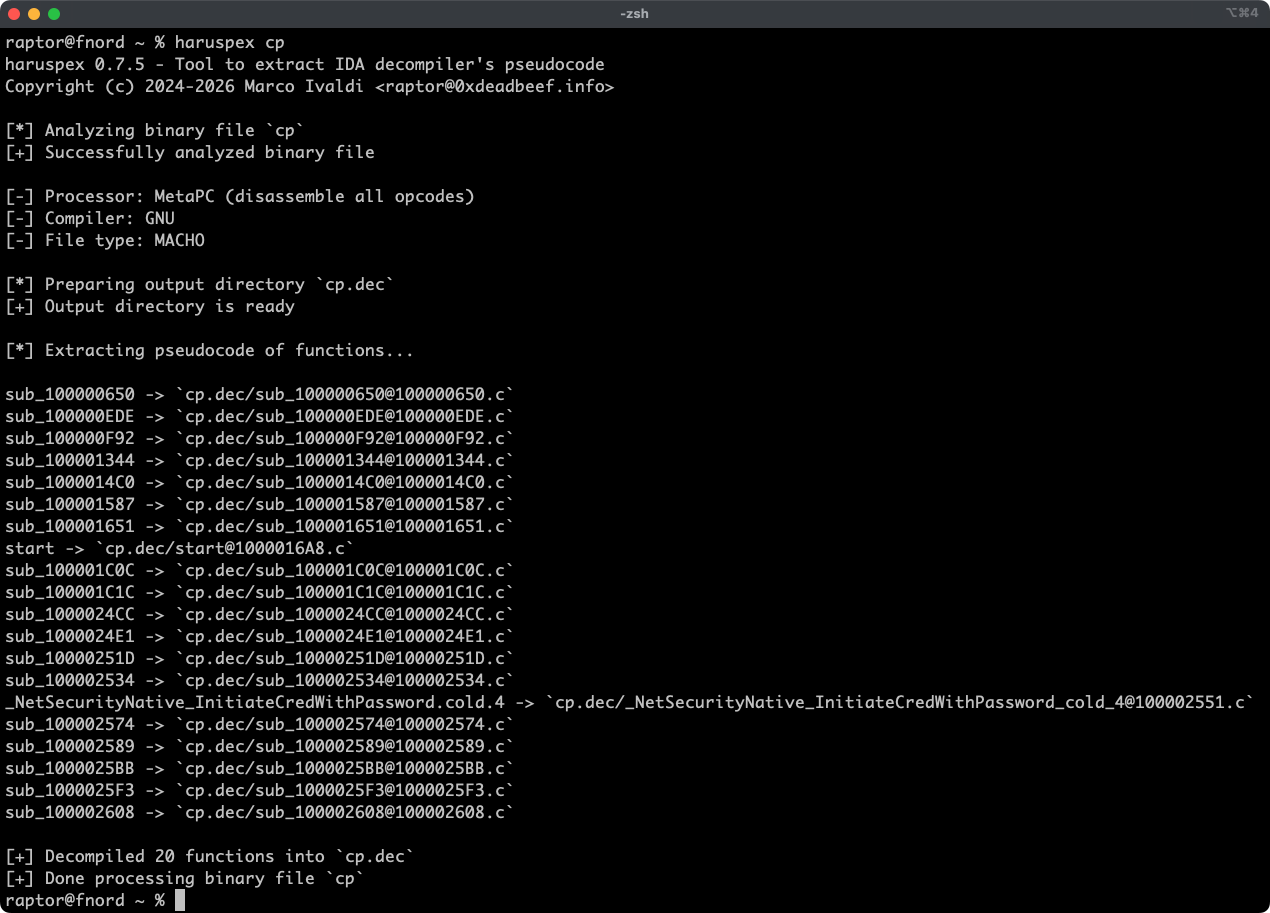 0xdea/haruspex
IDA Hex-Rays 디컴파일러에서 의사 코드를 추출하는 취약점 연구 보조 도구
 sonarsource/sonarqube
품질 게이트, 다중 언어 스캐닝, CI/CD 워크플로우에서 취약점 및 유지보수성 문제를 탐지하는 보안 중심 규칙을 갖춘 코드 품질 및 정적 분석 플랫폼입니다.
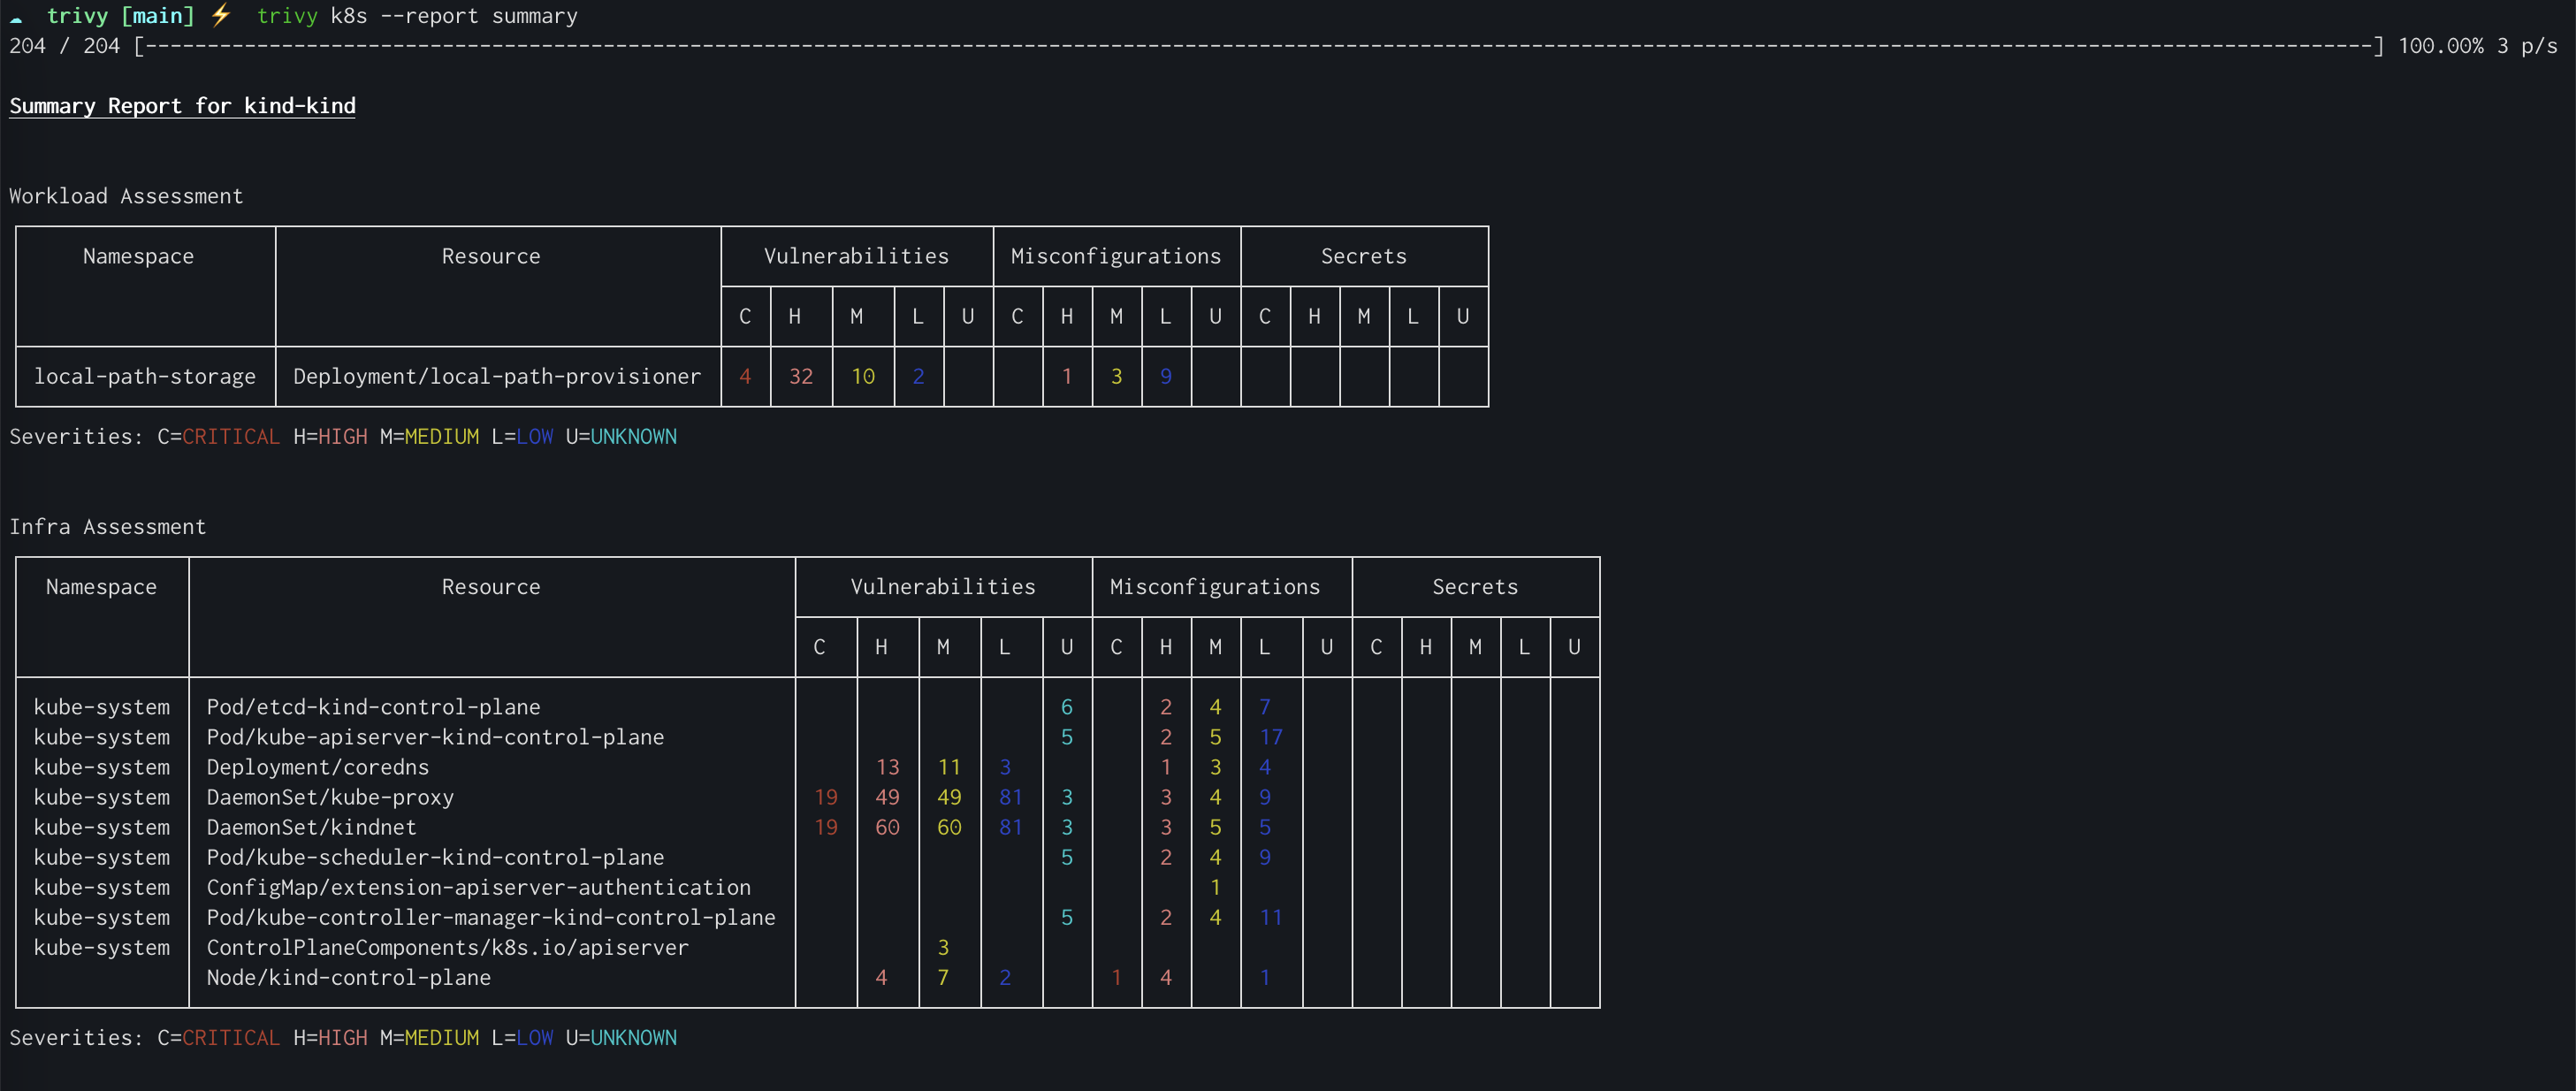 aquasecurity/trivy
컨테이너, Kubernetes, 코드 리포지토리, 클라우드 등에서 취약점, 잘못된 구성, 비밀, SBOM을 찾습니다.
 facebook/infer
Java, C, C++, Objective-C를 위한 정적 분석기
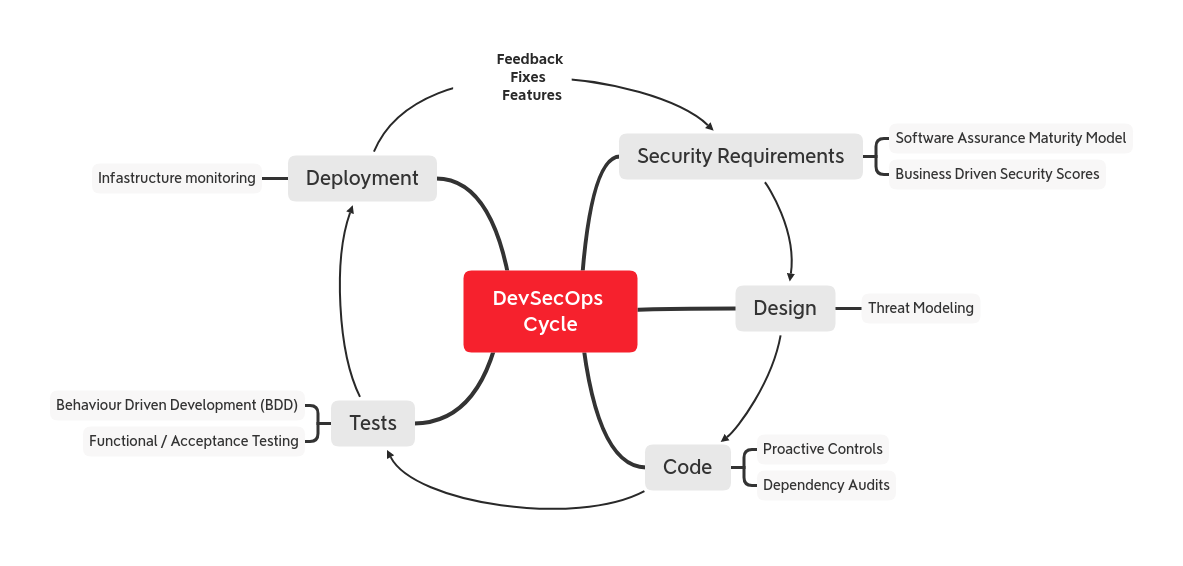 owasp/devsecopsguideline
OWASP DevSecOps 가이드라인은 보안을 개발 파이프라인의 일부로 내장하는 데 도움이 될 수 있습니다.